Does Linode Work in China? ICP, Data Residency & an Offshore Cloud
Linode runs no compute region inside mainland China — its servers sit in the US, Europe, Japan, Singapore, India, Australia and elsewhere — so a China-facing site is served offshore with no ICP-filing path, and your users' data lands outside the mainland under PIPL. A compliance-first look at the two doors.
Does Linode work in China?
Whether Linode works for a mainland-China audience is a licensing and data-residency question before it is a speed one. Linode — now Akamai's cloud-computing platform — is where your own servers and their data live, and China's law responds to where that is.
By Linode's own region list there is no compute region inside mainland China: its data centers span the United States, Europe, Japan, Singapore, India, Indonesia, Australia, Brazil and Canada, and for Asia-Pacific workloads Linode itself recommends Singapore or Sydney. So a public site you run on Linode reaches mainland users from offshore, with no ICP-filing path on Linode itself; and any personal data you hold there for Chinese users is a cross-border transfer PIPL governs. The table below is Linode's own footprint and the China rules it triggers — plus the compliant, ICP-filed in-country path.
This is a risk map, not a legal verdict — your duties turn on what you serve and the personal data you hold. Our China team can map the ICP and data-residency path with you →
What Linode's own documentation says about China
| Fact | Primary source |
|---|---|
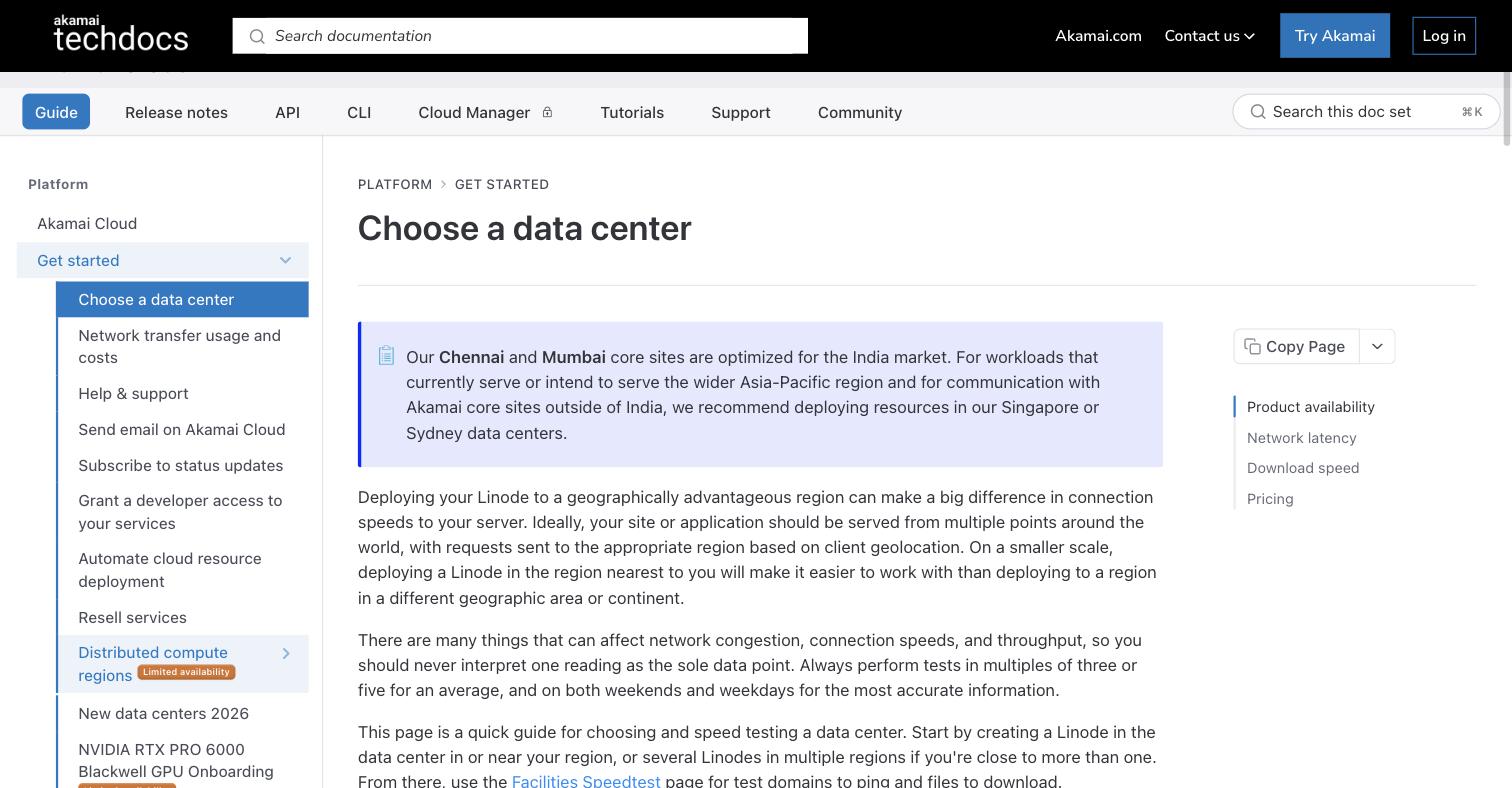
| In Linode's own documentation, its compute regions span 15 countries — the United States, Canada and Brazil; the United Kingdom, Germany, France, the Netherlands, Italy, Spain and Sweden; India, Japan, Indonesia and Singapore; and Australia — and for Asia-Pacific workloads it recommends "deploying resources in our Singapore or Sydney data centers." None of its regions is in mainland China; the nearest, in Japan and Singapore, are still offshore. | Akamai Cloud (Linode) — Choose a data center, and the Linode Regions API, retrieved 2026-10-07 |
| Serving a public website to mainland-China visitors from inside the mainland requires an ICP filing (ICP 备案) under the State Council's Order No. 292 and MIIT's Order No. 33, and that filing must attach to a hosting resource physically located in the mainland. Because Linode operates no mainland-China region, a Linode-hosted site has no ICP-filing path on Linode itself — it is reaching China from offshore. | PRC Regulations on Telecommunications (State Council Order No. 292); Administrative Measures for the Filing of Non-operational Internet Information Services (MIIT Order No. 33) |
| Store Chinese users' personal data on an offshore Linode region and it sits outside the mainland, so PIPL treats it as a cross-border transfer: the handler — you, Linode's customer, not Linode — must give notice, obtain separate consent, and satisfy one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification). | Personal Information Protection Law, Chapter III, Articles 38–43 |
| For a CIIO or large-volume handler, personal information collected in China must be stored inside mainland China (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). Linode publishes no mainland-China region, so none of its locations can satisfy a data-localization duty — keeping that data on Chinese soil means running the storage on infrastructure inside the mainland, which is where an ICP filing enters the picture. | PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) |
| The exposure scales with volume and role, not merely with using the host: under the CAC's March 2024 cross-border rules, a non-CIIO transferring fewer than 100,000 individuals' non-sensitive personal information in a calendar year is exempt from the security assessment, standard contract and certification — a line worth checking before you assume you are clear. | CAC — Regulations on Promoting and Regulating Cross-border Data Flows, March 2024 |
Sources verified by the 21YunBox compliance team on 2026-10-07.
Linode is easy to reach from China and easy to stand a server up on — which is exactly why the real question gets skipped. For a mainland audience it is not latency that decides whether you can use Linode; it is a licensing fact and a data-residency fact. Linode, the cloud-computing platform Akamai now runs, operates no region inside mainland China, so a China-facing site on it is served from offshore. That single geography decides two things at once: there is no mainland hosting resource to anchor an ICP filing to, and the personal data you collect from Chinese users comes to rest outside the country, where China’s cross-border rules take over. The network distance is a performance problem; these two are compliance problems.
Linode in China at a glance
| What decides it | In Linode's own terms |
|---|---|
| Where it runs | 33 compute regions across 15 countries — the US, Canada and Brazil; the UK, Germany, France, the Netherlands, Italy, Spain and Sweden; India, Japan, Indonesia and Singapore; and Australia. No region is inside mainland China; the nearest, in Japan and Singapore, are still offshore. |
| What it recommends for Asia | For Asia-Pacific workloads Linode's documentation recommends “deploying resources in our Singapore or Sydney data centers” — both outside the mainland. There is no mainland-China region to recommend. |
| Serving the public | A site served to mainland visitors from inside China needs an ICP filing tied to a mainland hosting resource. With no mainland region, Linode offers no ICP-filing path of its own. |
| Your data on Linode | Personal data of Chinese users stored on an offshore Linode region is a cross-border transfer PIPL governs — plus an in-country storage duty for CIIOs and large-volume handlers that an offshore region cannot meet. |
| Reachability vs. compliance | Reaching an offshore Linode from the mainland is a delivery matter, not a block — but a load does not create an ICP filing or in-country residency, so it is not the compliance answer. (No first-party speed figures are claimed for Linode here.) |
No mainland region, so nothing to anchor an ICP filing
Linode — Akamai’s cloud-computing platform — runs its compute regions across the United States, Canada, Brazil, the United Kingdom, Germany, France, the Netherlands, Italy, Spain, Sweden, India, Japan, Indonesia, Singapore and Australia. Not one sits in mainland China; the closest, in Japan and Singapore, are still outside it, and for Asia-Pacific workloads Linode’s own guidance is to recommend “deploying resources in our Singapore or Sydney data centers.”
That geography settles the licensing question before speed ever enters it. A public website delivered to mainland visitors from inside China turns on an ICP filing (ICP 备案) under State Council Order No. 292 and MIIT Order No. 33, and the filing has to attach to a hosting resource that physically sits in the mainland. A Linode instance is your origin — the place your application and its data actually run — and Linode gives you none inside the mainland, so there is nothing there to file against. Being part of Akamai’s wider delivery footprint does not change this: content delivery is not a mainland hosting resource, and it is your origin, not an edge, that an ICP filing and data-residency rules attach to. “We already run on Linode” is the point where that logic stops — reaching China is not the same as being cleared to operate there, and tuning the stack does not create the mainland footing a filing needs.
Your China users’ data stays offshore
Run your China service on Linode and the personal information you collect from mainland users lives wherever your region sits — the US, Europe, Japan, Singapore or elsewhere, all outside the mainland. Under China’s Personal Information Protection Law that movement is a cross-border transfer, and the duty falls on the handler — you, not Linode — to give notice, obtain separate consent, and clear one transfer mechanism: a CAC security assessment, the CAC standard contract, or certification. If you are a critical information infrastructure operator or a large-volume handler, personal information gathered in China has to be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — a residency duty none of Linode’s fifteen countries can meet.
Reachable or not, the compliance gaps remain
Linode is a mainstream cloud, not a categorically blocked one, so the honest framing is that reaching an offshore Linode site from China is a delivery question — distance and routing, not a wall. But reachability is only ever half the answer, and it is not the half that decides whether you may operate. Even on a day a Linode-hosted page loads cleanly for a mainland visitor, that visit still happens from offshore: it creates no ICP filing for your origin and no in-country residency for your data. Those two gaps are compliance facts, and no amount of network tuning closes them. We publish no first-party speed measurements for Linode from inside China, so none are claimed here.
None of this is a legal verdict — it is a map of where the risk sits. Whether an ICP filing, in-country storage, or both apply to you turns on what you serve, the volume of personal data you hold, and who your users are, and that is a call to make with counsel before you build.
Where 21YunBox fits — a compliant overlay, not a migration
Your application goes on running on Linode exactly as it does today. What an offshore cloud cannot hand you — a mainland footing to file against, and in-country data residency — we add as a layer: compliant, ICP-filed delivery from inside mainland China, placed in front of your existing Linode origin, with no rebuild, no second codebase and no move off Linode. Our China team maps your ICP and cross-border obligations against your entity and the personal data you hold, then stands up the in-country delivery and, where the law requires it, in-country storage — while your Linode servers stay put.
Related reading: