Does Azure Work in China? ICP, Data Residency & the 21Vianet Instance
Azure runs in mainland China only as a separate, 21Vianet-operated instance that needs a Chinese legal entity, a new account and an ICP filing — and global Azure keeps your China data offshore. A compliance-first look at the two doors.
Does Azure work in China?
Yes — Azure runs inside mainland China, but only as "Microsoft Azure operated by 21Vianet," a physically separated instance run by a licensed Chinese company. Your global Azure subscription does not reach into it.
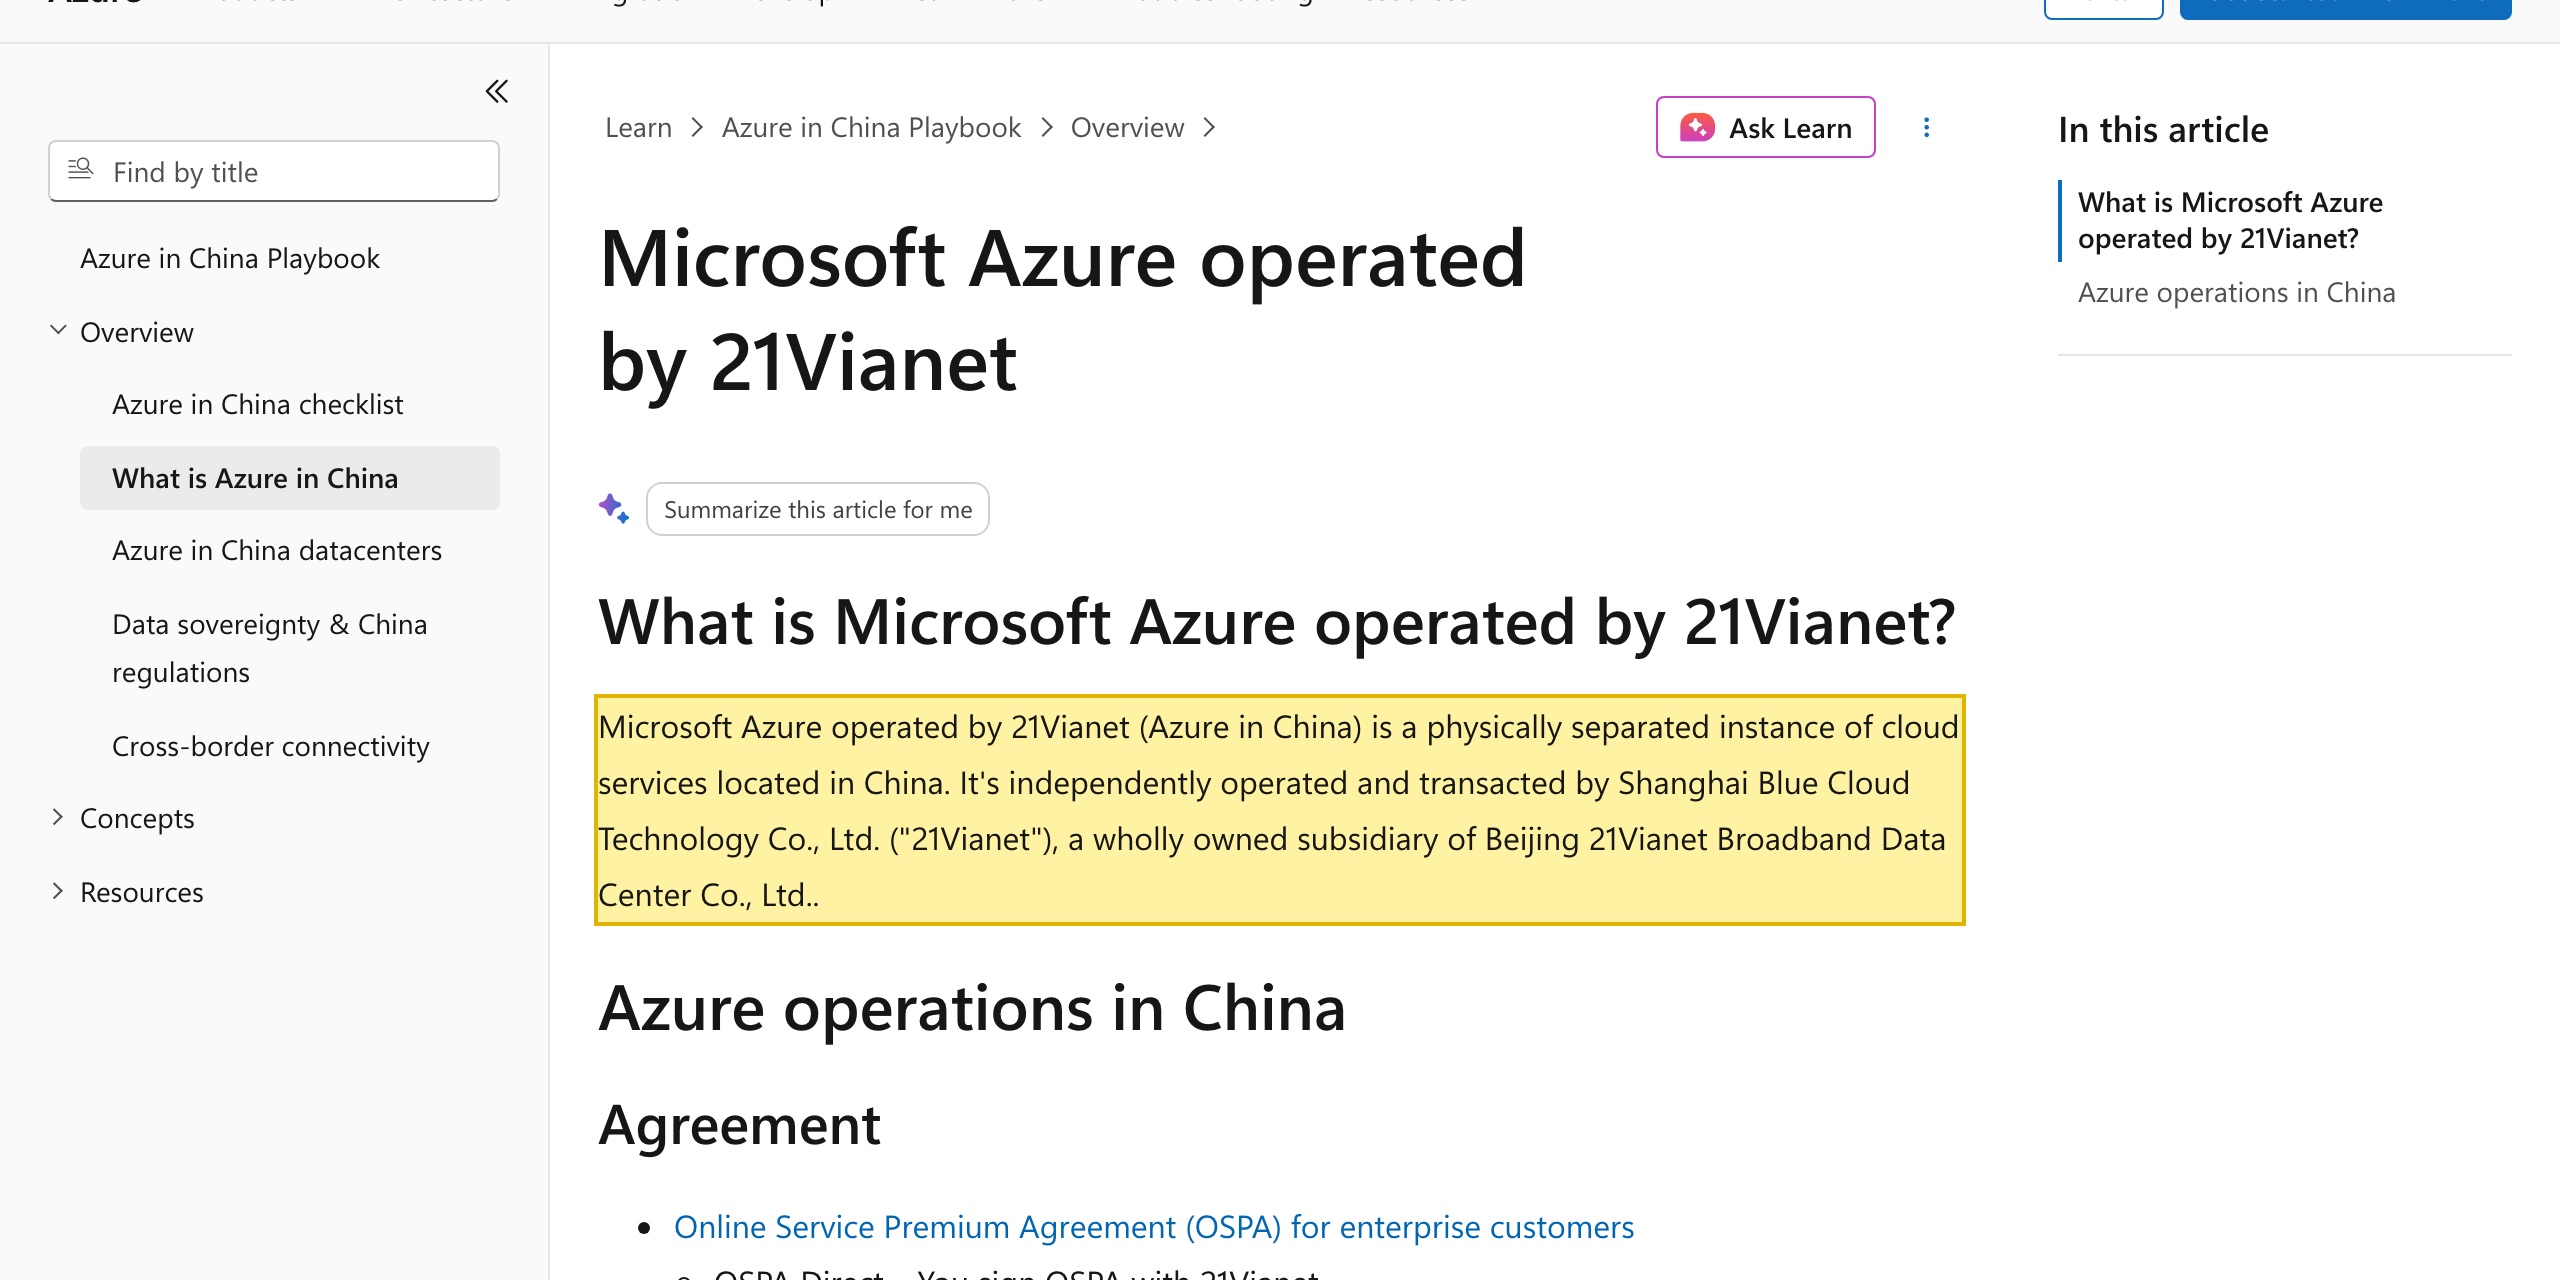
Microsoft describes Azure in China as "a physically separated instance of cloud services located in China," "independently operated and transacted by Shanghai Blue Cloud Technology Co., Ltd. ('21Vianet')." It is a different cloud with a different operator (21Vianet, not Microsoft), a different portal (portal.azure.cn), a China legal entity to sign up, and an ICP filing to host a public site — Microsoft's own China checklist lists every one of these. Keep serving China from your global Azure subscription instead and your users' data stays offshore: a cross-border transfer PIPL governs, on infrastructure that can't be ICP-filed. The table below is Microsoft's own wording and the rule each door triggers.
This is a risk map, not a verdict — which door fits turns on your entity, your data and who your users are. Our China team can map your exposure and the filing path with you →
What Microsoft Azure's own documentation says about China
| Fact | Primary source |
|---|---|
Azure in China is a separate cloud, not a region of your global subscription. Microsoft describes it as "a physically separated instance of cloud services located in China," "independently operated and transacted by Shanghai Blue Cloud Technology Co., Ltd. ('21Vianet'), a wholly owned subsidiary of Beijing 21Vianet Broadband Data Center Co., Ltd." The operator is 21Vianet, not Microsoft, and it runs on its own portal, portal.azure.cn, distinct from global portal.azure.com. | Microsoft Learn — Microsoft Azure in China (overview-operations) and Azure in China checklist (overview-checklist), retrieved 2026-10-07 |
| Microsoft flags the gap at signup. Its China checklist warns that "if you already purchased the Azure global service, please be aware that there are some differences between Azure global and Azure in China," and lists commercial-customer eligibility as a "Legal entity in China" for Azure in China versus "Any organization" for global Azure. A Chinese legal entity is a precondition of the account, not a later step. | Microsoft Learn — Azure in China checklist (overview-checklist), retrieved 2026-10-07 |
| Hosting a public site on Azure in China requires an ICP filing or license. Microsoft's China checklist lists, among the PRC-law obligations customers must follow, an "ICP filing for public non-commercial website," an "ICP license for commercial website," and "public security registration for public website" — the ICP regime under State Council Order No. 292 and MIIT Order No. 33. How ICP filing works → | Microsoft Learn — Azure in China checklist (overview-checklist), retrieved 2026-10-07; State Council Order No. 292; MIIT Order No. 33 |
| On global Azure, your China data stays offshore. Your global Azure subscription (operated by Microsoft) has no mainland-China region to deploy into; the only Azure regions physically in the mainland belong to the separate 21Vianet instance. Serving China from a global region is therefore a cross-border transfer under PIPL (notice, separate consent and a transfer mechanism, Articles 38–43), and Microsoft's own checklist notes the "China Cybersecurity Law states that PII and important data of CII operator must be stored domestically" (Cybersecurity Law Article 39 (formerly Article 37); PIPL Article 40) — which an offshore region cannot satisfy. | Microsoft Learn — Azure in China checklist (overview-checklist), retrieved 2026-10-07; PIPL Articles 38–43 and 40; Cybersecurity Law Article 39 (formerly Article 37) |
Sources verified by the 21YunBox compliance team on 2026-10-07.
Whether Azure “works” in mainland China is a licensing-and-data question before it is a performance one. Azure does run inside the mainland — but not as part of the global subscription most teams already hold. It runs there as a wholly separate cloud, “Microsoft Azure operated by 21Vianet,” reached through a Chinese legal entity, a separate account on a separate portal, and an ICP filing; meanwhile a global Azure stack that serves China keeps your users’ data offshore. Those are the two doors, and Microsoft documents both in its own words.
Azure in China at a glance
| What decides it | In Microsoft's own terms |
|---|---|
| Where it runs | Global Azure's regions all sit outside mainland China. Azure runs in-country only as the instance Microsoft calls “a physically separated instance of cloud services located in China” — the China North / China North 2 / China North 3 regions, which belong to that instance, not to your global account. |
| Who operates it | 21Vianet, not Microsoft: “independently operated and transacted by Shanghai Blue Cloud Technology Co., Ltd. (‘21Vianet’), a wholly owned subsidiary of Beijing 21Vianet Broadband Data Center Co., Ltd.” |
| Separate account & portal | A different cloud with a different sign-in — azure.cn and portal.azure.cn, apart from global azure.microsoft.com and portal.azure.com. Microsoft warns of “differences between Azure global and Azure in China.” |
| Entity required | Commercial eligibility for Azure in China is a “Legal entity in China,” versus “Any organization” for global Azure. |
| Serving the public | Microsoft's checklist lists an “ICP filing for public non-commercial website,” an “ICP license for commercial website,” and “public security registration for public website.” |
| Your data on global Azure | Personal information of your China users stays outside the mainland — a cross-border transfer PIPL governs, on infrastructure that cannot be ICP-filed. |
Door one — Azure in China is a separate, 21Vianet-operated instance
Azure does run inside mainland China, but not as a region of the subscription you already have. Microsoft calls it “a physically separated instance of cloud services located in China,” one that is “independently operated and transacted by Shanghai Blue Cloud Technology Co., Ltd. (‘21Vianet’), a wholly owned subsidiary of Beijing 21Vianet Broadband Data Center Co., Ltd.” The operator is 21Vianet, not Microsoft; it has its own marketing site and management portal — azure.cn and portal.azure.cn — separate from the global azure.microsoft.com and portal.azure.com. Microsoft puts the warning up front: “if you already purchased the Azure global service, please be aware that there are some differences between Azure global and Azure in China,” and the first difference it lists is eligibility — a commercial customer must be a “Legal entity in China,” where global Azure takes “any organization.”
Serving a public-facing site from inside the mainland then turns on an ICP filing. Microsoft’s own China checklist lists, as obligations customers must follow under PRC law, an “ICP filing for public non-commercial website,” an “ICP license for commercial website,” and “public security registration for public website.” So “we’re already on Azure” does not carry into China: the in-country door is a Chinese entity, a separate 21Vianet account, and an ICP filing — the regime under State Council Order No. 292 and MIIT Order No. 33.
Door two — global Azure keeps your China data offshore
Keep serving China from your global Azure subscription instead, and two facts follow. First, that subscription has no mainland-China region to deploy into: the Azure regions physically inside the mainland belong to the 21Vianet instance, not to your global, Microsoft-operated account, so there is nothing on global Azure to attach an ICP filing to. Second, your users’ personal information sits in whichever offshore region you chose. Under China’s Personal Information Protection Law that is a cross-border transfer: the handler — you, not Microsoft — must give notice, obtain separate consent, and satisfy one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification). Microsoft’s checklist flags the residency duty in the same breath, noting the “China Cybersecurity Law states that PII and important data of CII operator must be stored domestically” (Cybersecurity Law Article 39 (formerly Article 37); PIPL Article 40) — which an offshore region cannot do, and an offshore endpoint cannot be ICP-filed.
This is a risk map, not a verdict: which door fits turns on your entity, your data and who your users are, and it is worth confirming with counsel.
Where 21YunBox fits — a compliant overlay, not a migration
You keep building on Azure — global or the 21Vianet instance. We add the piece Azure leaves you to arrange yourself: compliant, ICP-filed delivery from inside the mainland, placed in front of your existing Azure origin — no rebuild, no second codebase, and no forced move between clouds. Our China team maps which door fits, assesses your PIPL cross-border and data-residency exposure for your entity and data volumes, and stands up the in-country delivery and storage a compliant China presence requires.
Related reading: