Does Smile.io Work in China? Loyalty Data, PIPL & Where It's Stored
Smile.io runs no region inside mainland China — its own privacy policy says customer data is stored in Canada and the United States. Running a loyalty program for your Chinese shoppers ships their personal data offshore, a PIPL cross-border transfer. A compliance-first look at the data-residency door.
Does Smile.io work in China?
Smile.io loads for mainland shoppers, but that was never the compliance question. Run a loyalty program for your Chinese customers and their personal data — names, emails, birthdays, order history — lands on servers in Canada and the United States, which Smile confirms in its own privacy policy. The exposure isn't whether it works; it's that it's an offshore transfer of personal information.
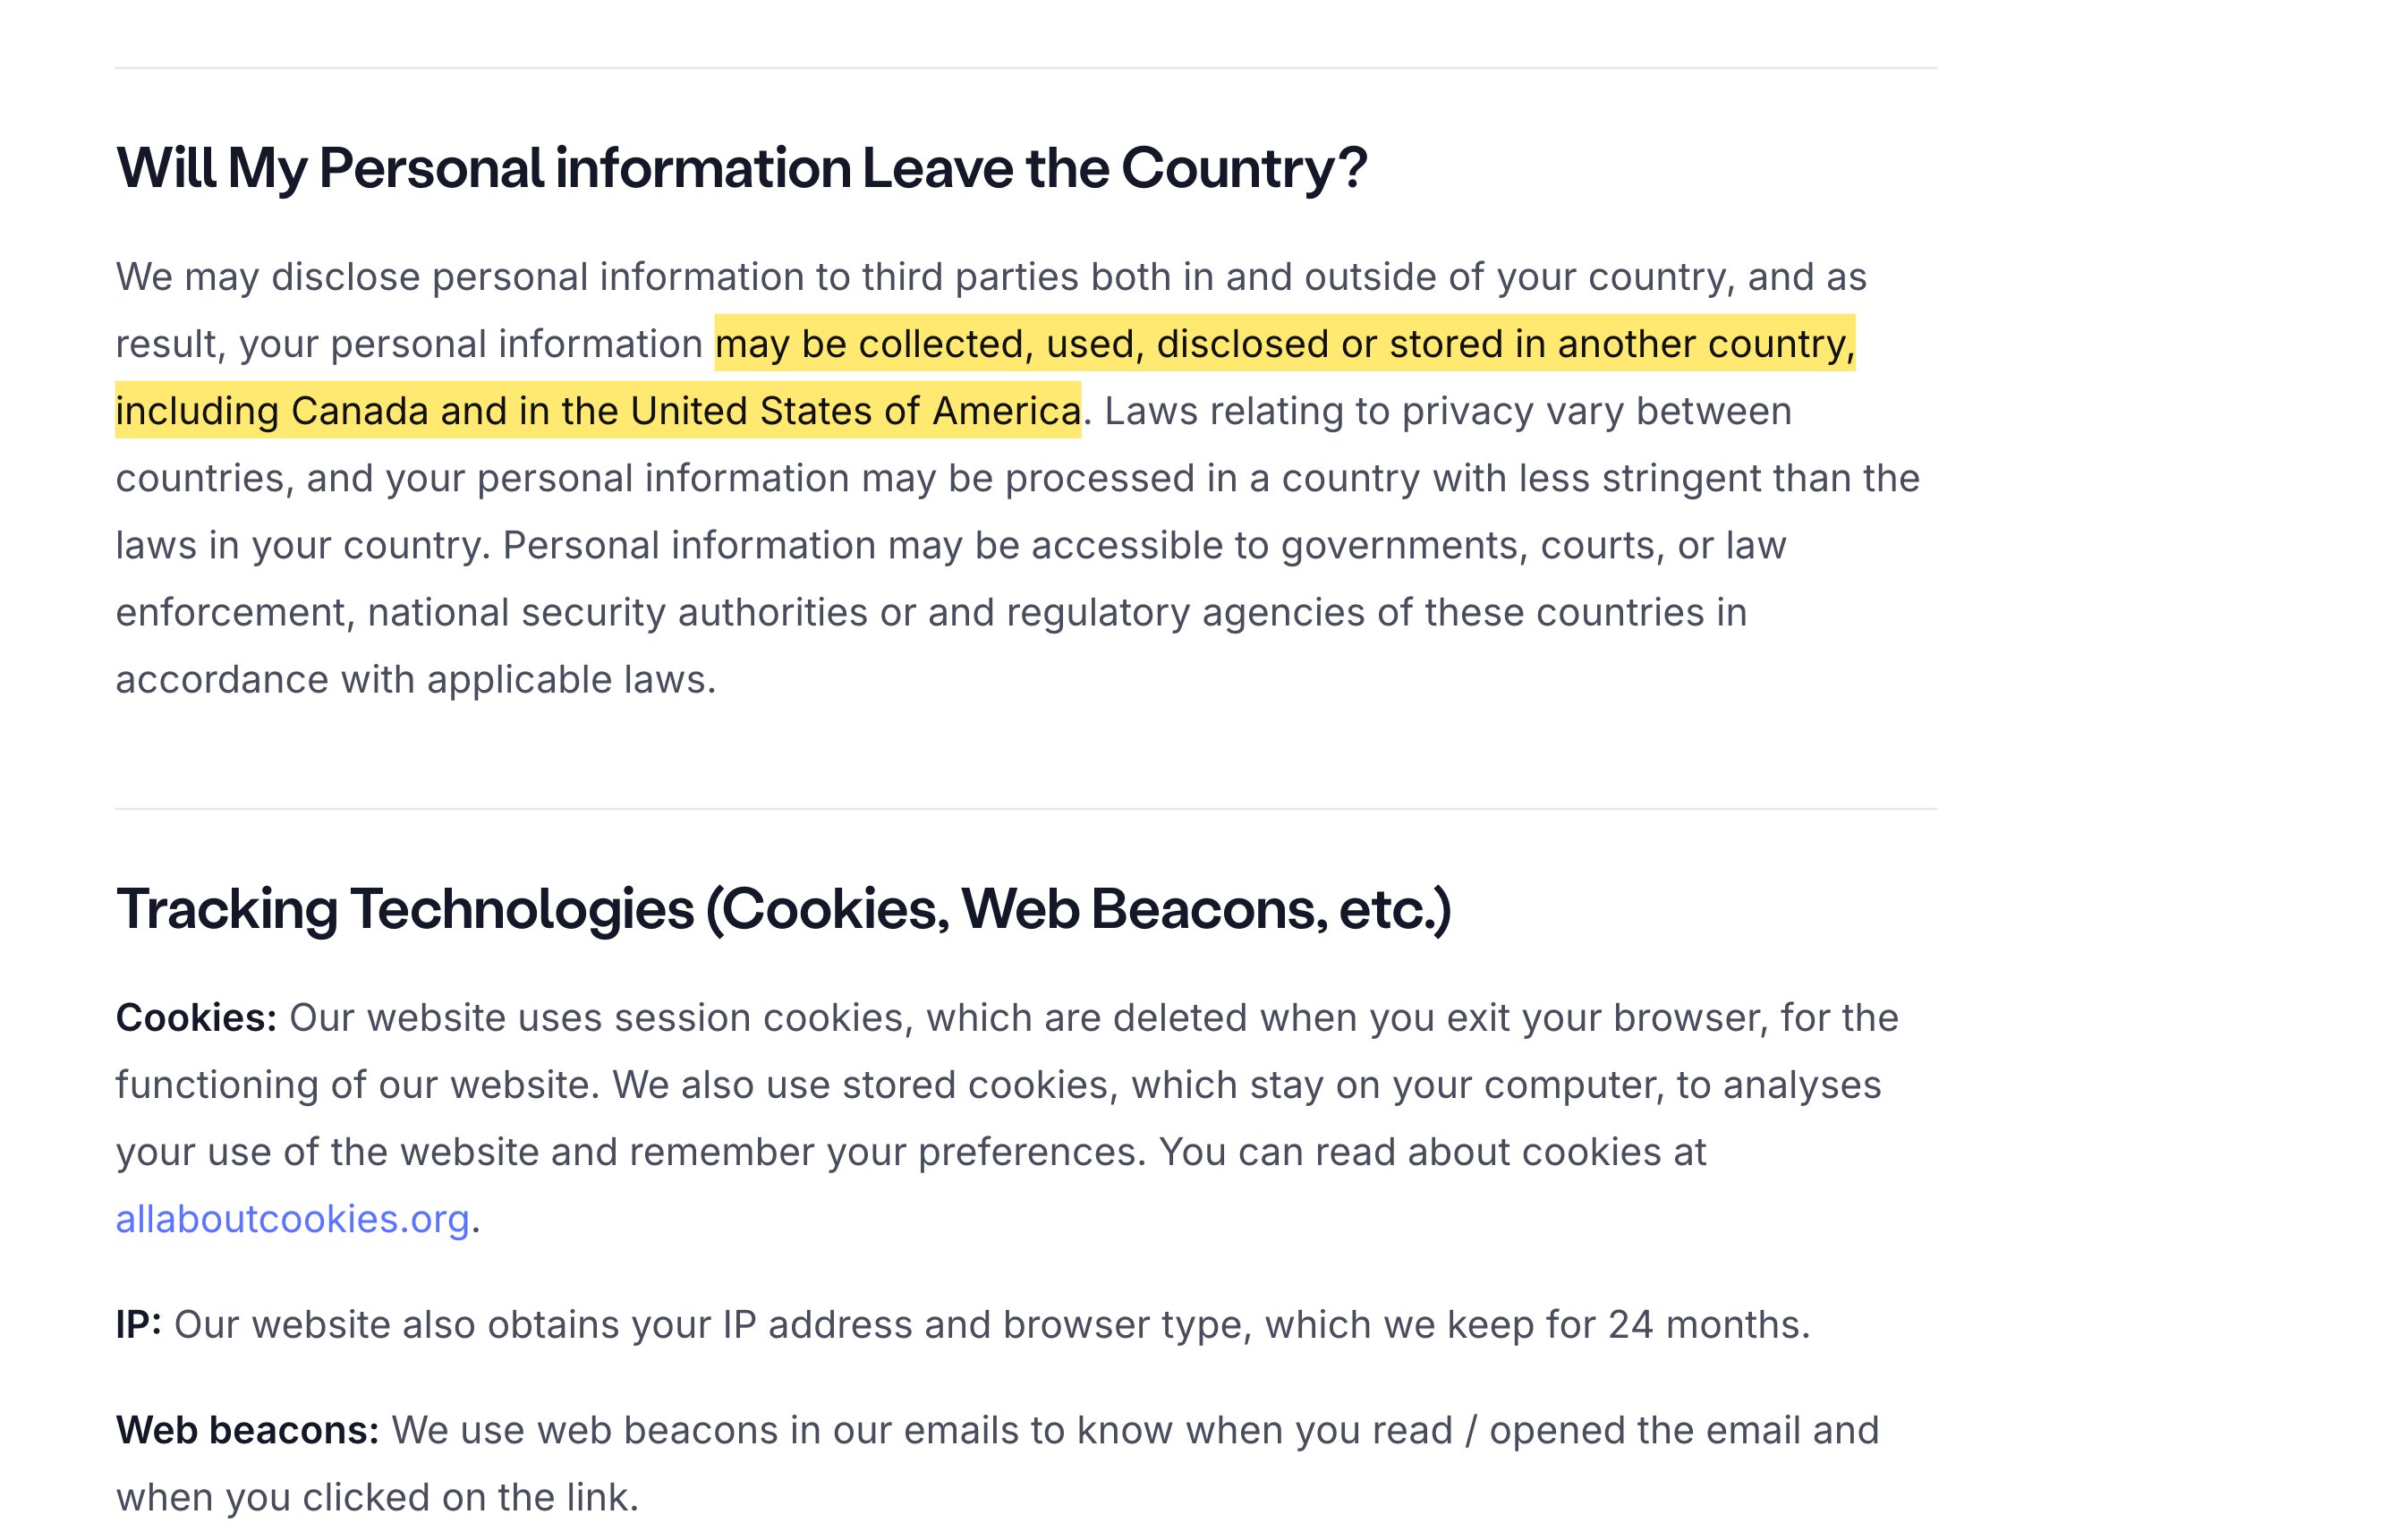
Smile's policy states your personal information "may be collected, used, disclosed or stored in another country, including Canada and in the United States of America," may be "processed in a country with less stringent than the laws in your country," and may be "accessible to governments, courts, or law enforcement." For your mainland customers, that offshore storage is a cross-border transfer PIPL governs — notice, separate consent and a transfer mechanism — and Smile runs no mainland-China region to keep the data in-country. The table below is Smile's own wording and the rule each line triggers.
This is a risk map, not a verdict — whether a localization duty also applies turns on your role and data volumes, worth settling with counsel. Our China team can map your loyalty-data exposure with you →
Compliance snapshot
- ! Smile stores your loyalty data in Canada and the United States
- ✕ Serving mainland shoppers sends their personal data offshore — PIPL cross-border
- ! Names, emails, birthdays and order history are personal information
- ! No mainland region, so in-country data residency isn't an option on Smile
- ✓ Smile isn't blocked in China — reachability isn't the compliance gap
What Smile.Io's own documentation says about China
| Fact | Primary source |
|---|---|
| Smile stores your customers' loyalty data in Canada and the United States — in its own words. Smile.io's privacy policy states that your personal information "may be collected, used, disclosed or stored in another country, including Canada and in the United States of America." Both sit offshore from the mainland, and Smile publishes no mainland-China region — so a loyalty program run for Chinese shoppers keeps their data outside China, a cross-border transfer under PIPL. | Smile.io Privacy Policy (smile.io/privacy-policy), retrieved 2026-10-07 |
| The loyalty data Smile holds is personal information. Smile's own data-collection documentation lists what it stores per shopper: customer first and last name, customer email, "Customer Date of Birth, if provided," and "Customer Transactional Data (order data)." Names, contact details, birthdays and purchase history identify and profile individuals — personal information under China's Personal Information Protection Law, not anonymous analytics. | Smile.io Help — Privacy and data collection, retrieved 2026-10-07 |
| Moving that data offshore is exactly what PIPL regulates. Smile's policy warns the data may be "processed in a country with less stringent than the laws in your country" and may be "accessible to governments, courts, or law enforcement." For a mainland handler, sending personal information abroad is a cross-border transfer requiring notice, separate consent and a transfer mechanism (PIPL Articles 38–43); and for a critical information infrastructure operator or large-volume handler, China-collected personal information must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — which an offshore-only service cannot do. | Smile.io Privacy Policy, retrieved 2026-10-07; PIPL Articles 38–43 & 40; Cybersecurity Law Article 39 (formerly Article 37) |
| ICP is your storefront's question, not the app's — and reachability isn't the gap. Smile runs as an app inside your e-commerce platform; its own docs tie each record to "your eCommerce platform." The ICP filing a public mainland site needs attaches to that storefront layer, not to Smile — so don't let an ICP checkbox hide the real exposure. Smile isn't blocked in China either; its on-store widget loads from offshore, but loading is not the same as lawful. The live question is where the loyalty data lives. | Smile.io Help — Privacy and data collection, retrieved 2026-10-07; State Council Order No. 292; MIIT Order No. 33 |
Sources verified by the 21YunBox compliance team on 2026-10-07.
For a mainland-China audience, the deciding question about Smile.io is not whether its rewards widget paints on screen — it is where the data behind your points, referrals and VIP tiers is allowed to live. Smile answers that in its own privacy policy: the personal information it holds for each shopper is stored offshore, in Canada and the United States, and Smile runs no region inside mainland China. The widget is reachable; the exposure is that running a loyalty program for Chinese customers moves their personal information across the border, into jurisdictions China’s law treats as foreign. Reachability is the easy half. Where the data sits is the half that decides whether you may use it as-is.
Smile.io in China at a glance
| What decides it | In Smile's own terms |
|---|---|
| Where your data lives | Smile's privacy policy says personal information “may be collected, used, disclosed or stored in another country, including Canada and in the United States of America.” No region sits inside mainland China. |
| What it collects | Per shopper: first and last name, email, “Customer Date of Birth, if provided,” and “Customer Transactional Data (order data)” — personal information, not anonymous metrics. |
| Crossing the border | Running the program for mainland customers moves that personal information offshore — a cross-border transfer PIPL governs, with notice, separate consent and a transfer mechanism. |
| Data residency | For a CIIO or large-volume handler, China-collected personal information must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — a duty an offshore-only service cannot meet. |
| ICP & reachability | ICP attaches to your storefront, not to the Smile app; Smile isn't blocked in China. Loading is the easy half — lawful handling is the half that decides it. |
Smile stores your loyalty data offshore — and says so plainly
Smile does not keep your program’s data in mainland China, and it is candid about where it does keep it. Its privacy policy states that your personal information “may be collected, used, disclosed or stored in another country, including Canada and in the United States of America,” that it “may be processed in a country with less stringent than the laws in your country,” and that it may be “accessible to governments, courts, or law enforcement.” Those are Smile’s words, not an inference — and both named countries are outside the mainland.
That geography is what turns a routine integration into a compliance question. The handler of your Chinese shoppers’ personal information is you, not Smile; when Smile stores that information in Canada or the United States on your behalf, you are the party sending it abroad. “Our loyalty app already works” does not settle it, because reaching a shopper and lawfully holding that shopper’s data are two different tests, and only the second is decided by where Smile’s servers sit.
The rewards data is personal information, so moving it is a transfer PIPL governs
A loyalty program is built from exactly the data China’s law protects. Smile’s own data-collection documentation lists what it stores for each customer: first and last name, email address, “Customer Date of Birth, if provided,” and “Customer Transactional Data (order data).” Points balances, referrals and VIP tiers are layered on top of those identifiers. None of that is anonymous telemetry — it names, contacts and profiles individual people, which is personal information under China’s Personal Information Protection Law.
Because that information is collected from mainland users and stored offshore, PIPL treats the flow as a cross-border transfer: the handler must give notice, obtain separate consent, and clear one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification (Articles 38–43). And if you are a critical information infrastructure operator or a large-volume handler, personal information collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — a residency duty a service that runs only in Canada and the United States has no way to satisfy.
Reachability isn’t the question — and ICP isn’t Smile’s door
Smile is not blocked in China. Its on-store widget loads from offshore, and because it loads from offshore it can be slower or less dependable than an asset served from inside the mainland — but a widget that paints is still a widget whose data lives in another country. Loading is not the same as lawful, and the compliance exposure is unchanged by how quickly the points balance appears.
It is just as important not to invent a door that isn’t there. Smile runs as an app inside your storefront, and its own records are tied to “your eCommerce platform.” The ICP filing a public-facing mainland site requires (State Council Order No. 292; MIIT Order No. 33) belongs to that storefront layer, not to the Smile app — so Smile does not need its own ICP, and treating it as if it did would point the assessment at the wrong risk. On Smile the live question is singular and narrow: where the loyalty data is collected and stored.
This is a risk map, not a verdict — whether you owe a cross-border mechanism, in-country storage, or both depends on what you collect, how much of it you hold, and who your users are, and it is worth settling with counsel before you build.
Where 21YunBox fits — a compliant overlay, not a migration
Smile stays on your storefront, exactly as it runs today — points, referrals and VIP tiers keep working, and you move nothing. What we add is the piece an offshore loyalty app cannot supply on its own: ICP-filed delivery from inside the mainland, placed in front of your existing origin, with no rebuild and no second codebase to maintain. Our China team works through your PIPL cross-border and data-residency position for your entity, your data volumes and your users, then stands up the in-country delivery and lawful data handling a compliant mainland presence calls for — while your storefront and Smile stay precisely where they already are.
Related reading:
Frequently Asked Questions
Does using Smile.io for Chinese customers comply with PIPL?
Treat it as a risk to assess with counsel, not a flat yes or no. Smile stores customer data in Canada and the United States — its own words — so running a loyalty program for mainland shoppers sends their personal information offshore, which PIPL governs as a cross-border transfer: you owe notice, separate consent and one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification). Whether a data-localization duty also applies turns on your role — for example a critical information infrastructure operator — and your data volumes.
Does Smile.io itself need an ICP filing for China?
No — and it matters not to force that door. Smile is an app that runs inside your storefront; the ICP filing a public-facing mainland site requires attaches to the storefront layer, not to the Smile app. On Smile, the exposure isn't ICP — it's data residency: where your customers' loyalty data is collected and stored. Keeping the ICP and data-transfer questions separate is what keeps the assessment honest.
Can 21YunBox help run a compliant loyalty program for China?
Yes. Our China team can map your PIPL cross-border and data-residency exposure for your entity, data volumes and users, and stand up the ICP-filed, in-country delivery a compliant China presence needs — set in front of the storefront and Smile stack you already run, with no rebuild. Get in touch to work through your specific case.