Does Builder.io Work in China? Content Delivery, ICP & the PIPL Line
Builder.io is a headless visual CMS that serves your content and page designs from an offshore CDN edge (Google Cloud, AWS CloudFront and Fastly) with no mainland-China point of presence, so fetching it live from inside China is a delivery risk — while the ICP filing and PIPL duties that decide legality sit on the site that embeds Builder.io, not on the CMS. An honest, compliance-first look.
Does Builder.io work in China?
It depends which half of the question you mean, and the two halves answer differently. Builder.io is reachable from mainland China, but it serves your content and designs from an offshore CDN edge — so the honest Builder.io-level risk is reliable delivery, not data residency. The ICP filing and PIPL duties that actually decide legality sit on the site that embeds Builder.io, not on the CMS.
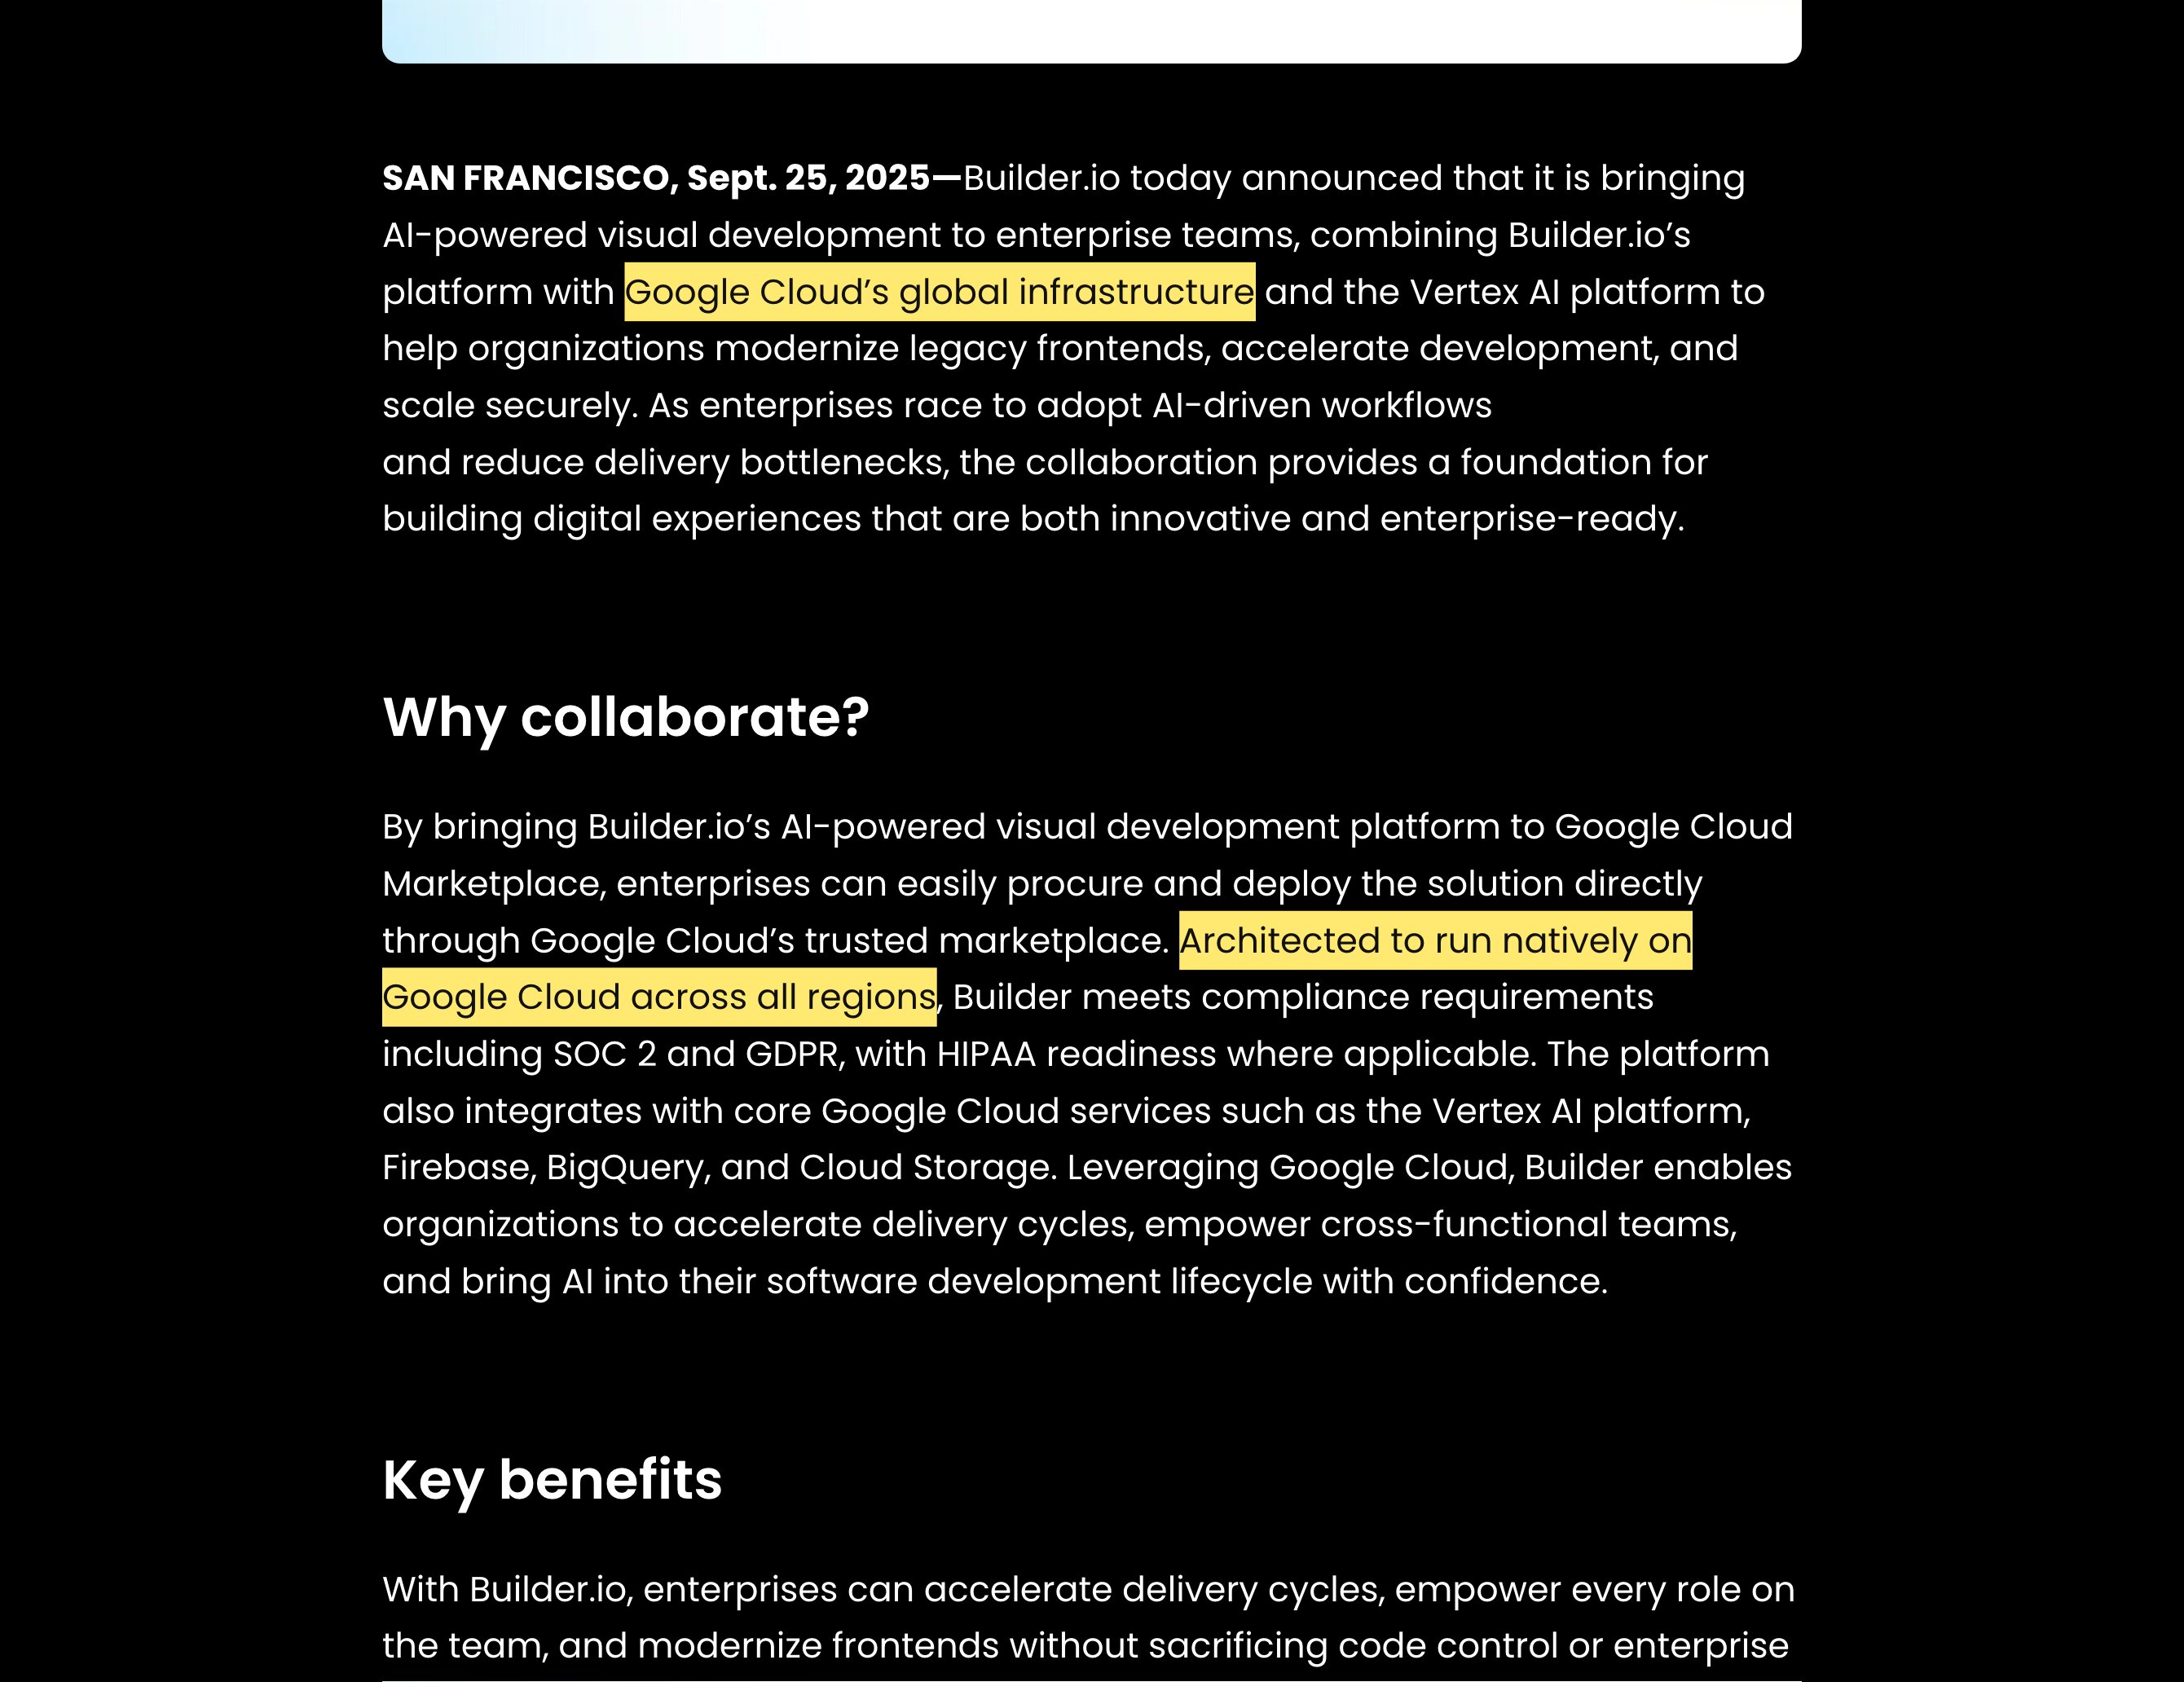
Builder.io's own documentation says "Builder Content serves content from the CDN edge cache while revalidating in the background," served from the cdn.builder.io content endpoint, and Builder describes that stack as "AWS CloudFront as our CDN" with "Fastly as a secondary caching layer," on a platform "Architected to run natively on Google Cloud across all regions" — none of it serving the mainland from inside it. So a page that fetches content at request time crosses the border on every call: a reachability risk, but not by itself a cross-border transfer of your users' personal information, because the payload is your own editorial content and designs. The duties that do decide legality — an ICP filing on in-country hosting, and PIPL for whatever personal data your site collects — attach to your embedding site, not to Builder.io. The table below is Builder.io's own wording and the line each fact sits on.
This is a risk map, not a verdict — which duties apply turns on how your site is hosted, what it collects and who your users are. Our China team can map your exposure with you →
Compliance snapshot
- ! Builder.io's content CDN is offshore — reachable, but every fetch crosses the border
- ✓ The payload is your own content and designs, not your users' personal data
- ✕ A public site served from outside the mainland can't be ICP-filed
- ! The ICP filing and PIPL duties sit on your embedding site, not the CMS
- ! Put personal data in a Builder field and it leaves the mainland on every fetch
What Builder.Io's own documentation says about China
| Fact | Primary source |
|---|---|
Builder.io is a headless, visual CMS: your site fetches its content from Builder's CDN edge at request time. Builder's Content API documentation states that "Builder Content serves content from the CDN edge cache while revalidating in the background," with your front end calling the https://cdn.builder.io/api/v3/content/ endpoint for each model. That is the delivery model — and it is the half of "does it work in China" that turns on reachability, not on law. | Builder.io — Content API documentation (builder.io/c/docs/content-api), retrieved 2026-10-07 |
| That CDN edge is entirely offshore, with no point of presence inside mainland China. Builder.io's own staff describe the delivery stack as "AWS CloudFront as our CDN" with "Fastly as a secondary caching layer," storing images on "a US-based Google Cloud Platform Bucket," and Builder's 2025 newsroom says the platform is "Architected to run natively on Google Cloud across all regions" on "Google Cloud's global infrastructure." Google Cloud runs no mainland-China region, and neither CloudFront's nor Fastly's standard global network serves the mainland from inside it — so a fetch made from behind the Great Firewall travels out and back. It is a delivery risk, not a block. | Builder.io — Google Cloud Marketplace announcement (builder.io/news/google-cloud-marketplace) & official community forum (forum.builder.io), retrieved 2026-10-07 |
| By itself, Builder.io is not a cross-border transfer of your users' data. What Builder stores and serves is your own editorial content and page designs — the material your team authors for public display — not the personal information of the people who view it. Moving that through Builder's US-based Google Cloud and AWS infrastructure does not, on its own, create a cross-border transfer of user data under PIPL (Articles 38–43). The one exception is self-inflicted: model personal data as content inside a Builder field, and it leaves the mainland with every fetch like any other payload. | Builder.io — Content API documentation (builder.io/c/docs/content-api), retrieved 2026-10-07; PIPL Articles 38–43 |
| The duties that decide legality sit on the site that embeds Builder.io, not on the CMS. A public site shown to mainland visitors needs an ICP filing (ICP 备案) on in-country hosting under State Council Order No. 292 and MIIT Order No. 33 — decided by where your HTML and origin are served from, not where your CMS lives. Separately, any personal information your site collects is your own PIPL responsibility as the handler: notice, separate consent and a transfer mechanism if it goes offshore (Articles 38–43), and in-country storage for a critical information infrastructure operator or large-volume handler (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). | State Council Order No. 292; MIIT Order No. 33; PIPL Articles 38–43 & 40; Cybersecurity Law Article 39 (formerly Article 37) (Cyberspace Administration of China), retrieved 2026-10-07 |
Sources verified by the 21YunBox compliance team on 2026-10-07.
For a mainland-China audience, “does Builder.io work” is really two questions wearing one coat, and keeping them apart is what makes the answer useful. Builder.io is a headless, visual CMS: it stores your content and your page designs and hands them to your site through a content API served from its own CDN edge. That edge runs on offshore infrastructure with no point of presence inside mainland China, so the honest Builder.io-level risk is reachability — a site that pulls its content live from behind the Great Firewall can be slow or unreliable. What Builder.io does not do, on its own, is turn your project into a data-residency problem, because what it carries is the material you publish, not the personal information of the people who read it. The filing and privacy duties that actually decide whether your China-facing site is lawful sit on the site that embeds Builder.io — and separating those from the delivery question is the entire job of this page.
Builder.io in China at a glance
| What decides it | In Builder.io's own terms |
|---|---|
| Where it runs | Builder's platform is “Architected to run natively on Google Cloud across all regions” on “Google Cloud's global infrastructure,” and its content stack uses “AWS CloudFront as our CDN” with “Fastly as a secondary caching layer.” None of those networks runs inside mainland China. |
| How your site gets content | Your front end queries Builder's Content API on the cdn.builder.io host at request time; “Builder Content serves content from the CDN edge cache.” With no mainland point of presence, each fetch crosses the border. |
| What's in the payload | Your own content and page designs — pages, layouts, copy, images — authored for public display, not your end users' personal information. By itself that is generally not a PIPL cross-border transfer of user data. |
| Serving the public | The public site that embeds Builder.io and is shown to mainland visitors needs an ICP filing on in-country hosting. That duty belongs to the site and its host, not to the CMS. |
| The edge case | Model personal data as content inside Builder and it leaves the mainland with every fetch — and PIPL's cross-border rules attach to it like any other payload. |
Reachability is the honest Builder.io-level question
Builder.io is open about how your content travels. Its Content API documentation says that “Builder Content serves content from the CDN edge cache while revalidating in the background,” with your front end calling the cdn.builder.io content endpoint for each model you request. Where that edge physically sits is the whole reachability story: Builder’s own staff describe the delivery stack as “AWS CloudFront as our CDN” with “Fastly as a secondary caching layer,” storing images on “a US-based Google Cloud Platform Bucket,” and Builder’s 2025 newsroom says the platform is “Architected to run natively on Google Cloud across all regions” on “Google Cloud’s global infrastructure.” Every one of those networks serves the mainland from the far side of the border — none runs a point of presence inside it — so a request made in Beijing or Guangzhou has to leave the country and come back to reach Builder’s edge. That round trip, and the filtering along the way, is where the slow renders and the occasional failed fetch come from. It is a genuine delivery risk, and it is also the half of the question network design can actually fix. Read it as reachability, not as a ruling on legality.
A visual CMS is not, by itself, a data-residency problem
It is easy to see “our CMS runs on US infrastructure” and reach straight for the cross-border-data alarm. For a content-and-design CMS, that is usually the wrong instrument. What Builder.io keeps and ships is the material your team builds for the public — marketing pages, layouts, copy, images, reusable design blocks — not the personal information of the people who view them. Moving that through Builder’s Google Cloud and AWS backend does not, in itself, amount to a cross-border transfer of user data under PIPL. Saying so plainly matters: inflate a visual CMS into a data-residency breach and you manufacture an obligation it never triggered, while the duties that are real drift out of view.
There is a single edge worth watching. Builder.io will store whatever you choose to model as content, so the moment you drop personal data — a user profile, a form entry, anything that identifies a real person — into a Builder field, that record now crosses the border with every fetch, exactly like a landing page, and PIPL’s cross-border rules (Articles 38–43) fasten onto it. The discipline is simple: keep Builder.io for content and design, keep personal data in systems you control, and the residency question never lands on the CMS.
The compliance doors live on your site, not the builder
The obligations that decide whether your China-facing site is lawful do not rest on Builder.io; they rest on the website that embeds it. A public site shown to mainland visitors needs an ICP filing (ICP 备案) under State Council Order No. 292 and MIIT Order No. 33, and that filing must bind to hosting physically inside the mainland. What settles it is where your HTML and your origin are served from — not where your CMS lives — so a front end assembled in Builder.io still needs its own in-country, ICP-filed hosting to run cleanly for Chinese users. Separately, any personal information your site collects from those users — sign-ups, orders, support requests — is yours to answer for as the handler: notice, separate consent and a transfer mechanism if that data goes offshore (Articles 38–43), and in-country storage if you are a critical information infrastructure operator or a high-volume handler (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). None of that is Builder.io’s to carry, and none of it is solved by making your pages arrive faster.
This is a risk map, not a verdict: whether your site needs an ICP filing, in-country storage, or simply a steadier way to reach Builder.io turns on how you host it, what personal data it collects, and who your users are — worth settling with counsel before you build.
Where 21YunBox fits — a compliant overlay, not a migration
You keep building in Builder.io, exactly as you do today. What we add is the piece an offshore content API cannot: compliant, ICP-filed delivery from inside the mainland, placed in front of your existing origin so your pages reach Chinese users without waiting on a cross-border round trip to Builder’s edge — no rebuild, no second codebase, and no change to your Builder.io workflow. Our China team takes the two halves one at a time: how reliably your content arrives, and the ICP and PIPL duties that sit on your embedding site, weighed against your entity, your hosting and the personal data your site actually collects. Builder.io stays your CMS; the compliant China presence is built around it.
Related reading:
Frequently Asked Questions
Is Builder.io blocked in mainland China, or just slow?
It is a reachability problem, not a block. Builder.io serves your content from an offshore CDN edge — CloudFront, Fastly and Google Cloud — with no point of presence inside mainland China, so a page that fetches content live from behind the Great Firewall has to make a cross-border round trip, which shows up as slow renders and the occasional failed load rather than an outright ban. That is the half of the question network design can address, and it is separate from whether you are cleared to operate — which is a licensing and privacy question, not a speed one.
Does putting our site on Builder.io move our users' personal data out of China?
Generally not on its own. Builder.io stores and delivers your editorial content and designs, not the personal information of the people who read them, so using it is not by itself a cross-border transfer of user data under PIPL. The exception is if you model personal data as content inside a Builder field — then it crosses the border on every fetch like any other payload. The personal data that does carry PIPL duties is whatever your own site collects — accounts, forms, orders — wherever you process it.
Can 21YunBox help make our Builder.io site work in mainland China?
Yes. Our China team separates the two halves for you — the reachability of your Builder.io content, and the ICP filing and PIPL duties that sit on your embedding site — then stands up compliant, ICP-filed, in-country delivery in front of your existing origin, with your Builder.io workflow left exactly as it is. Get in touch to work through your specific setup.