Does MailerLite Work in China? PIPL, Subscriber Data & ICP
MailerLite stores your subscribers' personal data in the European Union and runs no mainland-China region, so using it for people in China is a PIPL cross-border transfer — and where you embed its forms, the ICP filing sits on your site, not on MailerLite. A compliance-first look at the real exposure.
Does MailerLite work in China?
Yes — MailerLite is reachable and you can run it for a China audience, but it stores your subscribers' personal data in the European Union and operates no mainland-China region, so using it for people in China is a PIPL cross-border-transfer question before it is anything else.
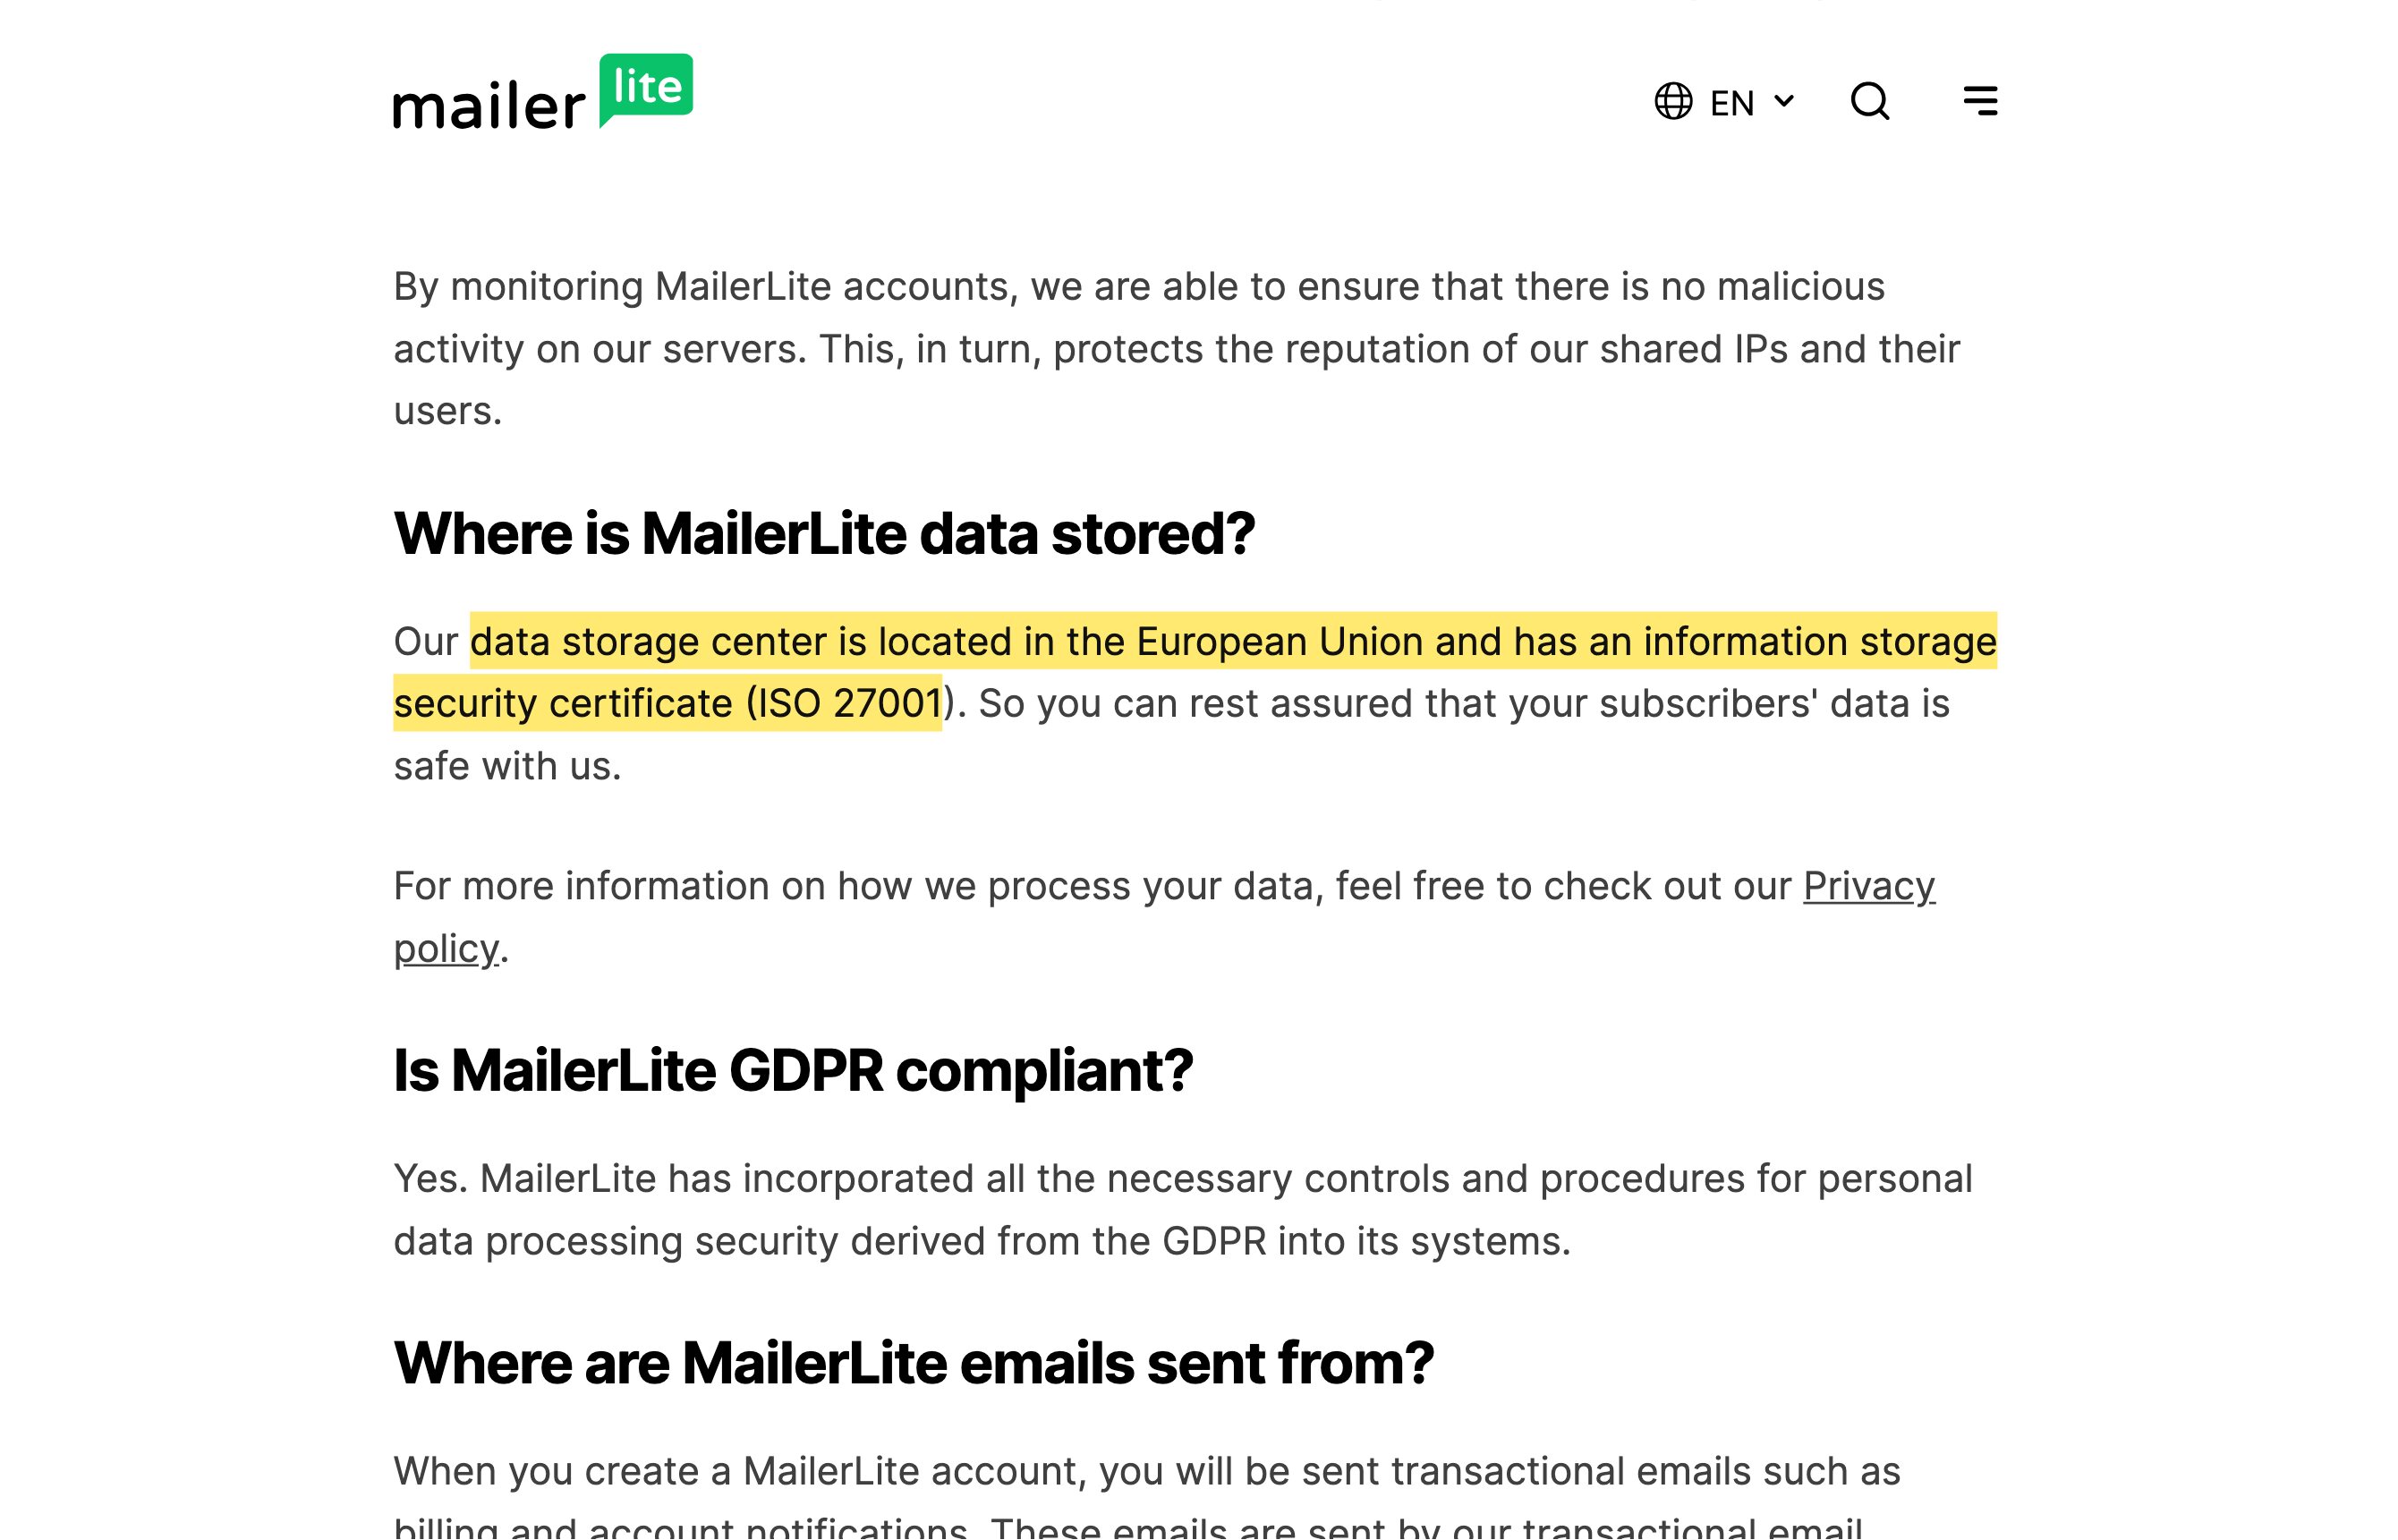
MailerLite's privacy policy opens, "We process Personal Data as a Processor on behalf of the Customer," and its help center states its "data storage center is located in the European Union." That makes you — not MailerLite — the handler the law looks to, and it puts every China subscriber's email address, IP and engagement data offshore: a cross-border transfer of personal information PIPL governs (notice, separate consent and a transfer mechanism), on infrastructure with no mainland region to localize to. And where you embed MailerLite's forms on a public mainland site, the ICP filing is yours to hold on that site, not something MailerLite carries. The table below is MailerLite's own wording and the rule each point triggers.
This is a risk map, not a verdict — what you must do turns on your entity, your data volumes and who your subscribers are. Our China team can map your exposure with you →
Compliance snapshot
- ! Your subscribers' personal data is stored in the EU, outside the mainland
- ! China subscribers' data leaving the mainland is a PIPL cross-border transfer
- ✕ MailerLite runs no mainland-China region — data can't be kept in-country
- ! You're the controller; MailerLite is only the processor — the duty is yours
- ! ICP filing rides on the site that embeds the form, not on MailerLite
What Mailerlite's own documentation says about China
| Fact | Primary source |
|---|---|
| MailerLite is the processor — the PIPL duty lands on you. In its own privacy policy MailerLite states, "We process Personal Data as a Processor on behalf of the Customer," with "no direct relationship with Customers' Subscribers or any individuals other than our Customers," while its GDPR page casts you as "a data controller." In PIPL terms you are the personal-information handler who must clear the cross-border transfer — MailerLite's processor role does not absorb that obligation. | MailerLite Privacy Policy & GDPR compliance pages (mailerlite.com), retrieved 2026-10-07; PIPL |
| Your subscribers' data is stored in the EU, not the mainland. MailerLite states its "data storage center is located in the European Union and has an information storage security certificate (ISO 27001)," and names no mainland-China region anywhere in its documentation. Serving China from MailerLite therefore holds your subscribers' personal information offshore — a cross-border transfer under PIPL (notice, separate consent and a transfer mechanism, Articles 38–43) — and for a critical information infrastructure operator or large-volume handler the data-localization duty (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) is one an EU-only service cannot meet. | MailerLite — "Is my data safe with MailerLite?" (mailerlite.com), retrieved 2026-10-07; PIPL Articles 38–43 & 40; Cybersecurity Law Article 39 (formerly Article 37) |
| The data at stake is your China subscribers' personal information. MailerLite's policy lists "Subscribers' information: email address and any other additional information that Customer provides to MailerLite," and describes email beacons that "collect information about when you open the email and your IP address," plus reports on "what actions your Subscribers took." Email, IP and engagement data of people in the mainland is personal information under PIPL — which is exactly what makes holding it in the EU a regulated cross-border transfer. | MailerLite Privacy Policy (mailerlite.com), retrieved 2026-10-07; PIPL |
| MailerLite's supply chain points at Europe and the US, never the mainland. MailerLite states "all of our sub-processors are based in the EU," and its US entity "has certified to the Department of Commerce that it adheres to the Data Privacy Framework Principles" for data reaching the United States. Useful for GDPR — but none of it is a China data path: the EU-and-US arrangement that keeps MailerLite GDPR-aligned is precisely what leaves a transfer out of China to be cleared separately under PIPL. | MailerLite GDPR compliance & Privacy Policy (mailerlite.com), retrieved 2026-10-07; PIPL |
| Embedding a MailerLite form does not put your ICP filing on MailerLite. MailerLite builds "embedded signup forms" and a builder to "create custom landing pages with interactive blocks and embedded signup forms" — a tool you drop into your own site, served from its EU infrastructure. A public site shown to mainland visitors needs an ICP filing (ICP 备案, under State Council Order No. 292 and MIIT Order No. 33) bound to that site and its mainland hosting; MailerLite neither carries one nor provides a path to one, and the offshore origin of the embed is a separate delivery consideration. | MailerLite — Email signup forms (mailerlite.com), retrieved 2026-10-07; State Council Order No. 292; MIIT Order No. 33 |
Sources verified by the 21YunBox compliance team on 2026-10-07.
For a mainland-China audience, the deciding question about MailerLite is not how fast it paints — it is whose personal data you are collecting and where the law lets that data live. MailerLite is an email-marketing platform that holds your subscribers’ email addresses, their engagement history and the IP data behind every open and click, and it states in its own documentation that it keeps that data in the European Union while acting only as a processor on your behalf. Point it at an audience in China and you, as the controller, are making a cross-border transfer of personal information — and that, not reachability, is what decides whether you may lawfully use it.
MailerLite in China at a glance
| What decides it | In MailerLite's own terms |
|---|---|
| Where it runs | Data storage center “located in the European Union” (ISO 27001). No mainland-China region is named anywhere in MailerLite's documentation; your subscribers' data sits offshore. |
| What you're moving | “Subscribers' information: email address and any other additional information,” plus the open, click and IP data its email beacons collect — personal information under PIPL. |
| Who is responsible | MailerLite processes personal data “on behalf of the Customer”; its GDPR page casts you as “a data controller.” The PIPL cross-border duty is the controller's — yours. |
| Serving the public | MailerLite's forms and landing pages load from offshore. An ICP filing attaches to the mainland site that embeds them — not to MailerLite, which offers no filing path. |
| MailerLite's supply chain | “All of our sub-processors are based in the EU”; the US entity relies on the Data Privacy Framework. A European-and-US setup, with no mainland-China data path. |
Your subscribers’ data lives in the EU — so serving China is a cross-border transfer
MailerLite is unambiguous about where the data goes. Its help center states its “data storage center is located in the European Union and has an information storage security certificate (ISO 27001),” its privacy policy repeats the European-Union location, and nowhere in its documentation is there a mainland-China region. It is equally clear about what it holds for you: “Subscribers’ information: email address and any other additional information that Customer provides to MailerLite,” alongside email beacons that “collect information about when you open the email and your IP address” and reports on “what actions your Subscribers took.” For people in the mainland, every piece of that is personal information.
Collect it from subscribers in China and keep it in the EU, and you have made a cross-border transfer of personal information under China’s Personal Information Protection Law. The duty falls on the handler — and MailerLite has already told you who that is. Its privacy policy opens, “We process Personal Data as a Processor on behalf of the Customer,” with “no direct relationship with Customers’ Subscribers,” and its GDPR page casts you as “a data controller.” As the controller you must give notice, obtain separate consent, and clear one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification — under PIPL Articles 38–43. And if you are a critical information infrastructure operator or a large-volume handler, personal information collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)), a residency duty an EU-only service has no way to satisfy.
The ICP filing rides on your site, not on MailerLite
MailerLite is something you embed, not the website of record — “embedded signup forms,” pop-ups, and a builder to “create custom landing pages with interactive blocks and embedded signup forms.” That changes where the licensing question lands. A public-facing site served to mainland visitors turns on an ICP filing (ICP 备案) under State Council Order No. 292 and MIIT Order No. 33, and that filing attaches to the site and its mainland hosting resource. Drop a MailerLite form onto a mainland-hosted, ICP-filed page and the filing is yours to hold; MailerLite neither carries one nor opens a path to one. Its forms and landing pages, meanwhile, are served from the same offshore infrastructure its data sits on — a delivery consideration for anything you embed on a China-facing page, and one quite separate from the licensing it does not touch.
Reachable is not the same as compliant
MailerLite is not a service that fails the China test because it cannot be opened; it falls short because of where the data rests and whose obligation that is. An embedded form loading from offshore is a delivery question worth checking on a real mainland connection before you lean on it — but even a form that appears instantly leaves the cross-border transfer and the controller’s PIPL obligations precisely where they stood. Here, reachability is the lesser half of the question; the personal-information law is the half that settles it.
This is a risk map, not a verdict: whether you need a transfer mechanism, in-country storage, a rethink of where the form is served, or some combination, depends on what you collect, how much of it you hold, and who your subscribers are — worth settling with counsel before you build.
Where 21YunBox fits — a compliant overlay, not a migration
You keep MailerLite for exactly what it does well — your campaigns, your automations, the subscriber list you already run. What it cannot give a China audience is a lawful, in-country home for the public site that collects the data and the ICP footing that site requires. That is the piece we add: ICP-filed delivery from inside the mainland, set in front of the origin you already run, with no rebuild, no second codebase and no move off MailerLite. Our China team maps your PIPL cross-border and data-residency exposure against your entity, your subscriber volumes and where your forms are served, then stands up the ICP-filed, in-country delivery and storage a compliant China presence needs — while your email stack stays exactly where it is.
Related reading:
Frequently Asked Questions
Where does MailerLite store my subscribers' data?
In the European Union. MailerLite states its "data storage center is located in the European Union and has an information storage security certificate (ISO 27001)," and it names no mainland-China region. For an audience in China that means your subscribers' email addresses, IP and engagement data are held offshore — a cross-border transfer of personal information under PIPL, which you, as the controller, are responsible for clearing (notice, separate consent and a transfer mechanism).
Do I need an ICP filing to use MailerLite in China?
The ICP filing isn't something MailerLite carries. It attaches to the public website served to mainland visitors — so if you embed MailerLite's signup forms or landing pages on a mainland-facing site, the ICP filing (State Council Order No. 292; MIIT Order No. 33) is yours to hold on that site and its mainland hosting. MailerLite's own forms are served from offshore, which is a separate delivery consideration. Whether a filing is required turns on where and how the form is served; confirm the specifics with counsel.
Can 21YunBox help make MailerLite work in China?
Yes. Our China team can assess your PIPL cross-border and data-residency exposure — for your entity, your subscriber volumes and where your forms are served — and stand up the ICP-filed, in-country delivery a compliant China presence needs, in front of the site you already run, while you keep MailerLite as your email platform. Get in touch to work through your specific case.