Does Better Stack Work in China? Log Data Residency, PIPL & Your Telemetry
Better Stack stores data in the EU by default and names no mainland-China region — by its own security page — so the application logs, uptime checks and incident contacts it ingests from your Chinese users come to rest offshore, a cross-border transfer of personal information under PIPL. A compliance-first look at where your log data lives, and the lawful in-country path.
Does Better Stack work in China?
Yes — Better Stack loads and ingests from mainland China, but reachability is the easy half. Better Stack runs no site inside the mainland: by its own security page data is stored in the EU by default, so every log line, uptime check and incident contact you collect in China comes to rest on an offshore backend — a cross-border transfer of personal information, not a speed problem.
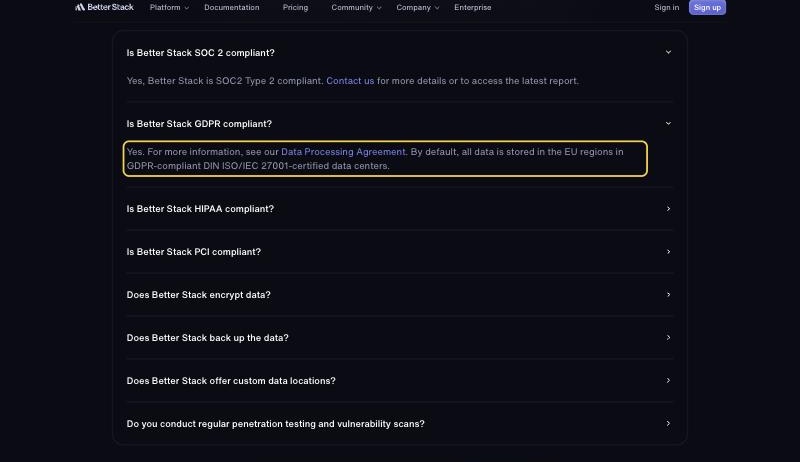
Better Stack's Security page states that "By default, all data is stored in the EU regions in GDPR-compliant DIN ISO/IEC 27001-certified data centers," and that it offers "custom data locations for enterprise accounts" only on request. The EU is the only storage region it names; none is in mainland China. Its log side ingests your application's full log streams — which routinely carry client IPs, user IDs, emails and request bodies — while its incident side holds responder names and contacts. Gathered on mainland servers and stored offshore, that personal information is a cross-border transfer PIPL governs (notice, separate consent and one transfer mechanism, Articles 38–40; a data-export security assessment above the volume thresholds), and for a CIIO or high-volume handler it must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39, formerly Article 37). The table below pairs Better Stack's own wording with the rule each line triggers.
This is a risk map, not a verdict — what applies turns on what your logs contain, how much of it is personal, and who your users are. Our China team can map your exposure with you →
What Better Stack's own documentation says about China
| Fact | Primary source |
|---|---|
| Better Stack runs no site inside mainland China. Its own Security page states that "By default, all data is stored in the EU regions in GDPR-compliant DIN ISO/IEC 27001-certified data centers," and that it offers "custom data locations for enterprise accounts" only on request. The EU is the only storage region it names in the open — there is no mainland-China option — so the application logs, uptime results and incident contacts you collect in China come to rest on an offshore backend. | Better Stack — Security (betterstack.com/security), retrieved 2026-10-09 |
| The data Better Stack ingests is personal information. Log management takes in your application's full log streams — which routinely carry client IPs, user IDs, emails and request bodies — while the uptime side records your probed endpoints and the incident side stores responder names and contacts. Better Stack's own privacy policy acknowledges that in using the service "you may be providing us with your clients' data, including PII such as name and email address." Collected on mainland servers and stored offshore, that is a cross-border transfer of personal information under PIPL — notice, separate consent and a transfer mechanism (Articles 38–40). | Better Stack — Privacy Policy (betterstack.com/privacy), retrieved 2026-10-09; PIPL Articles 38–40 |
| Better Stack offers no way to keep the data in the mainland. Storage defaults to the EU, custom locations are an unnamed enterprise-only arrangement, and its data-processing agreement adds that data may be processed "to and in the United States of America and other locations" — every one of them outside mainland China. For a critical information infrastructure operator or a high-volume handler, personal information gathered in China must stay on mainland soil (PIPL Article 40; Cybersecurity Law Article 39, formerly Article 37) — a residency duty Better Stack's offshore-only storage cannot meet. | Better Stack — Security and DPA (betterstack.com), retrieved 2026-10-09; PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) |
| Reachability is the easy half — Better Stack is a backend, not a hosted site. The dashboard loads and ingestion runs from inside China, so the exposure is not whether it connects but where the data it collects lives. An ICP filing (State Council Order No. 292; MIIT Order No. 33) attaches to the public mainland website or app you serve — not to Better Stack as a backend — while the PIPL cross-border and residency duties attach to the log data it carries offshore. | Better Stack documentation, retrieved 2026-10-09; State Council Order No. 292; MIIT Order No. 33 |
Sources verified by the 21YunBox compliance team on 2026-10-09.
For teams serving mainland China, what matters about Better Stack is not whether the dashboard opens — it usually does — but where the data it swallows is allowed to live. Better Stack is a log-management, uptime and incident-response platform: its log side ingests your application’s full log streams, the richest and least-filtered record your systems produce; its uptime side pings your endpoints; its incident side routes alerts to named, contactable responders. On its own Security page Better Stack says data is stored in the EU by default, and it names no site inside mainland China. So the logs your mainland servers emit, the uptime results tied to your mainland endpoints, and the responder contacts in your on-call rotation are gathered inside China and come to rest outside it. Connecting to Better Stack was never the obstacle; keeping what it ingests inside the border is.
Better Stack in China at a glance
| What decides it | In Better Stack's own terms — and China's law |
|---|---|
| Where the data lives | Better Stack's Security page says “all data is stored in the EU regions” by default, in ISO/IEC 27001-certified data centers, with “custom data locations for enterprise accounts” only on request. The EU is the only region it names; none is in mainland China. |
| What Better Stack ingests | The log side takes in your application's full log streams; the uptime side probes your endpoints; the incident side holds responder names and contacts. Log lines routinely carry client IPs, user IDs, emails and request bodies. |
| Your China users' data | Gathered on mainland servers and stored in the EU, those logs and contacts are a cross-border transfer of personal information PIPL governs — notice, a separate consent and one transfer mechanism (Articles 38–40). |
| In-country storage | A CIIO or high-volume handler must keep personal information collected in China inside the mainland (PIPL Article 40; Cybersecurity Law Article 39, formerly Article 37). Better Stack names no mainland region to meet that. |
| Serving the public & reachability | A Better Stack dashboard served to mainland visitors from inside China needs its own ICP filing; as an offshore backend it offers no mainland footing to file against. Reachability is not the axis — where the log data rests is. |
No mainland region, so your log data comes to rest offshore
Better Stack’s own Security page is explicit about geography: “By default, all data is stored in the EU regions in GDPR-compliant DIN ISO/IEC 27001-certified data centers.” A different location is possible, but only as a bespoke arrangement — the page offers “custom data locations for enterprise accounts” and asks you to contact the company to discuss one. The EU is the only region named in the open, and Better Stack’s data-processing agreement adds that data may be processed “to and in the United States of America and other locations.” Not one of those places is mainland China. So the log streams your mainland servers emit, the uptime checks tied to your mainland endpoints, and the responder details in your incident rotation are collected inside China and stored outside it. Reaching the service was never the hard part; keeping what it ingests on the right side of the border is.
The logs Better Stack ingests are personal information
A log stream is the least-filtered record a system produces, which is exactly why it is rarely anonymous. Application logs routinely carry client IP addresses, user and session IDs, email addresses printed in error lines, and whole request and response bodies; Better Stack’s own privacy policy acknowledges that in using the service “you may be providing us with your clients’ data, including PII such as name and email address.” The uptime side records which of your endpoints were probed and when, and the incident side stores the names and contact details of the people you page. Every one of those is personal information. Collected on mainland servers and sent to an EU backend, the export is what China’s Personal Information Protection Law treats as a cross-border transfer, and the duty rides on you as the handler — not on Better Stack: you owe affected users notice, a standalone consent for the transfer, and one cleared route out of the country — a CAC-led security assessment, the CAC standard contract, or certification (PIPL Articles 38–40). Above the regulator’s volume thresholds, that route is specifically a data-export security assessment. And because raw logs are unfiltered, a single unscrubbed line can carry Article 28 sensitive personal information — precise location, credentials, financial or health fields — which raises the bar on both consent and necessity.
Scrubbing narrows the exposure — it does not close the door
Better Stack lets you shape what you send: you can filter or drop fields before they are ingested and keep high-risk values out of the pipeline in the first place. That is worth doing. But redaction changes what crosses the border, not the fact that it crosses, and it does nothing for residency. If you are a critical information infrastructure operator or a high-volume handler, personal information gathered in China has to stay on mainland soil (PIPL Article 40; Cybersecurity Law Article 39, formerly Article 37 — the 2025 amendment, in force January 1, 2026, renumbered the data-localization article without changing its substance) — and with every Better Stack storage region offshore, there is no in-country store on Better Stack alone to satisfy that duty. Separately, if you put a Better Stack dashboard in front of mainland users from inside China, that public surface needs its own ICP filing (State Council Order No. 292; MIIT Order No. 33); as an offshore backend, Better Stack gives you no mainland hosting resource to file against.
Read this as a risk map rather than a ruling: whether you owe a transfer mechanism, in-country storage, an ICP filing, or some combination of them turns on what your logs actually hold, your data volumes, and who your users are — worth nailing down with counsel before you wire anything live.
The lawful path — map, localize, deliver
You keep running Better Stack. What an EU-hosted observability platform structurally cannot give you is a lawful home inside China for the personal data its log pipeline and incident tooling gather there — and 21YunBox never uses or suggests circumvention of any kind to get around that. Instead we work three ways. We map the lawful route: your PIPL cross-border and data-residency obligations read against your entity, your data volumes, and who your users are. We localize what cannot lawfully leave — standing up consented, in-country processing and storage for the log data that has to remain on mainland soil, so the records that must stay, stay. And we deliver the rest through ICP-filed, in-country delivery set in front of the stack you already run — no rebuild, no second codebase, and no move off Better Stack for the telemetry that can lawfully cross the border. The aim is plain: your monitoring runs legally and compliantly for your users in China.
Related reading:
- How to get an ICP filing for China
- Cross-border data transfers under PIPL
- China’s data-export security assessment measures
- China Cybersecurity Law — data localization