Does Datadog Work in China? Data Residency, PIPL & Your Telemetry
Datadog runs no site inside mainland China — its sites are in the US, the EU, Japan, Australia and the UK — so the logs, traces and RUM sessions it collects from Chinese users are shipped offshore, a cross-border transfer of personal information under PIPL. A compliance-first look at the data-residency door.
Does Datadog work in China?
Yes — Datadog loads and ingests from mainland China, but that is the easy half. Datadog operates no site inside the mainland, so every log, trace, metric and RUM session you collect in China is shipped to and stored on a Datadog site offshore — a cross-border transfer of personal information, not a speed problem.
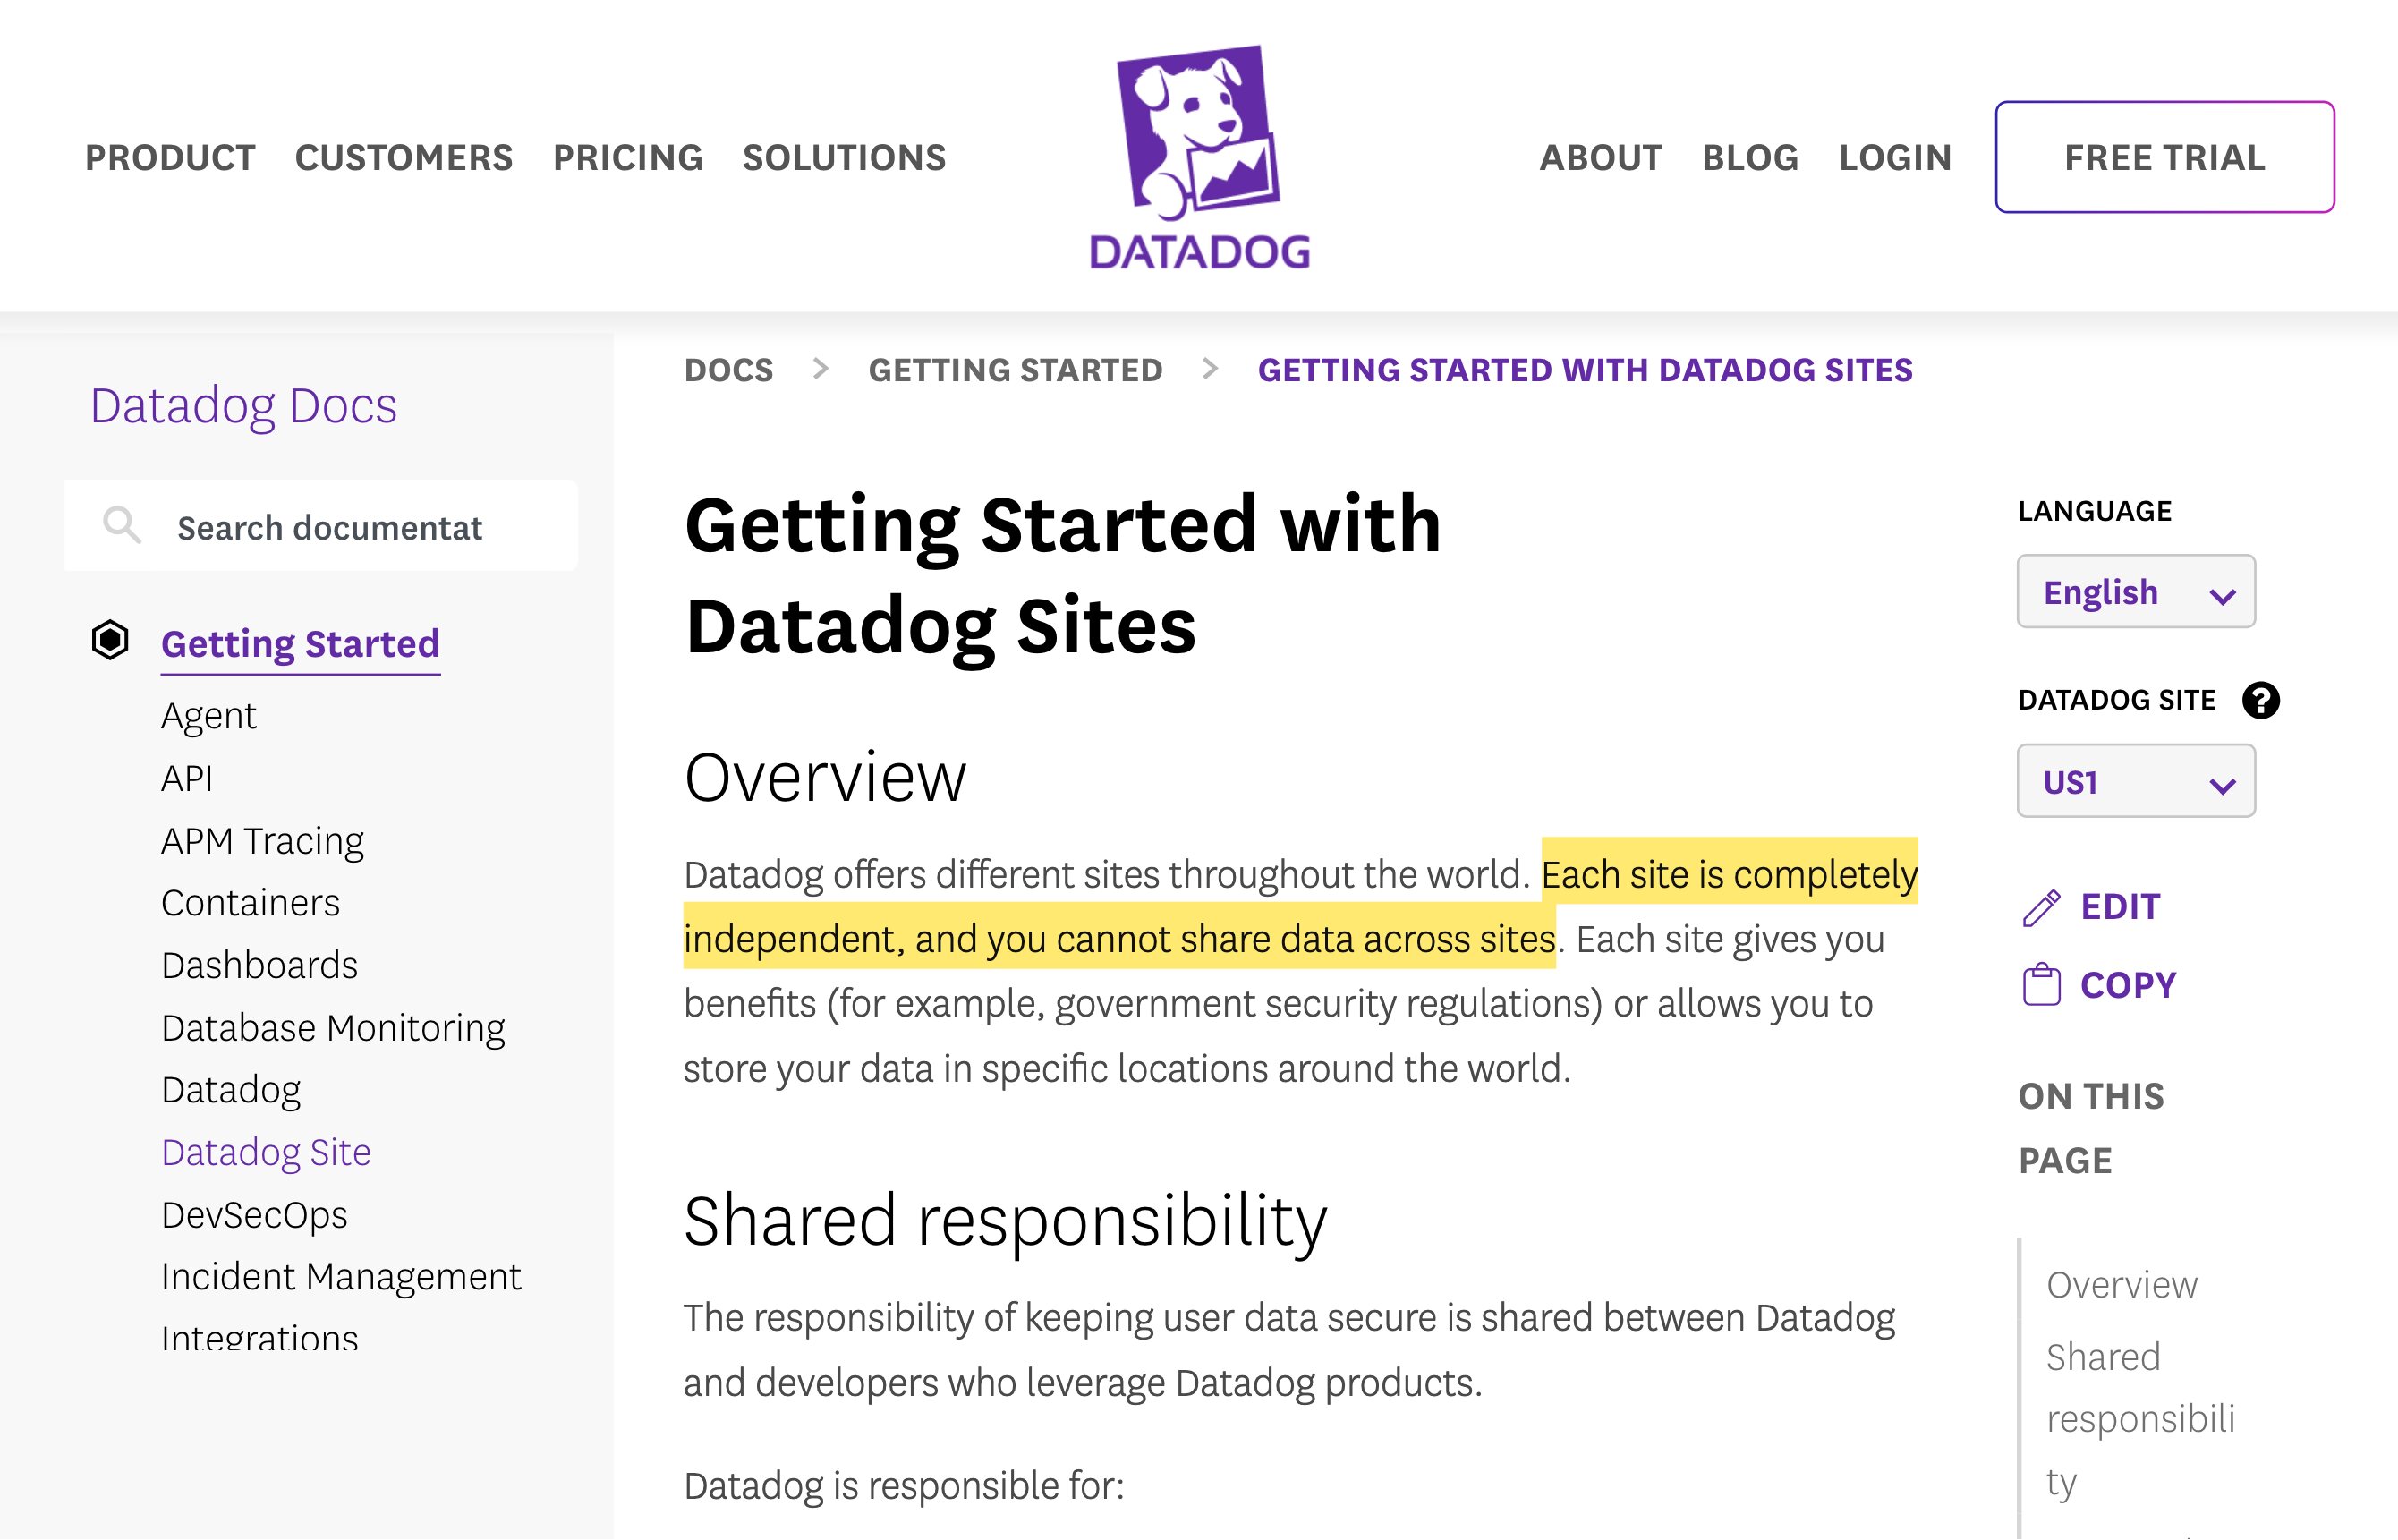
Datadog's own "Getting Started with Sites" lists its sites as US1, US3, US5 and the US1-FED and US2-FED government sites in the United States, EU1 in Germany, AP1 in Japan, AP2 in Australia and UK1 in the UK — and states that "Each site is completely independent, and you cannot share data across sites." None is in mainland China. Datadog's RUM carries a visitor's IP and geolocation and can pick up PII in action names and URLs, while logs and traces routinely carry user IDs and request contents. Gathered from mainland users and sent to an offshore site, that personal information is a cross-border transfer PIPL governs (notice, separate consent and a transfer mechanism, Articles 38–43), and for a CIIO or large-volume handler it must be stored in China (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). The table below is Datadog's own wording and the rule each line triggers.
This is a risk map, not a verdict — what applies turns on the data you collect, how much of it is personal, and who your users are. Our China team can map your exposure with you →
Compliance snapshot
- ! No mainland-China site — your China telemetry is stored offshore
- ! RUM sessions carry a visitor's IP and geolocation across the border
- ! Logs and traces carry PII — a cross-border transfer under PIPL
- ✕ No in-country storage, so data-residency duties can't be met on Datadog
- ✓ Reachability isn't the issue — where the data lands is
What Datadog's own documentation says about China
| Fact | Primary source |
|---|---|
| Datadog runs no site inside mainland China. Datadog's own "Getting Started with Sites" documentation lists the sites it operates — US1, US3, US5 and the US1-FED and US2-FED government sites in the United States, EU1 in Germany, AP1 in Japan, AP2 in Australia and UK1 in the UK — and states that "Each site is completely independent, and you cannot share data across sites." There is no mainland-China option to choose, so the logs, traces, metrics and RUM sessions you collect in China are stored on a Datadog site outside the mainland. | Datadog — Getting Started with Datadog Sites (docs.datadoghq.com), retrieved 2026-10-07 |
| The telemetry Datadog gathers is personal information. Datadog's RUM data-security doc says "you can choose whether or not you want to include IP or geolocation data" — a visitor's IP and location are collected unless you switch them off — and lists where PII surfaces: "Action names on buttons," "Names shown in URLs" and "Custom tracked events instrumented by the developers of the app." Logs and APM traces carry user IDs and request contents too. Collected from mainland users and shipped to an offshore site, that is a cross-border transfer of personal information under PIPL — notice, separate consent and a transfer mechanism (Articles 38–43). | Datadog — Data Security: Real User Monitoring (docs.datadoghq.com), retrieved 2026-10-07; PIPL Articles 38–43 |
| Datadog offers no way to keep the data in the mainland. Datadog lets you "store your data in specific locations around the world," but every one of those locations — the United States, the EU, Japan, Australia and the UK — is outside mainland China. For a critical information infrastructure operator or a large-volume handler, personal information collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — a data-residency duty Datadog's offshore-only sites cannot satisfy. | Datadog — Getting Started with Datadog Sites (docs.datadoghq.com), retrieved 2026-10-07; PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) |
| Reachability is the easy half — Datadog is a backend, not a hosted site. Datadog loads and ingests from inside China, so the exposure is not whether it connects but where the data it collects is stored. The ICP filing question (State Council Order No. 292; MIIT Order No. 33) attaches to the public mainland website or app you operate, not to Datadog itself — while the PIPL cross-border and data-residency duties attach to the telemetry Datadog carries offshore. | Datadog documentation, retrieved 2026-10-07; State Council Order No. 292; MIIT Order No. 33 |
Sources verified by the 21YunBox compliance team on 2026-10-07.
For a mainland-China audience, the question about Datadog is rarely whether the dashboard loads — it usually does. The question is where the data it gathers is allowed to live. Datadog answers that in its own documentation: it runs no site inside mainland China. So the Agent on your mainland servers, and the RUM snippet in your mainland visitors’ browsers, collect logs, traces, metrics and session data in China and ship them to a Datadog site in the United States, the EU, Japan, Australia or the UK. Because that telemetry routinely carries personal information — client IP addresses, user IDs, request contents — exporting it is a cross-border transfer China’s law governs. The dashboard being reachable is the delivery half; where the data lands is the exposure.
Datadog in China at a glance
| What decides it | In Datadog's own terms |
|---|---|
| Where it runs | Sites in the United States (US1, US3, US5, and the US1-FED and US2-FED government sites), the EU (EU1, Germany), Japan (AP1), Australia (AP2) and the UK (UK1). None is in mainland China. |
| Can data move between sites | “Each site is completely independent, and you cannot share data across sites” — and there is no mainland site to move it to in the first place. |
| What the telemetry contains | RUM lets you include a visitor's IP and geolocation, and PII can appear in “Action names on buttons,” “Names shown in URLs” and “Custom tracked events.” Logs and traces carry user IDs and request contents. |
| Your China users' data | Collected in the mainland and shipped offshore, it is a cross-border transfer PIPL governs; CIIOs and large-volume handlers owe an in-country storage duty Datadog's offshore sites cannot meet. |
| Is it reachable? | Yes — the dashboard and ingestion load from inside China. The exposure is where the data is stored, not whether it arrives. |
No mainland site, so your telemetry leaves the country
Datadog’s sites are in the United States (US1, US3, US5, and the US1-FED and US2-FED government sites), the EU (EU1, Germany), Japan (AP1), Australia (AP2) and the UK (UK1). In its own “Getting Started with Sites” documentation Datadog states that “Each site is completely independent, and you cannot share data across sites.” Not one of those sites is in mainland China, and there is no mainland site to pick. So the Datadog Agent running on your mainland servers, and the RUM snippet loaded in your mainland visitors’ browsers, gather their data in China and send it to whichever offshore site your account is on. Reaching Datadog was never the hard part; keeping the data it gathers inside the country is.
The data Datadog collects is personal information
Observability data is not anonymous by nature. Datadog’s RUM security documentation says “you can choose whether or not you want to include IP or geolocation data” — which means a visitor’s IP address and location are gathered unless you turn them off — and it lists the places PII tends to surface: “Action names on buttons,” “Names shown in URLs” and “Custom tracked events instrumented by the developers of the app.” Logs and APM traces are no cleaner: they routinely carry user IDs, session tokens and raw request contents. A single mainland visitor’s client IP is already personal information, and under China’s Personal Information Protection Law moving it to an offshore site is a cross-border transfer — the handler (you, not Datadog) must give notice, obtain separate consent, and clear one transfer mechanism: a CAC security assessment, the CAC standard contract, or certification (Articles 38–43).
Scrubbing narrows the exposure — it does not close the door
Datadog gives you tools to reduce what leaves: the Sensitive Data Scanner can hash, redact or drop matched patterns on ingestion, and you can switch off IP and geolocation collection in RUM. Those are worth doing. But scrubbing changes what crosses the border, not the fact that data crosses it, and it does nothing for the residency question. If you are a critical information infrastructure operator or a large-volume handler, personal information collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — and with every Datadog site offshore, there is no in-country store to meet that duty on Datadog alone. The ICP filing (State Council Order No. 292; MIIT Order No. 33) is a separate door that attaches to whatever public mainland site or app you run, not to Datadog as a backend service.
This is a risk map, not a verdict: whether a transfer mechanism, in-country storage, or both apply depends on what you collect, how much of it is personal, and who your users are — worth settling with counsel before you wire anything up.
Where 21YunBox fits — a compliant overlay, not a migration
You keep running Datadog. What a monitoring vendor with no mainland site cannot give you is a lawful place inside China for the personal data its agents and browser SDK collect there. That is the piece 21YunBox adds: ICP-filed, in-country delivery and a compliant mainland data path, set in front of the stack you already run — no rebuild, no second codebase, and no switch away from Datadog for the telemetry that can lawfully leave. Our China team maps your PIPL cross-border and data-residency obligations against your entity, your data volumes and who your users are, then stands up the in-country delivery and storage a compliant China presence needs.
Related reading:
Frequently Asked Questions
Does Datadog have a data center or region in mainland China?
No. Datadog's own "Getting Started with Sites" lists its sites as US1, US3, US5 and the US1-FED government site in the United States, EU1 in Germany, AP1 in Japan and AP2 in Australia, and notes that each site is completely independent with no data shared across sites. None sits in mainland China, so the logs, traces, metrics and RUM sessions you collect from Chinese users and servers are stored on a Datadog site offshore.
Is it a problem that our Datadog telemetry leaves China?
Treat it as a risk to assess with counsel, not a flat yes or no. Datadog's agents and browser SDK collect personal information in China — client IP addresses, user IDs, and PII that lands in logs, URLs and action names — and send it to an offshore site. Under PIPL that is a cross-border transfer requiring notice, separate consent and a transfer mechanism, and for a CIIO or large-volume handler the data must be stored in the mainland. Datadog's Sensitive Data Scanner can scrub some PII on ingestion, but scrubbing narrows the exposure rather than removing the border crossing.
Can 21YunBox help make our Datadog setup compliant in China?
Yes. Our China team can map your PIPL cross-border and data-residency exposure for your entity, your data volumes and your users, and stand up the ICP-filed, in-country delivery and storage a compliant China presence needs — in front of the stack you already run, so you keep Datadog for the telemetry that can lawfully leave the mainland. Get in touch to work through your specific case.