Does Hivebrite Work in China? ICP, Member Data & an Offshore Portal
Hivebrite hosts community portals offshore — on AWS and Google Cloud in the EU, US, Switzerland or Australia, with no mainland-China region — so a member site served to China runs offshore with no ICP-filing path, and member personal data lands outside the mainland under PIPL. A compliance-first look at the two doors.
Does Hivebrite work in China?
The portal may load, but running a Hivebrite community for mainland members puts two China laws in play at once: the member site is public, so it needs an ICP filing Hivebrite's offshore hosting cannot carry — and every member profile, post and private message is stored outside the mainland.
Hivebrite runs on Amazon Web Services and Google Cloud and offers data-storage regions in "the European Union, the United States, Switzerland, or Australia" — none inside mainland China. Because the member community it powers is a public-facing website served to mainland visitors, that site needs an ICP filing, and an offshore host has no mainland footing to file against. The member personal information you hold on it — profiles, contact details, posts, private messages — then sits abroad: a cross-border transfer PIPL governs. The table below is Hivebrite's own wording and the rule each door triggers.
This is a risk map, not a verdict — which obligations bite turns on your entity, your members and the data you hold. Our China team can map your exposure and the filing path with you →
Compliance snapshot
- ✕ A public community portal served from offshore can't carry a mainland ICP filing
- ! Member profiles, posts and private messages sit offshore — PIPL cross-border applies
- ! Hivebrite hosts in the EU, US, Switzerland or Australia — no mainland-China region
- ! Large-volume or sensitive member data can trigger China data-localization
- ! By Hivebrite's own list, even China visitors' requests resolve to offshore infrastructure
What Hivebrite's own documentation says about China
| Fact | Primary source |
|---|---|
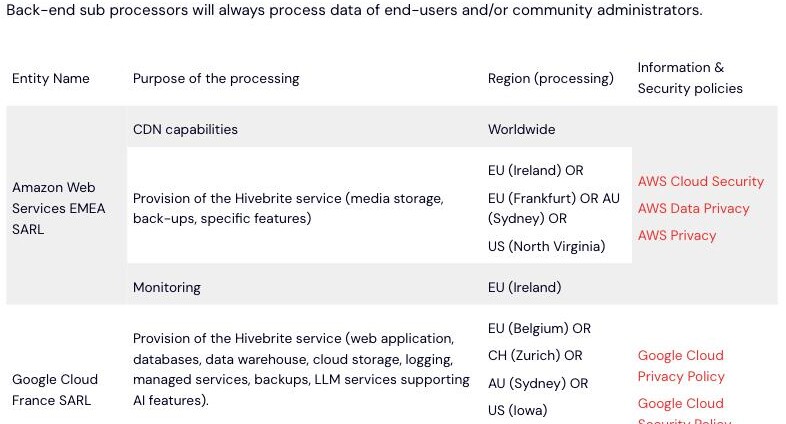
| Hivebrite hosts your community offshore — and publishes exactly where. Its sub-processor list shows the platform's hosting resolving to "EU (Ireland) OR EU (Frankfurt) OR AU (Sydney) OR US (North Virginia)" on Amazon Web Services and "EU (Belgium) OR CH (Zurich) OR AU (Sydney) OR US (Iowa)" on Google Cloud. Four countries, and not one of them is mainland China — there is no in-country region to choose. | Hivebrite — Sub-processors (hivebrite.io), effective Sept 28, 2026, retrieved 2026-10-07 |
| Because the community portal is a public site, an ICP filing really is in play — and there's nothing to file against. Hivebrite serves a member-facing website to visitors in the mainland, and a public site shown to mainland visitors turns on an ICP filing (ICP 备案) under State Council Order No. 292 and MIIT Order No. 33, tied to a hosting resource physically in China. Hivebrite's hosting sits only in the EU, US, Switzerland or Australia, so no such resource exists on the platform. Unlike a pure backend tool, this portal is public — the filing question does not pass it by. | Hivebrite — Sub-processors (hivebrite.io), retrieved 2026-10-07; State Council Order No. 292; MIIT Order No. 33 |
| Every member profile, post and private message is stored across the border. A community platform holds extensive personal information, and Hivebrite keeps it in one of its offshore regions — "the European Union, the United States, Switzerland, or Australia" — never the mainland. For members in China that is a cross-border transfer under PIPL: the handler (you, not Hivebrite) must give notice, obtain separate consent and clear one transfer mechanism (Articles 38–43). For a large-volume or sensitive-data handler, the data must instead be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — which no offshore region can do. | Hivebrite — Security & Privacy (hivebrite.io), retrieved 2026-10-07; PIPL Articles 38–43 & 40; Cybersecurity Law Article 39 (formerly Article 37) |
| Hivebrite's own list shows China visitors' requests going offshore. The sub-processor page records a geolocation service used "Only for end-users when browsing from China," with its processing region listed as "US." Hivebrite therefore anticipates members reaching the portal from inside the mainland — and documents that the data path for those requests runs to infrastructure outside China. That is the cross-border exposure stated in the vendor's wording, not an inference drawn from it. | Hivebrite — Sub-processors (hivebrite.io), effective Sept 28, 2026, retrieved 2026-10-07 |
Sources verified by the 21YunBox compliance team on 2026-10-07.
For a mainland-China audience, the deciding question about Hivebrite is not how quickly the community loads — it is whether you are cleared to run that community there at all. Hivebrite is an all-in-one community platform: it serves a public, member-facing portal and holds the personal information of everyone on it — profiles, contact details, posts, private messages. Both of those facts meet Chinese law head-on. The portal is a public website, so serving it to mainland members turns on an ICP filing; and because Hivebrite runs no region inside mainland China, that portal is hosted offshore with nothing to file against, while the member data it holds sits across the border under PIPL. Reaching the site is the easy part; the licensing and the data residency are the exposure.
Hivebrite in China at a glance
| What decides it | In Hivebrite's own terms |
|---|---|
| Where it runs | Hosted on Amazon Web Services and Google Cloud, with data-storage regions in the European Union, the United States, Switzerland or Australia. No region is inside mainland China; the nearest options are still offshore. |
| Who holds the data | A community platform by design: member profiles, contact details, posts and private messages all live in Hivebrite's chosen region — EU, US, Swiss or Australian — not in the mainland. |
| Serving the public | The member portal is a public-facing website. Served to mainland visitors it needs an ICP filing tied to a mainland hosting resource — which an offshore Hivebrite deployment does not have. |
| Your members' data | Personal information of Chinese members stored offshore is a cross-border transfer PIPL governs, plus a data-localization duty for large-volume or sensitive-data handlers that offshore regions cannot meet. |
| China visitors | Hivebrite's own sub-processor list carries a service used “Only for end-users when browsing from China,” processed in the US — so even mainland visitors' requests resolve to offshore infrastructure. |
Door one — a public member portal with no mainland footing for an ICP filing
Hivebrite’s product is a member-facing community site — sign-in pages, member directories, event and content pages — delivered over the open internet. For a mainland audience that makes it a public-facing website, and a public website served to visitors inside China turns on an ICP filing (ICP 备案) under State Council Order No. 292 and MIIT Order No. 33. That filing has to attach to a hosting resource physically in the mainland. Hivebrite’s sub-processor list shows its hosting resolving to “EU (Ireland) OR EU (Frankfurt) OR AU (Sydney) OR US (North Virginia)” on Amazon Web Services and “EU (Belgium) OR CH (Zurich) OR AU (Sydney) OR US (Iowa)” on Google Cloud — four countries, none of them China. With no mainland hosting resource, there is simply nothing on Hivebrite to file against. This is the point people miss when they assume a backend SaaS tool escapes ICP: because Hivebrite serves the public community site itself, the filing question is live, not theoretical.
Door two — member personal data stored across the border
A community platform exists to hold personal information, and a great deal of it: names, contact details, employment history, posts, and private member-to-member messages. Hivebrite stores that in whichever region you pick — “the European Union, the United States, Switzerland, or Australia” — all outside the mainland. For your Chinese members that is a cross-border transfer under PIPL: the handler — you, not Hivebrite — must give notice, obtain separate consent, and clear one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification) under PIPL Articles 38–43. And if you are a critical information infrastructure operator or a large-volume handler, personal information collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — a residency duty none of Hivebrite’s four countries can satisfy. The volume and sensitivity of what a community platform holds tends to push you toward the stricter end of that test, not the lighter one.
Hivebrite already sends China visitors’ data offshore
You do not have to infer the cross-border flow — Hivebrite documents it. Its sub-processor page, effective September 28, 2026, lists a geolocation service used “Only for end-users when browsing from China,” with the processing region recorded as “US.” In other words, Hivebrite expects members to reach the portal from inside the mainland, and the data path for those requests already runs to infrastructure outside China. Reachability, then, is not the problem; where the request and the record land is. No amount of delivery tuning changes which country the portal is filed in — or which country your members’ data sits in.
This is a risk map, not a verdict: whether you need an ICP filing, in-country storage, or both depends on what your community publishes, how much personal data you hold, and who your members are — worth settling with counsel before you build.
Where 21YunBox fits — a compliant overlay, not a migration
Hivebrite stays your community platform. What it cannot give you — because it has no mainland presence — is lawful delivery from inside China, and that is the single piece we add: ICP-filed, in-country delivery placed in front of your existing Hivebrite portal, with no rebuild, no second codebase and no migration off the platform. Our China team works out which obligations apply to your entity, your members and the data you hold, then stands up the in-country delivery and storage a compliant public community requires — while your members keep using the portal exactly as they do now.
Related reading:
Frequently Asked Questions
Does Hivebrite have a mainland-China region we can host in?
No. Hivebrite's own documentation offers data-storage regions in the European Union, the United States, Switzerland and Australia, and its sub-processor list shows hosting on Amazon Web Services and Google Cloud resolving only to Ireland, Frankfurt, Belgium, Zurich, Sydney, North Virginia or Iowa. None is inside mainland China, so a Hivebrite community served to members there runs from offshore — which is what puts both the ICP filing and the PIPL cross-border question in play.
Our Hivebrite community is members-only — do we still need an ICP filing?
Treat it as a risk to confirm with counsel. "Members-only" usually still means a public-facing website: it is reachable on the open internet, has public sign-in and landing pages, and is served to visitors in the mainland. A public site served to mainland visitors turns on the ICP regime (State Council Order No. 292; MIIT Order No. 33), and that filing must attach to a mainland hosting resource — which an offshore Hivebrite deployment does not have. Whether a registration wall changes your specific obligation is exactly the kind of question to settle with a China-qualified adviser.
Can 21YunBox help make our Hivebrite community work in China?
Yes. Our China team can map which obligations apply — assessing your ICP position and your PIPL cross-border and data-residency exposure for your entity, your member data and where your members are — and stand up the ICP-filed, in-country delivery a compliant public community portal needs, in front of the Hivebrite platform you already run. Get in touch to work through your specific case.