Does SonarQube Work in China? Data Residency, ICP & Cross-Border Rules
SonarQube holds your source code and its SAST findings — a map of your own vulnerabilities. Run offshore, that security-sensitive data and the PII inside your commits rest abroad: a PIPL cross-border and data-localization question, not reachability. SonarQube Server is self-hosted (keep it in-country); SonarQube Cloud is SaaS with no mainland-China region.
Does SonarQube work in China?
For a China engineering team the question is not whether SonarQube's dashboard loads from Shanghai — it is where your source code and its analysis findings are allowed to rest. SonarQube computes a concentrated map of your own code's weaknesses — a security-sensitive dataset — from source that routinely carries secrets and personal data in commits and fixtures. Run on an offshore SonarQube Cloud tenant, that code, those findings and your contributors' identities sit abroad.
That makes it a PIPL cross-border transfer (Articles 38–40) and, for a critical information infrastructure operator or high-volume handler, an in-country storage duty under the Cybersecurity Law's Article 39 (formerly Article 37) — none of which a reachability check can see. Because SonarQube Server is self-hosted, there is a lawful lever: run the Server on in-country infrastructure so the code and findings stay resident. SonarQube Cloud is SaaS, offered only in EU and US regions.
21YunBox is a compliance overlay and partner to the SonarQube you already run — we map what it holds, help you keep the regulated code and findings in-country, and deliver any China-facing developer surface compliantly. We never use or suggest circumvention of any kind; confirm the specifics with counsel.
What SonarQube's own documentation says about China
| Fact | Primary source |
|---|---|
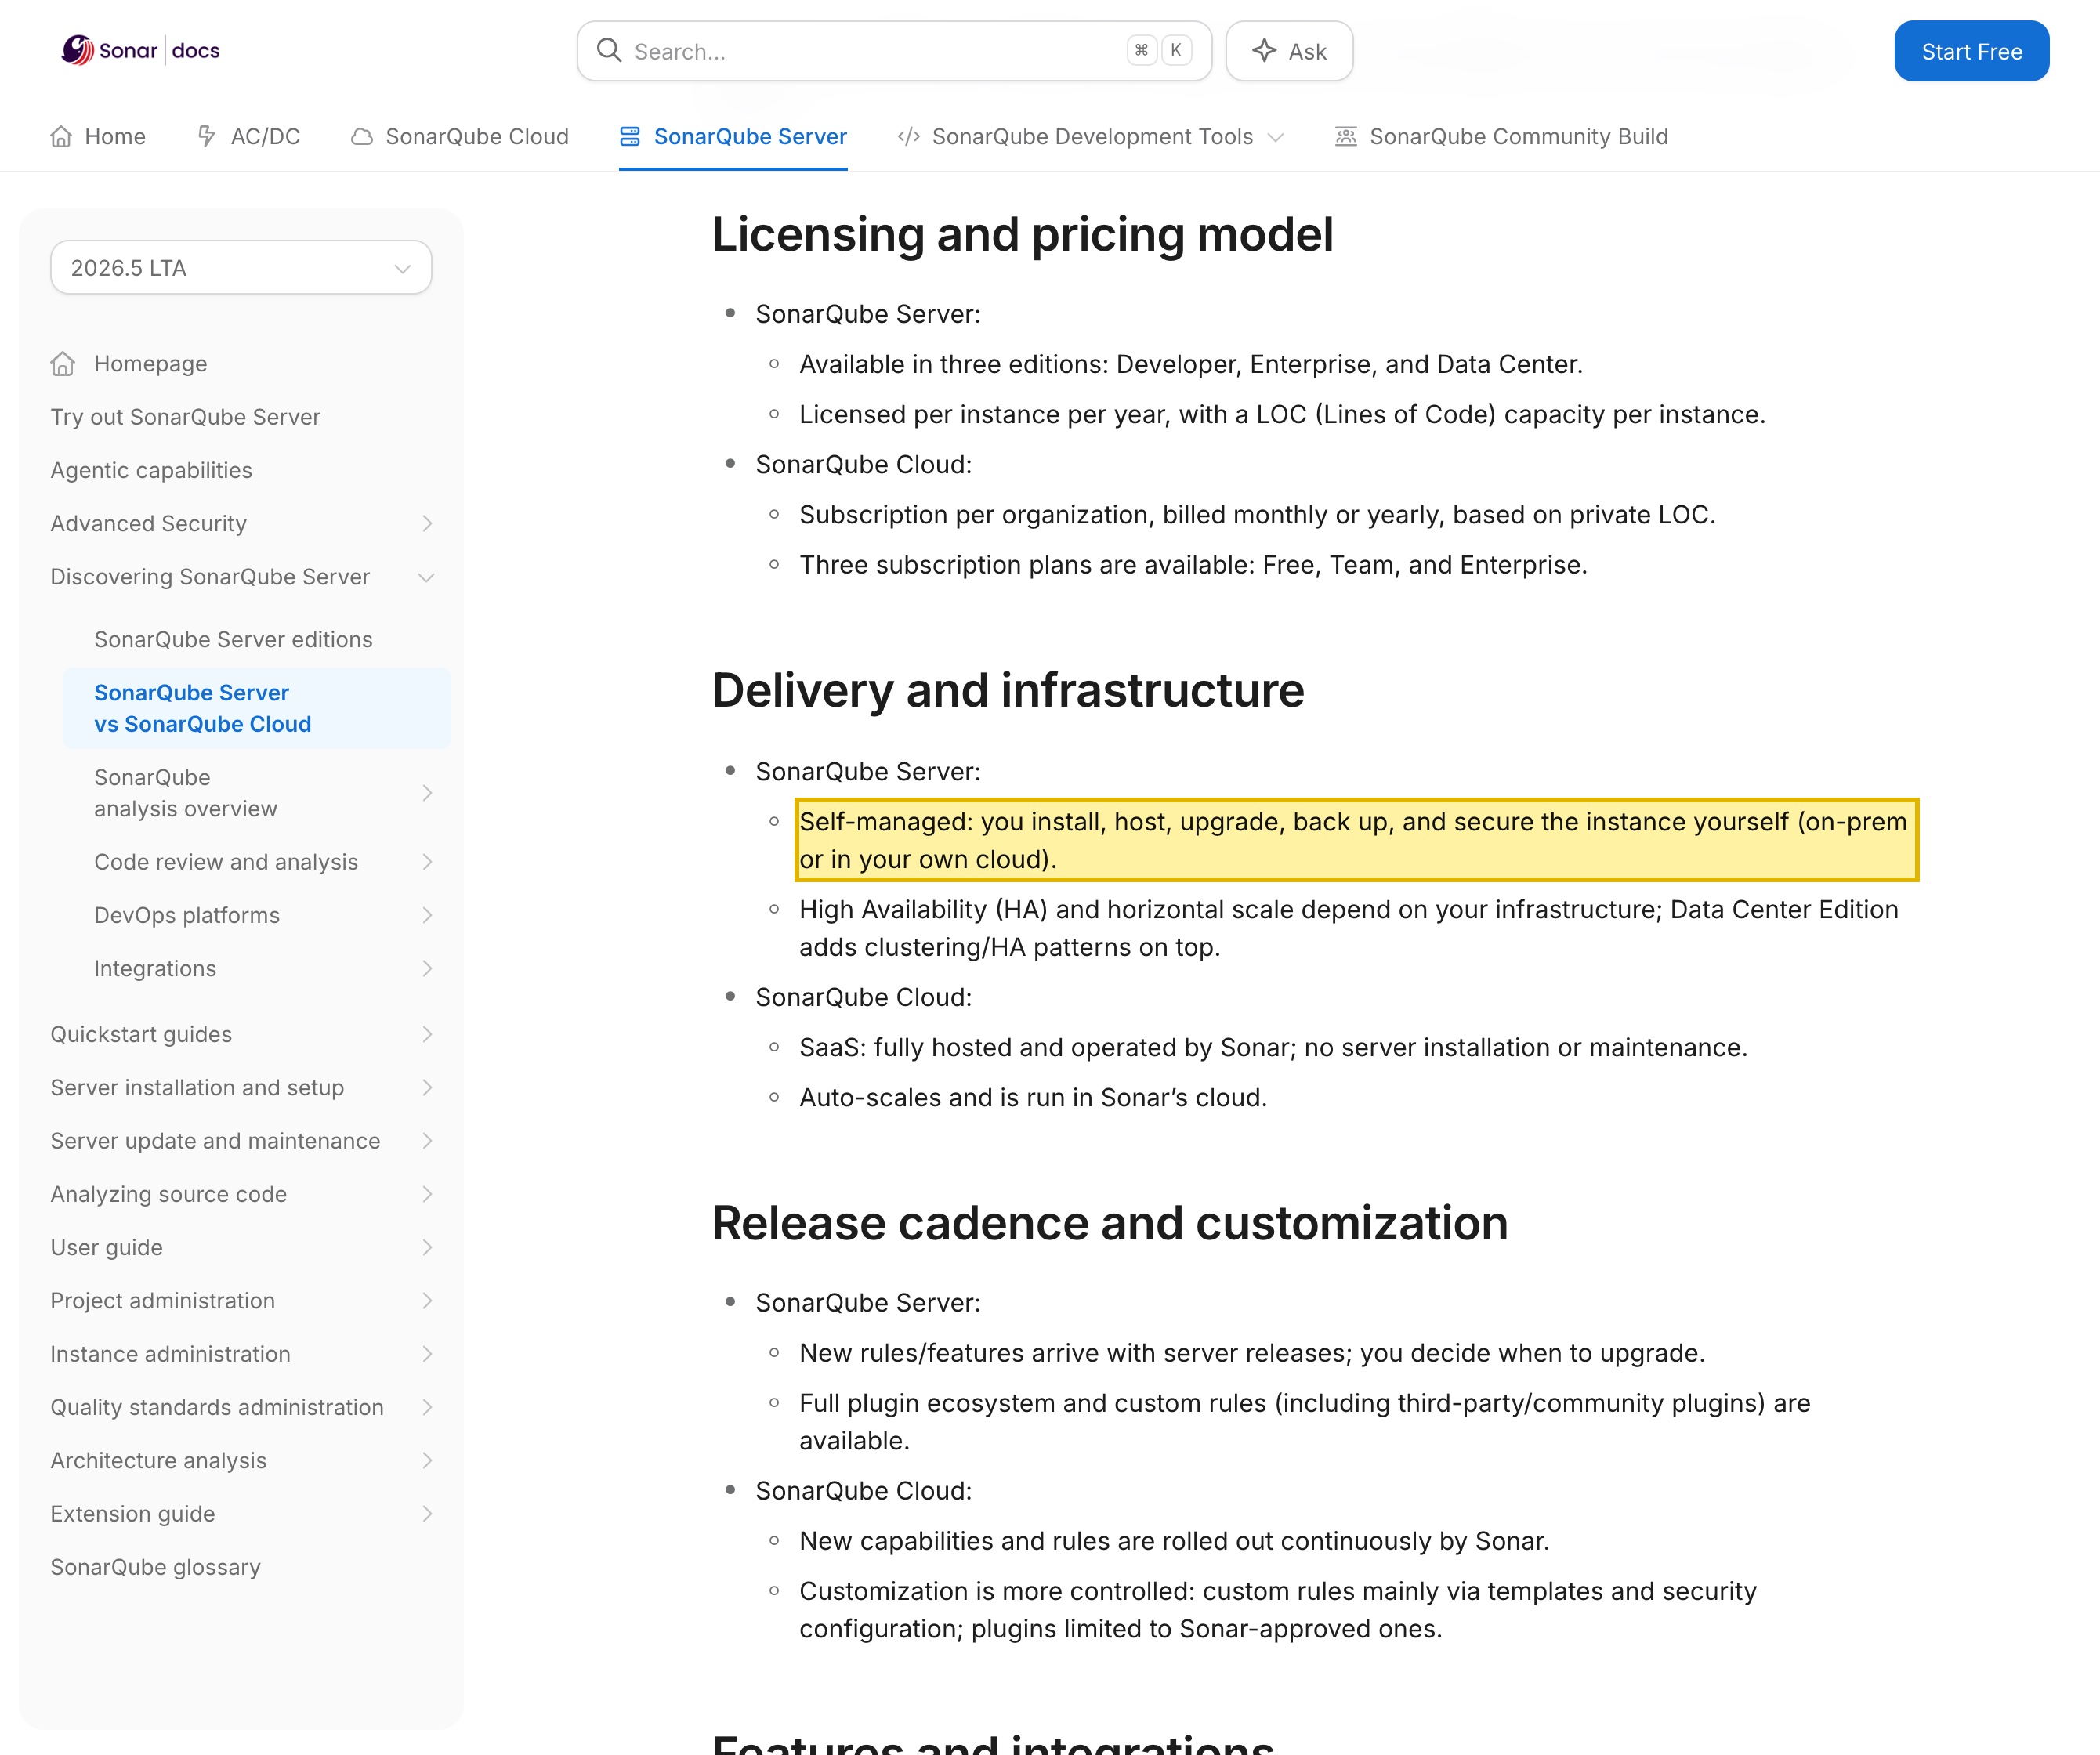
| SonarQube Server is self-managed — you choose where it runs and where its data lives. Sonar's own documentation states: “Self-managed: you install, host, upgrade, back up, and secure the instance yourself (on-prem or in your own cloud).” The same page adds that with Server “You fully control where data lives and how infrastructure meets your regulatory requirements,” and advises choosing SonarQube Server “if you need strict data residency.” | Sonar documentation, “SonarQube Server vs SonarQube Cloud” (docs.sonarsource.com), retrieved 2026-10-12 |
| SonarQube Cloud is SaaS, hosted only in an EU region and a US region — no mainland-China region. Sonar describes SonarQube Cloud (formerly SonarCloud) as “the SaaS delivery of the SonarQube platform,” and its “Choosing your region” guide offers only a European region (sonarcloud.io, AWS in Frankfurt) and a United States region (sonarqube.us, AWS in Northern Virginia); the region is chosen at sign-up and cannot be changed later. | Sonar, SonarQube Cloud product page and “Choosing your region” documentation (sonarsource.com / docs.sonarsource.com), retrieved 2026-10-12 |
| Sending China-collected code and PII to an offshore tenant is a cross-border transfer. Where commits, issues or fixtures carry names, emails or real records, exporting them off the mainland engages PIPL Articles 38–40: notice, a separate consent, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. | Personal Information Protection Law of the PRC, Articles 38–40 — 21YunBox gov-doc summary, retrieved 2026-10-12 |
| CIIOs and high-volume handlers must store China-collected data in-country. The Cybersecurity Law's Article 39 (formerly Article 37 — renumbered by the 2025 amendment in force 2026-01-01, substance unchanged) requires personal information and important data generated in China to be stored in the mainland, with a security assessment before any export; an offshore SaaS tenant cannot satisfy this. | Cybersecurity Law of the PRC, Article 39 (formerly Article 37) — 21YunBox gov-doc summary, retrieved 2026-10-12 |
Sources verified by the 21YunBox compliance team on 2026-10-12.
For a mainland-China engineering team, the first thing to settle about SonarQube is that the question is not whether the dashboard paints quickly from Shanghai, or whether a scanner can reach the server. SonarQube is a code-quality and static-analysis platform, and what it holds is unusually concentrated: a full snapshot of your source code — a trade secret in its own right, and routinely carrying embedded credentials, tokens and personal data inside configs, fixtures and test records — and, computed from that code, its analysis findings. Those findings are the distinctive part. A SonarQube project is, in effect, a detailed map of your own software’s weaknesses: the vulnerabilities, the security hotspots, the exact files and lines where your defenses are thinnest. Run on an offshore tenant, that map of where you are exploitable — together with the code it was computed from and every contributor’s identity — comes to rest abroad. Where all of that is allowed to live is the real question, and it has two shapes: SonarQube Server, the self-managed software you install on infrastructure you choose, and SonarQube Cloud, the SaaS that Sonar hosts in a fixed set of offshore regions.
SonarQube in China at a glance
| What decides it | In Sonar's own terms — and China's law |
|---|---|
| What it holds — code and a vulnerability map | A SonarQube project is your source code plus the findings computed from it. The code is a trade secret and routinely carries credentials, tokens and personal data in configs, fixtures and test records. The findings are the sharper asset: a concentrated map of your own software's weaknesses — the vulnerabilities, security hotspots and exact lines where you are exploitable. Add every contributor's identity and you have IP, a security-sensitive dataset and personal data in one place. |
| Two deployment shapes | SonarQube Server is self-managed: in Sonar's words, “you install, host, upgrade, back up, and secure the instance yourself (on-prem or in your own cloud),” and “You fully control where data lives.” SonarQube Cloud (formerly SonarCloud) is SaaS — “fully hosted and operated by Sonar” — offered only in a European region (sonarcloud.io, AWS in Frankfurt) and a United States region (sonarqube.us, AWS in Northern Virginia). No region is in mainland China, and the region cannot be changed later. |
| The findings are the distinctive second half | The half a reachability check never sees. SonarQube's output is not a brochure — it is an inventory of your exploitable surface, computed from code that itself holds secrets and personal data. Held on an offshore Cloud tenant, that vulnerability map and the source behind it rest abroad every working day. A page-load test cannot observe where that data lives, only whether a screen draws. |
| Residency & cross-border | Pushing a China team's code and the PII in its commits to an offshore tenant is a cross-border transfer (数据出境) under PIPL Articles 38–40 — notice, a separate consent, and one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification). For a critical information infrastructure operator or high-volume handler, Cybersecurity Law Article 39 (formerly Article 37) requires China-collected personal information to be stored in the mainland — which an offshore SaaS tenant cannot satisfy. |
| Sensitive PI & the ICP door | Where commits, issues or fixtures carry government IDs, financial or health records, that content can be sensitive personal information under PIPL Articles 28–29 — a risk to confirm against what your repositories actually hold. And any public, China-facing surface you stand up in front of SonarQube — a developer portal, a quality dashboard, documentation — is an internet information service carrying an ICP filing (备案) duty bound to mainland hosting. |
| Reachability is not the axis | Whether the server answers from the mainland is operational, not the compliance question. What decides it is where the code and findings live. Because SonarQube Server is self-hosted, there is a lawful lever: run the Server on in-country infrastructure so the code and findings stay resident, and deliver any China-facing developer surface compliantly — the 21YunBox Optimizer — in front of what you already run. |
What it actually holds — your code and the map of its weaknesses
SonarQube is not a brochure site; it is the working home of two sensitive things at once. The first is your source code: a full snapshot pulled in for analysis, itself a trade secret, and routinely carrying embedded credentials, API keys and tokens, plus personal data inside configuration files, fixtures and test records. The second is what SonarQube computes from that code — and this is where it differs from a plain repository. Its analysis produces a concentrated map of your own software’s weaknesses: the bugs, the code smells, and above all the vulnerabilities and security hotspots, located to the exact file and line. A SonarQube project tells a reader precisely where your defenses are thin. In the wrong hands offshore, that is not merely intellectual property leaking — it is a ready-made target list.
Wherever commits, tickets or fixtures name or depict a person, they are personal information under China’s Personal Information Protection Law, and where they include government IDs, financial or health data they may be sensitive personal information. Whether that combined store of code, findings and contributor identities lives in the mainland or offshore is decided by which SonarQube you run and where you run it.
The doors: residency, cross-border, sensitive PI and ICP
Point a China team at an offshore SonarQube Cloud tenant and the first door opens. The code pushed for analysis, the findings derived from it, and the contributor identities around them rest abroad, which makes it a cross-border transfer (数据出境). The duty lands on you, the handler, not on Sonar: PIPL Articles 13 and 23 require notice and a basis to collect the data, and Articles 38–40 require a transfer mechanism to send it offshore — a CAC security assessment, the CAC standard contract, or certification — with a separate consent for the overseas transfer.
For some handlers, storage is not a matter of mechanism at all — it must stay in-country. If your organization operates critical information infrastructure, or handles personal information at scale, the Cybersecurity Law’s Article 39 (formerly Article 37 — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, its substance unchanged) requires personal information and important data generated in China to be stored in the mainland, with a security assessment before any export. An offshore SaaS tenant with no mainland-China region structurally cannot meet that duty.
A quieter, sharper door is the sensitivity of the data. Where the code or its fixtures carry real government IDs, financial records or health data, that content can be sensitive personal information under PIPL Articles 28–29, which demand a specific purpose, heightened necessity and separate consent. And a third door follows from publishing: the moment you expose a public, China-facing surface in front of SonarQube — a developer portal, a shared quality dashboard, or documentation your mainland users reach — that surface is an internet information service and carries an ICP filing (备案) duty bound to a mainland hosting resource.
Why a reachability check misses this
A probe from inside China can watch the SonarQube dashboard load, or a scanner submit a report, and conclude “it works.” That answer is beside the point. The compliance exposure is not on the screen — it is in the data at rest and how it moves: the source snapshot, the vulnerability findings computed from it, and the contributor identities, all sitting on an offshore tenant in a region Sonar lists as the EU or the US — never mainland China. A page-load test measures none of that. It cannot see which region the data lives in, whether separate consent was taken, whether a transfer mechanism is in place, or that a China-facing dashboard needs an ICP filing.
There is a second trap specific to this kind of platform. Making the offshore server merely reachable — even pointing a self-hosted scanner or CI runner inside China at it — does not move any of the regulated data in-country. A scanner only reads your code and submits results; the project, the full source snapshot, the issue history and the Quality Gate findings still live wherever the Server or the Cloud tenant runs. The control plane is what holds the data, and a runner is not the control plane. That is the competitor-proof second half of the question — and it is why keeping the regulated code and findings in-country, not merely reachable, is the answer.
The lawful path — map, localize, deliver
There is a compliant way to run SonarQube for a mainland-China team, and because SonarQube Server is self-hosted it sits on the platform you already use — no rebuild, no migration off SonarQube.
First, map: our China compliance team inventories what your SonarQube footprint holds — the source repositories pulled in for analysis, the vulnerability and security-hotspot findings, the secrets and personal data that ride along in configs and fixtures, the contributor identities, and any China-facing dashboard or portal — establishes which SonarQube you run today and where its control plane rests (an offshore Cloud region, or a Server instance), and the consent and residency basis each flow relies on. We build the technical picture; the legal conclusions are settled with counsel.
Then localize: run SonarQube Server on in-country infrastructure so the code, the findings and the secrets come to rest on mainland soil, keep the project and its analysis history resident rather than on an offshore Cloud tenant, obtain the Article 13/23 notice and separate consent, treat any government IDs or financial data in fixtures as sensitive personal information, and minimize the personal data that enters the codebase in the first place. Localize means standing up a lawful, in-country SonarQube — never a route that ships the code offshore anyway, and never any form of circumvention.
Then deliver: any public, China-facing surface in front of the platform — a developer portal, a quality dashboard, or documentation your mainland users reach — is an internet information service, so it carries an ICP filing duty and needs compliant, in-country delivery. 21YunBox delivers it in-country — the 21YunBox Optimizer — in front of what you already run, so it serves your users in China legally and compliantly. 21YunBox never uses or suggests circumvention of any kind — we keep in-country what the law says must stay, deliver the rest compliantly from inside the mainland, and never move personal information or source code across the border by stealth. 21YunBox is a compliance overlay and partner to the SonarQube you already run, not a competitor to it.
None of this is a verdict that SonarQube is “blocked” or “illegal” in China. It is a residency-and-consent map, and which duties bite your case turns on your entity, your role under Chinese law, your data volumes, and what your repositories and findings actually hold — worth settling the specifics with counsel before your China team’s code and its vulnerability map depend on it.
Related reading:
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law (data localization, Article 39)
- China’s Personal Information Protection Law (PIPL)
- How to get an ICP filing for China


