Does GitHub Work in China? Data Residency, Localization & PIPL Cross-Border
GitHub (Microsoft-owned source control, Actions CI and Packages) stores GitHub.com data in the USA by default, and GitHub Enterprise Cloud's data-residency regions are EU, Australia, US and Japan — none in mainland China — so repositories, CI logs and secrets rest offshore. A compliance-first look at GitHub data residency, localization and PIPL cross-border transfer.
Does GitHub work in China?
Whether GitHub "works" in China is a data-residency question about your source code, CI logs and secrets — not whether git push connects.
GitHub.com stores repositories, GitHub Actions logs and encrypted secrets in the USA by default, and GitHub Enterprise Cloud's data-residency product (GHE.com) adds EU, Australia, US and Japan regions — but no mainland-China region exists to select. So your source code — a core trade secret that routinely carries embedded credentials and the personal information in commits, issues and test fixtures — comes to rest offshore: a PIPL cross-border transfer wherever China personal information is in scope, and a data-localization duty a CII operator or high-volume handler cannot meet on an offshore cloud. The lawful lever is GitHub Enterprise Server, GitHub's self-hosted edition, which runs on your own infrastructure — including on mainland-China soil — so the code, secrets and logs stay in-country.
This maps exposure; it is not a legal ruling — your duties turn on your entity, data volumes and role. Our China team can map your exposure →
What GitHub's own documentation says about China
| Fact | Primary source |
|---|---|
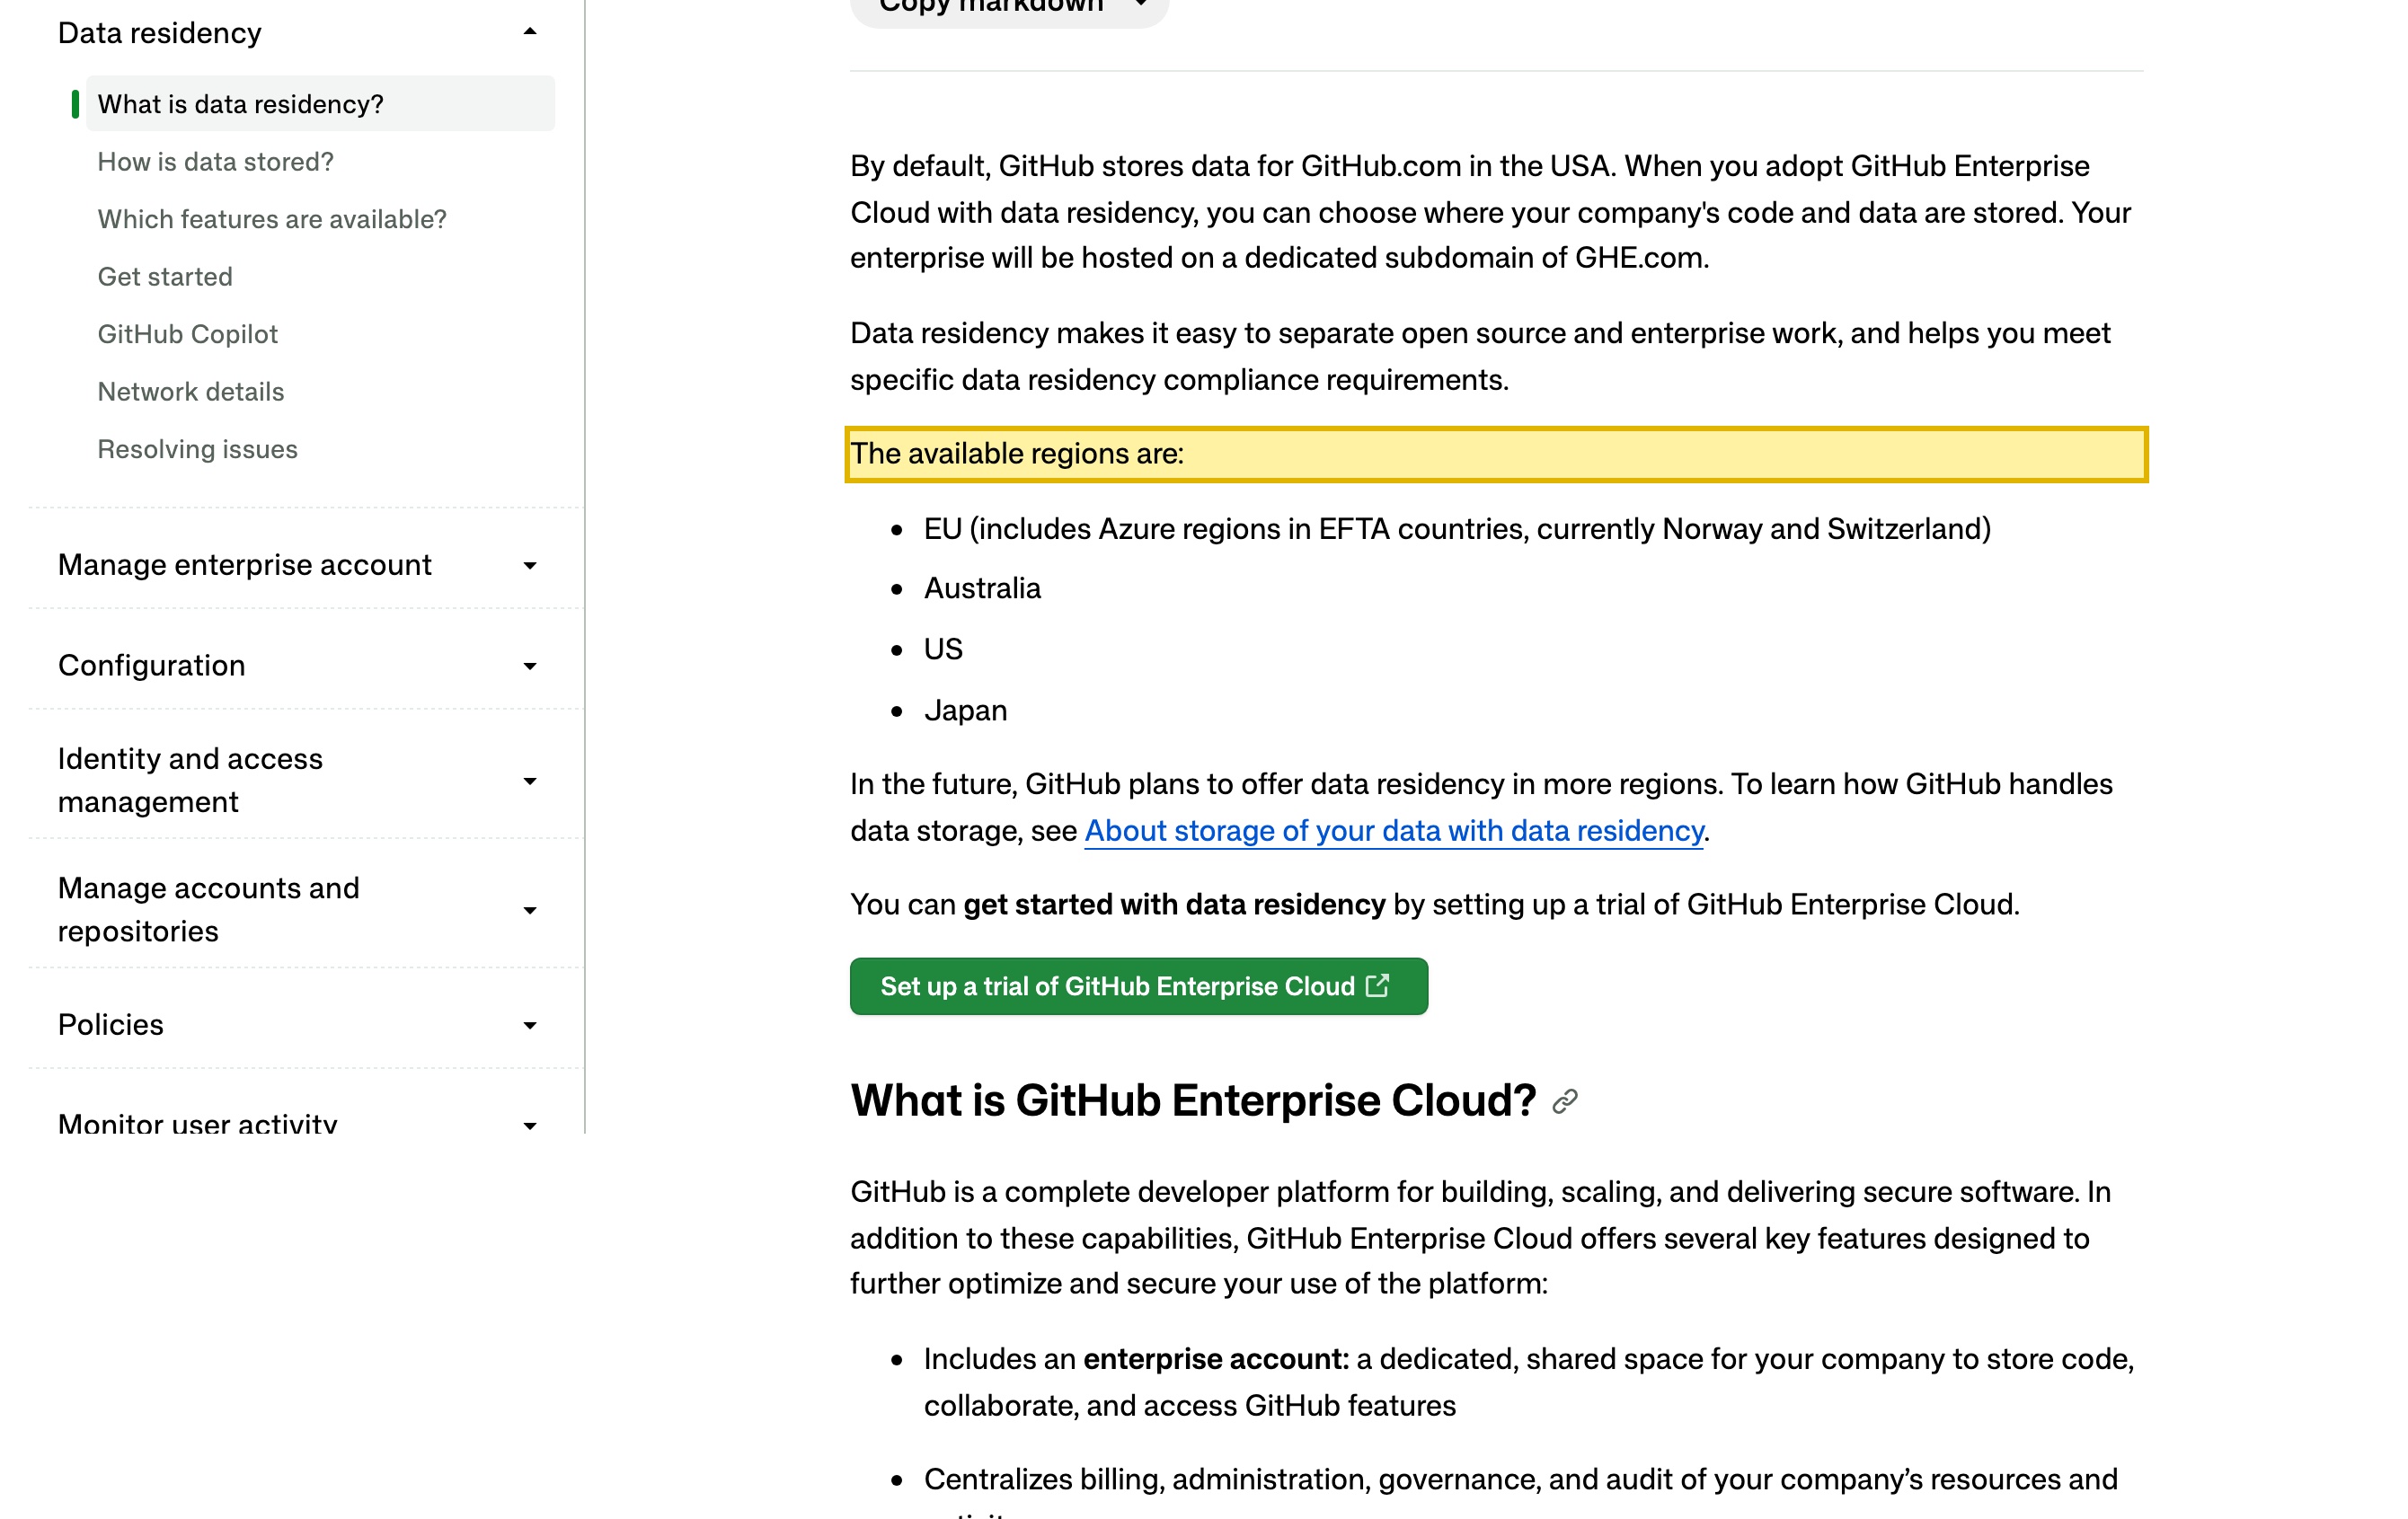
| GitHub Enterprise Cloud's data-residency regions are EU, Australia, US and Japan — none in mainland China. GitHub's documentation states that "By default, GitHub stores data for GitHub.com in the USA," and that its data-residency product, hosted on a dedicated subdomain of GHE.com, lets you choose among those four regions, with more regions promised but none announced for the mainland. So repositories, GitHub Actions logs and secrets rest offshore of China on both GitHub.com and GitHub Enterprise Cloud. | GitHub Docs — About GitHub Enterprise Cloud with data residency, retrieved 2026-10-10 |
| GitHub's lawful in-country lever is GitHub Enterprise Server (GHES), its self-hosted edition. GitHub's documentation describes GHES as "a self-hosted version of the GitHub platform" that "runs on your infrastructure and is governed by access and security controls that you define," distributed as a self-contained virtual appliance you can deploy in your own datacenter or on a public cloud. Because it runs where you provision it, you can place it on mainland-China infrastructure so the code, logs and secrets stay in-country — GitHub positions it for "enterprises that are subject to regulatory compliance." | GitHub Docs — About GitHub Enterprise Server, retrieved 2026-10-10 |
| Pushing China-origin code or personal information to an offshore GitHub tenant is a cross-border transfer under PIPL. Where repositories, commit history, issues or test fixtures carry the personal information of people in China, PIPL Articles 38–40 require notice, separate consent, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification — on top of the trade-secret exposure of the source code itself. | PIPL Articles 38–40 (Personal Information Protection Law) |
| A CII operator or high-volume handler must keep China personal information on the mainland. PIPL Article 40 and Cybersecurity Law Article 39 (formerly Article 37) impose in-country storage — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39 (substance unchanged). An offshore GitHub tenant with no mainland-China region structurally cannot satisfy that duty; a self-hosted instance inside China can. | PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a team serving mainland China, the deciding question about GitHub is not whether git push connects or whether github.com loads — both are routine, and github.com is reachable from the mainland, if sometimes throttled. It is where the assets GitHub holds are allowed to come to rest. GitHub — Microsoft-owned source control, GitHub Actions CI, and Packages — stores your repositories, build logs, artifacts and encrypted secrets wherever your plan hosts them. That content is among a company’s most sensitive: source code is a core trade secret, and it routinely carries embedded credentials and keys, plus the personal information that lands in commit history, issues, and test fixtures. On GitHub.com that data rests in the USA by default; GitHub Enterprise Cloud’s data-residency product adds EU, Australia, US, and Japan regions — but none inside mainland China. The self-hosted GitHub Enterprise Server is the in-country lever we return to below.
GitHub in China at a glance
| What decides it | In GitHub's own terms — and China's law |
|---|---|
| Where the code, logs and secrets physically rest (the region reality) | GitHub's own docs: "By default, GitHub stores data for GitHub.com in the USA." GitHub Enterprise Cloud with data residency (GHE.com) lets you choose a region, but the available regions are EU, Australia, US and Japan — none in mainland China. So repositories, GitHub Actions logs and secrets on either product come to rest offshore. |
| What GitHub holds, and why it is personal information | Repositories (your source code — a trade secret), GitHub Actions build logs and artifacts, and encrypted secrets. Source code routinely embeds credentials and keys, and commit history, issues, pull requests and test fixtures carry names, emails and sometimes real customer data — personal information under PIPL. Where it rests is a legal question, not a performance one. |
| Your China developers' pushes when the tenant is offshore | When code or the personal information inside it originates with people in China and rests in an offshore GitHub tenant, you are making a cross-border transfer under PIPL (Articles 38–40): notice, separate consent, and one transfer mechanism — a CAC security assessment, the standard contract, or certification. |
| The in-country storage duty (CIIO / high-volume handler) | A critical-information-infrastructure operator or high-volume handler must keep China personal information on the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged). An offshore GitHub tenant with no mainland-China region structurally cannot meet it. |
| Reachability is not the axis (and the China-facing surface) | That github.com loads from China is a delivery matter, not the legal test; data-at-rest residency is. The lawful levers are to run GitHub Enterprise Server — GitHub's self-hosted edition — on mainland infrastructure, and to put any China-facing surface (code-review portals, GitHub Pages, internal developer sites) on ICP-filed delivery. |
Where the data actually rests
GitHub comes in three shapes, and they answer the residency question differently. GitHub.com is the multi-tenant service most teams use; GitHub’s documentation states plainly that “By default, GitHub stores data for GitHub.com in the USA.” GitHub Enterprise Cloud with data residency — hosted on a dedicated subdomain of GHE.com — lets you choose where “your company’s code and data are stored,” but GitHub’s own list of available regions is EU, Australia, US and Japan, with more regions promised and none announced for the mainland. For a team whose obligation is that China data stay in China, neither option offers a region that satisfies it: the repositories, Actions logs, artifacts and secrets rest offshore.
The third shape changes the picture. GitHub Enterprise Server (GHES) is, in GitHub’s words, “a self-hosted version of the GitHub platform” that “runs on your infrastructure and is governed by access and security controls that you define.” GitHub distributes it as a self-contained virtual appliance you provision yourself — on a hypervisor in your own datacenter, or on a public cloud (GitHub lists AWS, Google Cloud and Microsoft Azure) — which means you can place it on mainland-China infrastructure. The software is not blocked anywhere; it runs where you deploy it. That is the in-country lever.
What it holds is personal information — and trade secrets
A source-control and CI platform concentrates a company’s crown jewels. The repositories hold your source code — a core trade secret — and that code routinely carries embedded credentials, API keys and connection strings, whether in configuration, fixtures or history. GitHub Actions adds build logs and artifacts and the encrypted secrets your pipelines use. And the collaboration layer — commit authorship, issues, pull requests, and the test data checked into a repo — routinely contains names, emails and, where real datasets are used in fixtures, actual customer records. Much of that is personal information under PIPL, some of it sensitive.
That is why residency, not reachability, is the test. When code or the personal information inside it originates with people in China and comes to rest in an offshore GitHub tenant, you are making a cross-border transfer, and PIPL Articles 38–40 govern it: notice, separate consent, and one lawful transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. The security-assessment measures set when that assessment is mandatory rather than optional.
On top of the transfer rules sits a harder duty. A critical-information-infrastructure operator or high-volume handler must store China personal information inside the mainland — PIPL Article 40 and the data-localization rule in Cybersecurity Law Article 39 (formerly Article 37). An offshore GitHub tenant, by definition, keeps that data out of the country, so it cannot satisfy the duty.
Running it on a no-China-region cloud doesn’t meet the residency duty — and what does
The fix is not to make an offshore GitHub endpoint reachable from China. Reachability was never the problem; residency is. If your obligations require China-origin code, or the personal information inside your repositories and pipelines, to stay on the mainland, the lawful lever is to run the platform in-country.
That is exactly what GitHub Enterprise Server allows. Because GHES runs on infrastructure you control, you can deploy it on mainland-China soil — a hypervisor in an in-country datacenter, or a licensed in-country cloud region — so the repositories, Actions logs, artifacts and secrets stay inside the border. GitHub itself positions GHES for “enterprises that are subject to regulatory compliance.” This is not a re-platforming project: you keep the GitHub workflows your developers already know and place the instance where the data must live, then put any China-facing surface — the code-review and developer portals, internal docs, or GitHub Pages sites your mainland users open — on ICP-filed, in-country delivery in front of it. Localize means an in-country deployment, not a tunnel back to an offshore endpoint.
This page maps exposure; it is not a legal ruling. Your actual duties turn on your entity, how you classify the data, your transfer volumes and whether you are a critical-information-infrastructure operator — so settle those specifics with qualified China counsel before you rely on any single path.
The lawful path — map, localize, deliver
21YunBox is a compliant overlay, not a migration — and a partner to GitHub and to your platform team, not a competitor to them.
- Map. We read the PIPL cross-border, data-residency, data-localization (CII) and ICP obligations against your entity, your data volumes and whose personal information actually lands in your repositories, issues and pipelines — so you know which duties bite before you move anything.
- Localize. We run the platform in-country so the code, secrets and logs stay on mainland soil — a self-hosted GitHub Enterprise Server deployment on mainland-China infrastructure, or a licensed in-country equivalent — and keep consented, in-country storage for what must stay. For GitHub.com or GHE.com, which offer no mainland-China region, localize means standing up that lawful in-country instance, not a tunnel to the offshore endpoint.
- Deliver. Any China-facing surface in front of the platform — the developer and code-review portals, internal documentation, and GitHub Pages sites your mainland users hit — runs over ICP-filed, in-country delivery (the 21YunBox Optimizer), in front of the stack you already run. No rebuild, no second codebase.
The result is a source-control and CI platform that runs legally and compliantly for your users in China. 21YunBox never uses or suggests circumvention of any kind.
Related reading
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law and data localization
- China’s data-export security assessment measures
- How to get an ICP license for a website in China


