Does Helm Work in China? Data Residency, ICP & Cross-Border Rules
Your private Helm charts are proprietary deployment packaging carrying configuration values and secret references; on an offshore chart repository they sit abroad — a data-residency and PIPL cross-border question, not a reachability one. A self-hosted in-country chart repository keeps them resident.
Does Helm work in China?
The question that decides Helm in mainland China is not whether a cluster can install a public chart — it is where your private charts live and what they carry. Helm is open-source tooling you run yourself, so the residency question is the chart repository behind it: your private charts are proprietary deployment packaging that describes your application topology and carries configuration values and references to your cluster's Secrets.
Hosted on an offshore chart repository or OCI registry, that packaging and those secret references sit outside the mainland, and your China cluster's chart supply chain — what it installs, with what provenance and integrity — resolves across the border. That makes it a data-residency and PIPL cross-border transfer question (Articles 38–40: notice, a separate consent, and a transfer mechanism), and for a critical information infrastructure operator the Cybersecurity Law's Article 39 (formerly Article 37) adds an in-country storage duty an offshore repository cannot meet. A reachability check never sees any of this, because the charts keep installing.
Because Helm's own docs describe a chart repository as an ordinary HTTP server you can run yourself, there is a genuine in-country path: 21YunBox maps where your private charts, values and Secrets live, stands up a self-hosted in-country chart repository (ChartMuseum, Harbor, or an OCI registry you host) with ICP-filed delivery in front of it, and keeps your China deployment's chart supply chain resident — no rebuild, and never any circumvention. Treat the specifics as a risk to confirm with counsel.
What Helm's own documentation says about China
| Fact | Primary source |
|---|---|
| A Helm chart is your deployment packaging, and it carries configuration values. Helm's documentation states: “A chart is a collection of files that describe a related set of Kubernetes resources,” and that “Chart developers may supply a file called values.yaml inside of a chart. This file can contain default values.” That packaging describes your proprietary application topology and references the config and Secrets your deployment uses. | Helm Docs, “Charts” (helm.sh/docs/topics/charts), retrieved 2026-10-13 |
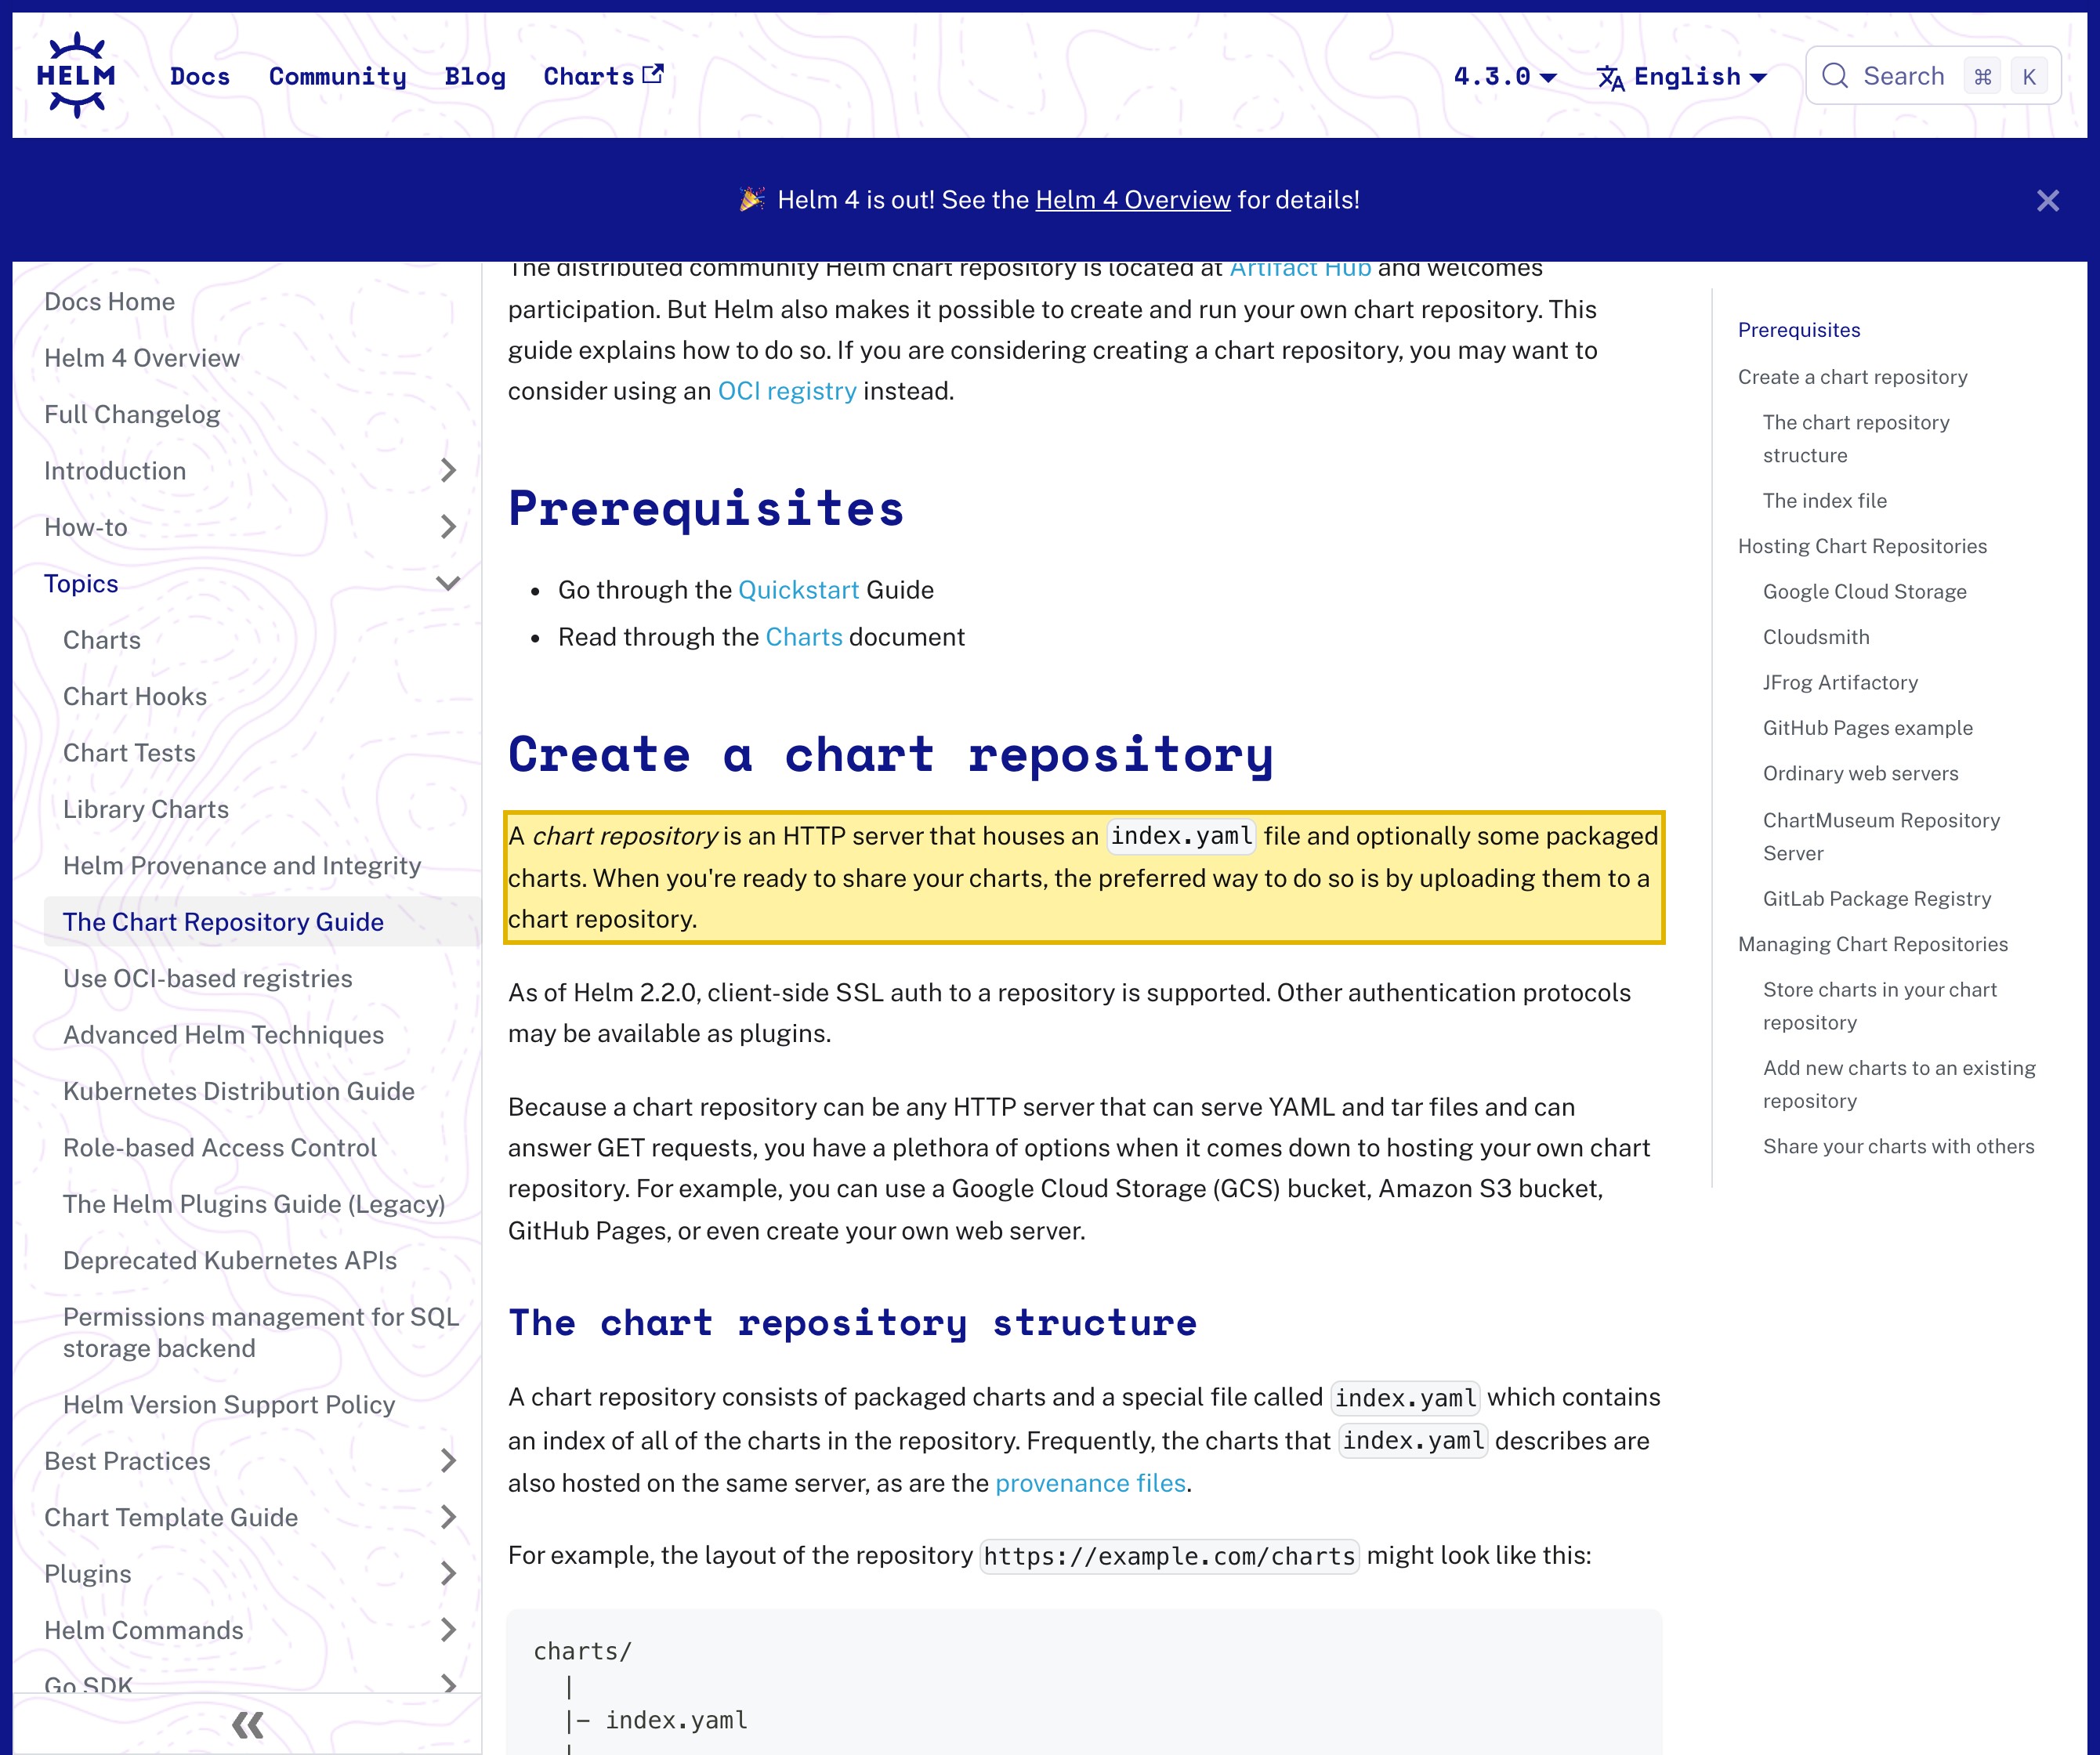
| A chart repository is an ordinary HTTP server, and Helm lets you run your own. Helm's Chart Repository Guide states: “A chart repository is an HTTP server that houses an index.yaml file and optionally some packaged charts,” and that “Helm also makes it possible to create and run your own chart repository.” Where that repository runs is where your private charts and their secret references reside. | Helm Docs, “The Chart Repository Guide” (helm.sh/docs/topics/chart_repository), retrieved 2026-10-13 |
| Charts, values and publishing metadata held offshore are a PIPL cross-border transfer. Any personal information in your China deployment's charts, values or release metadata — contributor identities, access logs — held on an offshore repository triggers PIPL Articles 38–40: notice, a separate consent distinct from product agreement, and one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification). | Personal Information Protection Law of the PRC, Articles 38–40, retrieved 2026-10-13 |
| A critical information infrastructure operator must keep China-collected data in the mainland. The Cybersecurity Law's Article 39 (formerly Article 37), as renumbered by the 2025 amendment in force 2026-01-01, requires personal information and important data collected and generated in the mainland to be stored there — a duty an offshore chart repository cannot meet. | Cybersecurity Law of the PRC, Article 39 (formerly Article 37), amended 2025, in force 2026-01-01, retrieved 2026-10-13 |
Sources verified by the 21YunBox compliance team on 2026-10-13.
For a mainland-China operation, the deciding question about Helm is not whether a cluster in Shanghai can install a public community chart — it is where your private charts live, what they carry, and on what legal basis they got there. Pulling open-source charts is a reachability topic, and not the one that decides whether your setup is defensible. Your private Helm charts are different: a chart is your deployment packaging — it describes your proprietary application topology (which Kubernetes resources run, and how they are wired) and carries the configuration values and the references to the Secrets your deployment uses. Helm itself is open-source tooling you run; what decides residency is the chart repository behind it. Hosted on an offshore chart repository, that packaging and those secret references sit abroad, and your China deployment’s chart supply chain — what it installs, with what provenance and integrity — resolves across the border. Residency and cross-border transfer, not install time, are what decide this.
Does Helm work in China? At a glance
| What decides it | What it means for mainland China |
|---|---|
| What your private charts hold | A chart is your proprietary deployment packaging: it describes your application topology and carries configuration values (values.yaml) plus references to the Secrets and config your deployment uses. |
| Where the chart repository runs | Helm is open-source tooling you run; your private charts live in a chart repository (an HTTP server) or an OCI registry. Hosted offshore, that repository sits outside the mainland (confirm your current hosting). |
| Data residency | For a CIIO or large-volume handler, personal information and important data collected in China must be stored in the mainland (Cybersecurity Law Article 39 (formerly Article 37)) — a duty an offshore repository cannot meet. |
| Cross-border transfer | Secret references, publishing metadata and any personal data inside charts or values, held offshore, are a PIPL cross-border transfer (Articles 38–40): notice, a separate consent, and one transfer mechanism. |
| Your deployment's supply chain | A China cluster that installs from an offshore repository runs its chart supply chain across the border. A registry mirror or cache speeds installs — it does not move your private charts or secrets in-country. |
| The residency lever | A self-hosted in-country chart repository (ChartMuseum, or Harbor / an OCI registry you host) keeps the private charts, their values and secret references resident. |
Door one — your private charts are proprietary packaging, and residency follows where they’re hosted
Start with what the repository holds, because that is what China’s law answers to. Pulling public community charts is a reachability topic, and not the part that decides this. Your private charts are the authoritative store of how your application is built and deployed: in Helm’s own words, “A chart is a collection of files that describe a related set of Kubernetes resources.” That packaging is a concentrated slice of your intellectual property — your application topology, your release wiring — and it carries configuration values and references to the Secrets your deployment uses. Helm documents that “Chart developers may supply a file called values.yaml inside of a chart. This file can contain default values,” and in practice those values files routinely hold the credentials, tokens and config a deployment needs.
Where that packaging is hosted is the point. Helm itself is open-source tooling you run; your private charts live in a chart repository — Helm defines one as “an HTTP server that houses an index.yaml file and optionally some packaged charts” — or in an OCI registry, which Helm also supports for storing and sharing chart packages. If that repository or registry runs offshore, your proprietary packaging and its secret references sit outside the mainland. If you are a critical information infrastructure operator, or you handle personal information at volume, personal information and important data collected and generated in China must be stored in the mainland, with a security assessment before any export — the Cybersecurity Law data-localization rule, Article 39 (formerly Article 37) as renumbered by the 2025 amendment in force 2026-01-01. An offshore repository holding your private charts and embedded secret references has no mainland footing to satisfy that.
Door two — secret references, publisher identities and supply-chain provenance
The second door is PIPL and the integrity of what your China cluster installs. A chart and the pipeline around it carry more than topology: the configuration values and secret references the deployment depends on, the usernames and email addresses of who packaged and promoted a release, access logs, and any personal data that finds its way into chart contents or values. Under the Personal Information Protection Law, holding that data on infrastructure outside the mainland is a cross-border transfer (Articles 38–40): the handler must give notice, obtain a separate consent for the transfer, and clear one mechanism — a CAC security assessment, the CAC standard contract, or certification. Minimizing the secrets and personal data that enter chart contents and values in the first place is part of the fix, but it does not move the store on its own. And because your China cluster installs its charts from wherever the repository runs, the provenance and integrity of what enters your China deployment are governed across the border too — a software-supply-chain exposure a connectivity check never surfaces.
Why a reachability check misses this
A “can my cluster install a chart from Shanghai” test answers the wrong question. A registry mirror or cache, or connectivity tuning, changes how fast and how reliably a chart resolves — it does not change where your private charts, their configuration values, their secret references and the install provenance actually live. So a setup can look perfectly healthy from inside China while every private chart, every secret reference baked into its values, and every publisher record still sits offshore. The residency and cross-border questions above are invisible to a reachability probe precisely because the charts keep installing — which is why the move that matters is moving the private chart repository in-country, not making the offshore one merely reachable or mirrored. We publish no first-party measurement of Helm chart-repository connectivity from inside China, so we put no figures here; it is something we would measure against your actual setup rather than assert.
This is a risk map, not a verdict: whether you need in-country storage, a transfer mechanism, a reworked consent flow, an ICP filing for any public-facing developer portal, or some combination depends on what your private charts and values carry, how much, and who your contributors are — worth settling with counsel before you build.
The lever — map, localize, deliver
Because Helm documents a chart repository as a server you can run yourself, there is a genuine in-country path, and 21YunBox never uses or suggests circumvention of any kind.
- Map — inventory which of your charts are private (your proprietary packaging), whether they embed configuration values and secret references, where that chart repository or OCI registry is hosted today, the residency basis, and how your China deployment’s chart supply chain crosses the border.
- Localize / govern — run the private chart repository in-country (self-hosted — ChartMuseum, or Harbor / an OCI registry you host in your own infrastructure), so the proprietary packaging and secret references stay resident; keep your China cluster’s supply chain in-country; and minimize what crosses the border.
- Deliver — put a compliant, in-country chart repository and image delivery in front of (or in place of) the offshore repository; 21YunBox stands up the in-country layer without a rebuild.
Making the public registry merely reachable or mirrored is not the answer — your private charts and secret references are still offshore, and installing them faster does not change that. Keeping the chart repository in-country is.
Where 21YunBox fits — a compliant overlay, not a migration
You keep using Helm. We add the piece an offshore chart repository cannot provide on its own: a lawful, in-country home for a self-hosted chart repository, so your proprietary charts, their configuration values and their secret references stay resident where the law requires, with compliant ICP-filed delivery for the developer access and any public-facing portal in front of it — placed around your existing setup, with no rebuild, no second codebase, and no migration off Helm. As a partner to the toolchain you already run, our China team maps your PIPL cross-border, consent and data-residency obligations against your entity and your pipeline, then stands up the in-country chart repository and delivery a defensible China presence needs. We never use or suggest circumvention of any kind.
Related reading:
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law and data localization
- How to get an ICP filing for China


