Does Jenkins Work in China? Data Residency, Localization & PIPL Cross-Border
Jenkins is open-source software you host yourself — including on mainland-China infrastructure, the lawful lever. The compliance question is where the controller runs: offshore, the source code, pipeline secrets and build state it holds rest abroad — a PIPL cross-border transfer for any China PII. A compliance-first look at where your CI/CD data is allowed to rest.
Does Jenkins work in China?
Whether Jenkins works in China is a data-residency question, not a reachability one — and the server itself is the lawful lever. Jenkins is a free, open-source automation server you host yourself, including self-hosted on a server inside mainland China; it is never "blocked."
Because Jenkins is residency-neutral, where its data comes to rest is decided by where you run the controller and its agents — not by the software. Self-host it in-country and your source code, the pipeline credentials Jenkins stores on the controller, your build logs and your infrastructure-as-code state stay on mainland soil. Host the controller offshore — on an offshore cloud, an offshore managed CI service, or the CloudBees distribution on offshore infrastructure — and all of it rests abroad: wherever China personal information sits in a commit, a CI log or a test fixture, that is a cross-border transfer PIPL governs (Articles 38–40), and for a critical-information-infrastructure operator or high-volume handler, a breach of the in-country storage duty (PIPL Article 40; Cybersecurity Law Article 39, formerly Article 37). Sovereign partitions exist to host it in-country — AWS China via Sinnet and NWCD, Azure China via 21Vianet — but each is a separate operator with its own account, ICP and feature gaps, so an in-country host is not automatic compliance.
This is a risk map, not a ruling — your obligations turn on your entity, your data volumes and whose personal information sits in your repositories and logs. Our China team can map your Jenkins data exposure with you →
What Jenkins's own documentation says about China
| Fact | Primary source |
|---|---|
| Jenkins is self-hosted, residency-neutral software — not a vendor-run cloud or a hosting location. Its own site calls Jenkins "the leading open source automation server" and "a self-contained Java-based program, ready to run out-of-the-box," and its installation guide notes that "Jenkins is typically run as a standalone application in its own process." You run the controller and build agents yourself, so where the code, logs and secrets come to rest is set entirely by where you deploy them — including self-hosted on mainland-China infrastructure, which keeps them on mainland soil (the lawful lever). Jenkins is a Continuous Delivery Foundation project; there is no vendor-run Jenkins SaaS, and the commercial distribution (CloudBees CI) is likewise deployed and operated. | Jenkins project — homepage and 'Installing Jenkins' guide, retrieved 2026-10-10 |
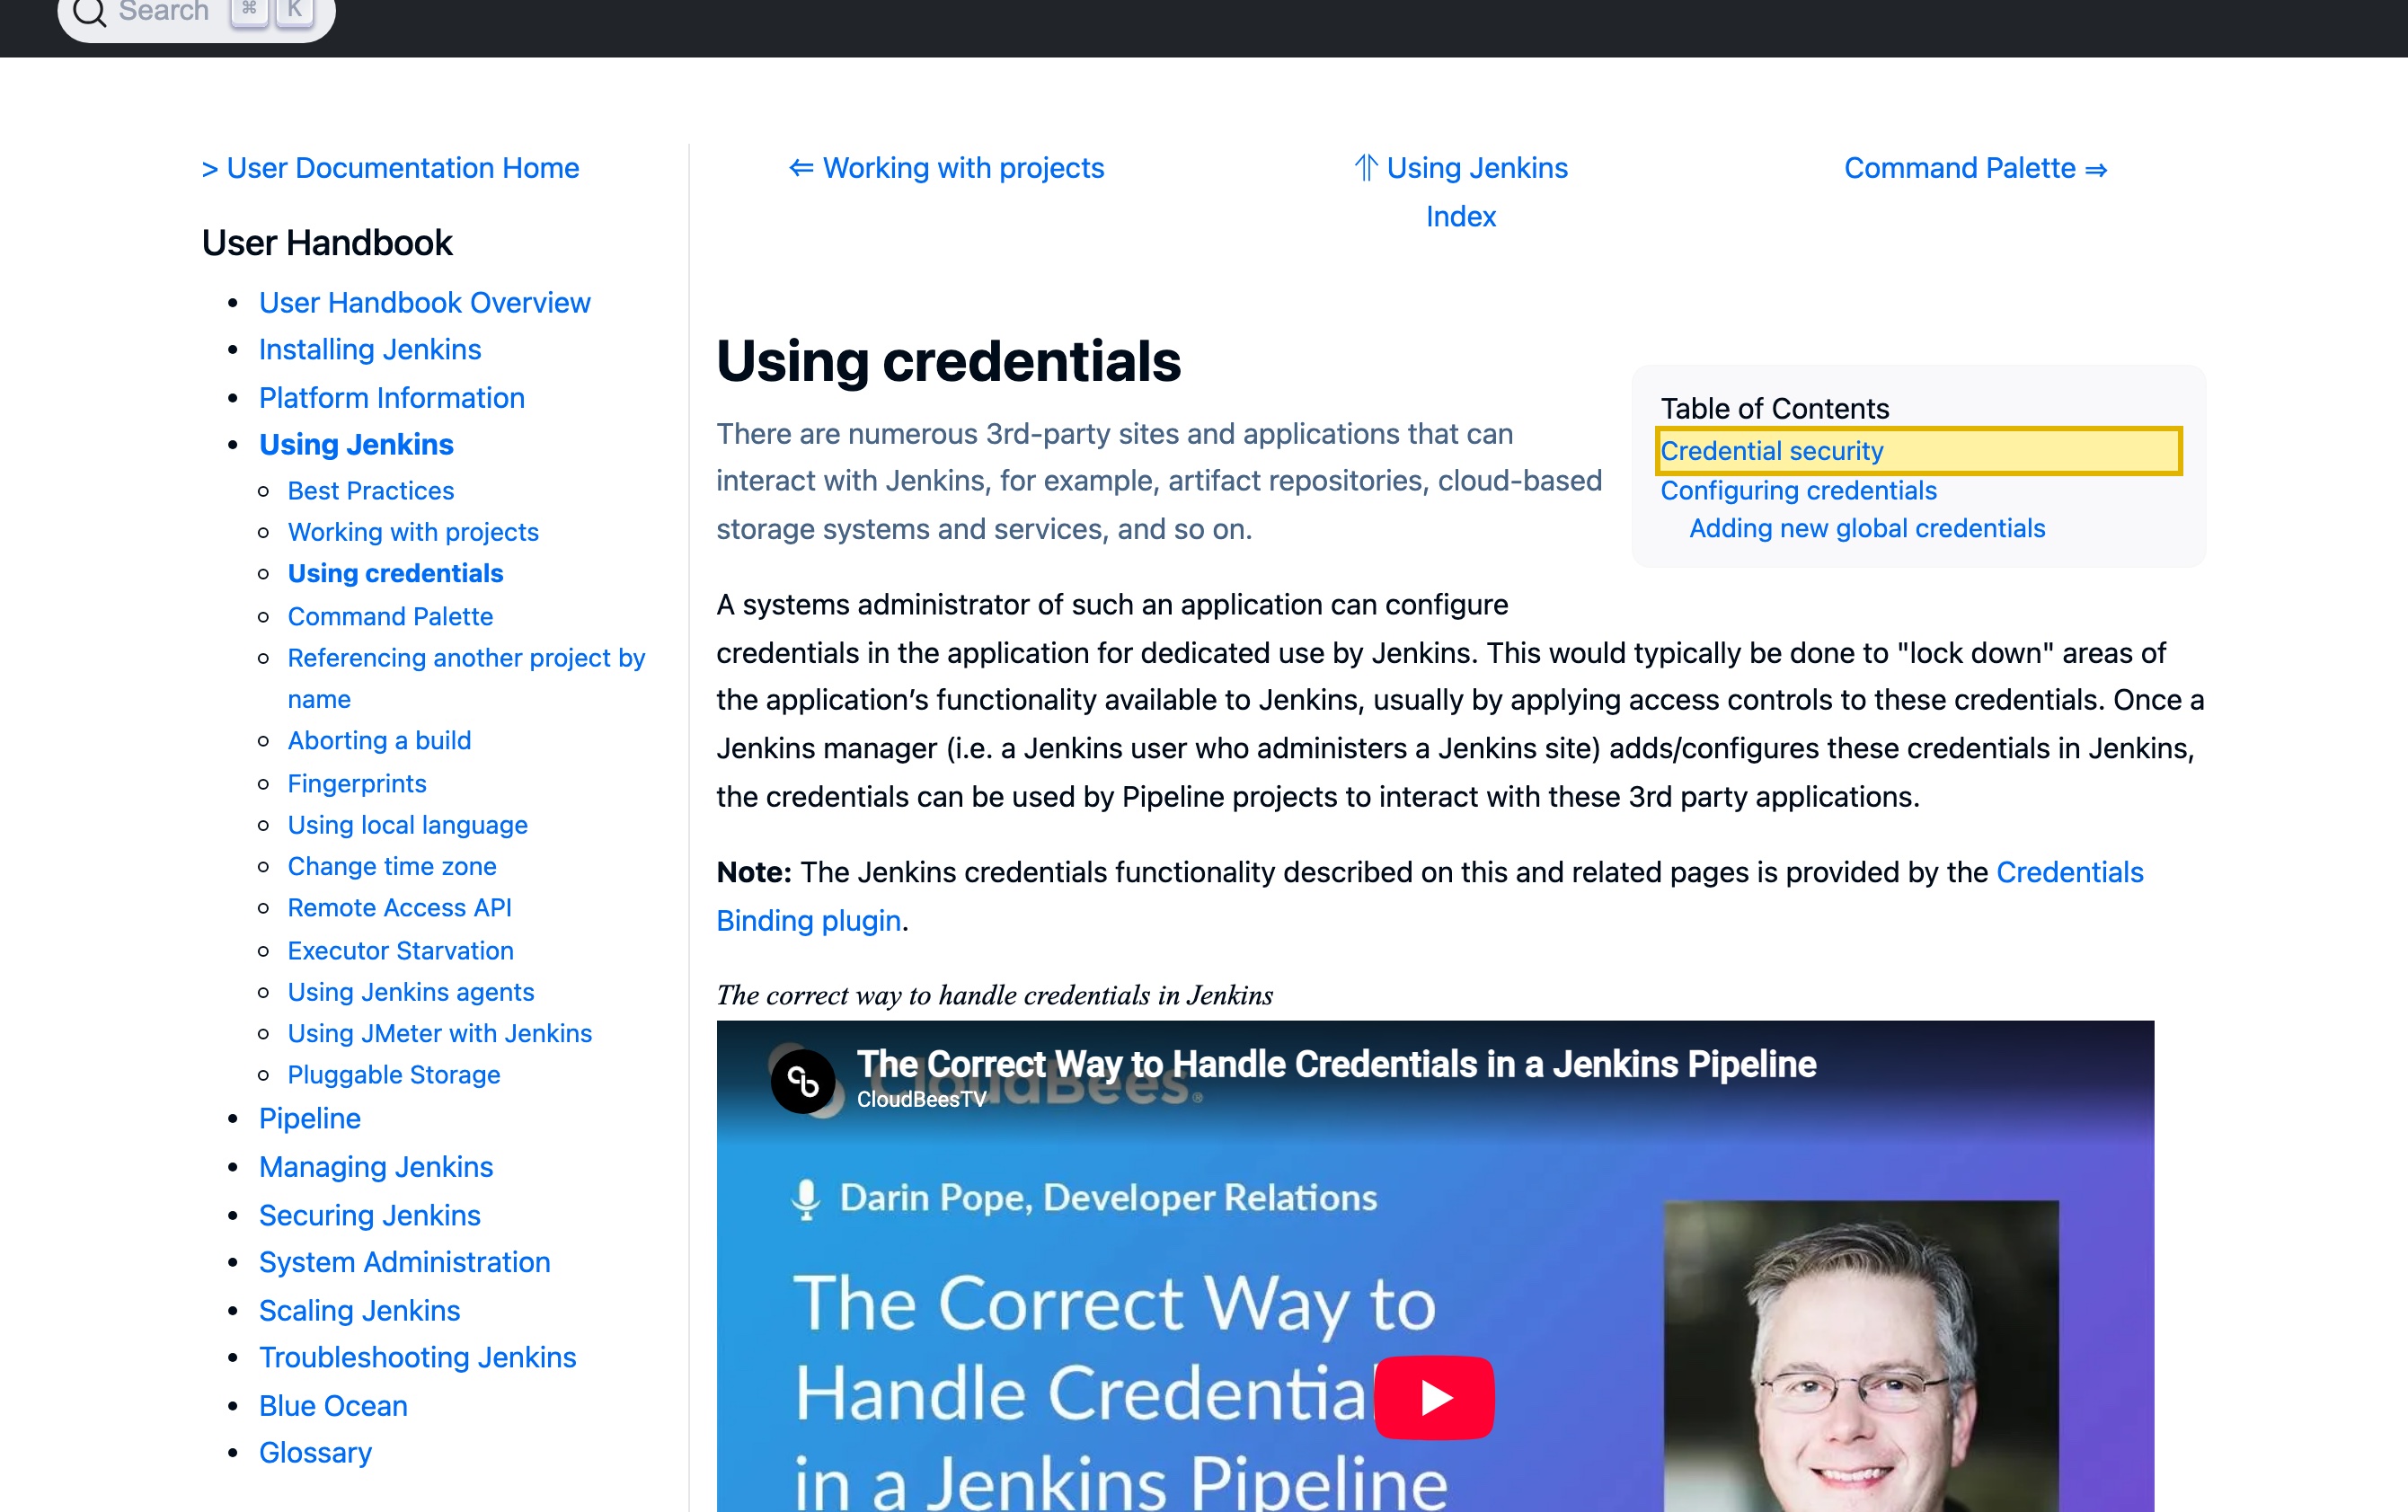
| Jenkins stores pipeline credentials and secrets on the controller you host. The Jenkins user documentation states that "Jenkins can store the following types of credentials" — secret text and API tokens, usernames and passwords, SSH keys and certificates — and that "credentials configured in Jenkins are stored in an encrypted form on the controller" (encrypted by the Jenkins controller ID). Those secrets, together with your source code, build logs and infrastructure-as-code state, rest wherever the controller runs: offshore they sit abroad, a residency gap; self-hosted in-country they stay on mainland soil. | Jenkins user documentation — Using credentials, retrieved 2026-10-10 |
| China personal information held on an offshore Jenkins controller is a cross-border transfer under PIPL. Where commit metadata, CI logs, tickets or test fixtures carry names, emails or customer data, storing them on a controller outside the mainland is an export PIPL governs — requiring notice, a separate consent, and one transfer mechanism (PIPL Articles 38–40), with a possible CAC security assessment above volume or sensitivity thresholds. The handler on the hook is you, the operator — not the open-source project. Source code itself is a trade secret exposed by the same offshore residency, independent of PIPL. | Personal Information Protection Law of the PRC, Articles 28 and 38–40 |
| CIIOs and high-volume handlers owe an in-country storage duty an offshore CI host cannot meet. Personal information and important data collected in the mainland must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39, formerly Article 37). The 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged. Because Jenkins runs identically in-country, self-hosting the controller on mainland infrastructure (or a licensed/sovereign in-country host) meets this duty without a migration. | PIPL Article 40; PRC Cybersecurity Law Article 39 (formerly Article 37) |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a team serving mainland China, the question about Jenkins was never whether it installs or runs. It does: Jenkins is “the leading open source automation server,” a self-contained Java program you download and run on your own machines — as readily on a server in Shanghai as on one in Virginia. What makes Jenkins a compliance question is not reachability but what it holds and where that comes to rest: your source code — a trade secret, and routinely the place credentials, keys and real data end up embedded in configs, fixtures and tests — the pipeline secrets Jenkins stores on its controller, your build logs and artifacts, and the infrastructure-as-code state that maps your whole topology. Jenkins itself is residency-neutral. The Continuous Delivery Foundation ships an automation server, not a hosting location, and where all of that rests is decided entirely by where you run the controller and its agents — self-hosted in-country, it stays on mainland soil; on an offshore host, it sits abroad.
Jenkins in China at a glance
| What decides it | In Jenkins's own terms — and China's law |
|---|---|
| Where the code, secrets and state physically rest | Jenkins is residency-neutral: its own site calls it "the leading open source automation server," a "self-contained Java-based program" you run yourself. It has no region of its own — where your source, secrets and build state rest is set by where you host the controller and its agents: self-hosted on mainland infrastructure, or offshore. Jenkins ships no vendor-run SaaS; the commercial distribution (CloudBees CI) is likewise deployed and operated, and on an offshore cloud the same residency gap applies. |
| What it holds, and why it's personal information | A CI/CD controller concentrates a company's most sensitive assets: source code (a trade secret), the pipeline credentials and API tokens Jenkins stores on the controller, build logs and artifacts, and infrastructure-as-code state that maps your topology and often holds secrets in plaintext. Where commits, test fixtures, CI logs or tickets carry names, emails or customer data, that is personal information under PIPL — and a single fixture or log can hold Article 28 sensitive personal information (financial, government-ID, precise-location or health fields). |
| Your mainland data in the system | Source, secrets and any China personal information collected in the mainland and held on an offshore Jenkins controller are a cross-border transfer PIPL governs: notice, a separate consent, and one transfer mechanism (PIPL Articles 38–40). The handler on the hook is you, the operator — not the open-source project. |
| In-country storage duty | A critical information infrastructure operator or high-volume handler owes an in-country storage duty an offshore CI host cannot meet — mainland personal information and important data must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged. |
| Is it reachable? | Treat reachability as the delivery half, not the question — the server runs fine in-country; only pulling the installer or plugins and any offshore pipeline dependencies are delivery matters. The lawful lever is to run the controller in-country (self-hosted, or a licensed/sovereign option), and any China-facing surface in front of it — a deployed app, a developer dashboard — needs an ICP filing tied to a mainland hosting resource (State Council Order No. 292; MIIT Order No. 33). |
Where the code, secrets and state actually rest
Jenkins does not have a region; your controller does. The automation server is the same bits whether it runs in Frankfurt, Singapore or Shanghai, so the residency question is entirely about the host you put the controller and its agents on.
On an offshore host — a controller you run on an offshore cloud, an offshore managed CI service, or the commercial CloudBees distribution deployed on offshore AWS or GCP — that host is outside the mainland. Point your pipelines there and your source code, the credentials Jenkins stores, your build logs and your infrastructure-as-code state all come to rest abroad; wherever any of it is China personal information, the Personal Information Protection Law treats that as a cross-border transfer, and the handler responsible is you.
In-country options genuinely exist, and they are the lawful lever. You can self-host Jenkins on mainland infrastructure, where the server runs identically. And the large foreign clouds reach China only through separate sovereign partitions — AWS China (the Beijing region operated by Sinnet and the Ningxia region operated by NWCD) and Azure China (operated by 21Vianet) are distinct clouds with their own accounts, their own ICP, and their own feature and availability gaps — on which you can stand up the controller in-country. An in-country host is not automatic compliance; it is the starting point for it.
What it holds is personal information — and trade secrets
A CI/CD system earns this scrutiny because of what it concentrates. Unlike a tool that touches one slice of your data, the Jenkins controller is where several of your most sensitive assets sit together: your source code — itself a trade secret, and routinely the place credentials, API keys and real data end up embedded in configuration, fixtures and test data — and the pipeline secrets Jenkins holds. By its own documentation, “Jenkins can store the following types of credentials,” and “credentials configured in Jenkins are stored in an encrypted form on the controller.” Add the build logs and artifacts a run produces and the infrastructure-as-code state that maps your whole topology, often with secrets in plaintext, and the controller becomes a single place where code, secrets and state converge.
Much of that is personal information under PIPL the moment it identifies a person — the names and emails in commit metadata and tickets, the customer rows that find their way into test fixtures and CI logs — and some of it is Article 28 sensitive personal information (financial records, government-issued IDs, precise location, biometric or health data), which carries a higher bar of specific purpose, strict necessity, and separate consent.
That is why residency is not merely good hygiene here. For a critical information infrastructure operator, and for a handler whose volumes cross the regulators’ thresholds, personal information and important data collected in the mainland must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). An offshore controller structurally cannot satisfy that duty — the code, logs and secrets are, by definition, in the wrong country. And where an export is permitted at all, crossing a volume or sensitivity threshold can trigger a CAC-led data-export security assessment before any of it lawfully leaves.
Running the controller offshore doesn’t meet the residency duty — and what does
The honest summary is narrow and important: nothing about Jenkins is off-limits, and you do not need to abandon it. The exposure is not the software; it is a deployment that parks your source, your secrets and your build state outside the mainland. Fix where the controller runs and the exposure closes.
The lawful lever is to run the same Jenkins in-country. Self-hosted on mainland infrastructure, or on a licensed domestic or sovereign-cloud host, the server behaves exactly as it does abroad — same jobs, same pipelines, same plugins, same credential store — so the code, logs and secrets China requires to stay in-country do, with no rewrite and no second pipeline. Pointing a mainland pipeline back at an offshore controller is not localization and does not meet the storage duty; standing up a lawful in-country controller is. Where a pipeline must still reach an offshore dependency — a source mirror, an artifact registry, a managed runner — you keep that flow minimized, consented, and backed by a transfer mechanism, and any China-facing surface in front of the system earns its own ICP filing.
This is a risk map, not a verdict. Whether you owe in-country storage, a transfer mechanism, a separate consent, an ICP filing, or some combination turns on your entity, your data volumes, how much of what your repositories and logs hold is personal or sensitive, and who your users are — and it is worth settling with counsel before you decide where a single mainland credential or commit comes to rest.
The lawful path — map, localize, deliver
You do not have to drop Jenkins to run it lawfully for mainland China. 21YunBox is a compliant overlay, not a migration — and, for an open-source automation server you already run, a partner that sits alongside your stack, not a competitor to it. There are three moves, and they fit together.
Map. Our China compliance team reads your PIPL cross-border, data-residency and data-localization (CII) obligations against your actual entity, your data volumes, and whose personal information sits in your repositories, logs and credential store — so the exposure is written down before anything moves.
Localize. Because the risk is where the code, secrets and state rest, we run the controller and its agents in-country — self-hosted on mainland infrastructure, or on a licensed domestic or sovereign-cloud host — so the source, pipeline secrets and build state China requires to stay on mainland soil do. Localize means a lawful in-country deployment of the same Jenkins, never a tunnel back to an offshore controller; only the minimized, lawfully transferable subset ever crosses.
Deliver. For any China-facing surface in front of the system — the application your pipeline ships to mainland users, the developer dashboard your in-country teams reach — the 21YunBox Optimizer provides ICP-filed, in-country delivery, in front of the stack you already run. No rebuild, no second codebase. 21YunBox never uses or suggests circumvention of any kind; the entire point is a lawful, filed, in-country path.
The goal is plain: your Jenkins pipelines run legally and compliantly for your users in China.
Related reading:
- How to get an ICP filing for China
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law and data localization
- China’s data-export security assessment measures


