Does ON24 Work in China? Attendee Data, PIPL & Data Residency
ON24 is a hosted webinar and digital-engagement platform: it collects your attendees' registration and behavioral data and stores it on its US-based cloud, with no mainland-China data region. Serving a mainland audience ships their personal information across the border under PIPL — and you, not ON24, are the handler. A compliance-first look at the data-residency door.
Does ON24 work in China?
Yes — ON24 runs, and your mainland audience can join a webinar. But ON24 is a US-hosted platform: the moment a China-based attendee registers, their personal data lands on ON24's American cloud, and ON24 publishes no mainland-China data region. The exposure here is the data, not the stream.
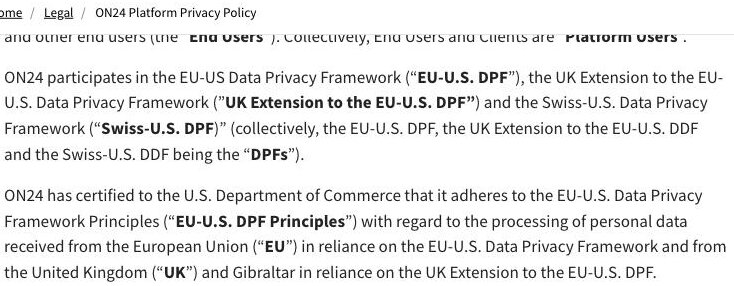
ON24's own Platform Privacy Policy says it "participates in the EU-US Data Privacy Framework" (plus the UK Extension and the Swiss-U.S. DPF) and has "certified to the U.S. Department of Commerce" its handling of personal data imported into the United States — and in the same policy ON24 is the "data processor" while "Clients are data controllers." So when a mainland attendee signs up, their registration and engagement data crosses the border to the US: a cross-border transfer of personal information PIPL governs (notice, separate consent and a transfer mechanism, Articles 38–43), and you — the controller — carry that duty, not ON24. The table below is ON24's own wording and the rule each line triggers.
This is a risk map, not a verdict — what PIPL asks turns on your entity, how much attendee data you hold and who your users are. Our China team can map your exposure with you →
Compliance snapshot
- ! ON24 is the data processor — you're the PIPL handler for attendee data
- ✕ Attendee data is stored on ON24's US cloud — no mainland-China region
- ! Mainland attendees' data crosses the border — PIPL applies (Arts 38–43)
- ! High-volume or sensitive attendee data can trigger data localization
- ! Live streaming from offshore is the delivery half, not the legal fix
What On24's own documentation says about China
| Fact | Primary source |
|---|---|
| ON24 holds your attendees' data as a processor — which makes you the handler under Chinese law. In its own Platform Privacy Policy ON24 says it is a "data processor" of the personal information collected via the platform, and that "Clients are data controllers with respect to Platform User personal information." That split matters for China: the controller — you, the company running the webinar — is the one PIPL treats as the personal-information handler responsible for any cross-border transfer, not ON24. | ON24 Platform Privacy Policy (on24.com), retrieved 2026-10-07 |
| Your attendees' data is stored in the United States — ON24 names no mainland-China region. ON24's privacy policy states it "participates in the EU-US Data Privacy Framework," the UK Extension and the Swiss-U.S. DPF, and has "certified to the U.S. Department of Commerce" its handling of personal data imported into the United States. The United States is the destination for the data it collects; no mainland-China data location is published. For your China audience, that makes every registration a cross-border transfer under PIPL (Articles 38–43). | ON24 Platform Privacy Policy (on24.com), retrieved 2026-10-07 |
| A webinar registration is personal information, and ON24 collects a lot of it. ON24's policy explains that it "collects, stores, uses, and shares personal information" through its Digital Engagement Platform, "which includes services related to our Virtual Events, Webinars, Virtual Conferences, Hybrid Capabilities, Content Hubs, and all other ON24 products" — names, business emails, employer, and the engagement and behavioral signals ON24 is built to score. Gathered from a mainland attendee, all of it is personal information that leaves the country the moment it reaches ON24's US cloud. | ON24 Platform Privacy Policy (on24.com), retrieved 2026-10-07 |
| Shipping that data offshore triggers real PIPL duties — and possibly data localization. Because ON24 stores the data in the US, serving mainland attendees is a cross-border transfer of personal information: as the handler you must give notice, obtain separate consent, and clear one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification (PIPL Articles 38–43). If you are a critical information infrastructure operator or a large-volume handler, personal information collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — which a US-hosted platform cannot do. Any public site you run for that audience separately needs an ICP filing an offshore host cannot carry. | PIPL Articles 38–43 & 40; Cybersecurity Law Article 39 (formerly Article 37); State Council Order No. 292; MIIT Order No. 33 (gov.cn) |
Sources verified by the 21YunBox compliance team on 2026-10-07.
For a mainland-China audience, the deciding question about ON24 is not whether the webinar plays — it is where your attendees’ data is allowed to live, and who answers for it once it leaves the country. ON24 is a hosted platform: the moment someone in China registers, their name, business email, employer and on-session behavior are collected into ON24’s US-based cloud. Reaching the broadcast is the easy half. The exposure is that the data crosses the border — and under China’s law it is you, not ON24, who has to account for it.
ON24 in China at a glance
| What decides it | In ON24's own terms |
|---|---|
| What it collects | ON24 “collects, stores, uses, and shares personal information” through its Digital Engagement Platform, “which includes services related to our Virtual Events, Webinars, Virtual Conferences, Hybrid Capabilities, Content Hubs, and all other ON24 products” — registration details plus the engagement and behavioral scoring it is built around. |
| Who is responsible | ON24 is the “data processor”; “Clients are data controllers with respect to Platform User personal information.” The handler duty under PIPL is yours, not ON24's. |
| Where the data lives | ON24 “participates in the EU-US Data Privacy Framework” and has “certified to the U.S. Department of Commerce” its handling of personal data imported into the United States. No mainland-China data region is named. |
| Your mainland attendees' data | Leaves the mainland to reach ON24's US cloud — a cross-border transfer of personal information PIPL governs (notice, separate consent, a transfer mechanism; Articles 38–43), with a localization duty for CIIOs and large-volume handlers. |
| Is it reachable? | Live webinar video is served from offshore and must cross the border in real time, so playback can be inconsistent. But reachability is the delivery half — never the half that decides whether you may collect and export the data. |
Where the data lives — and why that is the real question
ON24 is software you log into, not software you host, so the usual “where are the servers” question lands on ON24’s cloud, not yours. In its own Platform Privacy Policy ON24 says it “collects, stores, uses, and shares personal information” through its Digital Engagement Platform, “which includes services related to our Virtual Events, Webinars, Virtual Conferences, Hybrid Capabilities, Content Hubs, and all other ON24 products.” That is your attendees — their names, work emails, employers, and the attention and behavior ON24 exists to measure.
Where that personal information comes to rest is settled by ON24’s own cross-border posture. The policy states ON24 “participates in the EU-US Data Privacy Framework,” the UK Extension and the Swiss-U.S. DPF, and has “certified to the U.S. Department of Commerce” its handling of personal data imported into the United States. Those mechanisms exist to move data into the US; the United States is the destination, and ON24 names no mainland-China data location. So the geography is set before performance ever enters the picture: data collected from your China audience is stored offshore, and for that audience each registration is a cross-border transfer under the Personal Information Protection Law.
You are the handler, not ON24
The same policy draws the line that decides who carries the China exposure. ON24 is the “data processor of the personal information collected via the Platform,” and “Clients are data controllers with respect to Platform User personal information.” Under PIPL the controller — the company whose webinar it is — is the personal-information handler, and the handler is the party the law holds to the cross-border rules: giving notice, obtaining separate consent, and clearing one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification) before the data moves (PIPL Articles 38–43). ON24 processing the data on your instruction does not move that duty onto ON24.
Two further doors can open depending on who you are. If you are a critical information infrastructure operator or you handle personal information above the regulated volumes, data collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — a residency duty a US-hosted platform cannot meet. And if you stand up a public site of your own for that audience — a campaign page, a registration microsite — that site, served to mainland visitors, needs an ICP filing (State Council Order No. 292; MIIT Order No. 33) that an offshore host cannot carry. None of this is a problem ON24 is built to solve, because none of it is ON24’s to solve — it is the handler’s.
Reachability is the other half — and only the other half
ON24 is a live medium: interactive video, polls, and Q&A rendered in real time. Served from an offshore origin, that traffic has to cross the border every second the session runs, and real-time delivery is exactly the kind of workload the distance treats harshly — so a mainland viewer’s experience can be uneven even when the page opens. That is a genuine delivery concern, and it is worth taking seriously. But it is not the question that decides whether you may use ON24 for a China audience. Reaching the stream faster does not give you notice, separate consent, a transfer mechanism, or in-country residency; those are compliance facts, and no amount of network tuning produces them.
This is a risk map, not a verdict: whether PIPL’s cross-border rules, a localization duty, or an ICP filing for your own site apply to you turns on what you collect, how much of it, and who your attendees are — worth settling with counsel before your next mainland campaign.
Where 21YunBox fits — a compliant overlay, not a migration
You keep running ON24 for your webinars. We add the piece a US-hosted platform cannot hand you itself: compliant, ICP-filed delivery from inside the mainland, set in front of the China-facing origin your audience actually hits — the registration pages, landing pages and site around the broadcast — with no rebuild and no second codebase. Our China team traces exactly where your attendees’ personal data crosses the border, maps what PIPL asks of you as the handler against your entity and data volumes, and stands up the in-country delivery and data handling a lawful China presence needs, while ON24 stays exactly where it already sits in your stack.
Related reading:
Frequently Asked Questions
Where does ON24 store our attendees' data?
On its US-based cloud. ON24's Platform Privacy Policy says it participates in the EU-US Data Privacy Framework, the UK Extension and the Swiss-U.S. DPF, and has certified to the U.S. Department of Commerce its handling of personal data imported into the United States. It publishes no mainland-China data region. For your China audience that means every attendee's registration and engagement data leaves the country to reach ON24.
Is it illegal to run ON24 webinars for a mainland-China audience?
Treat it as a risk to assess with counsel, not a blanket yes or no. ON24 is the data processor and you are the data controller, so the duties fall on you: when mainland attendees register, their personal information is transferred offshore to the US, which PIPL governs as a cross-border transfer (notice, separate consent and a transfer mechanism, Articles 38–43). Whether a data-localization duty also applies turns on your role — for example a CIIO — and your data volumes. ON24 "works"; the legal exposure sits with you.
Can 21YunBox help us run ON24 compliantly in China?
Yes. Our China team can map where your attendee data crosses the border and what PIPL asks of you as the handler — for your entity, data volumes and audience — and stand up ICP-filed, in-country delivery in front of the China-facing origin your audience actually hits, such as your registration and landing pages, without moving you off ON24. Get in touch to work through your specific case.