Does Varonis Work in China? Data Residency, Localization & PIPL Cross-Border
Varonis SaaS stores only metadata — but that metadata is a classified map of where your sensitive files and personal information live, plus user identities and access events. Its regions span the US, Europe, the UK, Canada, Australia and India — none in mainland China — so that map rests offshore, a PIPL cross-border transfer. A compliance-first look at where your security metadata may rest.
Does Varonis work in China?
Varonis runs in China — the compliance question is residency: its SaaS stores only metadata, and that metadata is a classified map of where your sensitive data and personal information live, held offshore with no mainland-China region.
Varonis keeps file content on an in-environment collector and uploads metadata, classifications and access events — user identities, file paths, email senders and recipients, access records — to its SaaS Data Security Platform, which operates only in the US, Europe, the UK, Canada, Australia and India. Holding that China-sourced map and its identifiers offshore is a PIPL cross-border transfer, and because the classifications flag exactly where Article 28 sensitive data sits, the stakes rise rather than fall; a critical information infrastructure operator or high-volume handler also owes an in-country storage duty an offshore SaaS cannot meet. The obvious in-country option — the legacy self-hosted platform — reaches end-of-life on December 31, 2026.
This is a risk map, not a ruling — settle specifics with counsel. Our China team can map your exposure →
What Varonis's own documentation says about China
| Fact | Primary source |
|---|---|
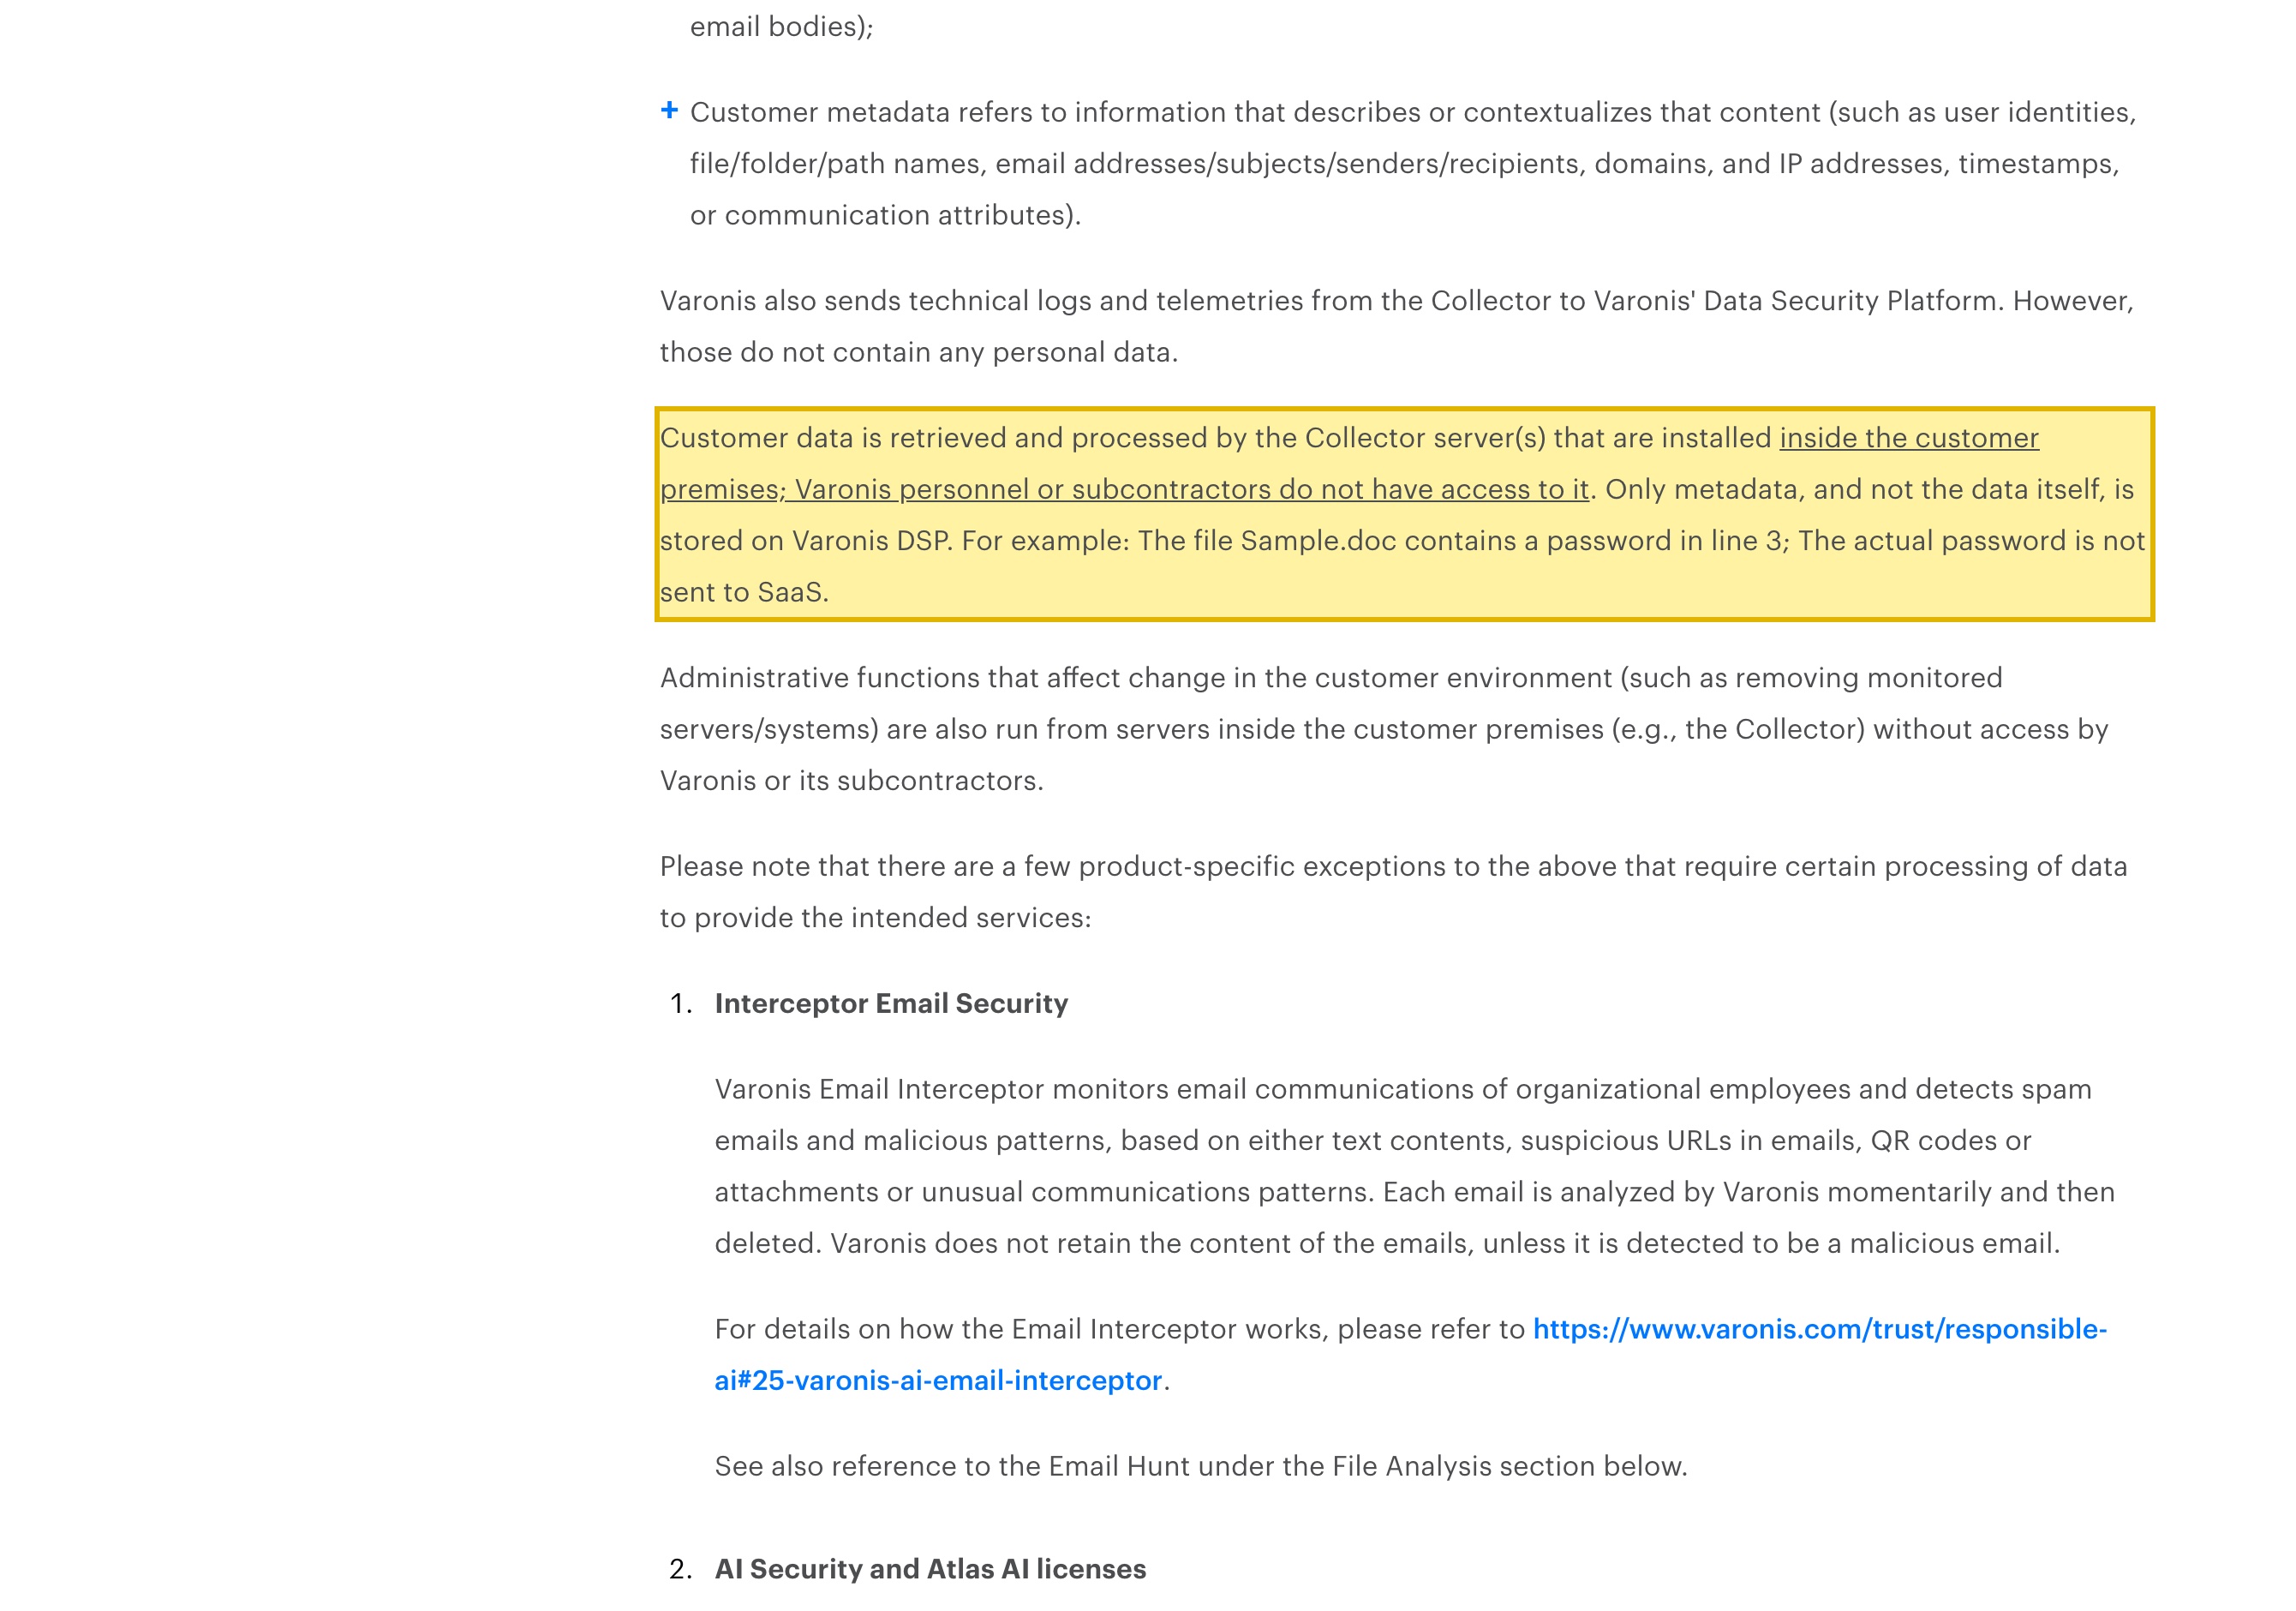
| Varonis stores only metadata on its SaaS — but that metadata is a classified map of where your sensitive data lives, held in a geography with no mainland-China region. Its privacy page states the platform "can be set to operate from the geography of the customer’s choice" and that "Only metadata, and not the data itself, is stored on Varonis DSP." That metadata includes user identities, file paths, email senders and recipients, access events and classification results; the operating geographies are the US, Europe, the UK, Canada, Australia and India. | Varonis — Privacy Standards and Practices (retrieved 2026-10-10) |
| Varonis’s legacy self-hosted platform reaches end-of-life on December 31, 2026 — the vendor is going all-in on SaaS. Varonis states it announced "the end-of-life (EOL) of our legacy self-hosted product by December 31, 2026," with SaaS now "76% of our business," so the run-it-on-your-own-mainland-servers option is closing and the in-country lever shifts to a licensed in-country or sovereign-cloud equivalent. | Varonis blog — Why We’re Going All In on SaaS, rev. 2025-11-12 (retrieved 2026-10-10) |
| Holding China-sourced metadata and identifiers on an offshore SaaS is a cross-border transfer of personal information under PIPL. PIPL Articles 38–40 put the duty on the handler — you, the operator, not Varonis the processor — to give notice, obtain a separate consent, and put one transfer mechanism in place (a CAC security assessment, the CAC standard contract, or certification). | Personal Information Protection Law, Articles 38–40 (retrieved 2026-10-10) |
| A critical information infrastructure operator must store personal information generated in China inside China — an offshore SaaS cannot meet this. Cybersecurity Law Article 39 (formerly Article 37) — the 2025 amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged — and PIPL Article 40 set the in-country storage duty; above volume or sensitivity thresholds a CAC data-export security assessment may apply before anything leaves. | Cybersecurity Law Art. 39 (formerly Art. 37); PIPL Art. 40 (retrieved 2026-10-10) |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a security team serving mainland China, the question about Varonis was never whether its collectors install or whether they can reach the cloud. They do. Varonis is a data-security platform: it discovers, classifies and continuously watches where your sensitive files and personal information live across file shares, Microsoft 365, SaaS apps and cloud stores. By design it keeps file content on a collector inside your environment and sends only metadata to its SaaS — and that metadata is the crux, because it is a classified map of exactly where your most sensitive data sits, together with user identities, email senders and recipients, access events and the labels that mark what is sensitive. The irony is sharp: the tool you bought to map and protect your sensitive data holds that map offshore. Varonis runs that SaaS in the US, Europe, the UK, Canada, Australia and India — none in mainland China — and its legacy self-hosted platform reaches end-of-life on December 31, 2026. So the real question is a residency one: where is the map of your China data allowed to rest?
Varonis in China at a glance
| What decides it | In Varonis's own terms — and China's law |
|---|---|
| Where the security data physically rests | Varonis keeps file content on a collector inside your environment and stores only metadata on its SaaS Data Security Platform (DSP). Its privacy page says the platform "can be set to operate from the geography of the customer's choice" — but the geographies it operates are the US, Europe, the UK, Canada, Australia and India. There is no mainland-China region to select, so the metadata comes to rest offshore. The legacy self-hosted platform that could run on your own mainland servers reaches end-of-life on December 31, 2026. |
| What it ingests, and why it is personal information | Varonis's own definition: metadata is "information that describes or contextualizes that content (such as user identities, file/folder/path names, email addresses/subjects/senders/recipients, domains, and IP addresses, timestamps, or communication attributes)." Add access events — who opened, moved or deleted which file — and classification results. Those are personal information under PIPL once they identify a person, and the classifications flag exactly where Article 28 sensitive data — financial, health, government-ID, biometric — sits. The store is a map of your most sensitive data. |
| Your mainland metadata in the store | Metadata, classifications and access events drawn from people and systems in China and held on an offshore DSP are a cross-border transfer PIPL governs: notice, a separate consent, and one transfer mechanism (PIPL Articles 38–40). The handler on the hook is you, the operator — not Varonis, the processor. |
| In-country storage duty | A critical information infrastructure operator or high-volume handler owes an in-country storage duty an offshore SaaS cannot meet — mainland personal information and important data must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged. |
| Is it reachable? | Treat reachability as the delivery half, not the question — collectors and consoles connect. With the legacy self-hosted option closing, the lawful lever is a licensed in-country or sovereign-cloud equivalent that keeps the metadata layer on mainland soil, and any China-facing surface in front of it — the admin console, the reporting portal — needs an ICP filing tied to a mainland hosting resource (State Council Order No. 292; MIIT Order No. 33). |
Where the data actually rests
Varonis does not place a region inside mainland China. The company built its SaaS cloud-native and scales it on global public-cloud infrastructure — Microsoft Azure, in its own architecture writing — with customer-facing data centers in the United States, Europe, the United Kingdom (London), Canada (Toronto), Australia (Sydney) and India (Mumbai and Pune). Its privacy page says the platform “can be set to operate from the geography of the customer’s choice,” but that choice is drawn from exactly those geographies; there is no mainland-China option to select. Point your tenant at any of them and the metadata Varonis gathers from your China systems comes to rest outside China.
The one deployment that could have kept everything on mainland soil — the legacy self-hosted Data Security Platform you ran on your own servers — is closing. Varonis has announced the end-of-life of that self-hosted product by December 31, 2026, saying SaaS “now makes up 76% of our business” and that it is going all in. What stays local in the SaaS model is file content: a collector inside your environment scans the files and uploads only metadata and classification results. That is a real and welcome design — but it is the metadata, not the file bodies, that carries the residency problem, because of what the metadata is.
What it ingests is personal information
Varonis earns this scrutiny because of what its metadata contains. In Varonis’s own words, metadata is “information that describes or contextualizes that content (such as user identities, file/folder/path names, email addresses/subjects/senders/recipients, domains, and IP addresses, timestamps, or communication attributes).” Add the access events it records — who opened, moved or deleted which file — and the classification results that label where regulated data lives. Each of those is personal information under China’s Personal Information Protection Law the moment it identifies a person, and the classifications point straight at Article 28 sensitive personal information — financial, health, government-ID and biometric fields — which carries a higher bar of specific purpose, strict necessity and separate consent.
So the thing Varonis concentrates offshore is not an incidental log; it is a precise, searchable index of where your most sensitive China data sits, who can reach it and who has touched it. “Only metadata, and not the data itself” is cold comfort when the metadata is the map. For a critical information infrastructure operator, and for a handler whose volumes cross the regulators’ thresholds, personal information and important data collected in the mainland must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). An offshore SaaS structurally cannot satisfy that duty — the index is, by definition, in the wrong country — and where an export is permitted at all, crossing a volume or sensitivity threshold can trigger a CAC-led data-export security assessment before any of it lawfully leaves.
Running it on a no-China-region SaaS doesn’t meet the residency duty — and what does
The honest summary is narrow and important: nothing about Varonis is “blocked” in China, and the exposure is not the software. The exposure is a SaaS deployment that parks the index of your mainland’s most sensitive data — and the identities and access events around it — outside the mainland, with no in-country region to select and the self-hosted alternative being retired.
Because the legacy self-hosted platform reaches end-of-life on December 31, 2026, the lawful lever is not a promise that you can run Varonis on your own Shanghai servers forever. It is to keep the sensitive-data metadata layer in-country by other means — a licensed in-country or sovereign-cloud equivalent that holds the classifications, identities and access events on mainland soil, with consented in-country storage for what must stay. Pointing a mainland collector back at the offshore Varonis SaaS is not localization and does not meet the storage duty; standing up a lawful in-country equivalent is. Where a minimized subset of metadata may lawfully cross the border, you keep that transfer consented and backed by a transfer mechanism, while any China-facing surface in front of the platform — the admin console, the reporting portal your mainland operators hit — earns its own ICP filing.
This is a risk map, not a verdict. Whether you owe in-country storage, a transfer mechanism, a separate consent, a data-export security assessment, an ICP filing, or some combination turns on your entity, your data volumes, how much of what your metadata describes is personal or sensitive, and whose data it is — and it is worth settling with counsel before you decide where a single classification record lives.
The lawful path — map, localize, deliver
You do not have to drop Varonis to run it lawfully for mainland China. 21YunBox is a compliant overlay, not a migration — and, for a platform you already run, a partner that sits alongside your stack, not a competitor to it. There are three moves, and they fit together.
Map. Our China compliance team reads your PIPL cross-border, data-residency and data-localization (CII) obligations against your actual entity, your data volumes, and whose personal information your Varonis metadata describes — the identities, the email senders and recipients, the access events, the classifications that mark where sensitive data sits — so the exposure is written down before anything moves.
Localize. Because the risk is where that metadata rests, we keep the sensitive-data layer in-country — on a licensed in-country or sovereign-cloud equivalent — so the classifications, identities and access events China requires to stay on mainland soil do. Localize means a lawful in-country deployment of the data layer, never a tunnel back to the offshore endpoint; only the minimized, lawfully transferable subset ever crosses.
Deliver. For any China-facing surface in front of the platform — the admin console, the reporting portal, the self-service page your mainland users and operators hit — the 21YunBox Optimizer provides ICP-filed, in-country delivery, in front of the stack you already run. No rebuild, no second codebase. 21YunBox never uses or suggests circumvention of any kind; the entire point is a lawful, filed, in-country path.
The goal is plain: your Varonis deployment runs legally and compliantly for your users in China.
Related reading:
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law and data localization (Article 39)
- China’s data-export security assessment measures
- How to get an ICP filing for China