Does Dropbox Sign (HelloSign) Work in China? PIPL, Cross-Border Data & ICP
Dropbox Sign — the service formerly called HelloSign — runs on offshore AWS with no mainland-China region, so your Chinese signers' names, IP addresses and signed documents leave the country as a PIPL cross-border transfer, and where its signing widget is embedded the ICP filing sits on your site. A compliance-first look at the doors.
Does Dropbox Sign (HelloSign) work in China?
It loads — but for your Chinese signers this is a cross-border data problem, not a signing one. Dropbox Sign (the service HelloSign became) runs on offshore AWS with no mainland-China region, so every name, email, IP address and signed agreement you collect in China leaves the country by design.
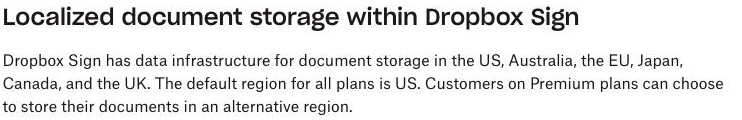
Dropbox's own data-residency page lists where signed documents can live — "the US, Australia, the EU, Japan, Canada, and the UK" — states "The default region for all plans is US," and notes that while a document is edited or signed "a temporary copy of the document is moved to our US servers." None of those regions is in the mainland. Its privacy policy adds that you "consent to have your information transferred to us and our facilities in the United States or elsewhere," and that "you are the data controller." So for Chinese signers that personal information is a cross-border transfer PIPL governs, and where you embed the signing widget on a public mainland site, the ICP filing sits on that site, not on Dropbox. The table below pairs Dropbox Sign's own wording with the rule each line triggers.
This is a risk map, not a verdict — what you owe turns on your entity, your signer volumes and the data you hold. Our China team can map your signer-data exposure and the filing path with you →
What Dropbox Sign (Formerly Hellosign)'s own documentation says about China
| Fact | Primary source |
|---|---|
| Dropbox Sign has no region inside mainland China. On its own data-residency page Dropbox describes where signed documents can live — "Dropbox Sign has data infrastructure for document storage in the US, Australia, the EU, Japan, Canada, and the UK" — and states "The default region for all plans is US." None of the six is in the mainland, so there is no setting that keeps a Chinese signer's documents in-country on Dropbox Sign. | Dropbox — Dropbox Sign data residency (help.dropbox.com), retrieved 2026-10-07 |
| Even a non-US region still processes in the United States. Dropbox's residency page says at-rest files are "stored in our AWS data infrastructures in the selected region," but when a document is edited, sent or signed, "a temporary copy of the document is moved to our US servers where processing is performed." Choosing the EU or Japan region does not keep a Chinese signer's live document off US infrastructure — it is a cross-border transfer under PIPL (notice, separate consent and a transfer mechanism, Articles 38–43) either way. | Dropbox — Dropbox Sign data residency (help.dropbox.com), retrieved 2026-10-07; PIPL Articles 38–43 |
| It holds highly sensitive personal data — and the PIPL duty is yours, not Dropbox's. The privacy policy records your "email address and a password, your phone number, your address and an electronic image of your signature," "IP addresses," and the documents you upload "for review or signature," and says you "consent to have your information transferred to us and our facilities in the United States or elsewhere." It also states "you are the data controller," with "Dropbox International Unlimited Company act[ing] as a processor" for most non-US customers — so for Chinese signers this is a cross-border transfer of personal information PIPL governs, and the obligation falls on you. | Dropbox Sign Privacy Policy (sign.dropbox.com/about/privacy), effective 2025-01-14, retrieved 2026-10-07; PIPL Articles 38–43 |
| The ICP filing lands on your site, and a localization duty may apply to the data. Where you embed Dropbox Sign's signing widget in — or send its links from — a public, mainland-facing website, that site needs an ICP filing (State Council Order No. 292; MIIT Order No. 33); the offshore service itself cannot be filed. And if you are a critical information infrastructure operator or a large-volume handler, personal information collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — which an offshore-only service cannot meet. | State Council Order No. 292; MIIT Order No. 33; PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37); anchored on Dropbox Sign Privacy Policy (offshore storage, customer is controller), retrieved 2026-10-07 |
Sources verified by the 21YunBox compliance team on 2026-10-07.
For a mainland-China audience, the deciding question about Dropbox Sign — the e-signature service that was called HelloSign until Dropbox renamed it — is not how quickly the signing page paints. It is whether the personal data it collects is allowed to leave the country, and whether the site that carries the signing flow is cleared to operate in China at all. Dropbox answers the first half in its own documentation: Dropbox Sign stores and processes signed documents on offshore AWS, with no region inside the mainland. So a China-facing signing flow is reachable, but every name, email, IP address and signed agreement it captures lands outside China — and that, not latency, is the exposure.
Dropbox Sign in China at a glance
| What decides it | In Dropbox Sign's own terms |
|---|---|
| Where it runs | “Data infrastructure for document storage in the US, Australia, the EU, Japan, Canada, and the UK,” with “The default region for all plans is US” — all on offshore AWS, none inside mainland China. |
| What it holds | Your “email address and a password, your phone number, your address and an electronic image of your signature,” “IP addresses,” and the documents you upload “for review or signature” — highly sensitive personal data. |
| Crossing the border | Serving Chinese signers, you “consent to have your information transferred to us and our facilities in the United States or elsewhere” — a cross-border transfer of personal information PIPL governs. |
| Who carries the duty | Dropbox's policy: “you are the data controller,” with “Dropbox International Unlimited Company act[ing] as a processor” for most non-US customers — so the PIPL obligations are yours, not Dropbox's. |
| Serving the public | A public, mainland-facing site that embeds the signing widget or sends its links needs an ICP filing on that site; Dropbox Sign has no mainland region to file against. |
No mainland region, so your signers’ data lives offshore
Dropbox Sign stores signed documents in one of six places, and in Dropbox’s own words that list is “the US, Australia, the EU, Japan, Canada, and the UK.” The same page states “The default region for all plans is US,” and that at-rest files are “stored in our AWS data infrastructures in the selected region.” Not one of those regions is in mainland China, and choosing a nearer one does not change the arithmetic for a Chinese signer: the data has still left the country. Residency controls where the finished file comes to rest — it does not keep the data inside China.
Picking a non-US region does not even keep the live document off US infrastructure. Dropbox’s residency page is explicit that while a document is edited, sent or signed, “a temporary copy of the document is moved to our US servers where processing is performed.” So the EU or Japan setting moves where the completed file rests, not where your Chinese signer’s document is handled in the moment it matters most. The geography is offshore either way.
Highly sensitive personal data, crossing the border by design
An e-signature service collects some of the most sensitive data a form ever touches, and Dropbox Sign’s privacy policy says so plainly: your “email address and a password, your phone number, your address and an electronic image of your signature,” network identifiers including “IP addresses,” and the documents you upload “for review or signature” — the agreements themselves. For a Chinese signer, sending all of that to offshore AWS is a cross-border transfer of personal information under China’s Personal Information Protection Law: the handler must give notice, obtain separate consent, and clear one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification (Articles 38–43). If you are a critical information infrastructure operator or a large-volume handler, personal information collected in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — a residency duty an offshore-only service cannot satisfy.
And the duty is yours to carry, not Dropbox’s. Its policy states “you are the data controller,” with “Dropbox International Unlimited Company act[ing] as a processor” for most customers outside the US. In PIPL terms you are the personal-information handler: the consent, the notice and the transfer mechanism are obligations the law puts on you, the operator who collected the signers, rather than on the platform that stores the files.
The ICP door sits on your site, not on Dropbox Sign
Dropbox Sign is usually reached through a widget embedded in your own pages or a signing link sent from your own site. That placement is what pulls in the second door. A public-facing website delivered to mainland visitors from inside China turns on an ICP filing (ICP 备案) under State Council Order No. 292 and MIIT Order No. 33, and that filing attaches to the operator’s site — the one that carries the embed or sends the link — not to the SaaS behind it. Dropbox Sign has no mainland region, so there is nothing on Dropbox to file against; the obligation lands on your site instead. “We just drop in the signing widget” does not move that duty somewhere else.
This is a risk map, not a verdict: whether you owe notice and separate consent, a transfer mechanism, in-country storage, an ICP filing, or several of these at once depends on what you sign, how much personal data you hold and who your signers are — worth settling with counsel before you roll it out.
Where 21YunBox fits — a compliant overlay, not a migration
You keep using Dropbox Sign. We add the piece an offshore e-signature service cannot: compliant, ICP-filed delivery from inside the mainland, set in front of the public site that carries your signing flow — no rebuild, no second codebase, and no move off Dropbox Sign. Because the signer data still lands on Dropbox’s offshore AWS, our China team maps your PIPL cross-border and data-residency exposure against your entity, your signer volumes, and the consent and transfer mechanism each flow actually needs — so the paperwork matches what crosses the border, and the site that collects your signers is cleared to operate where they are.
Related reading: