Does hCaptcha Work in China? Visitor Data, PIPL Cross-Border Transfer & Data Residency
hCaptcha's anti-bot widget is reachable from mainland China, so loading is not the real question. To tell humans from bots it collects each visitor's IP address, device and browser data, and behavioral signals — mouse movements, keypresses, touch events — all personal information under PIPL; and by Intuition Machines' own privacy policy hCaptcha is operated from the United States, with visitor data "transferred to, processed, and stored in the United States" (its GDPR FAQ adds EU data centers and "regional servers around the world"), naming no mainland-China region. For visitors in China that makes the collection a cross-border transfer (数据出境) under PIPL Articles 38–40 — notice, a separate consent, one transfer mechanism — with the collection itself needing a PIPL lawful basis and clear notice. A compliance-first look at what hCaptcha collects, where it goes, and the lawful in-country path.
Does hCaptcha work in China?
hCaptcha's widget is reachable from mainland China, so loading is not the real question. What decides it is that a CAPTCHA, by design, inspects every visitor — and hCaptcha collects their IP address, device and browser data, and behavioral signals, all personal information under PIPL, then processes it offshore.
By Intuition Machines' own Privacy Policy, hCaptcha "is based in the United States," is "controlled and operated by us from the United States," and visitor data "will be transferred to, processed, and stored in the United States"; its GDPR FAQ adds data centers in Europe and the US and "regional servers around the world," and names no mainland-China region. For visitors in China that makes the collection a cross-border transfer (数据出境) under PIPL Articles 38–40 — notice, a separate consent, and one transfer mechanism — and it may trigger China's data-export security assessment. The collection itself needs a PIPL lawful basis and clear notice, and for a critical information infrastructure operator the Cybersecurity Law's Article 39 (formerly Article 37) adds an in-country storage duty no offshore region meets.
21YunBox maps your cross-border and consent exposure, localizes China human-verification onto a China-resident, consented footing, and delivers your China-facing site in-country on ICP-filed infrastructure — with no rebuild, and never any form of circumvention. Treat the specifics as a risk to confirm with counsel. Our China team can map your exposure with you →
What hCaptcha's own documentation says about China
| Fact | Primary source |
|---|---|
| hCaptcha inspects every visitor and collects their IP address, device and browser data, and behavioral signals. By its own Privacy Policy, hCaptcha gathers from end users "mouse movements, scroll position, keypress events, touch events, and similar information as applicable" to tell humans from bots, alongside "IP addresses, browser type, Internet service provider, platform type, device type, operating system"; its Data Privacy Framework disclosure says it may process "Communications metadata (e.g. information on originating IP address or other identifier, date and time of interaction)" in the United States. An IP address and device identifiers are personal information under PIPL. | hCaptcha — Privacy Policy (hcaptcha.com), retrieved 2026-10-09 |
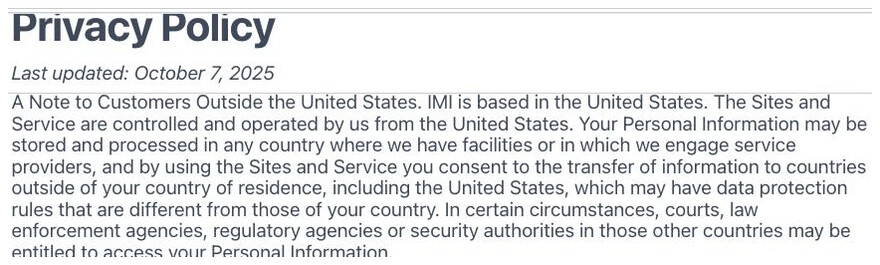
| hCaptcha is operated from the United States, and its Privacy Policy says visitor data is processed and stored there. Under "A Note to Customers Outside the United States," it states: "IMI is based in the United States. The Sites and Service are controlled and operated by us from the United States," and under "Cross-Border Data Transfer" that "your personal data will be transferred to, processed, and stored in the United States." hCaptcha is a service of Intuition Machines, Inc. (IMI). | hCaptcha — Privacy Policy (hcaptcha.com), retrieved 2026-10-09 |
| hCaptcha names no mainland-China data region. Its GDPR FAQ says it is "operated by Intuition Machines, a company headquartered in the United States," that it "processes the vast majority of data within one of our many regional servers around the world," that it processes metadata "in our main data centers in Europe and, if applicable, the US," and that "by default, analytics data is already stored in the EU." Mainland China appears nowhere in its privacy or GDPR documentation, so visitor signals collected in China come to rest outside the mainland. | hCaptcha — GDPR FAQ (hcaptcha.com), retrieved 2026-10-09 |
| Sending China visitors' signals to hCaptcha's offshore infrastructure is a PIPL cross-border transfer. Moving personal information collected from people in mainland China to infrastructure in the US or EU triggers PIPL Articles 38–40: notice, a separate consent distinct from any general agreement, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. The collection of the IP, device, and behavioral signals itself also needs a PIPL lawful basis and clear notice. | Personal Information Protection Law of the PRC, Articles 38–40 (cac.gov.cn), retrieved 2026-10-09 |
Sources verified by the 21YunBox compliance team on 2026-10-09.
For a site serving mainland China, hCaptcha carries the same awkward twist a privacy tool does: it is a security control that, used as-is, can create a data-compliance exposure of its own. The first instinct is to ask whether the widget even loads from China — and on the wire it generally does. hCaptcha serves from its own endpoints rather than Google-owned domains, so it is not blocked at the border the way some foreign CAPTCHAs are. Reachability, then, is not where the China decision is settled. What settles it is simpler and sits upstream of speed: a CAPTCHA works by inspecting every visitor, and hCaptcha collects each one’s IP address, device and browser details, and behavioral signals to tell a human from a bot — all of it personal information under China’s law — and then processes that data outside the mainland.
hCaptcha in China at a glance
| What decides it | In hCaptcha's own terms — and China's law |
|---|---|
| What it is | hCaptcha is a human-verification / anti-bot widget from Intuition Machines, Inc. (IMI). To decide whether a visitor is human it collects, in its own words, “IP addresses, browser type, Internet service provider, platform type, device type, operating system,” and from end users “mouse movements, scroll position, keypress events, touch events, and similar information as applicable.” That is a continuous record of identifiable visitors. |
| Is it reachable from the mainland? | Generally, yes. hCaptcha loads from its own hosts (js.hcaptcha.com) and does not depend on Google-owned domains, so it is not blocked at the border the way some foreign CAPTCHAs are. Reachability is the delivery half of the question, not the half that decides whether you may lawfully use it. |
| Where do the visitor signals go? | Offshore. Its Privacy Policy says hCaptcha is “controlled and operated by us from the United States” and that personal data “will be transferred to, processed, and stored in the United States”; its GDPR FAQ adds “main data centers in Europe and, if applicable, the US” and “many regional servers around the world.” It names no mainland-China region. |
| Collecting China visitors' signals into it | The IP address, device identifiers, and behavioral signals are personal information. Holding them on infrastructure in the US or EU is a cross-border transfer (数据出境) under PIPL (Articles 38–40): notice, a separate consent, and one transfer mechanism. The collection itself needs a PIPL lawful basis and clear notice before the challenge fires, a data-export security assessment may apply above thresholds, and for a critical information infrastructure operator the Cybersecurity Law's Article 39 (formerly Article 37) sets an in-country storage duty an offshore region cannot meet. |
| Who owes the duty | You, the operator of the China-facing site — the personal-information handler. hCaptcha's own policy says the processing of end-user data “is governed by the agreement we have with our Integrator customers,” i.e. IMI acts as the entrusted processor. Embedding the widget does not move the PIPL obligation onto the vendor. |
| The lawful path | Run a China-resident human-verification option that keeps the challenge and signal data in-country on a consented footing, send offshore only what may lawfully leave, and deliver the China-facing site in-country on ICP-filed infrastructure. 21YunBox maps, localizes, and delivers; it never uses or suggests circumvention of any kind. |
A CAPTCHA inspects every visitor — so it gathers personal information by design
The structural point is easy to miss precisely because hCaptcha is a security tool. Its entire method is to watch what a visitor does and decide whether they are human — and to do that it reads signals from the person. In hCaptcha’s own Privacy Policy those signals are spelled out: automatic collection of “IP addresses, browser type, Internet service provider, platform type, device type, operating system,” and, from end users specifically, “mouse movements, scroll position, keypress events, touch events, and similar information as applicable.” Its Data Privacy Framework disclosure goes further and names what it may process in the United States: “Communications metadata (e.g. information on originating IP address or other identifier, date and time of interaction).”
Under China’s Personal Information Protection Law, an IP address and a device identifier are personal information, and the interaction signals describe the behavior of an identifiable person. So the widget you added to stop bots is, for every China visitor, a collection point for personal information — gathered silently, before the visitor has done anything but arrive at the form. That makes two duties attach at once: a lawful basis and clear notice for collecting it, and — because the data then leaves the mainland — the cross-border rules below.
Reachable — but where the signals land is the question
Because hCaptcha generally loads from China, it is tempting to treat the box as ticked. It is not. The decision is where the visitor’s signals come to rest and whether they had a lawful basis to leave the country, and hCaptcha answers the “where” in its own documents. Its Privacy Policy states that IMI “is based in the United States,” that “the Sites and Service are controlled and operated by us from the United States,” and that personal data “will be transferred to, processed, and stored in the United States.” Its GDPR FAQ describes a wider but still-offshore footprint — processing “within one of our many regional servers around the world,” metadata “in our main data centers in Europe and, if applicable, the US,” with analytics “by default… already stored in the EU.” Nowhere does it name a mainland-China region.
For that reason this page publishes no first-party China latency or reachability figure for hCaptcha: speed is not the axis for a decision that turns on residency and consent. hCaptcha does offer Enterprise controls — it advertises “First-Party Hosting” and “Zero PII” features and says Enterprise customers can obtain “hard technical guarantees on what data is stored, where data will be processed.” Those are worth exploring, but they name no mainland-China region and, by themselves, do not discharge the PIPL consent, notice, and transfer duties that sit with you as the handler. Whether any of them give you a China-resident footing is a configuration to confirm with hCaptcha and with counsel — not a default you inherit by embedding the widget.
The cross-border transfer — and the consent it needs
Here is the gate most teams miss. An hCaptcha deployment that processes data in the US or EU is, by definition, outside the mainland. The IP, device, and behavioral signals it holds for your visitors in China are personal information, and loading them onto offshore infrastructure is a cross-border transfer of personal information under PIPL. The law puts the duty on the handler — you, the site operator, not hCaptcha the processor: Articles 38–40 require notice, a separate consent distinct from any general agreement to use your site, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification.
Two more rules can bite on top. Above certain thresholds, or where the data is “important data,” the transfer may require China’s data-export security assessment (数据出境安全评估) before anything leaves. And if your organization is a critical information infrastructure operator, the Cybersecurity Law’s Article 39 (formerly Article 37 — the data-localization provision was renumbered by the 2025 amendment that took effect on January 1, 2026, with its substance unchanged) requires personal information generated in China to be stored in China, which an offshore hCaptcha deployment cannot satisfy. None of this turns on how quickly the challenge renders; it turns on whether the data had a lawful basis to be collected and to travel. A particular nuance for a CAPTCHA: you may be able to rest the collection on a basis other than consent — security of the service — but that is exactly the kind of judgment to settle with counsel, and it does not remove the separate consent and transfer mechanism the cross-border move still needs. Which of these obligations apply to your specific deployment is a risk to confirm with counsel against what you actually collect and where it goes.
The lawful path — map, localize, deliver
There is a lawful way to run bot defense for a China-facing site, and it has a shape. First, map: our China team works through your PIPL exposure on both fronts — the collection and the transfer — identifying what the challenge gathers from China visitors, which of it must stay in the country, what may lawfully leave, where a data-export security assessment or an Article 39 storage duty bites, and what your consent and notice flow has to cover. The legal conclusions are settled with counsel; we build the technical picture that feeds them.
Then localize: we stand up and integrate a human-verification option that keeps the China challenge and signal data on a China-resident, consented footing — China has well-established domestic human-verification services, for example GeeTest (极验) and the CAPTCHA/人机验证 offerings built into the major Chinese cloud platforms — so the protection you depend on keeps working while the visitor signals stop leaving the country by default. Where hCaptcha still serves your other markets, it keeps serving them.
Then deliver: the China-facing site that renders the challenge is itself a public service in the mainland, so it carries an ICP filing (备案) duty and needs compliant, in-country delivery. 21YunBox delivers it in-country — the 21YunBox Optimizer — set in front of the stack you already run, with no rebuild and no re-platform. The result is bot defense that runs legally and compliantly for the people who actually use your site in China. What we never do — and what no one lawfully can — is hand you a way around China’s data-export rules or around any network restriction: we localize what must stay, deliver in-country, and never move personal information out of China by stealth.
Related reading:
- Cross-border data transfers under PIPL
- China’s data-export security assessment
- China’s Cybersecurity Law (data localization, Article 39)
- How to get an ICP filing for China