Does CrowdStrike Work in China? Falcon Telemetry, PIPL & Data Residency
CrowdStrike's Falcon sensor streams endpoint telemetry to CrowdStrike's cloud — and that cloud has no mainland-China region. Its commercial regions are in the US and EU (plus a US GovCloud), and its new in-country data-residency clouds are in Saudi Arabia, India, and the UAE. So the process, user, network, and file telemetry your sensors collect from endpoints in China crosses the border, making its collection a cross-border transfer under PIPL, with a data-export security assessment and a Cybersecurity Law storage duty in play for larger handlers and CIIOs. A compliance-first look at Falcon's regions, the cross-border and residency questions, and the lawful in-country path.
Does CrowdStrike work in China?
Yes — the Falcon sensor can reach CrowdStrike's cloud from mainland China, so the honest answer is that reachability is not the problem. What decides the China question is data residency and cross-border transfer.
CrowdStrike runs no Falcon cloud in mainland China; its commercial regions are in the US and the EU (plus a US GovCloud), and the in-country data-residency clouds it is now standing up are in Saudi Arabia, India, and the UAE — none in the mainland. So the process, user, network, and file telemetry your Falcon sensors continuously ship from endpoints in China comes to rest offshore, which makes its collection a cross-border transfer (数据出境) of personal information under PIPL — requiring notice, a separate consent, and a transfer mechanism — and, above thresholds or for a critical information infrastructure operator, it may trigger China's data-export security assessment. For a CIIO, the Cybersecurity Law's Article 39 (formerly Article 37) requires such data to be stored in China, which no offshore Falcon region can satisfy.
21YunBox maps your cross-border and residency exposure, keeps the China endpoint telemetry on an in-country, consented footing, and delivers your China-facing services in-country on ICP-filed infrastructure — with no rebuild, and never any form of circumvention. Treat the specifics as a risk to confirm with counsel.
What CrowdStrike's own documentation says about China
| Fact | Primary source |
|---|---|
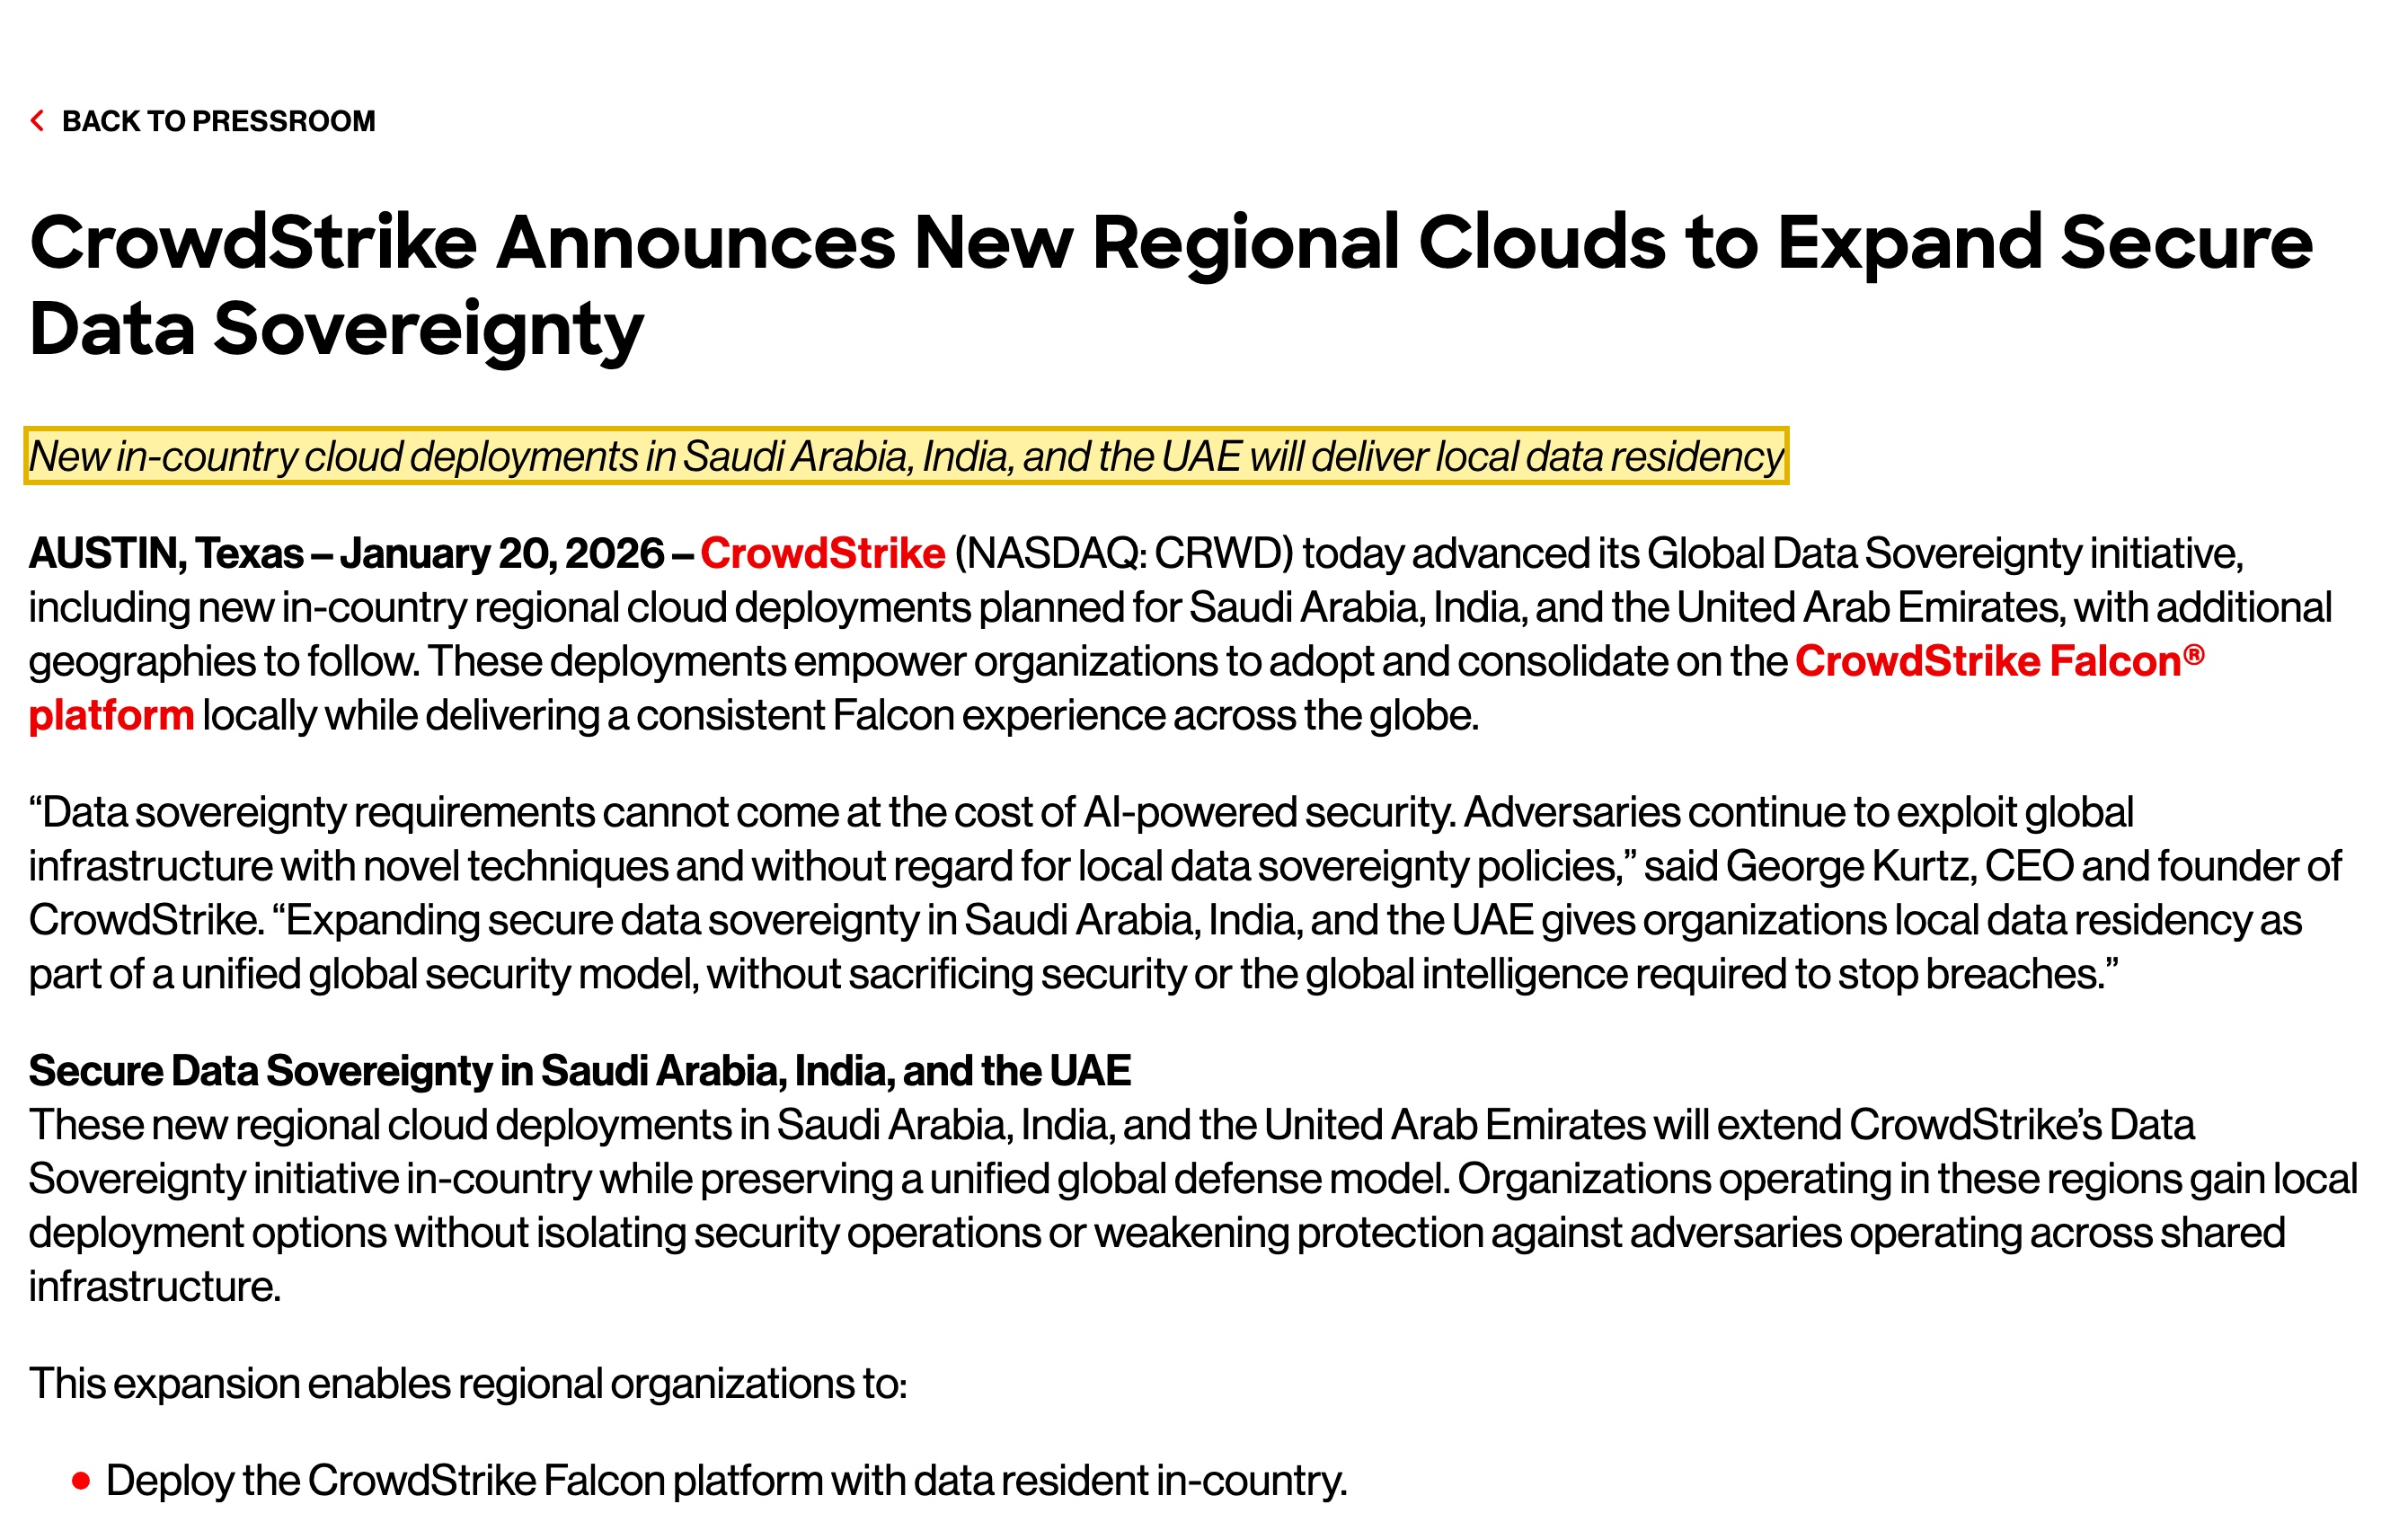
| CrowdStrike's new in-country data-residency clouds are in Saudi Arabia, India, and the UAE — not mainland China. CrowdStrike's own announcement states that “New in-country cloud deployments in Saudi Arabia, India, and the UAE will deliver local data residency,” as part of regional cloud deployments “planned for Saudi Arabia, India, and the United Arab Emirates, with additional geographies to follow.” No mainland-China Falcon region is named, so China-collected endpoint telemetry has no in-country Falcon home. | CrowdStrike, “CrowdStrike Announces New Regional Clouds to Expand Secure Data Sovereignty” (crowdstrike.com), retrieved 2026-10-09 |
| Falcon's documented cloud regions are US and EU, plus a US GovCloud — with no China region. CrowdStrike's developer documentation pairs the Falcon API with region hosts api.crowdstrike.com (US-1, default), api.us-2.crowdstrike.com (US-2), api.eu-1.crowdstrike.com (EU-1), and api.laggar.gcw.crowdstrike.com (US-GOV) — commercial clouds in the United States and the European Union plus a US government cloud, and no mainland-China endpoint to send telemetry to. | CrowdStrike Developer Documentation — Falcon API base URLs / regions (developer.crowdstrike.com), retrieved 2026-10-09 |
| Endpoint telemetry collected in China and held on a US or EU Falcon cloud is a PIPL cross-border transfer. The process, user, network, and file activity a Falcon sensor streams is personal information; moving it from endpoints in mainland China to an offshore Falcon cloud triggers PIPL Articles 38–40 — notice, a separate consent, and one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification). The duty falls on the handler — you — not on CrowdStrike as processor. | Personal Information Protection Law of the PRC, Articles 38–40 (cac.gov.cn), retrieved 2026-10-09 |
| At volume, for “important data,” or for a CIIO, the telemetry can trigger a data-export security assessment and an in-country storage duty. Because EDR telemetry concentrates detailed activity data, a China deployment can cross the thresholds of China's data-export security assessment (数据出境安全评估, CAC Order No. 11) before anything leaves; and for a critical information infrastructure operator, the Cybersecurity Law's Article 39 (formerly Article 37) requires personal information generated in China to be stored in China — a duty an offshore Falcon region cannot meet. | Measures for Security Assessment of Data Exports (数据出境安全评估办法), CAC Order No. 11 (cac.gov.cn); Cybersecurity Law of the PRC, Article 39 (formerly Article 37), retrieved 2026-10-09 |
Sources verified by the 21YunBox compliance team on 2026-10-09.
For an organization running CrowdStrike Falcon across devices in mainland China, the first instinct is to check whether the sensor can even phone home — and on the wire it generally can: the Falcon agent is designed to hold a persistent connection to CrowdStrike’s cloud, and it is not a consumer service blocked at the border. So reachability is not where the China decision is settled. What settles it is data residency and cross-border transfer — where the endpoint telemetry Falcon continuously ships comes to rest, and whether moving that data out of the country was lawful in the first place.
That is because CrowdStrike runs no Falcon cloud inside mainland China. Its commercial regions sit in the United States and the European Union, plus a US GovCloud; the in-country data-residency clouds it is now standing up are in Saudi Arabia, India, and the UAE. The moment the process, user, network, and file telemetry your Falcon sensors gather from endpoints in China lands in a US or EU Falcon cloud, you have made a cross-border transfer (数据出境) of personal information — and a separate body of law decides whether that was allowed.
CrowdStrike in China at a glance
| What decides it | In CrowdStrike's own terms — and China's law |
|---|---|
| What it is | CrowdStrike Falcon is an endpoint detection & response (EDR/XDR) platform. A lightweight sensor on each endpoint continuously streams telemetry — process execution, logged-in users, network connections, file activity — to CrowdStrike's cloud, so it holds a detailed, continuous record of endpoint and user activity. |
| Is it reachable from the mainland? | Generally, yes. The sensor is built to maintain a persistent connection to CrowdStrike's cloud, and it is not a consumer service China blocks at the border. Reachability is not the China question. (Cross-border connectivity from the mainland to an offshore cloud can be inconsistent — an operational matter, below, not the decision.) |
| Where does the telemetry live? | Offshore. CrowdStrike's documented Falcon clouds are US regions (US-1, US-2) and an EU region (EU-1), plus a US GovCloud; its new in-country data-residency clouds are Saudi Arabia, India, and the UAE. There is no mainland-China region. |
| Collecting China telemetry into it | The telemetry is personal information — usernames, device identifiers, IP addresses, file and process activity. Holding it in a US or EU Falcon cloud is a cross-border transfer (数据出境) under PIPL (Articles 38–40): notice, a separate consent, and one transfer mechanism. Above thresholds, for “important data,” or for a CIIO, a data-export security assessment may apply, and Cybersecurity Law Article 39 (formerly Article 37) sets an in-country storage duty an offshore region cannot meet. |
| The lawful path | Keep the China endpoint telemetry on an in-country, consented, PIPL-compliant footing, send offshore Falcon only what may lawfully leave, keep Falcon for your other regions, and deliver your China-facing public services in-country on ICP-filed infrastructure. 21YunBox maps, localizes, and delivers; it never uses or suggests circumvention of any kind. |
Reachable — but where does the endpoint telemetry live?
CrowdStrike’s China posture is set by where its clouds are, not by a load-time test. The Falcon sensor is designed to keep a live link to CrowdStrike’s cloud, and from the mainland that link generally comes up — so “can the sensor reach CrowdStrike from Shanghai?” is the wrong test. It reaches. The real question is where your China-collected telemetry sits and whether it had a lawful basis to leave the country at all. For that reason this page publishes no first-party China latency or reachability figure for Falcon: speed is not the axis for a decision that turns on residency and cross-border transfer.
One operational note worth naming: cross-border connectivity from the mainland to an offshore cloud can be inconsistent, and the temptation is to force the connection through a network workaround. 21YunBox neither uses nor suggests any such circumvention — it is both a compliance risk and beside the point. The productive question is how to keep the China telemetry on a lawful footing.
No mainland-China Falcon cloud, so the telemetry crosses the border
CrowdStrike documents its Falcon clouds plainly, and none is in the mainland. Its developer documentation pairs the Falcon API with region hosts for US-1 (the default, api.crowdstrike.com), US-2, EU-1, and a US GovCloud — commercial environments in the United States and the European Union plus a US government cloud. Its own data-sovereignty announcement then adds in-country residency clouds, but only for Saudi Arabia, India, and the UAE, “with additional geographies to follow.” On today’s map there is no Falcon region inside mainland China to send endpoint data to.
So the telemetry your sensors stream from China endpoints lands in a US or EU Falcon cloud, and that makes its collection a cross-border transfer of personal information under China’s Personal Information Protection Law. PIPL puts the duty on the handler — you, the organization operating the endpoints, not CrowdStrike the processor: Articles 38–40 require notice, a separate consent distinct from any general IT or employment agreement, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. The security tool collecting the data does not discharge the duty attached to where that data is then stored.
Endpoint telemetry is dense personal information — which raises the stakes
The residency question is sharper for EDR than for most software, because of what the telemetry is. Falcon’s whole value is visibility: it records who logged in, what executed, what connected where, and the file paths and command lines behind it — a continuous, identifiable picture of activity on each device. That density is exactly what China’s law scrutinizes most closely, and it pulls in two further regimes beyond the baseline transfer rules.
First, assessment: above certain volume thresholds, where the data qualifies as “important data,” or where your organization is a critical information infrastructure operator, the transfer may require China’s data-export security assessment (数据出境安全评估) before anything leaves the country. Second, residency: if you are a critical information infrastructure operator, the Cybersecurity Law’s Article 39 (formerly Article 37 — the data-localization provision was renumbered by the 2025 amendment that took effect on January 1, 2026, with its substance unchanged) requires personal information generated in China to be stored in China — an in-country storage duty an offshore Falcon cloud cannot satisfy no matter how the tenant is configured. None of this turns on how fast an event is ingested; it turns on whether the data had a lawful basis to be there, and in what volume.
Why pointing Falcon at “a different region” isn’t the fix
The obvious move is to switch the tenant’s region and keep the data in-place — but the only homes Falcon offers are the US, the EU, a US GovCloud, and the new in-country clouds in Saudi Arabia, India, and the UAE. Not one is in mainland China, so none resolves a China residency duty; moving a tenant from the US region to the EU region merely relocates the cross-border transfer, it does not end it. Keeping China-collected endpoint telemetry in-country means standing up an in-country, consented handling path for that data, and sending offshore Falcon only what may lawfully leave. That split — what must stay, what may go — is the heart of the work, and it is a legal question before it is a technical one.
This is a risk map, not a verdict: whether you owe separate consent, a transfer mechanism, a data-export security assessment, in-country storage, or some combination depends on your data volumes, your role as handler, and who your endpoints’ users are — worth settling with counsel before you rely on it.
The lawful path — map, localize, deliver
There is a lawful way to run endpoint security for a China presence, and it has a shape. First, map: our China team works through your PIPL exposure for the endpoint telemetry — which process, user, network, and file data collected in China must stay in the country, what may lawfully leave, where a data-export security assessment or an Article 39 storage duty bites, and what notice and consent the people behind those endpoints are owed. The legal conclusions are settled with counsel; we build the technical picture that feeds them.
Then localize: we stand up and integrate an in-country, consented, PIPL-compliant handling path for the China endpoint telemetry, so the security signal you depend on keeps working while that data stops leaving the country by default — and you keep Falcon for the regions where it already serves you. Where a China-legal, in-country option fits your estate, we localize the customer’s stack onto it rather than route sensitive telemetry offshore.
Then deliver: the customer-facing sites and apps your organization actually serves to users in mainland China are public internet services, so they carry an ICP filing (备案) duty and need compliant, in-country delivery. 21YunBox delivers them in-country — the 21YunBox Optimizer — in front of what you already run, with no rebuild and no re-platform. The result is a China presence that runs legally and compliantly for your users in China. What we never do — and what no one lawfully can — is hand you a way around China’s data-export rules or any network restriction: we localize what must stay and deliver in-country, and we never move personal information out of China by stealth.
Related reading:
- Cross-border data transfers under PIPL
- China’s data-export security assessment
- China’s Cybersecurity Law (data localization, Article 39)
- How to get an ICP filing for China