Does Coursera Work in China? Data Residency, ICP & Cross-Border Rules
Coursera is US-hosted — by its own Privacy Notice its site runs on servers in the United States, with no mainland-China region. Your China learners' enrollments, progress and assessment records sit offshore under PIPL, and a China-facing paid course site adds an ICP and licensed-payment door a speed test never sees.
Does Coursera work in China?
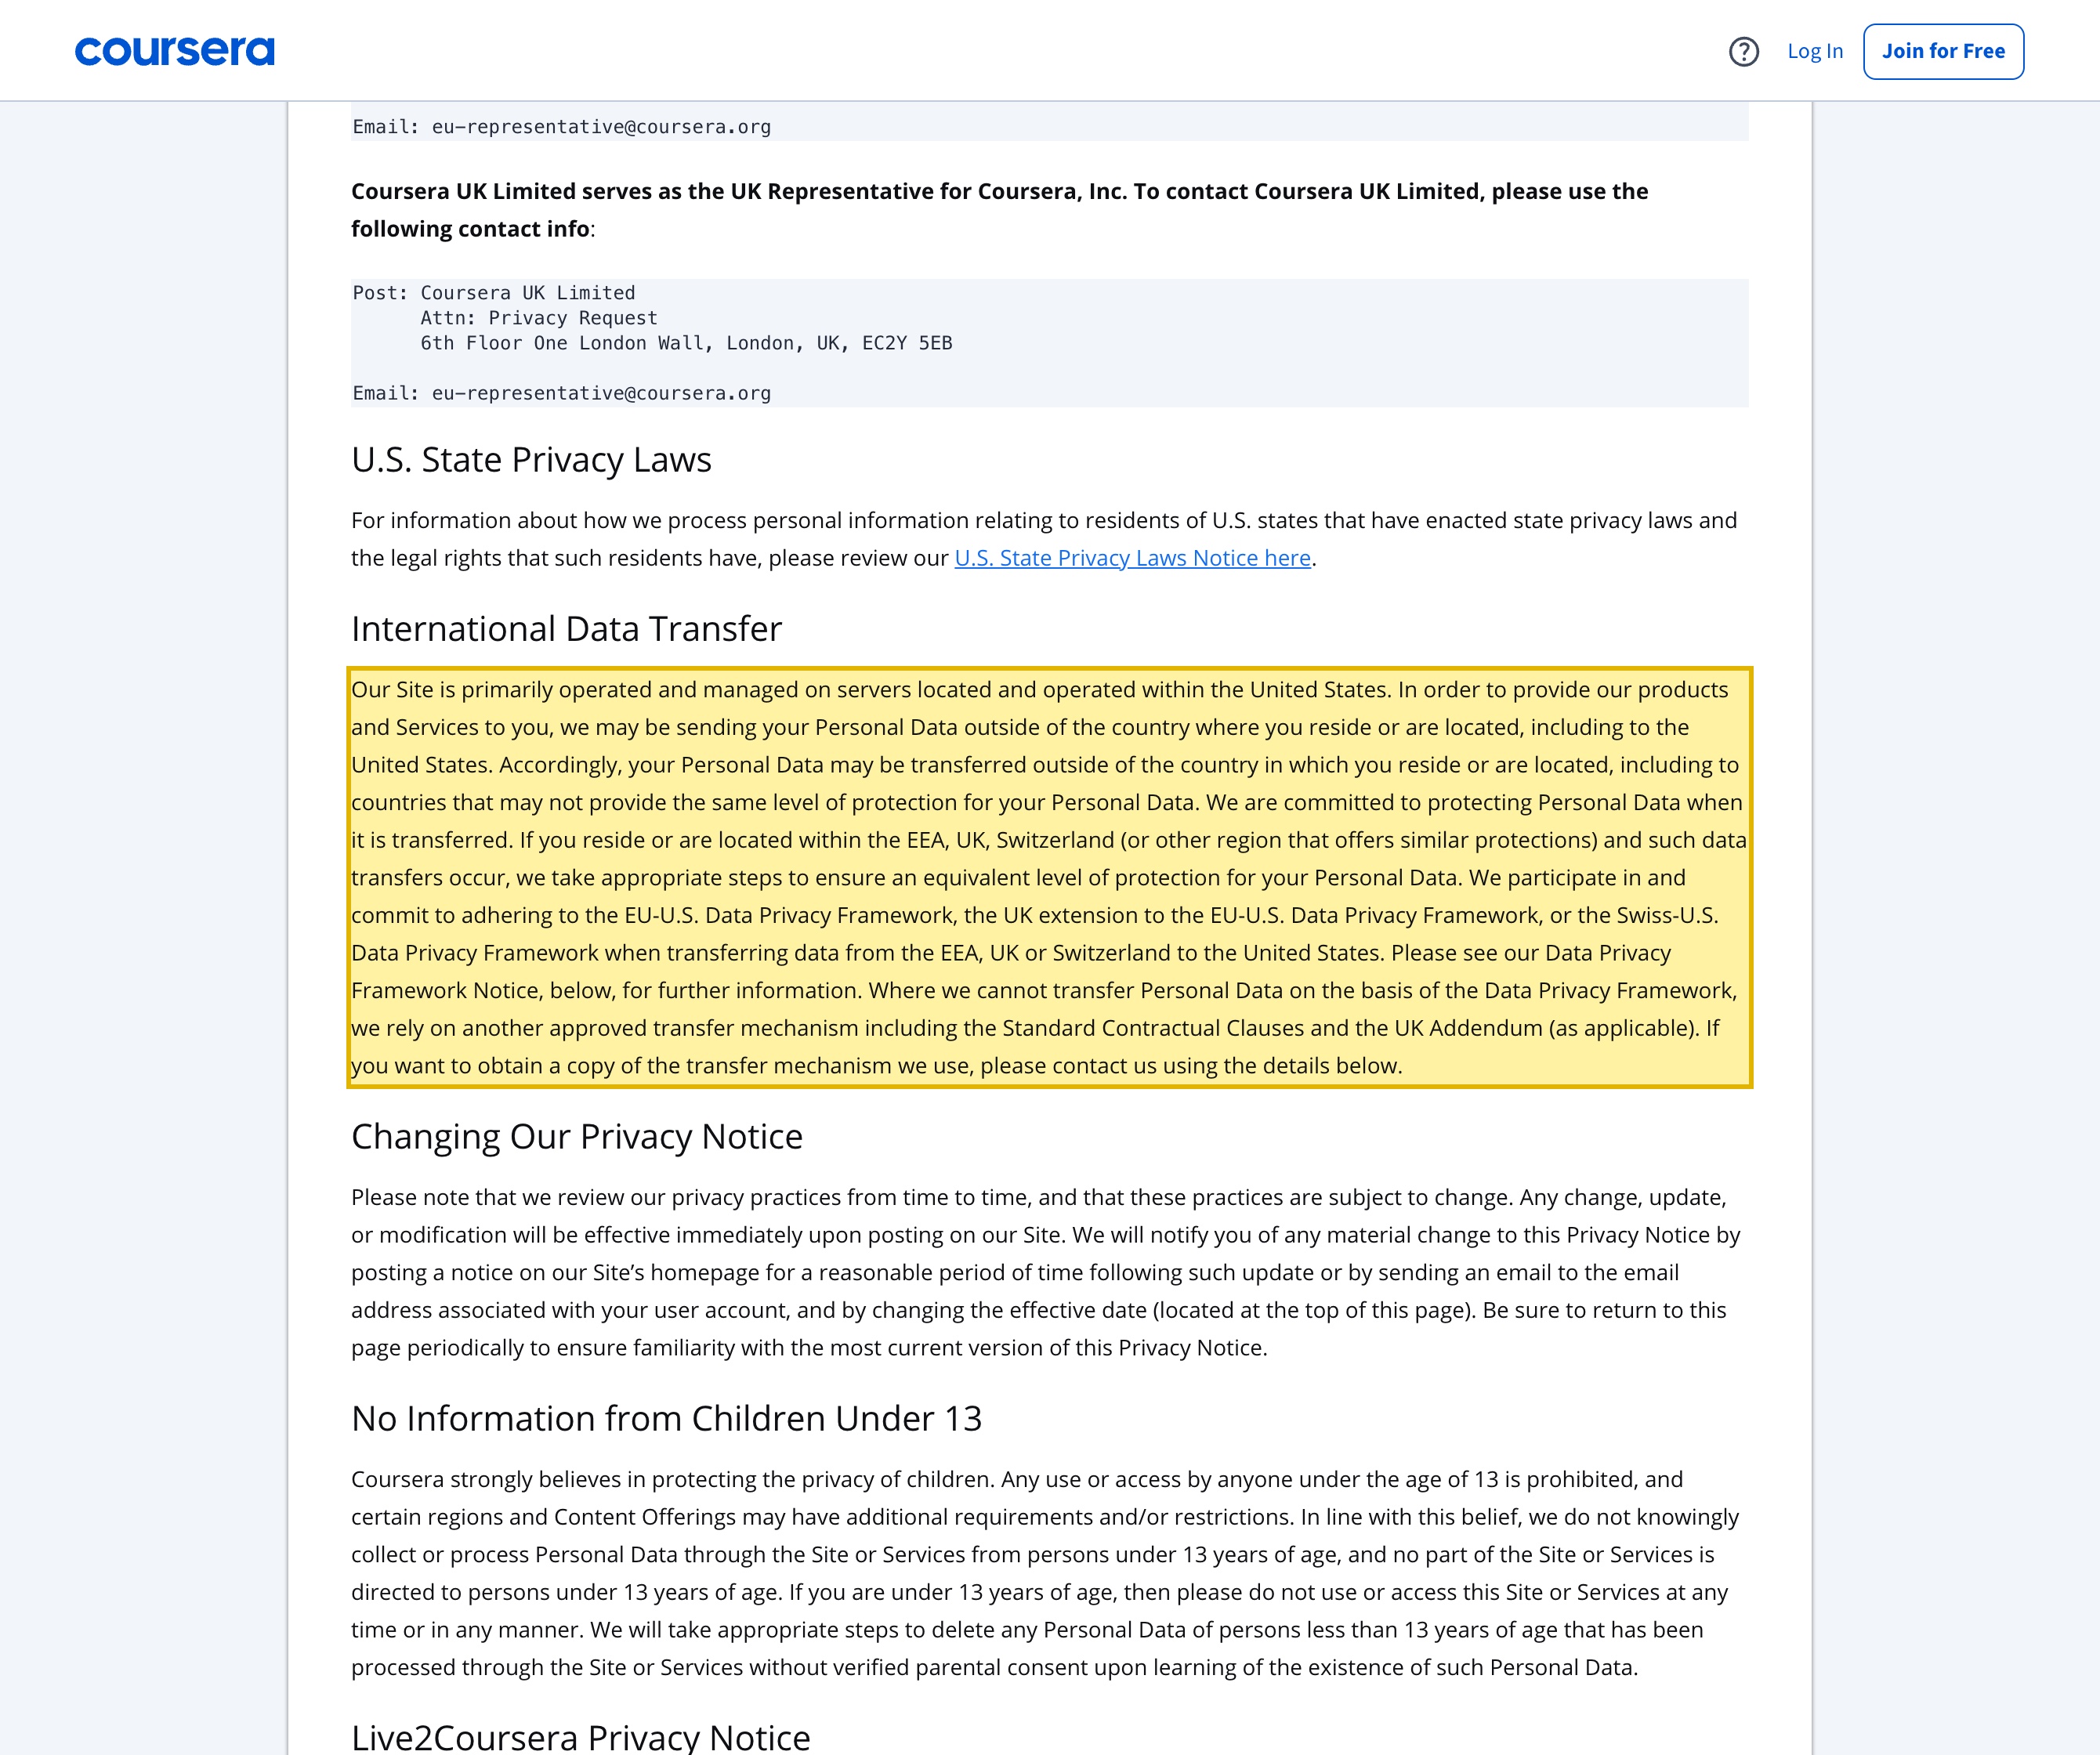
Reaching Coursera from China was never the question — where your China learners' records live is. Coursera's own Privacy Notice says its site “is primarily operated and managed on servers located and operated within the United States,” and its sub-processor list places cloud storage (AWS) in the USA, with no mainland-China region — so the identities, enrollments, progress, completion and assessment records of your China learners sit offshore.
Held abroad, that learner personal information is a cross-border transfer under PIPL Articles 38–40 (notice, a separate consent, and one transfer mechanism), and for a CIIO or high-volume handler the Cybersecurity Law Article 39 (formerly Article 37) wants that China-collected data stored in the mainland. The same applies to the workforce learning records in Coursera for Business or Campus.
And a reachability check never sees the second door: a China-facing course site is a public internet information service that needs an ICP filing, and selling courses to mainland learners must run on a licensed in-China payment channel. Keeping the regulated learner data in-country — and filing and licensing the China-facing site — is the answer.
What Coursera's own documentation says about China
| Fact | Primary source |
|---|---|
| Coursera's Privacy Notice states that “Our Site is primarily operated and managed on servers located and operated within the United States,” and that using Coursera from abroad may send your personal data “including to the United States”; it names no mainland-China hosting location. | Coursera — Privacy Notice (coursera.org/about/privacy; retrieved 2026-10-13) |
| Coursera's Data Protection Addendum lists its cloud storage sub-processor as “Amazon Web Services, Inc.” with a processing location of “USA”; every sub-processor location the table names sits outside mainland China, and no mainland-China region is offered. | Coursera — Data Protection Addendum, Exhibit D sub-processor list (retrieved 2026-10-13) |
| Under PIPL Articles 38–40, personal information may leave China only via a CAC security assessment, the CAC standard contract, or certification — with Article 13/23 notice and a separate consent. China learners' records held on Coursera's US servers are such a cross-border transfer. | PIPL — cross-border transfer rules (21YunBox gov-doc summary; retrieved 2026-10-13) |
| For a CIIO or high-volume handler, the Cybersecurity Law Article 39 (formerly Article 37) requires personal information collected in China to be stored in the mainland; and a China-facing course site is an internet information service needing an ICP filing, with paid enrollments routed through a licensed in-China payment channel. | China Cybersecurity Law (data localization) & ICP filing (21YunBox gov-doc summaries; retrieved 2026-10-13) |
Sources verified by the 21YunBox compliance team on 2026-10-13.
For a business running Coursera into mainland China — whether you enroll consumers on the course marketplace or roll out Coursera for Business or Campus to your workforce — the decision is not a performance benchmark. It is a question about where your learners’ personal data lives, and whether a China-facing course site is cleared to operate. Coursera is not something you host; Coursera hosts it for you, and it holds a learner personal-data system: each China learner’s identity, the courses they enroll in, their progress and completion records, quiz and assessment results, and — for paid courses, certificates and degrees — order and payment-adjacent data. By Coursera’s own Privacy Notice, its site runs on servers in the United States; its published sub-processor list places cloud storage in the USA. None of it is in mainland China. That single fact sets a cross-border-data floor under everything you do — and it sits next to a second question a speed test never asks: a China-facing course site that sells to mainland learners is a licensed, filed activity, not just a page that loads. Coursera is an excellent platform, and nothing here asks you to leave it; this is about the China-residency and compliance layer it was never built to provide. 21YunBox never uses or suggests circumvention of any kind.
Coursera in China at a glance
| What decides it | In Coursera's own words — and China's own law |
|---|---|
| What it is | An online-course marketplace and, for organizations, Coursera for Business and Coursera Campus. It holds your learners' identities, enrollments, progress and completion records, quiz and assessment results, and — for paid courses, certificates and degrees — order and payment-adjacent data. Coursera hosts all of it for you; you do not host it. |
| A mainland-China region? | No. Coursera's Privacy Notice says its site is “primarily operated and managed on servers located and operated within the United States,” and its Data Protection Addendum lists cloud storage sub-processor “Amazon Web Services, Inc.” with a processing location of “USA.” No mainland-China hosting location is named. Confirm your own hosting with Coursera. |
| Learner PII residency (the floor) | The identities, enrollments, progress, completion and assessment records of your China learners are personal information. Held offshore they are a cross-border transfer under PIPL — notice, a separate consent, and a transfer mechanism (Articles 38–40; consent in Articles 13 and 23). CIIOs and high-volume handlers must store that data in-country (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). |
| A China-facing course site | Any China-facing course portal, academy or sign-in landing you stand up for learners is a public internet information service in its own right — it needs an ICP filing (备案) on mainland hosting held by a mainland legal entity. Offshore SaaS gives a filing nothing to attach to. |
| Selling courses to China learners | If you take payment for courses, certificates or degrees from learners in the mainland, the payment must run through a licensed in-China channel. A China-facing commercial course site cannot lawfully collect payment on an unlicensed offshore flow — a door a reachability check never sees. |
| Coursera for Business / Campus | Rolling courses out to a China workforce or student body puts those learners' identities, enrollments and completion records into the same offshore US hosting — a workforce/learner personal-data store governed by PIPL's cross-border rules, not a question of whether the video streams. |
No mainland region — your learners’ records sit offshore
Coursera is not something you host; Coursera hosts it for you, and Coursera publishes where. Its Privacy Notice is explicit: “Our Site is primarily operated and managed on servers located and operated within the United States,” and when you use Coursera from abroad it may be “sending your Personal Data outside of the country where you reside or are located, including to the United States.” Its Data Protection Addendum carries the same geography at the infrastructure layer: the cloud storage sub-processor is listed as “Amazon Web Services, Inc.” with a processing location of “USA,” and every sub-processor location the table names sits outside mainland China. Mainland China does not appear as a storage location anywhere.
That matters because of what Coursera holds. A course platform is a learner personal-information store: each learner’s identity, the courses they take, their progress and completion history, their quiz and assessment results, and — for paid courses — their order and payment-adjacent records all flow into Coursera and come to rest in those US servers. For your mainland-China learners, that data is offshore the moment it is collected — which turns the China question into a legal one before it is ever a performance one. This is regulated personal data, not “can the video stream.”
Selling courses into China: the ICP and payment door
Here is the half a reachability check never sees. A course that merely loads in Shanghai tells you nothing about whether you may lawfully run a course site there. The moment you stand up a public surface for mainland learners — a China-facing course portal, a branded academy, a Coursera for Business sign-in landing, a marketing-and-enrollment page — that surface is a public internet information service in its own right. It needs an ICP filing (备案) attached to a hosting resource inside the mainland, held by a mainland legal entity. Offshore SaaS gives a filing nothing to attach to; being reachable from China is a network fact, while being cleared to publish there is a licensing one.
And if you take payment from those learners — for a paid course, a certificate, a Specialization or a degree — the payment has to run through a licensed in-China channel. A China-facing commercial course site cannot lawfully collect payment on an unlicensed offshore flow. Whether this prong applies to you depends on how you deploy Coursera and whether you operate the China-facing surface and the enrollment yourself — settle it with counsel before you build.
The data at the border: PIPL consent and cross-border rules
Every China learner you enroll hands over personal information — an identity, an enrollment and learning history, quiz and assessment results, and for paid courses an order record — and because Coursera stores it in offshore US servers, it crosses the border the moment it is collected. China’s cross-border data transfer rules treat that as a cross-border transfer, and the handler — you, the business, not Coursera — must give notice, obtain a separate consent (not a bundled, take-it-or-leave-it consent), and clear one transfer mechanism: a CAC security assessment, the CAC standard contract, or certification (PIPL Articles 38–40, with the consent duty in Articles 13 and 23).
If you are a critical information infrastructure operator, or you process personal information above the regulated volumes, that learner data has to be stored inside the mainland in the first place (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37, renumbered by the 2025 amendment in force January 1, 2026)) — an in-country storage duty no US region can satisfy.
Why a reachability check misses this
This is why a speed test or an uptime check answers the wrong question. A probe can tell you a course page paints for a learner in Shanghai; it cannot tell you that your learners’ records just crossed the border without a lawful basis, that the separate consent these transfers require was never obtained, that in-country storage may be owed, that your China-facing course site is unfiled, or that paid enrollments are running on an unlicensed offshore payment flow. The things that decide whether you may operate live in filings, consents, transfer mechanisms and payment licensing — not in milliseconds. Making an offshore platform merely load faster changes none of them, and 21YunBox never uses or suggests circumvention of any kind.
The lawful path — map, localize, deliver
Map. We inventory what your Coursera setup actually holds — learner identities, enrollments, progress and completion records, quiz and assessment results, and any order and payment-adjacent data — where each sits today, the consent and residency basis for every flow out of China, and whether you run a China-facing course site that needs an ICP filing and a licensed in-China payment path.
Localize and govern. We keep the regulated China learner data on a China-resident, in-country-deployed footing; stand up the Article 13/23 notice and the separate consent these transfers require; route payment for mainland learners through a licensed in-China channel; and minimize what crosses the border — never through circumvention of any kind.
Deliver. We ICP-file the China-facing course portal and serve it in-country with the 21YunBox Optimizer, set in front of the stack you already run — no rebuild, no re-platform, no second codebase.
The rule underneath all three: making an offshore platform merely reachable from China is not the answer, because the learner records are still offshore, the consent is still missing, the China-facing site is still unfiled, and paid enrollments are still on an unlicensed flow. Keeping the regulated learner data in-country, on a consented and (where needed) ICP-filed and licensed path, is.
Whether you owe in-country storage, a separate consent, an ICP filing, a licensed payment channel, or all of them depends on how much learner data you hold, your role, and whether you operate the China-facing course site yourself — so settle it with counsel before you build. Tell us who your China learners are and how you run Coursera, and we’ll map the path and deliver any China-facing portal in-country. Reach out for a compliance assessment and a quote.
Related reading:
- Cross-border data transfers under PIPL
- China’s Personal Information Protection Law (PIPL)
- China’s Cybersecurity Law — data localization (Article 39, formerly Article 37)
- What is the China ICP license, and how do you get one?