Does Calendly Work in China? Data Residency, ICP & Cross-Border Rules
Calendly's booking page loads from the mainland — but that is not the China question. Calendly stores account-holder and invitee data (name, email, meeting purpose, often a phone number) in U.S. data centers run by Google Cloud and AWS, with no mainland-China region. A China-facing booking page is both a cross-border transfer of invitee personal information under PIPL and a public internet service carrying an ICP filing duty. A compliance-first look at the data-residency, consent and ICP exposure — and the lawful in-country path, with no circumvention of any kind.
Does Calendly work in China?
Whether you can use Calendly for a China-facing audience is a data-residency and consent question, not a question of whether the calendar loads. A Calendly booking page can open from the mainland, and that is exactly what hides the real exposure.
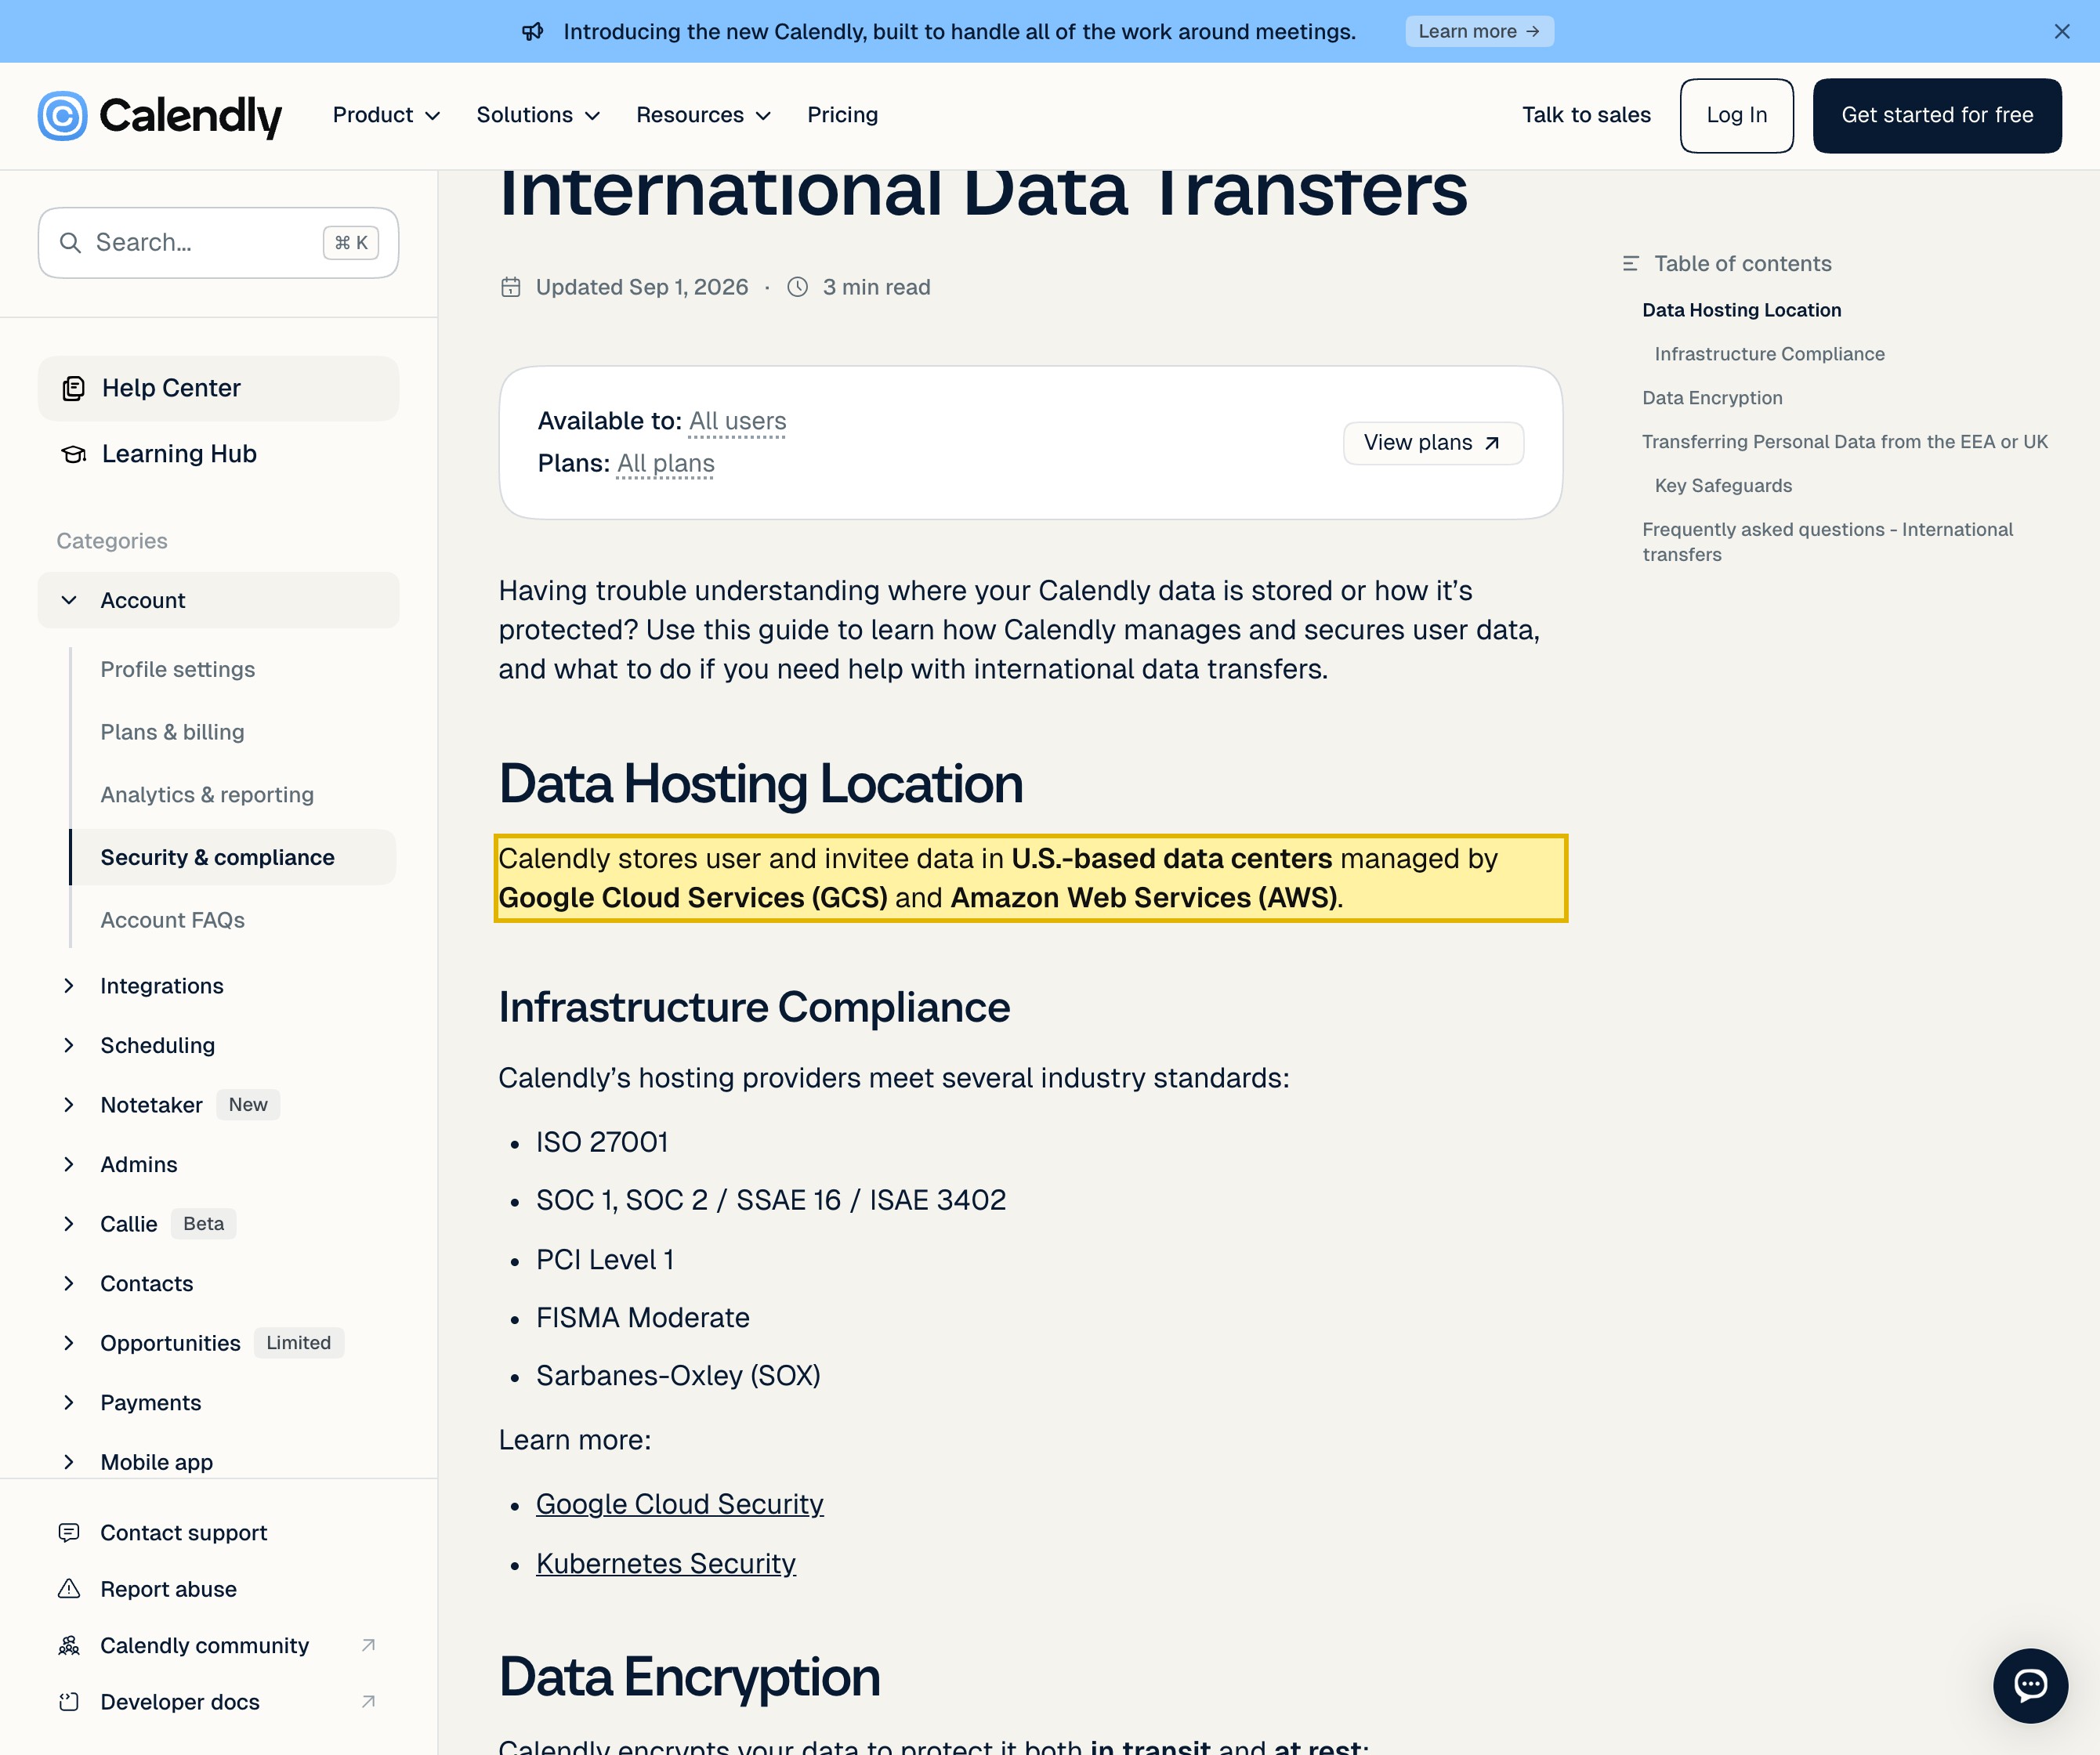
Every time someone in China books a meeting, Calendly collects their name, email, the meeting purpose they type in and often a phone number, and stores it offshore — its own Help Center says it keeps user and invitee data in facilities "managed by Google Cloud Services (GCS) and Amazon Web Services (AWS)," with no mainland-China region. So a China-facing booking page is both a cross-border transfer of invitee personal information under PIPL — owing notice and a separate consent at the moment of booking — and a public internet service that carries an ICP filing duty of its own.
This is a risk picture, not a verdict — your duties turn on what you collect and your role as handler. Our China team can map your Calendly invitee-data exposure with you →
What Calendly's own documentation says about China
| Fact | Primary source |
|---|---|
| In Calendly's own words: Calendly stores "user and invitee data in U.S.-based data centers managed by Google Cloud Services (GCS) and Amazon Web Services (AWS)." The page names no country other than the United States and lists no mainland-China region or China data option. | Calendly Help Center — Data Storage and International Data Transfers, retrieved 2026-10-12 |
| Calendly treats getting data to the U.S. as a cross-border transfer: for personal data gathered from people in the EEA or UK, its Help Center says "Standard Contractual Clauses (SCCs) are included in Calendly's Data Processing Agreement (DPA)" and a "UK Addendum is also part of the DPA." It offers no equivalent in-country option for mainland China — the data still lands in its U.S. facilities. | Calendly Help Center — Data Storage and International Data Transfers, retrieved 2026-10-12 |
| Because the booking page collects invitee personal information in China and Calendly stores it offshore, PIPL governs the handler — you, not Calendly. Articles 38–40 require one transfer mechanism, and Articles 13 and 23 require notice and a separate, informed consent taken from the invitee at the point of booking, distinct from any general terms. | PIPL, Articles 13, 23 and 38–40 |
| A booking page served to the mainland public is a public internet service needing an ICP filing bound to in-country hosting; Calendly names no mainland region, so there is nothing of its own to file against. For a critical information infrastructure operator, the Cybersecurity Law's Article 39 (formerly Article 37) adds an in-country storage duty an offshore calendar cannot meet. | China ICP filing (State Council Order No. 292); Cybersecurity Law, Article 39 (formerly Article 37) |
Sources verified by the 21YunBox compliance team on 2026-10-12.
The first instinct with a tool like Calendly is to ask whether the booking page even loads from Shanghai or Shenzhen. It usually does — and that is exactly what hides the real question. Calendly is a scheduling tool, so the thing that matters is not whether the calendar renders but what the booking page quietly gathers and where it keeps it. Every invitee who picks a time hands over a name, an email address, the meeting purpose they type into your questions, and frequently a phone number for reminders. That is personal information, collected from people in China, and the moment it is stored a different body of law decides whether that was lawful. Even if every booking page loaded instantly, that question would still stand — which is why this is a compliance decision, not a performance one. And to be unambiguous from the outset: 21YunBox never uses or suggests circumvention of any kind; for anything that will not open in the mainland, the answer is a China-resident alternative, never a way around a block.
Calendly in China at a glance
| What decides it | In Calendly's own terms — and China's law |
|---|---|
| What it is | Calendly is a scheduling and booking tool. Its public booking page collects each invitee's name, email, the meeting purpose they type in and often a phone number. There is no Calendly data region or operating entity inside mainland China. |
| Is it reachable from the mainland? | A Calendly booking page generally loads from the mainland. But reachability is not the China question — a working calendar reveals nothing about where the invitee data goes — and 21YunBox never uses or suggests circumvention to force a connection to anything that will not open. |
| Where does the invitee data actually sit? | Offshore. Calendly's Help Center says it stores “user and invitee data in U.S.-based data centers managed by Google Cloud Services (GCS) and Amazon Web Services (AWS).” China is not a region, and there is no China data instance to select. |
| Collecting China invitee data into it | A cross-border transfer (数据出境) of personal information under PIPL (Articles 38–40): a transfer mechanism, plus — under Articles 13 and 23 — notice and a separate, informed consent obtained from the invitee at the point of booking. For a critical information infrastructure operator, the Cybersecurity Law's Article 39 (formerly Article 37) adds an in-country storage duty an offshore calendar cannot meet. |
| Serving a public China-facing booking page | A booking page served to the mainland public is a public internet service and needs an ICP filing (备案) bound to a mainland hosting resource. Calendly names no mainland region, so there is nothing of its own to file against. |
| The lawful path | Keep the invitee personal information that must stay in-country on a consented, China-resident booking surface, move only what may lawfully leave, and ICP-file and deliver the China-facing surface in-country. 21YunBox maps, localizes and delivers; it never uses or suggests circumvention. |
The data-residency question: your invitees’ data sits offshore
Here is the gate most teams miss. A Calendly booking page is not just a time-picker — it is a small intake form. Everything an invitee enters when they book — their name, their email, the answers to your meeting questions, and, where you switch on reminders, a phone number — is stored on Calendly’s infrastructure, and by Calendly’s own account that infrastructure sits in the United States. Its Help Center puts it plainly: Calendly stores “user and invitee data in U.S.-based data centers managed by Google Cloud Services (GCS) and Amazon Web Services (AWS).” None of those is in China. So the ordinary act of a prospect in Shanghai booking a call places personal information collected in China onto storage outside the country. That is a cross-border transfer of personal information under China’s Personal Information Protection Law.
PIPL puts the duty on the handler — you, Calendly’s customer, not the vendor. Articles 38–40 require one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. And because a booking page gathers data straight from the public, Articles 13 and 23 bite at the moment of booking: you owe the invitee clear notice and a separate consent, distinct from any blanket terms, before their details cross the border. Calendly’s own cross-border posture confirms it treats this as a transfer out of the region of collection — for EEA and UK data its Help Center says “Standard Contractual Clauses (SCCs) are included in Calendly’s Data Processing Agreement (DPA)” — but there is no equivalent in-country option for the mainland; the data still lands in its U.S. facilities.
And if your organization is a critical information infrastructure operator, the Cybersecurity Law adds a harder duty. Its Article 39 — renumbered from Article 37 in the 2016 text by the amendment in force January 1, 2026, the obligation unchanged — requires that personal information collected and generated in the mainland be stored in the mainland. An offshore Calendly calendar cannot satisfy that. Which of these obligations actually bite on your data is a risk to confirm with counsel against what your booking pages collect and from whom.
Why there is no Calendly “China region” to switch on
With some vendors the fix is to move onto a mainland instance the vendor itself runs. Calendly is not one of them. Its hosting is the U.S. facilities its Help Center names, full stop; there is no China setting to enable and no in-China operating partner for your account. So localizing for China is not a toggle inside Calendly — it is a decision about where the invitee data lives.
The work, then, is to separate the China-collected invitee records that must stay in the country from those that may lawfully leave: capture the first on a consented, China-resident booking surface inside the mainland, and let only what may lawfully leave reach the Calendly your team already uses for scheduling. There is no clean, drop-in domestic twin of Calendly to name here — what there is, is a lawful in-country pattern: consented, China-resident capture for the invitee data that has to stay, and that pattern is the heart of the fix.
Serving a China-facing booking page adds an ICP duty
If your use of Calendly is purely an internal scheduling aid among colleagues, the residency and consent questions above are the whole story. But the moment a booking page is served to the public from inside the mainland — an embedded “book a demo” widget, a sales-intake link, a support-scheduling page — that surface is a public internet service in China and carries an ICP filing (备案) duty under State Council Order No. 292 and MIIT Order No. 33, bound to a hosting resource physically in the mainland. Calendly names no mainland region, so there is nothing of its own to file against.
This is a risk map, not a verdict: whether you owe a transfer mechanism, separate consent at booking, in-country storage, an ICP filing, or some combination turns on your data volumes, your role as handler and who your invitees are — worth settling with counsel before you rely on it.
Why a reachability check misses all of this
Open a Calendly link from the mainland and it will very likely load: you see a working calendar, free slots, a confirmation screen. That test answers one question — can the page render — and it is the wrong one. It sees none of what the compliance question turns on: that the name, email, meeting purpose and phone number the invitee just entered have been written to a U.S. data center, that no separate consent was taken at the point of booking, and that a public booking page served into China owes an ICP filing. A booking page that loads perfectly can still be a daily, unconsented export of invitee personal information. Reachability is a performance fact; residency, consent and ICP are the compliance facts, and only the second set decides whether you can lawfully run this for a China-facing audience.
The lawful path — map, localize, deliver
There is a lawful way to run scheduling for a China-facing audience, and it has a clear shape — three moves, in order.
Map. Our China team works through the PIPL cross-border exposure and the consent duties that attach to what your booking pages collect — sorting which China-collected invitee records carry personal information that must stay in-country, which may lawfully be transferred, and where an Article 13/23 consent, a transfer mechanism or an Article 39 storage duty applies. The legal conclusions are settled with counsel; we supply the technical picture that feeds them.
Localize. Keep the invitee personal information that must stay on a consented, China-resident booking surface inside the mainland, and let only what may lawfully leave reach your global Calendly — so your scheduling keeps running, without the booking page becoming the thing that carries regulated data out of China unlawfully. 21YunBox stands up and integrates that in-country capture in place of the collection that cannot run compliantly in the mainland.
Deliver. Any China-facing booking page is itself a public service in the mainland, so it needs compliant, ICP-filed, in-country delivery — the 21YunBox Optimizer, set in front of what you already run, with no rebuild and no re-platform. The result is scheduling and a booking surface that run legally and compliantly for your invitees in China. What we never do — and what no one lawfully can — is hand you a way around a block: we localize what must stay and deliver in-country, and circumvention is never on the table.
Related reading:
- China’s Personal Information Protection Law (PIPL)
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law (data localization, Article 39)
- How to get an ICP filing for China


