Does Meta Pixel Work in China? PIPL Cross-Border, Profiling Consent & Data Transfer
The Meta Pixel (formerly Facebook Pixel) tracks a visitor's clicks, page views and purchases — and via Advanced Matching ships hashed email, phone and name — to Meta offshore. For a mainland-China visitor that is a PIPL cross-border transfer, an Article 24 profiling mechanism, and tracking that needs separate consent. A compliance-first look at the data-export, profiling and consent exposure, and the lawful in-country path.
Does Meta Pixel work in China?
Meta's advertising platform does not operate normally in mainland China, so the Meta Pixel on a China-facing page buys you no usable measurement — it is dead weight that still ships your visitors' behavioral data to Meta offshore the moment it resolves.
On a mainland visitor the pixel collects page views, clicks and purchases, the Pixel ID and Facebook cookie, the visitor's IP, and — through Advanced Matching — hashed email, phone and name, and reports them to Meta's own offshore servers. That makes an ad tag a PIPL cross-border transfer of personal information (Articles 38–40) and an Article 24 profiling mechanism, and the tracking plus the overseas transfer each need their own separate, informed consent (Articles 13/23). The lawful lever is to gate or suppress the offshore pixel for mainland visitors and route measurement to a licensed in-country alternative — never to make the offshore pixel load.
This is a risk map, not a verdict — settle the specifics with counsel. The lawful lever is to govern and gate the offshore pixel, not to make it reach further. Our China team can map your exposure →
What Meta Pixel's own documentation says about China
| Fact | Primary source |
|---|---|
| The Meta Pixel collects behavioral data and device identifiers. Meta's developer documentation states the pixel can collect HTTP-header data that “may include data like IP addresses, information about the web browser,” the “Pixel ID and the Facebook Cookie,” and button-click data — “any buttons clicked by site visitors, the labels of those buttons and any pages visited as a result of the button clicks.” Under PIPL those online identifiers are personal information. | Meta for Developers, “Meta Pixel” documentation (developers.facebook.com), retrieved 2026-10-10 |
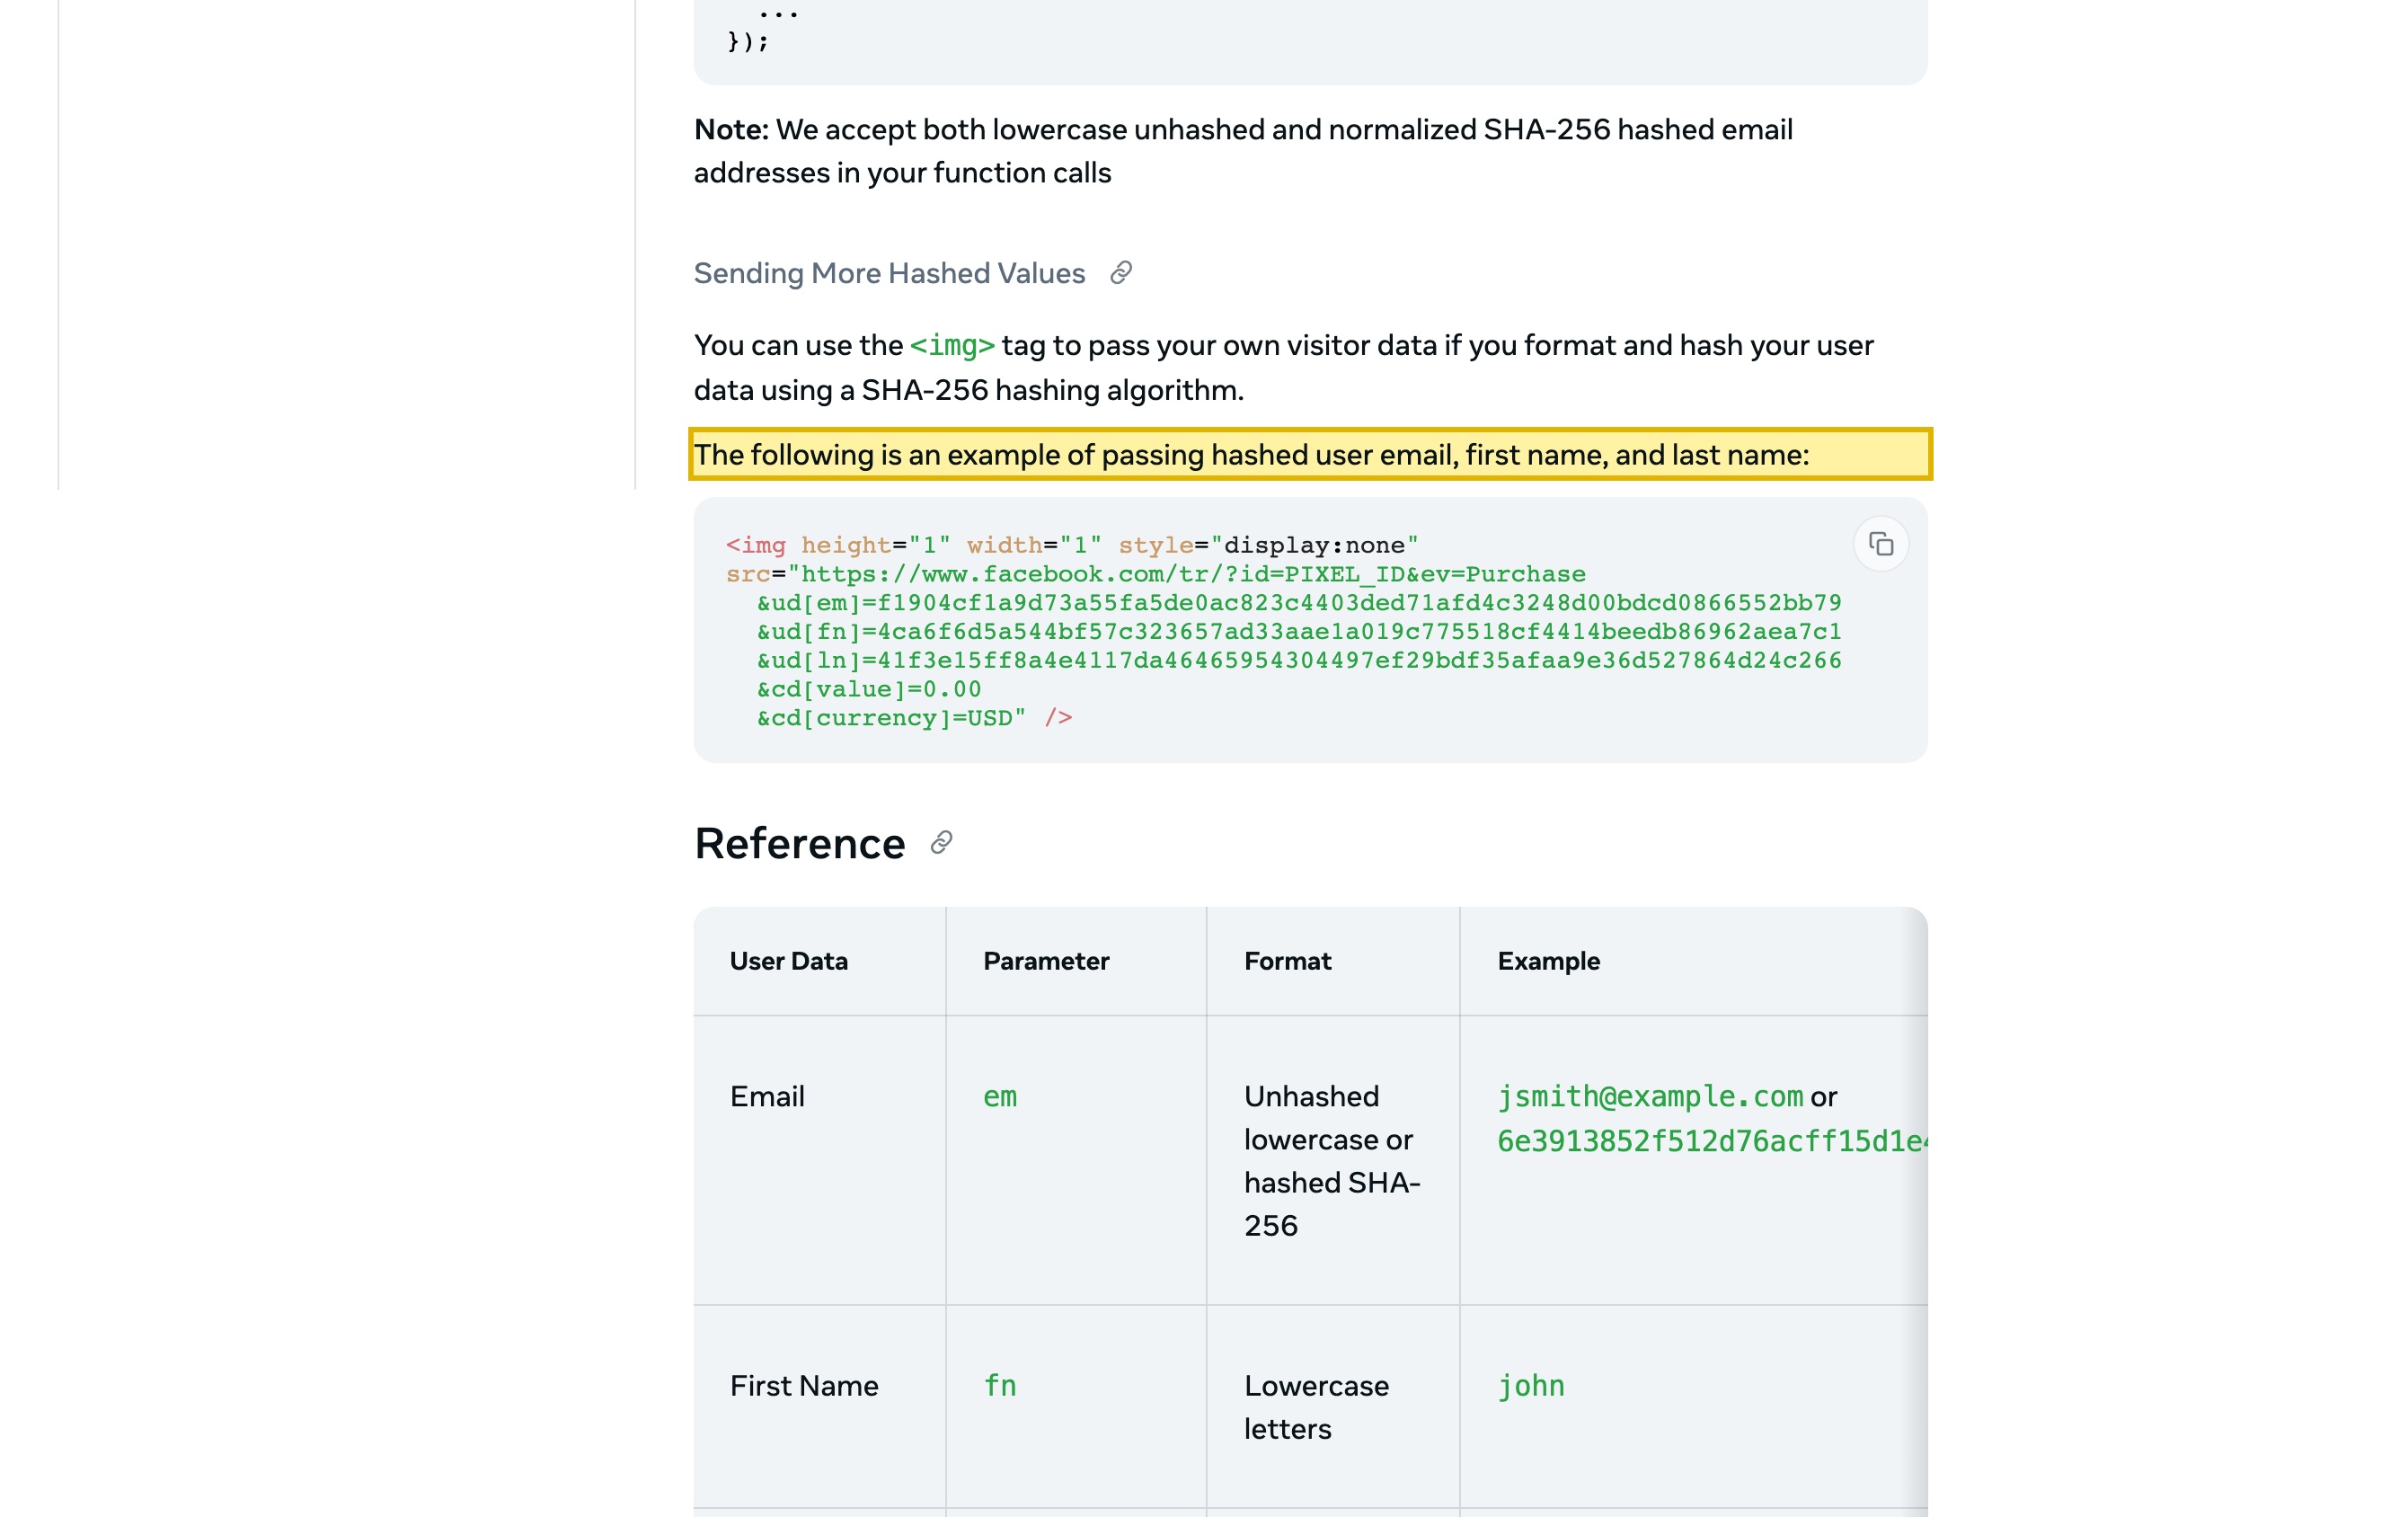
| Advanced Matching sends hashed customer PII to Meta. Meta's Advanced Matching documentation shows the pixel passing customer identifiers — “The following is an example of passing hashed user email, first name, and last name:” — and notes “Values will be hashed automatically by the pixel using SHA-256.” Hashed email, phone and name still identify a person and still leave China for Meta's offshore servers. | Meta for Developers, “Advanced Matching” documentation (developers.facebook.com), retrieved 2026-10-10 |
| Sending the data offshore is a PIPL cross-border transfer. Shipping a Chinese visitor's cookie IDs, IP, event log and hashed identifiers to Meta's offshore servers triggers PIPL Articles 38–40: notice, a separate consent for the overseas transfer, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. | Personal Information Protection Law of the PRC, Articles 38–40 (cac.gov.cn), retrieved 2026-10-10 |
| A tracking pixel is an Article 24 profiling mechanism. Conversion tracking and retargeting build a profile to decide which ad reaches whom — automated decision-making used for commercial marketing. PIPL Article 24 requires transparency and fair outcomes, an option not based on the individual's personal characteristics, and a convenient way to refuse. Non-essential tracking and the transfer also need informed, separate consent (Articles 13 and 23). | Personal Information Protection Law of the PRC, Articles 24, 13 and 23 (cac.gov.cn), retrieved 2026-10-10 |
Sources verified by the 21YunBox compliance team on 2026-10-10.
The question most teams ask about the Meta Pixel in China is whether it still fires — whether the tag loads and conversions come back. For a mainland audience that is the wrong test twice over. Meta’s advertising platform does not operate normally in mainland China, so the pixel earns you no usable measurement there: it is a third-party call you neither host nor control, failing or stalling on the page. The quieter problem is what happens wherever it does resolve. The Meta Pixel (renamed from Facebook Pixel in 2022) exists to watch a visitor — page views, button clicks, items purchased — and report them to Meta, building a profile for ad targeting. On a visitor in China that is three things at once under Chinese law: a cross-border transfer of personal information, an automated-decision and profiling mechanism, and tracking that needs its own separate consent.
Meta Pixel in China at a glance
| What decides it | In Meta Pixel's own terms — and China's law |
|---|---|
| What it collects | The Meta Pixel (formerly Facebook Pixel) is a JavaScript tag you embed to track visitors — page views, button clicks, add-to-cart and purchases — alongside the Pixel ID, the Facebook cookie, the visitor's IP and HTTP-header data. With Advanced Matching it also sends hashed customer identifiers: email, phone, first and last name. Under PIPL those identifiers are personal information. |
| Where the data goes | Meta receives and processes that behavioral data on its own offshore infrastructure; there is no mainland-China region for the Meta Pixel. Collecting it from a visitor in China is a cross-border transfer (数据出境) under PIPL — notice, a separate consent, and a transfer mechanism (Articles 38–40). |
| Profiling for ads | Conversion tracking and retargeting build a behavioral profile to decide which ad reaches whom — automated decision-making used for commercial marketing. PIPL Article 24 requires transparency and fair outcomes, an option not based on personal characteristics, and an easy way to refuse. |
| Consent | Setting tracking cookies and identifiers and shipping the data abroad is non-essential processing: under PIPL Articles 13 and 23 it needs informed consent before the tag fires, and the overseas transfer needs its own separate consent — not a single buried "by using this site" line. |
| Is the tag reachable? | That is the delivery half, not the decision. Meta's platform does not operate normally in the mainland, so the pixel is dead weight that also drags page performance; the fix is to gate or suppress it for mainland visitors and route measurement to a licensed in-country alternative — while the China-facing site itself carries an ICP filing and needs in-country delivery. |
What the pixel actually sends — and where
Strip away the marketing and the Meta Pixel is a reporting tag. Meta’s own developer documentation lists what it can collect: HTTP-header data that “may include data like IP addresses, information about the web browser,” page location and referrer; “Pixel ID and the Facebook Cookie”; and button-click data — “any buttons clicked by site visitors, the labels of those buttons and any pages visited as a result of the button clicks.” On top of that sits Advanced Matching, which passes hashed customer identifiers — email, phone number, first and last name — so Meta can tie the visit to a known account; the pixel hashes them with SHA-256 and sends them along. A server-side companion, the Conversions API, reports the same kind of event data to Meta from your own servers rather than the browser. Every path ends in the same place: Meta’s infrastructure, offshore.
Then the China-specific twist. Because Meta’s advertising platform does not operate normally in mainland China, for a mainland visitor the tag mostly cannot do its job — it is a request to an endpoint you do not run, and a stalled third-party script is a performance drag on the page besides. That tempts teams to treat the pixel as harmless there. It is not. Wherever the request does resolve — a visitor on a corporate network, an unusual route, a cached library — it still collects that person’s behavioral data and starts it toward Meta. Dead weight for measurement; live liability for compliance. And note what the vendor’s own controls do not solve: Meta’s “Limited Data Use” flag is a switch for United States state privacy laws, not a China data-residency option, and Meta offers no mainland region for the pixel at all.
It’s a cross-border transfer and a profiling mechanism — under PIPL
Point the pixel at a visitor in China and three PIPL duties attach at once. First, the data leaves the country. Those cookie IDs, the IP address, the event log and any hashed identifiers are personal information, and sending them to Meta’s offshore servers is a cross-border transfer (数据出境): the handler — you, the site operator, not Meta — owes the visitor notice, a separate consent for the overseas transfer, and one lawful transfer mechanism, a CAC security assessment, the CAC standard contract, or certification (PIPL Articles 38–40). Above the regulated volume thresholds, or where the data counts as “important data,” China’s data-export security assessment (数据出境安全评估) can apply before anything is allowed to leave.
Second, the pixel is a profiling mechanism. Conversion tracking and retargeting exist to build a behavioral profile and decide which ad chases which user — the textbook case PIPL Article 24 governs: automated decision-making used for information push and commercial marketing. The article demands transparency and fair outcomes and, for marketing aimed at individuals, a genuine option not based on their personal characteristics or an easy way to refuse. A China-facing campaign that only knows how to target by profile does not meet that on its own; the opt-out and the non-profiled path have to be built into the flow.
Third, none of this rides on a blanket agreement. Setting non-essential tracking cookies and identifiers needs a lawful basis, which for behavioral advertising is informed consent captured before the tag fires (PIPL Articles 13 and 23); the overseas transfer then needs its own separate consent. A single “by using this site you agree” line does not carry any of them. And where you are a critical information infrastructure operator or a high-volume handler, a storage-localization duty is added on top — personal information generated in China must be kept in China under Cybersecurity Law Article 39 (formerly Article 37 — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, with the substance unchanged) and PIPL Article 40 — a duty an offshore ad pixel cannot satisfy.
Making the offshore pixel reachable is the wrong fix — what actually works
The instinct, once someone notices the pixel misfires in the mainland, is to find a way to make it load. That is precisely the wrong move. Making an offshore ad endpoint reachable creates no lawful basis, no transfer mechanism, and no Article 24 opt-out; it simply guarantees the unconsented export you were previously only risking. The compliant direction is the opposite — reduce what leaves, not increase it.
Three things actually work. Gate or suppress the Meta Pixel (and its Conversions API) for mainland visitors, so it fires only for consented, out-of-scope audiences and stops exporting behavioral data from people in China by default. Honor consent and the Article 24 right to refuse in the flow itself, before any tag runs. And where you still need measurement or advertising to reach Chinese users, route it through a lawful, licensed in-country advertising-and-analytics alternative whose data is collected and held on mainland infrastructure — a China-resident path, not the offshore pixel dressed up to reach further.
None of this is a ruling that the Meta Pixel is banned in China. It is a risk map: which duties actually bite — and how hard — depends on what your tag collects, your data volumes, your role under Chinese law, and who your visitors are. Settle the specifics with counsel before a China-facing campaign relies on any of it.
The lawful path — map, localize, deliver
There is a compliant way to run marketing for a China audience, and it begins by separating the legal question from the technical one.
First, map. Our China compliance team inventories which advertising and tracking pixels fire on your mainland-facing pages — the Meta Pixel and anything beside it — what behavioral personal information each sends offshore, and where you lack a lawful basis: the consent your flow must capture before a tag runs, the separate consent the overseas transfer needs, the Article 24 options you owe on profiled marketing, and any data-export assessment or in-country storage duty. We build the technical picture; your counsel draws the legal conclusions.
Then localize. We gate, suppress or defer the offshore pixels for mainland visitors and, where you still need to measure or advertise to Chinese users, stand up a consented, PIPL-aligned path on a licensed in-country platform — the China-side data collected and held on mainland infrastructure — while you keep the Meta Pixel for the markets where it already serves you. Localizing here means ending the unconsented offshore export and replacing it with a lawful in-country path; it is never a tunnel that makes the offshore pixel fire anyway.
Then deliver. The China-facing site that carried the tag is itself a public internet information service in the mainland, so it needs an ICP filing and compliant, in-country delivery — the 21YunBox Optimizer, set in front of the stack you already run, with no rebuild and no re-platform. The result is a site that runs legally and compliantly for your users in China. 21YunBox never uses or suggests circumvention of any kind. We keep what must stay in-country and deliver the rest in the open — a compliant overlay and partner, not a competitor to any ad platform.
Related reading:
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law (data localization, Article 39)
- China’s data-export security assessment
- How to get an ICP filing for China