Does Bun Work in China? Data Residency, ICP & Cross-Border Rules
Bun is an open-source JavaScript/TypeScript runtime you run on your own servers, so it is residency-neutral and runs fine in China. The real China question is not Bun — it is where you deploy it (ICP, MLPS) and whether the data it handles stays in-country or crosses the border under PIPL.
Does Bun work in China?
Yes — Bun runs fine in China; it is open-source code you run on your own servers, with no region to select, so the runtime is never the blocker. The real China questions are about deployment and data, not reachability. If your Bun app serves mainland users, its host owes an ICP filing (备案) and the operator owes MLPS (等级保护) duties; the personal information it collects from China users is governed by the Personal Information Protection Law, and an offshore database or backend makes that a cross-border transfer needing a lawful basis. Bun's bundled package manager also resolves dependencies from offshore registries at install. The lawful path is to run Bun in-country on ICP-filed, MLPS-appropriate infrastructure with China user data kept resident.
What Bun's own documentation says about China
| Fact | Primary source |
|---|---|
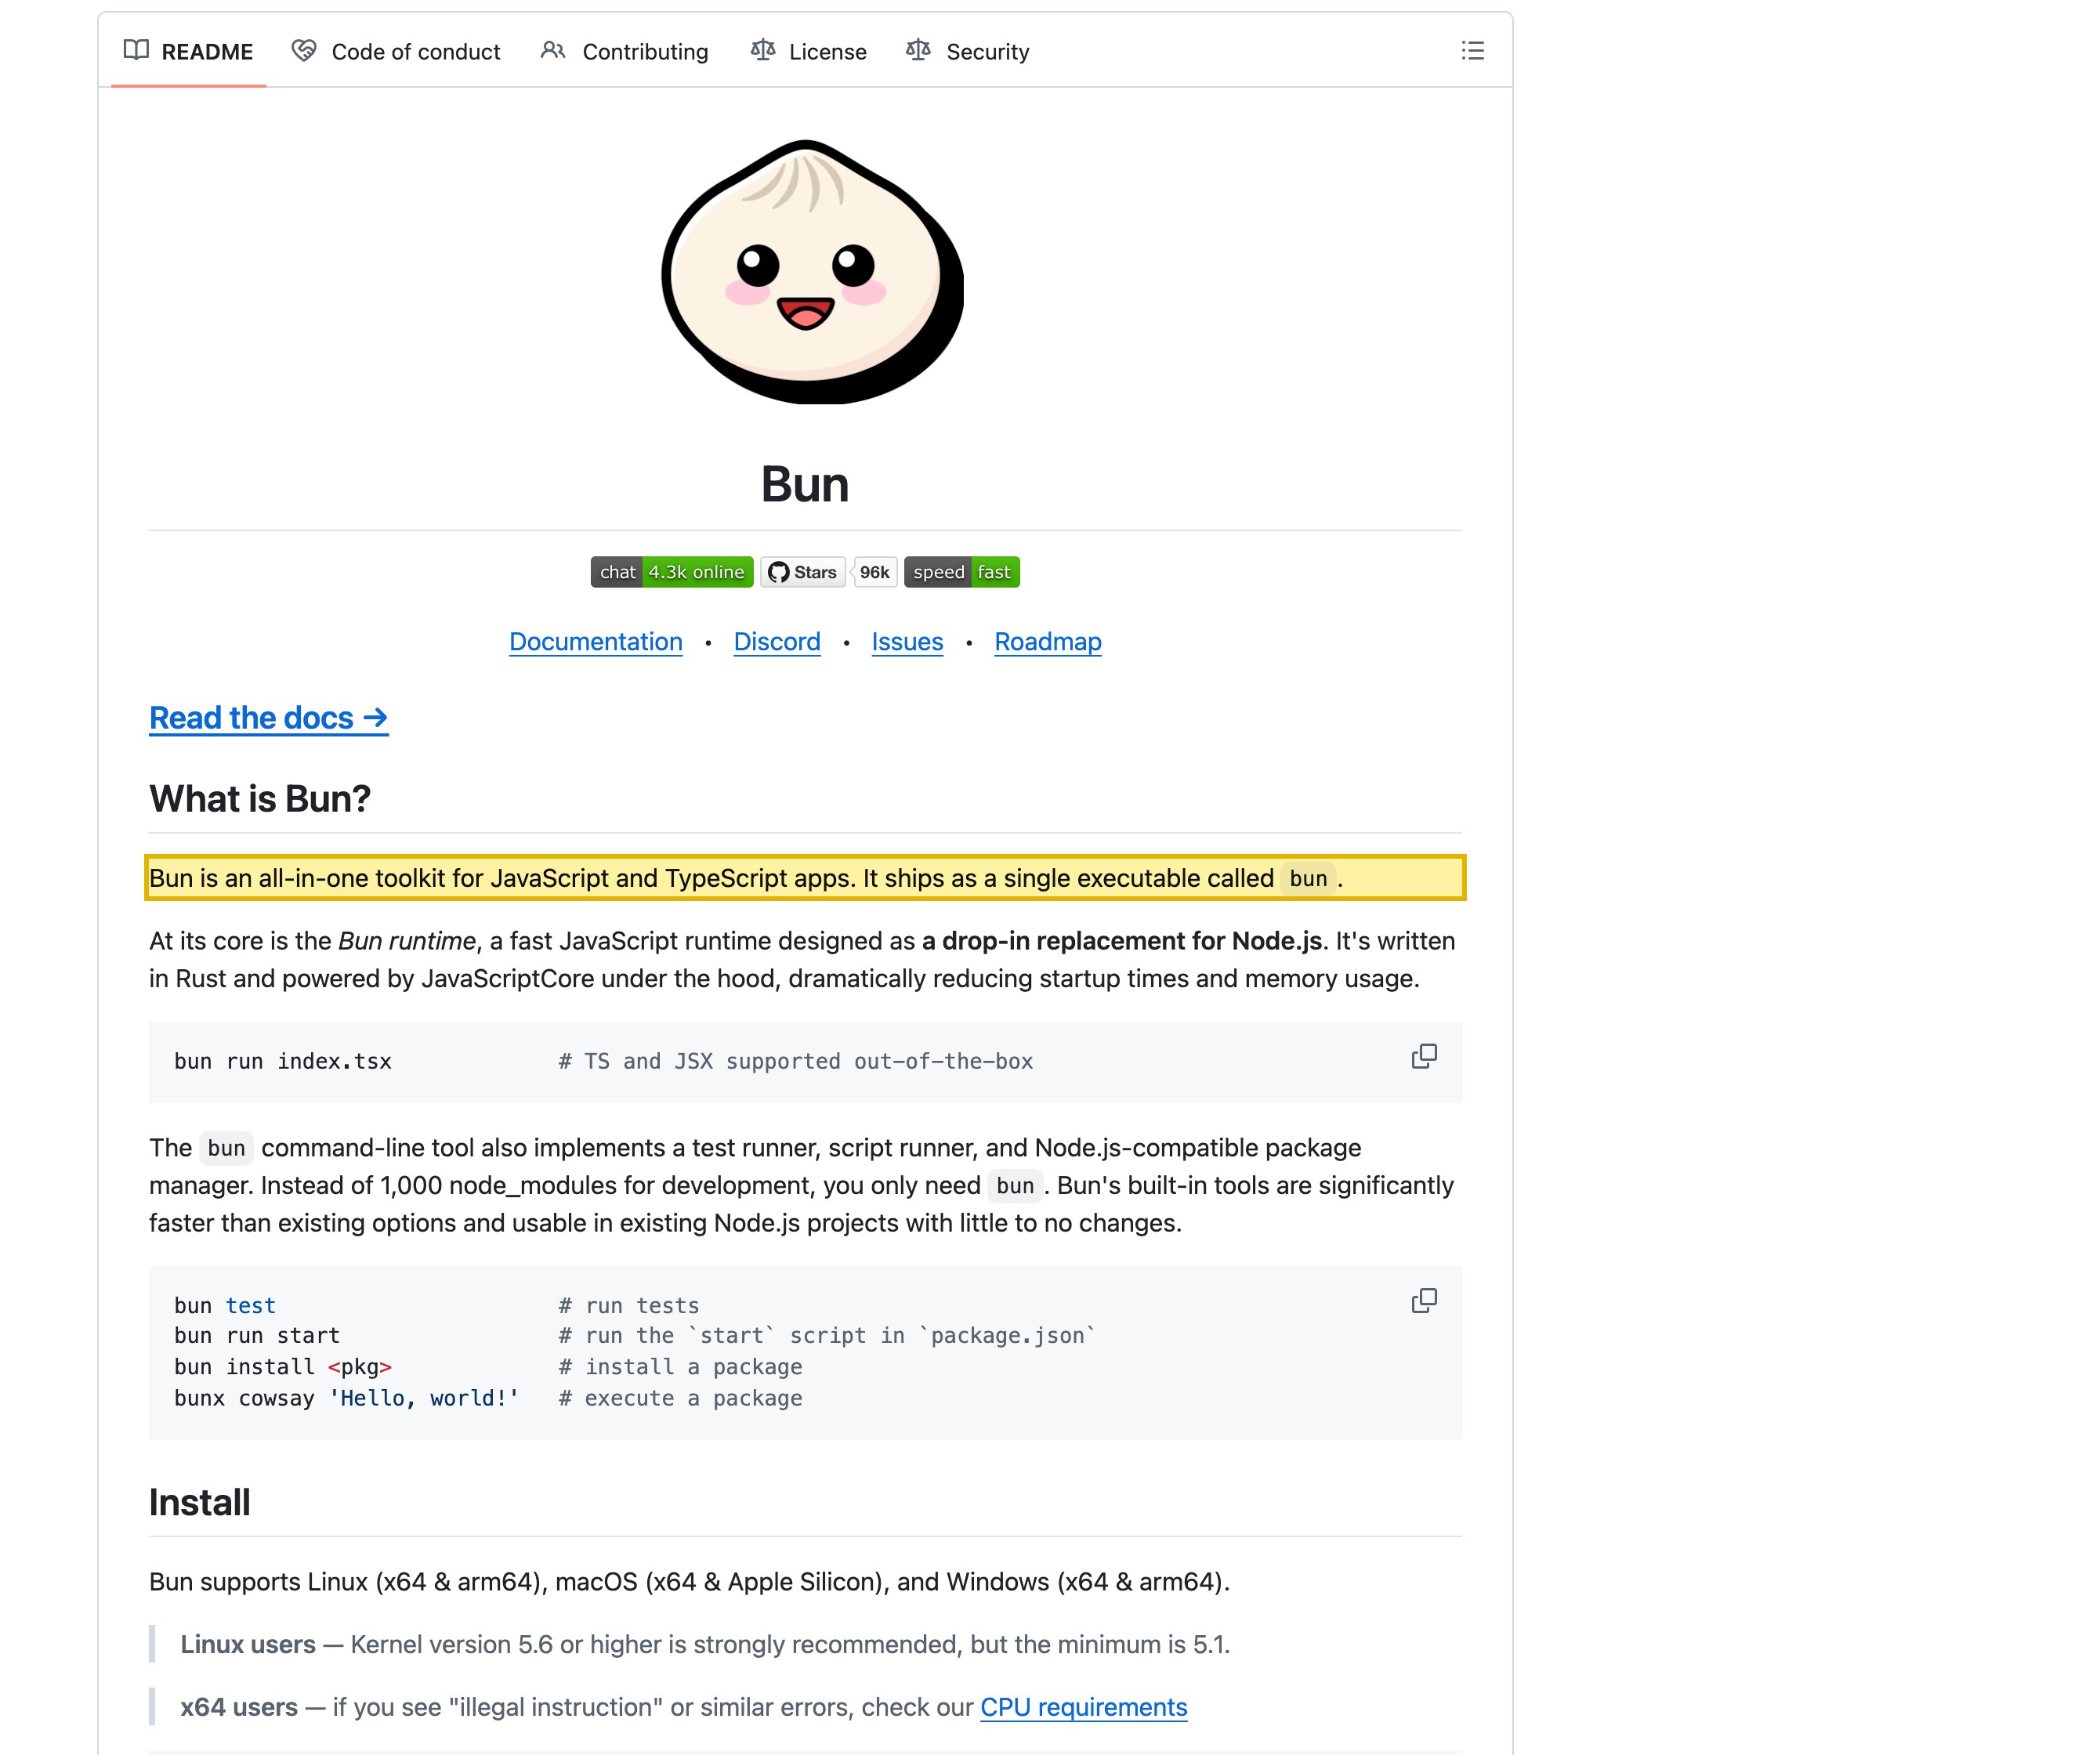
| Bun's own README describes it as "an all-in-one toolkit for JavaScript and TypeScript apps" that ships as a single executable and includes a "Node.js-compatible package manager" — open-source software you run on your own servers, with no hosted service and no in-country region to select. | Bun GitHub repository README (oven-sh/bun), retrieved 2026-10-14 |
| Bun's official site describes it as "a fast JavaScript runtime & toolkit" — a runtime plus bundler, test runner, and package manager that you install and run yourself, not a hosted platform with a managed region, so where it runs is a deployment decision. | bun.com homepage, retrieved 2026-10-14 |
| Under the Personal Information Protection Law, sending the personal information of China users to an offshore server or database is a cross-border transfer (Articles 38–40): it requires notice, a separate consent, and a transfer mechanism — a CAC security assessment, the CAC standard contract, or certification — with the duty falling on you as the handler. | Personal Information Protection Law of the PRC (21YunBox English reference), retrieved 2026-10-14 |
| For operators of critical information infrastructure (and large-volume handlers), China's Cybersecurity Law requires personal information and important data collected or generated in the mainland to be stored in-country, with a security assessment before any export — Article 39 (formerly Article 37; renumbered by the 2025 amendment in force January 1, 2026, substance unchanged). | Cybersecurity Law of the PRC (21YunBox English reference), retrieved 2026-10-14 |
Sources verified by the 21YunBox compliance team on 2026-10-14.
For a mainland-China audience, the first thing to settle about Bun is that the question is not whether it installs or how fast it runs, and not really about Bun at all. Bun is an open-source toolkit — a JavaScript and TypeScript runtime, bundler, test runner, and a Node.js-compatible package manager, all in one executable — that you run on your own servers. There is no “Bun data centre” and no “Bun region” to select: the same binary runs identically in a Beijing data centre or a Frankfurt one, stores nothing offshore on its own, and phones nothing home for your data. So “does Bun work in China” resolves into three different questions — where you deploy it, what data it processes, and what it reaches out to at build time — and not one of them is answered by checking that bun install succeeds.
Bun in China at a glance
| What decides it | In Bun's own terms — and China's law |
|---|---|
| Where it actually runs | Bun is open-source code you run on your own servers; there is no Bun "service" with a region to select, and the runtime runs fine on mainland infrastructure. What is not neutral is the host you deploy to: an app serving mainland users owes an ICP filing (备案) on a mainland hosting resource, and the system's operator owes MLPS (等级保护) obligations. |
| What data your app processes | A Bun backend holds session and user state server-side and reads and writes a database. The personal information it collects from China users — names, contact details, identifiers, account and order records — is what the Personal Information Protection Law governs, independent of the runtime you chose. |
| Data crossing the border | Wire the app to an offshore database, or forward China users' personal information abroad, and that is a cross-border transfer under PIPL Articles 38–40: notice, a separate consent, and one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification), with the duty on you as the handler. |
| What it pulls at build time | Bun bundles a Node.js-compatible package manager; bun install resolves your dependencies from package registries that sit offshore, and any private or scoped packages carry your proprietary source. That is a supply-chain and residency concern that rides along with the runtime — a probe that confirms the install completes cannot see where those dependencies came to rest. |
| Reachability is not the axis | That bun install succeeds and the app renders says nothing about whether the deployment and its data were allowed to sit where they sit. The decision turns on residency and the ICP/MLPS duties the host carries — not speed. This page publishes no first-party latency figure; speed is the wrong axis. |
The runtime runs where you run it — the deployment host is the exposure
Start with where Bun runs, because the rest rests on it. Bun’s README opens by calling it “an all-in-one toolkit for JavaScript and TypeScript apps” that ships as a single executable, and positions its runtime as “a drop-in replacement for Node.js.” That is server software you deploy on infrastructure of your choosing — which can just as easily be a mainland server as an offshore one. In that sense Bun is usable in China in a way a blocked consumer service is not, and it can run entirely in-country.
What that also means is that Bun never sets your residency posture — your deployment does. If your Bun app serves mainland users, the hosting resource behind it owes an ICP filing (备案), and as the operator of a system running in the mainland you take on MLPS (等级保护) obligations. An offshore VM that mainland users reach is the real exposure, and it is a deployment choice, not a property of Bun. So the compliance question is not answered by looking at the runtime; it is answered by looking at where you host the app and where its data lives.
The data your app processes is what PIPL governs
A Bun backend is not neutral plumbing. It terminates HTTP, holds session and user state server-side, and reads and writes a database — and the personal information your app collects from China users is governed by China’s Personal Information Protection Law, whichever runtime executes the code. The moment that data is written to an offshore database, or your backend forwards it to an offshore service, it has left the country: under PIPL that is a cross-border transfer (Articles 38–40), and the law puts the duty on you as the handler — notice, a separate consent, and one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification), with heightened duties under Article 28 where the data is sensitive, such as government IDs, financial, or health information.
And if your organization operates critical information infrastructure, or you handle personal information at volume, the Cybersecurity Law adds a data-localization duty — Article 39 (formerly Article 37; renumbered by the 2025 amendment in force January 1, 2026, substance unchanged) requires personal information and important data collected and generated in-country by such operators to be stored in-country, with a security assessment before any export. None of that is decided by Bun; it is decided by where your database sits and what crosses to reach it.
The package manager reaches offshore at install — the supply-chain prong
Bun is more than a runtime, and the extra piece has its own residency edge. Its README describes a “Node.js-compatible package manager” built into the same executable, so bun install resolves your dependencies from package registries that sit offshore, at build and install time. That is a supply-chain and residency concern that rides along with the runtime: your build reaches across the border on every resolve, and any private or scoped packages you publish carry your proprietary source and, too often, embedded credentials. Crash and analytics telemetry, and third-party APIs the app calls at run time, can route offshore the same way. A reachability check that confirms bun install completed tells you nothing about where those dependencies — and the secrets bundled with them — came to rest.
Why a reachability check misses this
A reachability or latency test installs the toolkit, hits an endpoint, and reports that it answered and how fast. For a runtime that is the wrong question three times over. That bun install succeeds proves a registry was reachable, not where your dependencies and their secrets ended up. That the app renders proves the server answered, not that the server was allowed to sit where it sits or that it carries an ICP filing. And a green light says nothing about whether the personal information flowing through your database crossed the border lawfully. Those are deployment and legal facts, invisible to a probe — the half a pure speed-or-reachability view cannot supply, and the half we lead with.
The lawful path — map, localize, deliver
For an open-source runtime, 21YunBox’s role is focused, and we will say so plainly: there is no “domestic Bun” to sell you — the runtime is already yours to run, including in-country. Our value is in three moves.
First, we map the exposure: where your Bun app actually runs, what personal information it collects from China users, where its database and caches live, which flows cross the border, and what your build pulls from offshore registries — and how all of that lands against PIPL’s cross-border rules, Article 28, and the Cybersecurity Law, so you and your counsel can set the guardrails. Second, we help you localize what cannot lawfully sit offshore: run your Bun app in-country on ICP-filed, MLPS-appropriate infrastructure, keep China user data resident in a mainland database, and resolve the dependencies your build needs from in-country sources. Third, we deliver your China-facing surface — the app or API edge your mainland users hit — over ICP-filed, in-country infrastructure (the 21YunBox Optimizer), in front of the Bun app you already run, with no rebuild and no second codebase.
21YunBox is a compliant overlay, not a migration, and a partner to the tools you use, not a competitor to them. 21YunBox never uses or suggests circumvention of any kind. The result is a setup that runs legally and compliantly for your users in China.
Related reading:
- Cross-border data transfers under PIPL
- China’s Personal Information Protection Law
- How to get an ICP filing for China
- China’s Cybersecurity Law (data localization, Article 39)