Does Zuora Work in China? Data Residency, ICP & Cross-Border Rules
Zuora is offshore cloud SaaS: your China customers' identities, subscription records, invoices and payment-method data live in Zuora data centers in North America, Germany or Japan — none in mainland China. A compliance-first look at the PIPL, payment-licensing and ICP doors a speed test never sees.
Does Zuora work in China?
Whether you can run Zuora for China is a data-residency and payment-licensing question, not a speed one. Zuora is reachable from the mainland; the exposure is legal, not performance.
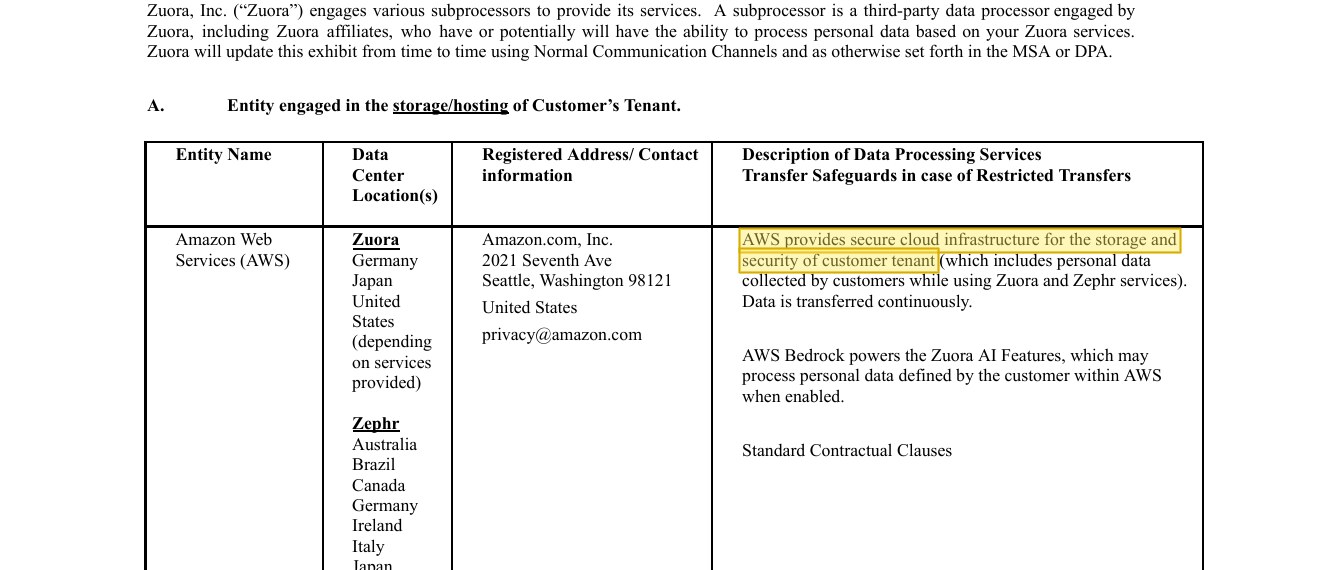
By Zuora's own sub-processor exhibit, customer tenant data is hosted on AWS in Germany, Japan and the United States — none in mainland China — so your China customers' identities, subscription and contract records, invoices and payment-method references sit abroad: a cross-border transfer of personal information that PIPL governs. The distinctive second door is payment: a foreign subscription platform is not a licensed China payment institution, so the actual money movement from China customers has to run over a licensed domestic payment path with Zuora orchestrating the billing on top of it, and any China-facing billing or self-service portal needs an ICP filing.
This is a risk picture, not a verdict — your duties turn on your volumes, your role and how you collect payment. Our China team can map your Zuora exposure with you →
What Zuora's own documentation says about China
| Fact | Primary source |
|---|---|
| In Zuora's own documentation: its services run from four data centers — “US Cloud Data Center 1” and “US Cloud Data Center 2” (both “located in North America”), the “EU Cloud Data Center” (Germany), and the “APAC Cloud Data Center” whose data is hosted “in the latest data center located in Japan.” None is in mainland China, so a China customer's billing data is assigned to an offshore region. | Zuora Product Documentation — Zuora Data Centers, retrieved 2026-10-12 |
| Zuora's own sub-processor exhibit names Amazon Web Services as the host of “customer tenant (which includes personal data collected by customers while using Zuora and Zephr services),” and lists the hosting locations as Germany, Japan and the United States — with no mainland-China location. Your China customers' tenant data, including payment-related personal information, therefore rests offshore. | Zuora — List of Data Center Location(s) and Subprocessors (sub-processor exhibit), retrieved 2026-10-12 |
| China's Regulations on the Supervision and Administration of Non-Bank Payment Institutions (State Council Order No. 768, in force May 1, 2024) require a payment business license to provide payment services in China; Article 2 requires an offshore institution intending to provide cross-border payment services to users in China to establish a non-bank payment institution within China, and Article 19 requires domestic transaction processing, fund settlement and data storage inside China. A foreign subscription platform is not that licensed institution, so the money movement must run over a licensed domestic path. | State Council Order No. 768 — Regulations on the Supervision and Administration of Non-Bank Payment Institutions, Articles 2 and 19 |
| Holding China customers' identities and payment-method personal information offshore is a cross-border transfer under PIPL Articles 38–40, on top of the Article 13/23 notice-and-separate-consent duty, with payment and identity detail capable of being sensitive personal information (Articles 28–29). For a critical information infrastructure operator or high-volume handler, the Cybersecurity Law's Article 39 (formerly Article 37) requires China-collected personal information to be stored in the mainland — which an offshore tenant cannot satisfy. | PIPL Articles 13, 23, 28–29, 38–40; Cybersecurity Law Article 39 (formerly Article 37) |
Sources verified by the 21YunBox compliance team on 2026-10-12.
For a company running Zuora to bill a mainland-China operation, the deciding question is not how quickly the billing UI or a customer’s self-service portal paints from Shanghai. It is where your data is allowed to live — and who is licensed to move the money — because Zuora is the system of record for your China subscription revenue. It holds the identity of every China customer you bill, their subscription and contract records, their invoices and usage, the payment-method references kept on file, and the recurring revenue those relationships represent. Zuora is offshore cloud SaaS, hosted in data centers in North America, Germany and Japan, with no region inside mainland China — so all of that is held and processed abroad. And because this is billing, a second, distinctive door opens: a foreign subscription platform is not a licensed China payment institution, so the actual movement of money from your China customers has to run over a licensed domestic payment path. That makes this a compliance-risk question first, not a performance one.
Zuora in China at a glance
| What decides it | In Zuora's own terms — and China's law |
|---|---|
| What it holds | Your China subscription revenue, end to end: the identities and billing contacts of your China customers; their subscription and contract records; invoices, usage and the payment-method references (tokens and gateway references) kept on file; and the recurring revenue those relationships represent. |
| Where it runs | Zuora is offshore cloud SaaS. By its own documentation its data centers are US Cloud Data Center 1 and 2 (“located in North America”), the EU Cloud Data Center (Germany) and the APAC Cloud Data Center (Japan); by its own sub-processor exhibit, customer tenant data is hosted on AWS in Germany, Japan and the United States. None is inside mainland China, and there is no China region to pick. |
| Customer & payment PII | Your China customers' identities and payment-method detail rest in whichever offshore region your tenant is assigned — a cross-border transfer under PIPL Articles 38–40, layered on the Article 13/23 notice-and-consent, with payment and identity detail capable of being sensitive personal information (Articles 28–29). For a critical information infrastructure operator or a high-volume handler, Cybersecurity Law Article 39 (formerly Article 37) requires China-collected personal information to be stored in the mainland. |
| The money movement — the distinctive second half | This is the half a speed test never sees. Collecting recurring payment from China customers is a licensed activity: under the Non-Bank Payment Institutions regime (State Council Order No. 768), Article 2 requires an offshore provider of cross-border payment services to China users to establish a non-bank payment institution in China, and Article 19 requires domestic processing, settlement and data storage. Zuora is not that licensed institution — it rates, invoices and orchestrates collection, but the actual money movement must run over a licensed domestic path, with Zuora on top. Frame it as a risk to confirm with counsel. |
| A China-facing portal | A public billing, checkout or customer self-service portal served to mainland users is an internet information service, so it carries an ICP filing (备案) duty bound to a mainland hosting resource. A Zuora-hosted portal runs on offshore infrastructure, so it offers no ICP-filing path of its own. |
| Reachability is not the axis | Whether the billing console loads quickly from the mainland is operational, not the compliance question. What decides it is where the customer and payment data live and who is licensed to move the money. 21YunBox helps you keep the regulated data in-country, route the money over a licensed domestic path, ICP-file any public portal, and deliver it compliantly — the 21YunBox Optimizer — in front of the Zuora you already run. |
What it actually holds — your China subscription revenue, and the money path
Zuora is not a static asset like a font or a script; it is the commercial core of your China subscription business, and it concentrates exactly the kinds of data and activity China’s law cares about. On the data side it holds personal and commercial information: the identities and billing contacts of your China customers, their subscription and contract records, invoices, usage, and the payment-method references (tokens and gateway references) kept on file, together with the recurring revenue those relationships represent. On the activity side — the half a reachability check never sees — it sits astride money movement: Zuora rates usage, raises invoices and orchestrates collection from your China customers. Because Zuora is offshore cloud SaaS hosted in data centers in North America, Germany and Japan, the customer and payment data rests abroad by default; and because Zuora is not a licensed Chinese payment institution, the money it orchestrates has to settle over a licensed domestic channel. Both halves are compliance questions, and neither is answered by the app loading quickly.
The doors: residency, payment licensing, and ICP
The first door is personal-information residency. The customer identities and payment-method detail your Zuora tenant collects from people and businesses in China are personal information under China’s Personal Information Protection Law, and holding them in an offshore data center is a cross-border transfer (数据出境). The duty lands on you, the handler, not on Zuora: Articles 13 and 23 require notice and a basis to collect the data, and Articles 38–40 require a transfer mechanism to send it abroad — a CAC security assessment, the CAC standard contract, or certification. Payment-method and identity detail can rise to sensitive personal information, where PIPL Articles 28–29 add a specific-purpose, necessity and separate-consent test. And for a critical information infrastructure operator or a high-volume handler, the Cybersecurity Law’s Article 39 (formerly Article 37 — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, its substance unchanged) requires personal information generated in China to be stored in the mainland, which an offshore tenant cannot satisfy.
The second door is the one that makes a billing platform different from an ordinary SaaS, and it is where a reachability check is most blind. Collecting recurring payment from customers in China is a licensed activity. Under China’s Regulations on the Supervision and Administration of Non-Bank Payment Institutions (State Council Order No. 768, in force May 1, 2024), providing payment services in China requires a payment business license (支付业务许可); Article 2 requires an offshore institution that intends to provide cross-border payment services to users in China to establish a non-bank payment institution within China; and Article 19 requires domestic transaction processing, fund settlement and data storage to happen inside China. A foreign subscription platform is not that licensed institution — Zuora rates, invoices and orchestrates collection, but the actual money movement for your China customers must run over a licensed domestic payment path, with Zuora sitting on top of it. The compliance question here is twofold: where the customer and payment data lives, and who is licensed to move the money. Treat the specifics as a question for qualified counsel, not a settled classification — but note that a speed test answers neither half.
The third door is the ICP filing. If you publish a China-facing billing, checkout or customer self-service portal to mainland users, you are running a public internet information service, and that turns on an ICP filing (ICP 备案) duty bound to a hosting resource physically inside the mainland. A Zuora-hosted portal runs on offshore infrastructure, so it offers no ICP-filing path of its own — tuning the stack does not create the mainland footing a filing needs.
A reachability check never sees this
Zuora is not the kind of service that simply refuses to load in China — the exposure is quieter and more durable than a slow paint. Even if the billing console and the customer portal opened instantly, using them would still place your China customers’ identities and payment-related personal information outside the country, and would still leave the money movement to a channel that, offshore, is not licensed to perform it in China. A reachability test answers “did the page come back?”; it is blind to where the subscription records and payment-method data come to rest, and to who is lawfully allowed to move the money. Where the data lives and who holds the license — not how fast the page arrives — is what China’s law responds to.
This is a risk map, not a verdict that Zuora is “blocked” or “illegal” in China. Which duties bite your case turns on your entity, what your tenant actually holds, your role under Chinese law, your data volumes, and how you collect payment from China customers — worth settling the specifics with counsel before your China revenue depends on it.
The lawful path — map, localize, deliver
There is a compliant way to run subscription billing for a China operation, and it sits in front of the Zuora your team already uses — no rebuild, no second system, no migration.
First, map: our China team inventories what your Zuora tenant holds — the customer identities, subscription and contract records, invoices, usage and payment-method references, and any China-facing portal — establishes where it is hosted (an offshore Zuora/AWS region), the ICP status of any public portal, and the consent, residency and payment-licensing basis each flow relies on. We build the technical picture; the legal conclusions are settled with counsel.
Then localize/govern: we help you keep the regulated data — customer and payment-related personal information — on a lawful in-country path, obtain the Article 13/23 notice-and-consent, and route the actual money movement through a licensed domestic payment path and settlement rather than an offshore channel. Localize means keeping the data and the money path in-country — never a route that quietly ships either across the border.
Then deliver: any public China-facing billing or self-service portal is an internet information service, so it carries an ICP filing duty bound to mainland hosting and needs compliant, in-country delivery. 21YunBox stands that up — the 21YunBox Optimizer — in front of what you already run, so it serves your users in China legally and compliantly. 21YunBox never uses or suggests circumvention of any kind — we keep in-country what the law says must stay, deliver the rest compliantly from inside the mainland, and never move personal information across the border by stealth. Making an offshore tenant merely reachable is not the answer; keeping the regulated data in-country, using a licensed domestic payment path, ICP-filing the portal and delivering it compliantly is. 21YunBox is a compliance overlay and partner to the billing platform you already run, not a competitor to it.
Related reading:
- How to get an ICP filing for China
- Cross-border data transfers under PIPL
- China’s Personal Information Protection Law (PIPL)
- China’s Cybersecurity Law
- Regulations on Non-Bank Payment Institutions (Order No. 768)


