Does Shippo Work in China? Data Residency, ICP & Cross-Border Rules
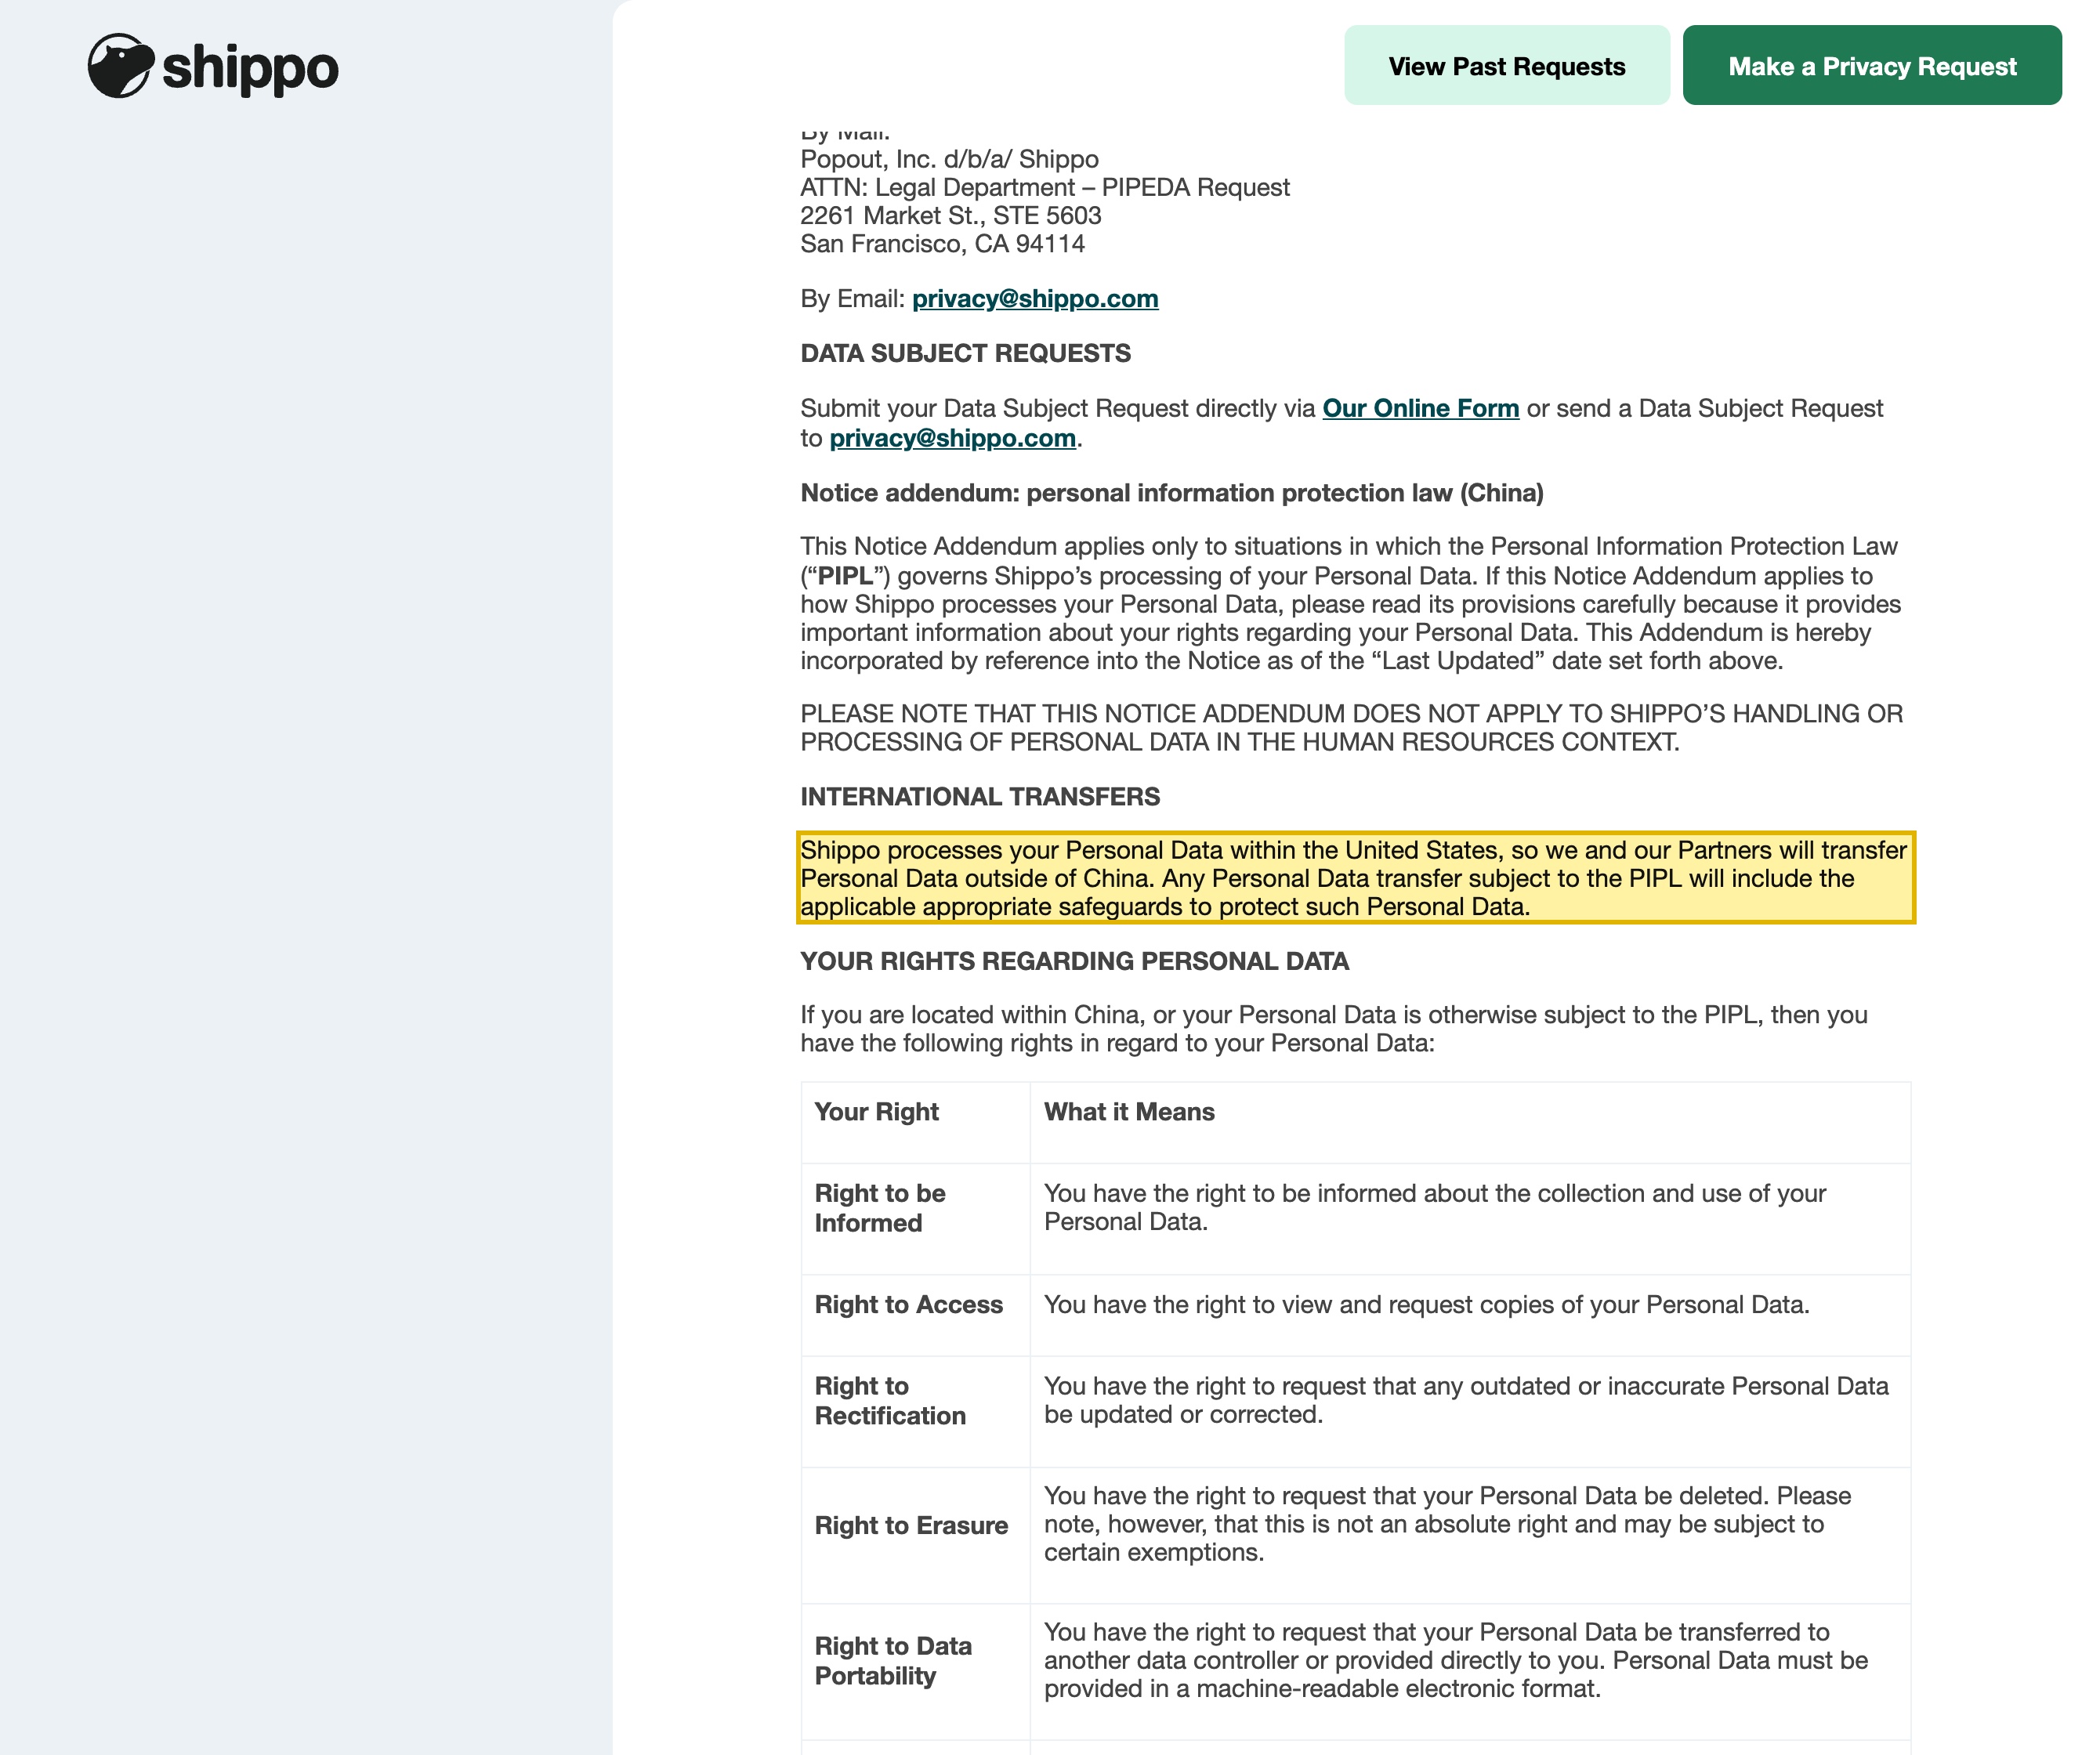
Shippo is offshore, US-hosted shipping software: by its own privacy notice it processes personal data within the United States and transfers it outside of China — no mainland-China region. Every China recipient's name, address and phone sits abroad, fanned out to offshore carriers. A compliance-first look at PIPL cross-border, residency and ICP.
Does Shippo work in China?
Whether you can use Shippo in China is a data-residency question, not a speed one. Shippo is multi-carrier shipping software that ingests every China parcel recipient's name, address and phone in bulk to buy labels and track shipments.
By Shippo's own privacy notice it “processes your Personal Data within the United States” and transfers it “outside of China” — there is no mainland-China region. The distinctive exposure is the fan-out: that bulk consumer personal information is disclosed to “carriers, merchant platforms integrated with Shippo, and service providers”, all offshore, which is a cross-border transfer PIPL governs and, at parcel volumes, puts the high-volume in-country-storage duty under Cybersecurity Law Article 39 (formerly Article 37) in play. Any China-facing tracking page you publish is an internet information service needing an ICP filing.
This is a risk picture, not a verdict — your obligations turn on your parcel volumes and your role. Our China team can map your Shippo data exposure with you →
What Shippo's own documentation says about China
| Fact | Primary source |
|---|---|
| In Shippo's own words, its China privacy addendum states: “Shippo processes your Personal Data within the United States, so we and our Partners will transfer Personal Data outside of China.” Its general international-users section adds that it may store or process data “in locations around the world (including the United States).” No mainland-China region is offered, so the recipient personal information your China shipments generate is held offshore. | Shippo (Popout, Inc.) — Privacy Notice, China addendum, effective Dec 17 2025, retrieved 2026-10-12 |
| Shippo's notice lists the data it collects to ship — name, email, phone, billing address and shipping address — for “facilitating shipping ... creating labels, tracking shipments, address validation,” and states it “may disclose data to carriers, merchant platforms integrated with Shippo, and service providers.” So each China recipient's contact and address data is both held in the US and fanned out to multiple offshore parties (the notice reproduces USPS and FedEx carrier privacy statements). | Shippo (Popout, Inc.) — Privacy Notice, data collected & sharing, retrieved 2026-10-12 |
| Because Shippo holds the recipient name, address and phone that your China shipments generate — personal information — and stores it in the US, that is a cross-border transfer governed by PIPL. The personal-information handler (you, the Shippo customer — not Shippo) must give notice and separate consent (Articles 13 and 23) and satisfy a transfer mechanism under Articles 38–40 — a CAC security assessment, the CAC standard contract, or certification. A delivery address plus phone is whereabouts-level data, raising the bar under Articles 28–29. | China's PIPL — Articles 13, 23, 28–29, 38–40 (21YunBox gov-doc), retrieved 2026-10-12 |
| Because a shipping platform handles high-volume consumer personal information — every parcel recipient — and replicates it to multiple offshore carriers, the in-country storage duty is in play: the Cybersecurity Law's Article 39 (formerly Article 37) (2025 amendment, in force Jan 1 2026; renumbered 37→39, substance unchanged) requires personal information generated in China by a critical information infrastructure operator or high-volume handler to be stored in the mainland — which a US-only platform cannot satisfy. | China's Cybersecurity Law — Article 39 (formerly Article 37) (21YunBox gov-doc), retrieved 2026-10-12 |
Sources verified by the 21YunBox compliance team on 2026-10-12.
For a company shipping into mainland China on Shippo, the deciding question is not how quickly a label prints or a tracking page paints from Shanghai. It is where your data is allowed to live — because Shippo is a multi-carrier shipping and label platform that ingests, at parcel scale, the one thing China’s law cares about most: the personal information of every consignee. To buy a label and track a parcel, Shippo takes each China recipient’s name, delivery address and phone number, then fans that data out to the carriers, marketplace integrations and service providers that actually move and track the shipment. By Shippo’s own privacy notice it processes that personal data within the United States and transfers it outside of China, and it offers no mainland-China region. That makes this a compliance-risk question first, not a performance one.
Shippo in China at a glance
| What decides it | In Shippo's own terms — and China's law |
|---|---|
| What it holds | Consignee personal information at scale: for every China parcel, the recipient's name, delivery address and phone number, plus email, billing and transaction detail and the linked carrier and marketplace account credentials — collected, in Shippo's words, for “facilitating shipping ... creating labels, tracking shipments, address validation.” |
| Where it runs | Shippo is an offshore cloud SaaS. Its privacy notice states it “processes your Personal Data within the United States” and may store or process it “in locations around the world (including the United States)”; its China addendum confirms it will “transfer Personal Data outside of China.” There is no mainland-China region or data-residency option. |
| Recipient PII residency | Every recipient's details your China shipments generate rest in the US — a cross-border transfer under PIPL Articles 38–40, on top of the Article 13/23 notice-and-consent. A home address plus phone is high-risk, whereabouts-level data, raising the bar under PIPL Articles 28–29. |
| The bulk, multi-party fan-out | This is the half a reachability check never sees. Shippo doesn't just hold the data — it “may disclose data to carriers, merchant platforms integrated with Shippo, and service providers” (its notice reproduces USPS and FedEx privacy statements). High-volume consumer PII, fanned out to many offshore parties, is exactly the case where the in-country storage duty — Cybersecurity Law Article 39 (formerly Article 37) — comes into play. |
| A consumer-facing tracking page | A branded tracking or self-service page served to recipients in mainland China is a public internet information service, so it carries an ICP filing (备案) duty bound to a mainland hosting resource. A Shippo-hosted page runs offshore, so it offers no ICP-filing path of its own. |
| Reachability is not the axis | Whether the label API or the tracking page answers quickly from the mainland is operational, not the compliance question. What decides it is where the recipient PII lives and who it is handed to. 21YunBox helps you keep the regulated data in-country, ICP-file any public tracking page, and deliver it compliantly — the 21YunBox Optimizer — in front of the Shippo you already run. |
What it actually holds — your China consignees, in bulk
Shippo is not a static asset like a font or a script; it is the data layer around every parcel you send into China, and it concentrates the personal information of people who are usually not your account-holders at all — your customers’ customers. To create a shipping label and track delivery, Shippo collects and stores each recipient’s name, delivery address and phone number, alongside email, billing and transaction information and the carrier and marketplace account credentials you connect. Its own notice is explicit that when it provides these services it acts as “a data processor of consumer personal data.” At any real shipping volume that is a steady, high-volume stream of consumer personal information — and because Shippo processes it within the United States, that stream crosses the border by default.
The doors: recipient PII residency, the bulk fan-out, and ICP
The first door is personal-information residency. The recipient names, addresses and phone numbers your China shipments generate are personal information under China’s Personal Information Protection Law, and holding them in a US region is a cross-border transfer (数据出境). The duty lands on you, the personal-information handler, not on Shippo: Articles 13 and 23 require notice and a basis to collect the data, and Articles 38–40 require a transfer mechanism to send it abroad — a CAC security assessment, the CAC standard contract, or certification. A delivery address paired with a phone number is whereabouts-level, high-risk data, so PIPL Articles 28–29 raise the bar with a specific-purpose, necessity and separate-consent test.
The second door is the one that makes a shipping platform different from an ordinary offshore app, and it is the half a speed test is blind to: bulk and fan-out. Shippo ingests consignee PII for every parcel and then, by its own account, discloses it to “carriers, merchant platforms integrated with Shippo, and service providers” — a web of offshore sub-processors, with its notice reproducing USPS and FedEx carrier privacy statements as a sign of how far the data travels. High-volume consumer personal information generated in China, replicated out to multiple parties abroad, is precisely the pattern that triggers the in-country-storage duty: the Cybersecurity Law’s Article 39 (formerly Article 37 — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, with its substance unchanged) requires personal information generated in China by a critical information infrastructure operator or a high-volume handler to be stored in the mainland, which a US-only platform cannot satisfy. Whether that duty bites your case turns on your volumes and role — treat it as a risk to confirm with counsel, not a settled label.
The third door is the ICP filing. If you publish a China-facing branded tracking page or a recipient self-service page to mainland users, you are running a public internet information service, and that turns on an ICP filing (ICP 备案) duty bound to a hosting resource physically inside the mainland. A Shippo-hosted tracking page runs offshore, so there is nothing on it to file against — tuning the stack does not create the mainland footing a filing needs.
A reachability check never sees this
Shippo is not the kind of service that simply refuses to load in China — the exposure is quieter and more durable than a slow paint. Even if the label API and the tracking page answered instantly from the mainland, using them would still place your China recipients’ names, addresses and phone numbers outside the country and hand them to a chain of offshore carriers and sub-processors. A reachability test answers “did the request come back?”; it is blind to where the consignee data comes to rest, how many parties it reaches, and whether a public tracking page is lawfully filed. Where the data lives and who holds it, not how fast it arrives, is what China’s law responds to.
This is a risk map, not a verdict that Shippo is “blocked” or “illegal” in China. Which duties apply to you depends on your entity, your shipping volumes, your role under Chinese law and whose personal information you are shipping — worth settling the specifics with counsel before your China fulfilment depends on it.
The lawful path — map, localize, deliver
There is a compliant way to run multi-carrier shipping for a China operation, and it sits in front of the Shippo your team already uses — no rebuild, no second tool, no migration.
First, map: our China team inventories what your Shippo account holds — the recipient name, address and phone for each shipment, the tracking data, and any China-facing tracking or self-service page — establishes where it is hosted (an offshore US region), which carriers and sub-processors it is disclosed to, the ICP status of any public page, and the consent and residency basis each flow relies on. We build the technical picture; the legal conclusions are settled with counsel.
Then localize/govern: we help you keep the regulated data — the consignee PII — on a lawful in-country path, obtain the Article 13/23 notice-and-consent, and honor the high-volume in-country-storage expectation rather than letting every recipient’s address and phone replicate abroad to each carrier by default. Localize means keeping the data on an in-country path — never a route that ships it offshore anyway.
Then deliver: any public China-facing tracking or self-service page is an internet information service, so it carries an ICP filing duty bound to mainland hosting and needs compliant, in-country delivery. 21YunBox stands that up — the 21YunBox Optimizer — in front of what you already run, so it serves your recipients in China legally and compliantly. 21YunBox never uses or suggests circumvention of any kind — we keep in-country what the law says must stay, deliver the rest compliantly from inside the mainland, and never move personal information across the border by stealth. Making an offshore platform merely reachable is not the answer; keeping the recipient data in-country, ICP-filing the tracking page and delivering it compliantly is. 21YunBox is a compliance overlay and partner to the shipping platform you already run, not a competitor to it.
Related reading:
- How to get an ICP filing for China
- Cross-border data transfers under PIPL
- China’s Personal Information Protection Law (PIPL)
- China’s Cybersecurity Law


