Does Resend Work in China? PIPL Cross-Border, Recipient Data & Delivery Compliance
Resend's email API is reachable from China, but it stores your recipients' email addresses, message content, and delivery logs on AWS in the United States, with no mainland-China region — so every send to a China recipient is a PIPL cross-border transfer. A compliance-first look at where Resend keeps your recipient data and the lawful path into China.
Does Resend work in China?
Resend is reachable from China, but it stores your recipients' email addresses, message content, and delivery logs in the United States — so every send to a person in mainland China is a cross-border transfer of their personal information, not a speed question.
Resend is an AWS-hosted email API: you hand it the recipient's address and the message body, and it stores that message content, delivery logs, webhook payloads, and account records in the US — with no mainland-China region, and its sending regions (such as eu-west-1) do not move where data is stored. Sending to someone in China therefore makes you the handler of a PIPL cross-border transfer (Articles 38–40): notice, a separate consent, and a transfer mechanism, with a marketing consent and opt-out on top (Articles 13/23). The lawful lever is a compliant in-country delivery path with consent and data minimization — plus ICP-filed delivery for the app that triggers the mail — not making the offshore API reachable.
This is a risk map, not a verdict — settle the specifics with counsel. Our China team can map your exposure →
What Resend's own documentation says about China
| Fact | Primary source |
|---|---|
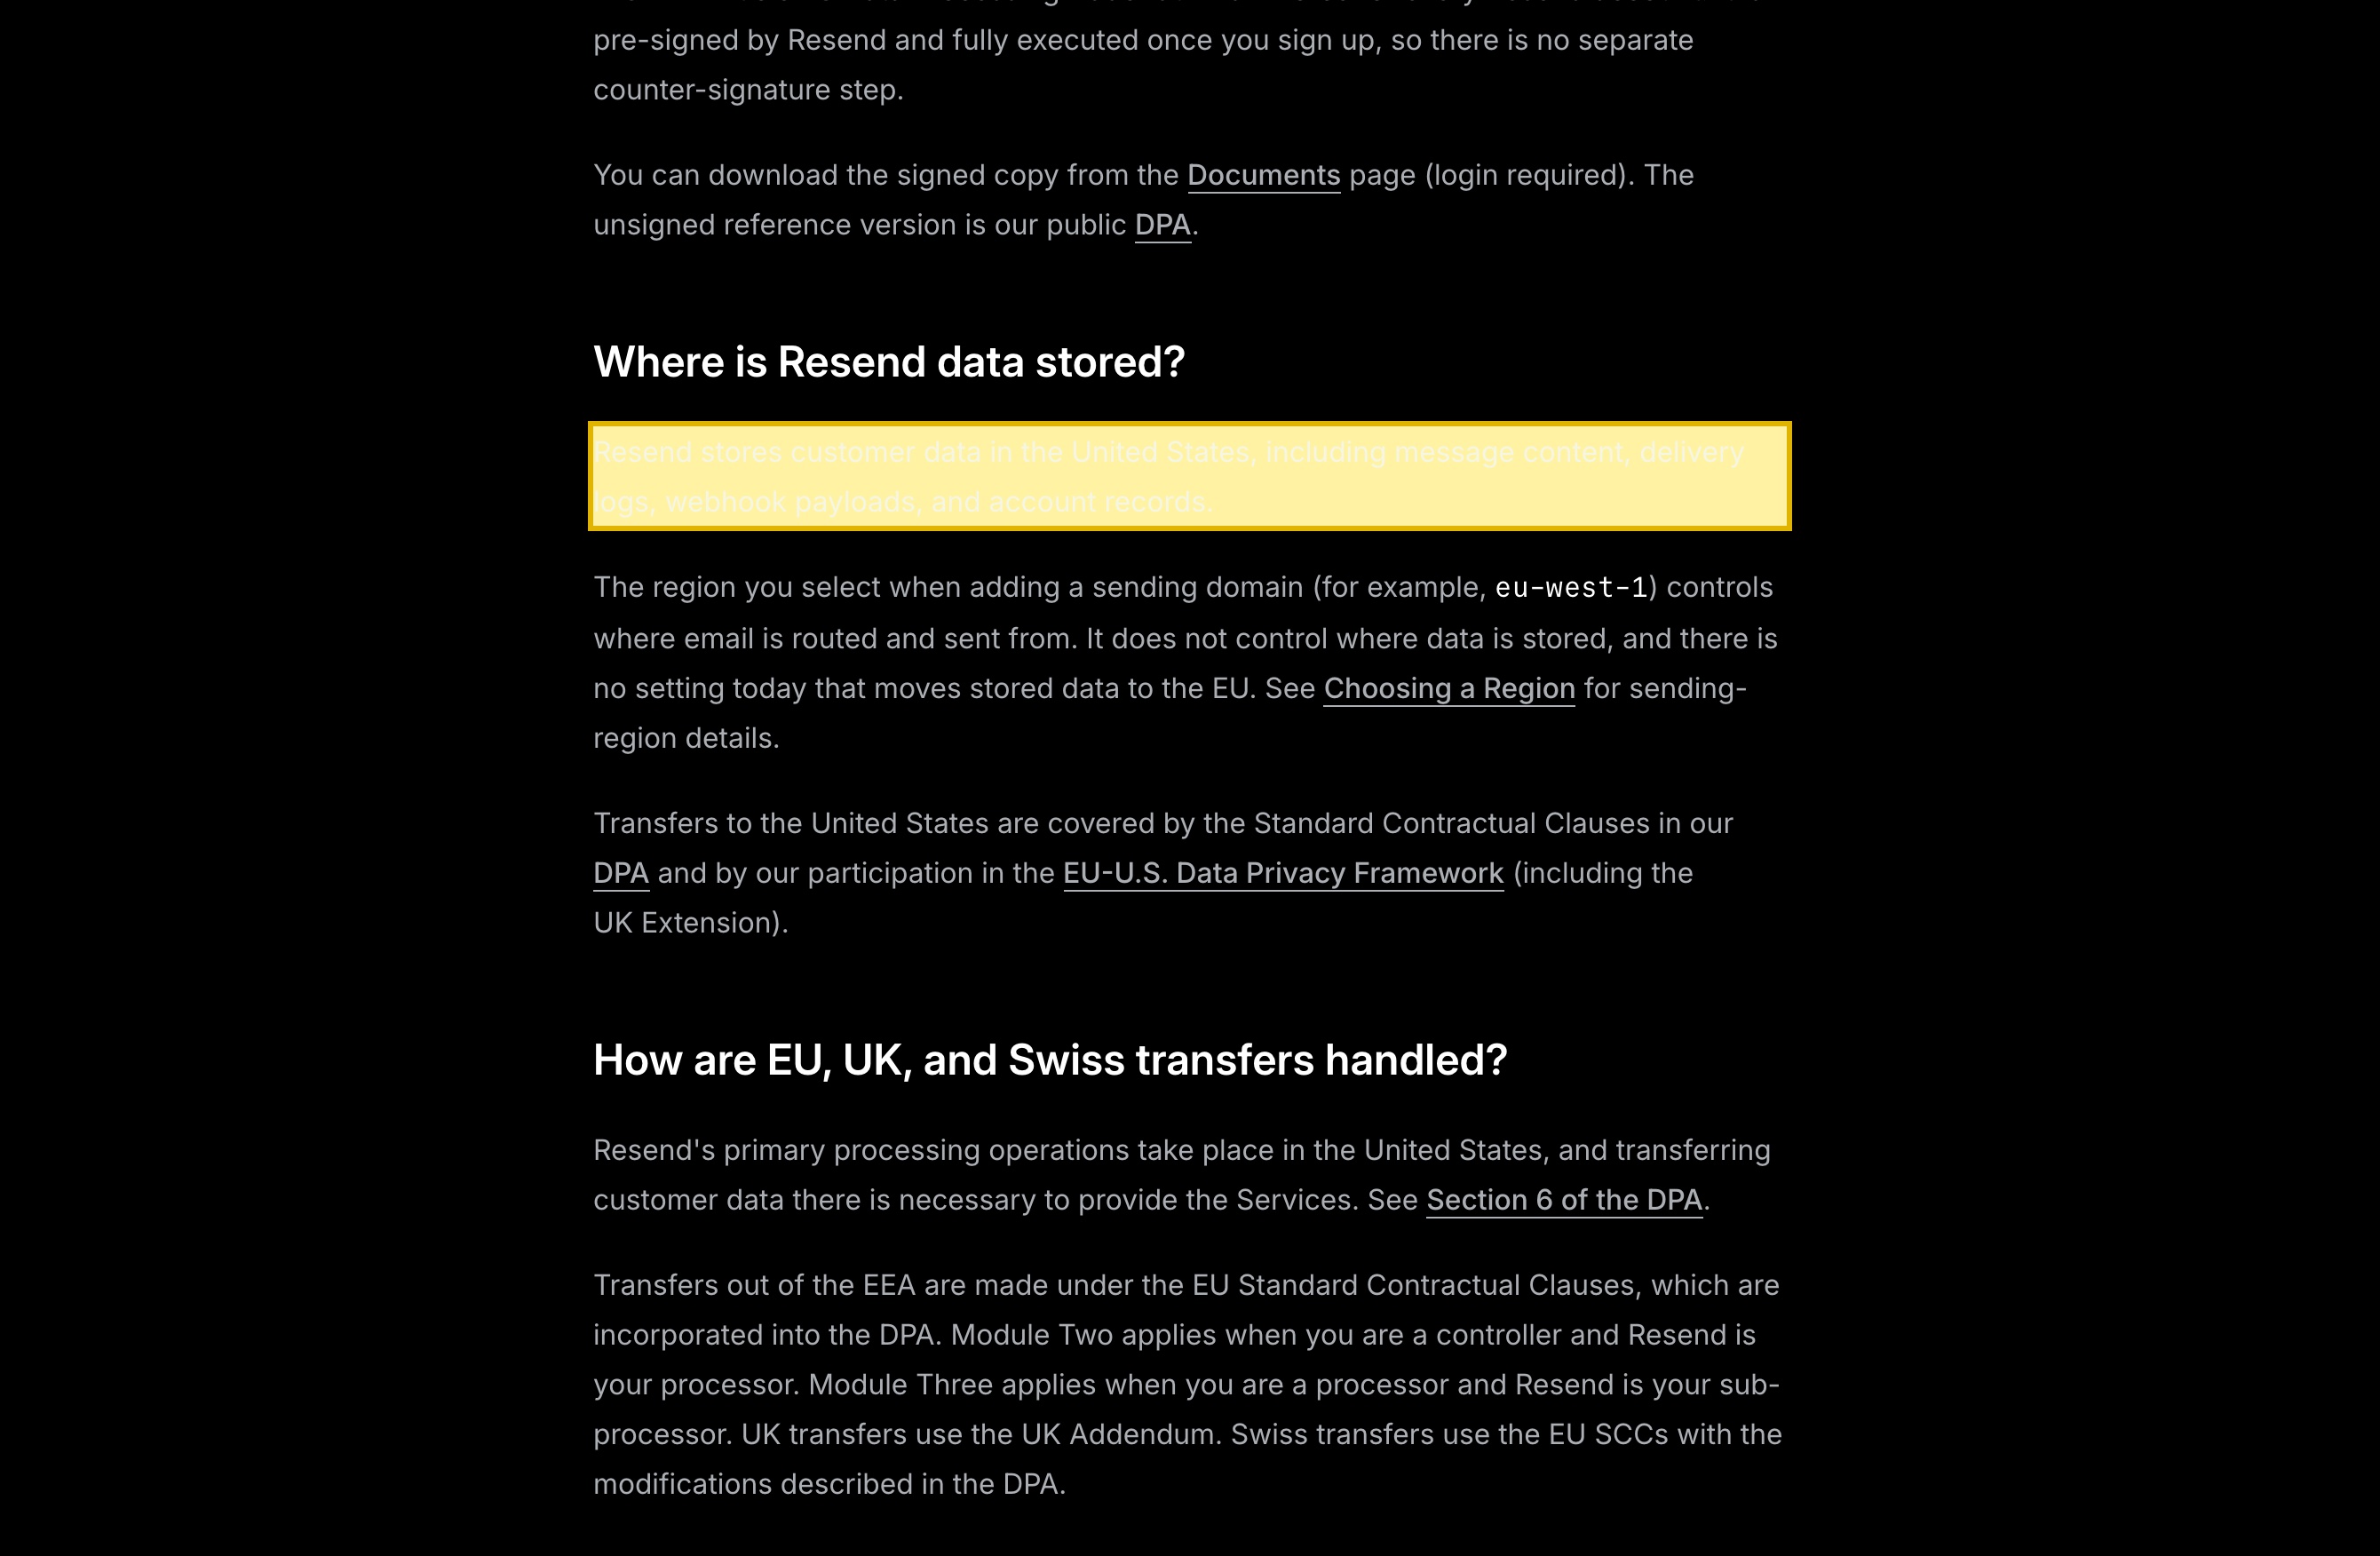
| Resend stores customer data in the United States, with no mainland-China region. Its GDPR page states it stores “message content, delivery logs, webhook payloads, and account records” in the US, and that the sending region you choose (for example eu-west-1) “does not control where data is stored, and there is no setting today that moves stored data to the EU.” | Resend — GDPR page (resend.com), retrieved 2026-10-10 |
| Hosting is AWS, every sub-processor is US-based, and records are retained offshore. Resend lists “Amazon Web Services, Inc. (USA): Third party hosting and sending provider” first among 22 sub-processors, each tagged (USA) and none in China; email and log data is retained for 30 days while an account is active, remaining data deleted within 90 days of termination, and backups kept for 7 days. | Resend — Subprocessors and GDPR pages (resend.com), retrieved 2026-10-10 |
| Sending a China recipient's address and content offshore is a PIPL cross-border transfer. Uploading the recipient's email and the message body to US servers triggers PIPL Articles 38–40 on you, the handler — notice, a separate consent, and one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification) — and marketing sends add a consent-and-opt-out duty under Articles 13/23. | PIPL Articles 38–40 and 13/23 (21YunBox cross-border explainer), retrieved 2026-10-10 |
| A CIIO or high-volume handler owes an in-country storage duty US servers cannot meet. The Cybersecurity Law Article 39 (formerly Article 37) requires personal information collected in China to be stored in China; the 2025 amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, with its substance unchanged. | China Cybersecurity Law Article 39 (formerly 37), retrieved 2026-10-10 |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a product emailing users in mainland China, the first question about Resend is usually whether its API can even be reached from the mainland — and it can; Resend is a developer-focused email API that China does not block outright. So reachability is not where the China decision is made. What decides it is what happens when you hand Resend your China recipients’ contact details and the message itself to deliver on your behalf. Resend is hosted on AWS and, by its own account, stores customer data — message content, delivery logs, webhook payloads, and account records — in the United States, with no mainland-China region. That puts two distinct questions on the table: the cross-border transfer of your recipients’ personal information out of China, and the delivery-and-filing counterpart — getting mail into mainland mailboxes, and the ICP duty the app that triggers the mail carries.
Resend in China at a glance
| What decides it | In Resend's own terms — and China's law |
|---|---|
| What you hand Resend | The recipient's email address and the message body. Resend itself stores “message content, delivery logs, webhook payloads, and account records” — all of it personal information once the recipient is a person in mainland China. |
| Where it goes | Offshore. Resend stores customer data in the United States and lists “Amazon Web Services, Inc. (USA)” as its hosting and sending provider. Its sending regions (us-east-1, eu-west-1, sa-east-1, ap-northeast-1) include none in mainland China, and choosing the EU region “does not control where data is stored.” |
| Sending China-collected email through it | Every send to a China recipient moves that recipient's email address and message content out of the country — a cross-border transfer (数据出境) under PIPL Articles 38–40. The duty is on you, the handler: notice, a separate consent, and one transfer mechanism. |
| Retention, residency & consent | Resend retains email and log data for 30 days while an account is active, deletes remaining data within 90 days of termination, and keeps backups for 7 days — all in the US. A critical information infrastructure operator owes an in-country storage duty (Cybersecurity Law Article 39, formerly Article 37); marketing sends also need a separate consent and a working opt-out (PIPL Articles 13/23). |
| The lawful path | Reachability is not the axis. Route China-recipient delivery through a compliant in-country path, keep recipient data minimized, obtain the cross-border and marketing consents, and deliver the triggering app in-country on ICP-filed infrastructure. 21YunBox maps, localizes, and delivers; it is advisory on licensing and legal questions, which sit with your counsel. |
What you actually hand it — your recipients’ contact data and content
With a transactional email API, the thing you send is not a page to render — it is a person’s contact details and a message about them. Each call to Resend carries the recipient’s email address and the message body, which for a China-facing product routinely contains exactly what a notice reveals: a one-time passcode, a password reset, an order or shipping confirmation, an account or billing notice. Resend then keeps a record of it. Its GDPR page states that it stores “message content, delivery logs, webhook payloads, and account records” in the United States, retaining email and log data for 30 days while the account is active (longer under enterprise agreements), deleting remaining customer data within 90 days of account termination, and keeping backups for 7 days. All of that is personal information, and all of it rests offshore.
Resend is hosted on AWS — it lists “Amazon Web Services, Inc. (USA): Third party hosting and sending provider” first among its sub-processors, every one of which is tagged (USA), and none in mainland China. Resend has added sending regions — North Virginia (us-east-1), Ireland (eu-west-1), São Paulo (sa-east-1), and Tokyo (ap-northeast-1) — but those control only where outgoing mail is dispatched from. In Resend’s own words, the choice “does not control where data is stored, and there is no setting today that moves stored data to the EU.” The data rests in the United States wherever you send from, and there is no mainland-China region at all.
It’s a cross-border transfer — of your recipients’ personal information
Here is the gate most teams miss. The moment you send to a person in mainland China, you upload that person’s email address — and whatever the message body reveals about them — to Resend’s US infrastructure. Under China’s Personal Information Protection Law that is a cross-border transfer of personal information (数据出境), and PIPL puts the duty on the handler — you, Resend’s customer, not Resend. Articles 38–40 require notice, a separate consent distinct from any agreement to receive your email, and one transfer mechanism: a CAC security assessment, the CAC standard contract, or certification. Above certain thresholds, or where the data is “important data,” that transfer may also require China’s data-export security assessment (数据出境安全评估) before anything leaves.
Two more duties stack on top. If any of your China messaging is commercial — a promotion, a newsletter, a win-back — PIPL Articles 13 and 23 require a lawful basis and the recipient’s consent, and you must honor opt-out; a transactional relationship does not by itself license marketing. And if your organization is a critical information infrastructure operator or a high-volume handler, the Cybersecurity Law’s Article 39 (formerly Article 37 — the data-localization article was renumbered by the 2025 amendment, in force since January 1, 2026, with its substance unchanged) requires that personal information collected in China be stored in China, an in-country storage duty that US-resident email records cannot satisfy. None of this turns on how fast the API answers; it turns on whether the data had a lawful basis to leave the country.
Reaching the API isn’t the question — a compliant in-country delivery path is
So “can we reach Resend from China?” is the wrong test. It reaches. The productive question is how to keep your China recipients’ data on a lawful footing and still get the mail delivered — and that has two parts. The compliance part is to stop the unconsented offshore send of China contact data: route your China-recipient messaging through a compliant, in-country delivery path, keep the recipient data you transfer to a minimum, obtain the separate cross-border consent (and the marketing consent where it applies), and keep a lawful basis for anything that still leaves.
The practical part is delivery itself. Email sent from offshore IP ranges to the big mainland mailbox providers meets filtering and deliverability friction that senders outside China rarely encounter. This page puts no number on that — a deliverability rate means nothing without a stated method, sample, and date — but it is a common reason teams want an in-country sending path regardless of the legal analysis. And separately, the app or site that triggers and manages the mail — the sign-up, the receipt, the reset — is itself a public service in the mainland, so it carries an ICP filing (备案) duty and needs compliant, in-country delivery. This is a risk map, not a verdict: whether a transfer mechanism, in-country storage, or a reworked consent flow applies to your program depends on what you actually send, how much, and to whom — settle the specifics with counsel before you build.
The lawful path — map, localize, deliver
There is a lawful way to run email for a China-facing product, and it has a shape. First, map: our China team inventories which messages go to China recipients, what contact data and content each one carries, where Resend processes and stores it, and what it retains — then works through your PIPL cross-border exposure, your marketing-consent duties, and any Article 39 in-country storage duty. We frame the technical picture; you settle the legal conclusions with counsel.
Then localize: route the China leg — the transactional and notification mail you send to users in the mainland — through a compliant, in-country delivery path, while you keep Resend for the markets where it already serves you. Localizing means stopping the unconsented offshore send of China contact data and moving China delivery onto a lawful in-country path — never a tunnel that ships the data offshore anyway. Where a telecom or messaging license bears on the channel, that sits with a licensed domestic operator and your counsel; 21YunBox is advisory there and holds no such license.
Then deliver: the China-facing app that triggers and renders those emails carries an ICP filing (备案) duty and needs compliant, in-country delivery — the 21YunBox Optimizer, in front of the stack you already run, with no rebuild and no re-platform. The result is an email program that runs legally and compliantly for your users in China. 21YunBox never uses or suggests circumvention of any kind. We are a compliant overlay and partner to Resend, not a competitor to it.
Related reading:
- Cross-border data transfers under PIPL
- China’s data-export security assessment
- China’s Cybersecurity Law (data localization, Article 39)
- How to get an ICP filing for China


