Does Postmark Work in China? PIPL Cross-Border, Recipient Data & Delivery Compliance
Postmark's API and SMTP are callable from mainland China, so reachability is not the real question. Postmark (an ActiveCampaign product) runs no mainland-China region — it processes and stores email in the United States and retains message content for 45 days — so every send to a China recipient is a cross-border transfer (数据出境) of their personal information under PIPL. A compliance-first look at Postmark's processing location, retention, the cross-border and consent duties, and the lawful China path.
Does Postmark work in China?
Yes — Postmark's API and SMTP are callable from mainland China, so reachability is not the problem; what decides it is where your recipients' data goes.
Postmark (an ActiveCampaign product) runs no mainland-China region: its own EU Data Protection page places its primary data and servers at a Deft data center outside Chicago and on Amazon Web Services, with no plans for EU servers. It retains message content and metadata for 45 days and keeps bounces, complaints, and unsubscribes indefinitely in a suppression list. So handing it a China recipient's email address and message content is a PIPL cross-border transfer (数据出境) of their personal information — notice, a separate consent, and a transfer mechanism — and promotional sends add an Article 13/23 consent duty; for a critical information infrastructure operator, the Cybersecurity Law's Article 39 (formerly Article 37) requires in-country storage an offshore region cannot meet. The lawful lever is a licensed, China-resident delivery path plus consent and data minimization — not making the offshore API reachable.
Treat the specifics as a risk to confirm with counsel. Our China team can map your exposure →
What Postmark's own documentation says about China
| Fact | Primary source |
|---|---|
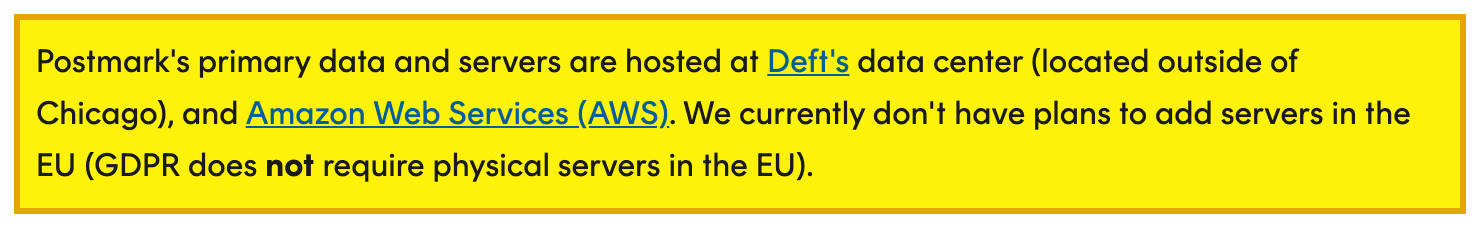
| Postmark runs no mainland-China region — it processes and stores email in the United States. Its EU Data Protection page states that “Postmark's primary data and servers are hosted at Deft's data center (located outside of Chicago), and Amazon Web Services (AWS),” and that “We currently don't have plans to add servers in the EU.” There is no China sending region. | Postmark, “EU Data Protection” (postmarkapp.com), retrieved 2026-10-10 |
| Postmark retains message content and metadata for 45 days by default, and keeps suppression data indefinitely. Postmark states it “stores email content, events (e.g. delivery, click, open), and metadata for all messages for 45 days by default,” adjustable “from 7 to 365 days with our Retention Add-on,” while bounces, complaints, and unsubscribes are “stored indefinitely in a Streams Suppression list.” | Postmark Support, “How long are Inbound and Outbound messages stored in activity?” and EU Data Protection (postmarkapp.com), retrieved 2026-10-10 |
| Sending a China recipient's email address and message content offshore is a cross-border transfer under PIPL. A recipient's email address — and the names, codes, orders, and balances a message carries — is personal information; handling it on offshore infrastructure triggers PIPL Articles 38–40 (notice, a separate consent, and one transfer mechanism), while promotional content adds an Article 13/23 consent-and-opt-out duty. | Personal Information Protection Law of the PRC, Articles 38–40, 13, 23 (cac.gov.cn), retrieved 2026-10-10 |
| For a critical information infrastructure operator, China-collected data must stay in China (CSL Article 39, formerly 37). The Cybersecurity Law requires personal information and important data collected in the mainland to be stored there; the 2025 amendment, in force January 1, 2026, renumbered this duty from Article 37 to Article 39, substance unchanged — an in-country storage duty an offshore Postmark region cannot meet. | Cybersecurity Law of the PRC (2025 amendment, in force 2026-01-01), Article 39 (cac.gov.cn), retrieved 2026-10-10 |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a product that emails users in mainland China — password resets, one-time passcodes, receipts, account notices — the first question about Postmark is usually whether it can be reached. It can: its API and SMTP are callable from the mainland, and it is not a service China blocks outright. So reachability is not where the China decision is made. That turns on what happens the moment you hand Postmark your China recipients’ email addresses and message content to deliver on your behalf. Postmark — a transactional email service owned by ActiveCampaign — processes and sends from infrastructure in the United States, and retains each message’s content and metadata for 45 days, with bounces, complaints, and unsubscribes kept indefinitely in a suppression list. Two legs decide whether that is lawful: the cross-border transfer of your recipients’ personal information offshore, and the delivery counterpart — mainland-mailbox deliverability plus the triggering app’s ICP filing duty.
Postmark in China at a glance
| What decides it | In Postmark's own terms — and China's law |
|---|---|
| What you hand it | Postmark is a transactional email API and SMTP relay (password resets, one-time passcodes, receipts, account notices). To send, you hand it the recipient's email address and the message content — plus whatever the body reveals, such as a name, an order, or a verification code. For a recipient in the mainland, all of it is personal information. |
| Where it processes and stores it | Offshore, in the United States. Postmark's own EU Data Protection page places its primary data and servers at a Deft data center outside Chicago and on Amazon Web Services, and says it has no plans to add servers even in the EU. There is no mainland-China region. |
| Sending China email through it | Recipient addresses, message content, and event data (opens, clicks, bounces) are personal information. Sending them through an offshore Postmark is a cross-border transfer (数据出境) under PIPL (Articles 38–40): notice, a separate consent, and one transfer mechanism. Promotional (Broadcast) sends also need a lawful basis and consent (Articles 13 and 23) and must honor opt-out. |
| What it keeps — and the delivery counterpart | Postmark retains content and metadata for 45 days by default (adjustable 7–365 days) and keeps bounces, complaints, and unsubscribes indefinitely in a suppression list. For a critical information infrastructure operator, the Cybersecurity Law's Article 39 (formerly Article 37) adds an in-country storage duty an offshore region cannot meet. Separately, getting mail into mainland mailboxes from offshore IPs is an operational hurdle, and the app that triggers the email carries its own ICP filing duty. |
| The lawful path | Route the China leg through a compliant, China-resident email or notification service, keep Postmark for your other markets, minimize the recipient data that still leaves, obtain the Article 13/23 consent for anything promotional, and deliver the China-facing app in-country on ICP-filed infrastructure. 21YunBox maps, localizes, and delivers — advisory on any telecom or licensing question, which sits with a licensed local operator and your counsel. |
What you actually hand it — your recipients’ contact data and content
A transactional email service is not a passive pipe. To send a password reset or a receipt to someone in Shanghai, you pass Postmark that person’s email address and the full content of the message — and often a name, an order number, a verification code tied to a real account, or a balance or status the body reveals. Postmark processes and sends that from its own infrastructure, which its EU Data Protection page places at a Deft data center outside Chicago and on Amazon Web Services; it states plainly that it has no plans to add servers in the EU, and there is no mainland-China region at all.
It also keeps the data. Postmark’s documentation says it “stores email content, events (e.g. delivery, click, open), and metadata for all messages for 45 days by default,” a window its Retention Add-on can set anywhere “from 7 to 365 days.” Even after a message expires, the record is not fully gone: bounces, spam complaints, and unsubscribed recipients are “stored indefinitely in a Streams Suppression list.” Postmark is transactional-focused — bulk and promotional mail is meant to run through a separate Broadcast stream — but either way, the recipient addresses, the content, and the engagement events your China-facing email generates live on offshore infrastructure for as long as Postmark holds them. That retained, offshore personal information is what China’s law weighs, not how fast the API answers.
It’s a cross-border transfer of your recipients’ personal information
Here is the gate most teams miss. The recipient addresses, message content, and event data a Postmark account holds for your users in China are personal information — and once they sit on infrastructure in the United States, you have made a cross-border transfer (数据出境) of that data out of the mainland. China’s Personal Information Protection Law puts the duty on the handler — you, the sender, not the email vendor: Articles 38–40 require notice to the individual, a separate consent distinct from their agreement to receive your email, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. Where the content you send is promotional rather than strictly transactional, PIPL Articles 13 and 23 add a lawful-basis-and-consent duty of their own, and the recipient’s opt-out must be honored.
Residency can bite on top of consent. Above certain volumes, or where the data is “important data,” the transfer may require China’s data-export security assessment (数据出境安全评估) before anything leaves. And if your organization is a critical information infrastructure operator, the Cybersecurity Law’s Article 39 (formerly Article 37 — the 2025 Cybersecurity Law amendment, in force since January 1, 2026, renumbered the data-localization article from 37 to 39, with its substance unchanged) requires personal information collected and generated in China to be stored in China. That is an in-country storage duty a Postmark account hosted in the United States — retaining content for 45 days and suppression data indefinitely — simply cannot satisfy. None of this turns on how quickly a message is delivered; it turns on whether your recipients’ data had a lawful basis to leave the country, and whether it had to stay in the first place.
Reaching the API isn’t the question — a compliant in-country delivery path is
Even setting the compliance gate aside, there is an operational reality worth naming: email sent from offshore IP ranges to mainland mailbox providers meets filtering and deliverability friction that senders outside China rarely see. This page puts no number on it — a deliverability rate is meaningful only with a stated method, sample, and date, and we do not publish an invented one — but it is a common reason teams end up wanting a China-resident sending path regardless of the legal analysis. It is, though, a delivery problem, not the decision.
The decision is the data question above, and the lawful answer is not to make the offshore API more “reachable.” It is to stop the unconsented offshore send of your China recipients’ contact data and move the China leg onto a compliant, in-country delivery path — a China-resident email or notification service that keeps those recipient addresses and message bodies in-country — while you keep Postmark for the markets where it already serves you, obtain the Article 13/23 consent for any promotional content, and minimize the recipient data that still crosses the border. This is a governed, in-country delivery path, never a tunnel that ships the data offshore anyway. Where any telecom or licensing question touches the arrangement, that sits with a licensed local operator and your counsel — 21YunBox is advisory there and holds no China telecom or SMS license. Which of these duties apply to your specific program, and in what combination, is a risk to settle with counsel against what you actually send, store, and retain — this page is a risk map, not a verdict.
The lawful path — map, localize, deliver
There is a lawful way to run email for a China-facing product, and it has a shape. First, map: our China team inventories which messages go to your China recipients, what contact data and content each one carries, where Postmark processes and stores it and what it retains (content and metadata for 45 days, suppression data indefinitely), the consent basis for anything promotional, and where a data-export security assessment or an Article 39 storage duty bites. Settle the legal conclusions with counsel; we frame the technical picture that feeds them.
Then localize: route the China leg — the transactional and notification email you send to users in the mainland — through a compliant, China-resident email or notification service that keeps those recipient addresses and message bodies in-country, while you keep Postmark for the markets where it already serves you. We stand up and integrate that in-country path in place of the offshore send, keep the recipient data minimized, and help you hold the Article 13/23 consent for any promotional content — so your China email stops being the thing that quietly carries personal information out of the country.
Then deliver: the China-facing app or site that triggers and renders those emails — the sign-up, the receipt, the password reset — is itself a public service in the mainland, so it carries an ICP filing (备案) duty and needs compliant, in-country delivery. 21YunBox delivers it in-country — the 21YunBox Optimizer — in front of what you already run, with no rebuild and no re-platform. The result is a China-facing email program that runs legally and compliantly for your users in China. 21YunBox never uses or suggests circumvention of any kind. What we do is localize the China leg onto a lawful, in-country service and deliver in-country — we never route your recipients’ personal information out of China by stealth.
Related reading:
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law (data localization, Article 39)
- China’s data-export security assessment
- How to get an ICP filing for China


