Does Hive Work in China? PIPL Cross-Border, Data Residency & Sensitive-Data Rules
Hive is a United States content-moderation and computer-vision API — Visual, Text and Audio Moderation — operated from the United States with no mainland-China region. The images, video and user-generated content your China users send it to moderate ARE the personal information, often sensitive (a face is biometric), so moderating them is a PIPL cross-border transfer: a compliance-first look at the residency, sensitive-data and cross-border exposure, and the lawful in-country path.
Does Hive work in China?
The images, video, and user-generated content your China users send Hive to moderate ARE the personal information — often the most sensitive kind, because a face in a moderated photo is biometric data — and Hive has no mainland-China region, so moderating them offshore is a PIPL cross-border transfer of sensitive personal data.
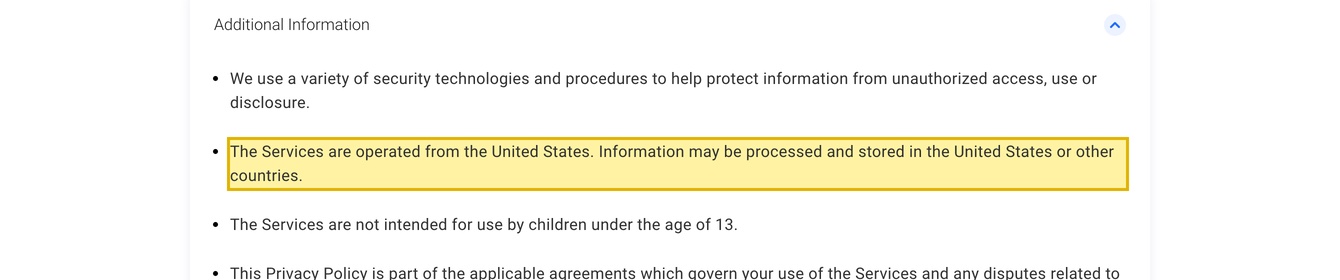
Hive is a United States content-moderation and computer-vision API whose privacy policy says its services "are operated from the United States," with information "processed and stored in the United States or other countries." The content you send to be moderated is other people's personal information and expression, and it cannot be minimized or anonymized because it IS the input — a face, an uploaded ID, the UGC itself — which makes it PIPL Article 28 sensitive personal information. Sending it abroad is a cross-border transfer (Articles 38–40 plus the Article 29 separate consent), and wiring Hive's scores into automatic takedowns is an Article 24 automated decision. The lawful lever is to keep the moderation of China content in-country, minimize, obtain the separate consent, and ICP-file any China-facing surface — not to make the offshore API reachable.
Whether a given image or piece of UGC is sensitive or "important data" turns on what you process and your sector — settle the specifics with counsel. Our China team can map your exposure →
What Hive's own documentation says about China
| Fact | Primary source |
|---|---|
| Hive is operated from the United States, with no mainland-China region. Hive's privacy policy (last updated September 21, 2026) states the services "are operated from the United States" and that information "may be processed and stored in the United States or other countries." The content your China users post is therefore analyzed and retained outside the mainland. | Hive — Privacy Policy (thehive.ai/privacy), retrieved 2026-10-11 |
| Hive moderates images, video, text and audio, and returns classification metadata — your platform enforces. Hive's documentation lists support for "text, images, videos, audio, and text within images (OCR)" and live RTMP/HLS streams, states "The Hive API simply returns classification metadata based on our model outputs," and sets a "default policy ... to retain customer data for 14 days" (adjustable on request). Wiring those scores into automatic takedowns is your automated decision under PIPL Article 24. | Hive Docs — Frequently Asked Questions (docs.thehive.ai), retrieved 2026-10-11 |
| A face or an uploaded ID is sensitive personal information that can't be minimized. Under PIPL Article 28, biometric data (a face) and ID and financial-account numbers are sensitive personal information, requiring a separate consent (Article 29) and a prior personal-information protection impact assessment. Because the sensitive content is the very thing you send to be moderated, it cannot be anonymized before transfer. | 21YunBox — Personal Information Protection Law (Articles 24, 28, 29), retrieved 2026-10-11 |
| Moderating China content offshore is a PIPL cross-border transfer. Sending China-collected UGC to a service operated from the United States triggers PIPL Articles 38–40: notice, a separate consent, and a transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. A CIIO or high-volume handler also owes in-country storage under Cybersecurity Law Article 39 (formerly Article 37), and high image/video volumes can require a CAC data-export security assessment. | 21YunBox — Cross-Border Data Transfers under PIPL, retrieved 2026-10-11 |
Sources verified by the 21YunBox compliance team on 2026-10-11.
For a platform running Hive across a China operation, the instinct is to ask whether the moderation API answers from Shanghai. It does — Hive is cloud software China does not block — so reachability is not the question. What settles it is that the images, video, text, and user-generated content you send Hive to moderate ARE the personal information, often the most sensitive kind: a face in a moderated photo is biometric data, and the UGC is other people’s data and expression. Hive is a United States content-moderation and computer-vision API whose privacy policy states the services “are operated from the United States,” with information “processed and stored in the United States or other countries” — no mainland-China region, no in-country build. So that content is analyzed offshore: a PIPL cross-border transfer of (often sensitive) personal information, with an Article 28 sensitive-data door, an Article 24 question where you auto-enforce on its scores, residency rules for a high-volume handler, and an ICP filing for any China-facing surface.
Hive in China at a glance
| What decides it | In Hive's own terms — and China's law |
|---|---|
| What you send it | Hive moderates the content your users post — images, video, text, audio, and text within images (OCR), including live RTMP and HLS streams. For a China-facing community that content is user-generated content: it is other people's personal information and expression, and the sharp case is a face in a photo or video frame, which is biometric data. The content you send to be moderated IS the personal information — you cannot minimize or anonymize it, because it is the input. |
| Where it runs | Offshore. Hive's privacy policy states the services "are operated from the United States," with information "processed and stored in the United States or other countries." There is no mainland-China region and no customer-run, in-country deployment named. So the content your China users post comes to rest outside China when you send it to be moderated — a cross-border transfer (数据出境) under PIPL (Articles 38–40), reinforced by a separate-consent duty for sensitive data (Article 29). |
| The sensitive-PI door | A face in a moderated image or frame is biometric data — sensitive personal information under PIPL Article 28 — which requires a separate consent and a prior personal-information protection impact assessment. If the UGC contains an ID card, a passport or a bank card, those ID and financial-account numbers are sensitive too. None of it can be minimized away: the face, or the content itself, IS what you sent Hive to read. |
| Automated decision + residency | Hive itself returns only classification metadata ("The Hive API simply returns classification metadata based on our model outputs") and does not remove content; you enforce. When you wire those scores into automatic action — removing or restricting a user's content — that enforcement is an automated decision under PIPL Article 24, and the duty is yours. A critical information infrastructure operator or high-volume handler must store China-generated personal information in the mainland under the Cybersecurity Law's Article 39 (formerly Article 37 — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged); large image and video volumes can raise the "important data" question and a CAC data-export security assessment. |
| Reachability is not the axis | Whether Hive's API answers from the mainland is not the decision; where the content your China users post is analyzed, and on what legal basis, is. The lawful path keeps the moderation of China content on an in-country footing — a China-resident processing path or a China-legal domestic alternative — minimizes and obtains the separate consent for the sensitive data, handles any Article 24 and important-data duty, and delivers any China-facing surface in-country on ICP-filed infrastructure. 21YunBox maps, localizes and delivers; it never moves personal information offshore by stealth. |
What you actually send it — and why the content is the risk
Hive does not hold an abstraction; it reads the content your users post. Hive’s own documentation lists the media its models classify — “text, images, videos, audio, and text within images (OCR)” — and confirms it processes “live RTMP and HLS streams across both audio and visual inputs.” So the inputs are photos, video frames, comments, captions, audio clips and livestreams uploaded by the people in your community. For a China-facing platform, every one of those items is user-generated content: it is other people’s personal information and their expression, sent out of the country to be read.
The sharp cases are the sensitive ones, and they cannot be designed around. A face captured in a moderated photo or video frame is biometric data. If a user uploads an ID card, a passport, a bank card or a KYC selfie — exactly the material a trust-and-safety pipeline is built to catch — the identifiers in it are sensitive too. You cannot “minimize” or anonymize this content before moderation, because the content IS what you sent Hive to analyze: the whole point is to read the image, not a redacted version of it.
Where is it read? Offshore. Hive’s privacy policy (last updated September 21, 2026) states the services “are operated from the United States” and that information “may be processed and stored in the United States or other countries,” and Hive’s FAQ states its “default policy is to retain customer data for 14 days” (adjustable on request, including not retaining it at all). There is no mainland-China region named, and no customer-run, in-country deployment. So the moment your China users’ uploads enter the moderation pipeline, that content leaves the country.
The doors: sensitive personal data, cross-border transfer, and automated decisions
Once the content is offshore, a different body of law decides whether it was allowed to go. The UGC you send Hive is personal information under China’s Personal Information Protection Law, and sending it to a service operated from the United States is a cross-border transfer (数据出境). PIPL puts the duty on the handler — your China entity, not Hive the processor: Articles 38–40 require notice, a separate consent distinct from any general terms of use, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification — with the minimization duties of Articles 13 and 23.
The distinctive door for moderation is the sensitive one. A face in a moderated image is biometric data, and biometric data is sensitive personal information under PIPL Article 28; so are the ID and financial-account numbers that surface when users upload identity documents. Sensitive personal information raises the bar — Article 29 requires a separate consent specific to it, and a prior personal-information protection impact assessment — and, crucially, it cannot be minimized away, because the sensitive content is the very thing you sent to be read.
Automated decisions are the third door. Hive returns classification metadata and does not itself remove content; your platform does. The moment you wire a confidence score into automatic enforcement — taking down, hiding or restricting a user’s content without a human in the loop — that is automated decision-making under PIPL Article 24, which gives the user the right to an explanation and to refuse a decision made solely by automated means. Running a China-facing community that hosts this content also carries content-management duties under China’s own network-information rules — a separate obligation to settle with counsel.
Residency sits underneath all of it. If your organization is a critical information infrastructure operator or a high-volume handler, the Cybersecurity Law’s Article 39 (formerly Article 37) requires personal information generated in China to be stored in the mainland — a duty no offshore moderation service can meet. And high volumes of image and video data can raise the “important data” (重要数据) question under the Data Security Law, which makes a CAC data-export security assessment (数据出境安全评估) mandatory before anything leaves. Which doors apply, and in what combination, depends on your sector, your data volumes and your role as handler.
Calling the API isn’t the question — compliant in-country processing is
Because Hive is a cloud moderation service operated from the United States with no mainland-China region and no customer-run, in-country build, you cannot localize the data by relocating the product: there is nothing in the mainland to provision, and moving between offshore locations only relocates the transfer, it does not end it. The lawful shape is therefore to keep the moderation of China-collected content on an in-country footing — a China-resident processing path or a China-legal domestic alternative — send out of the country only what may lawfully leave, minimize and obtain the Article 29 separate consent for the sensitive content, handle any Article 24 automated-decision and important-data duty, and treat any China-facing surface — the upload page, the community, the trust-and-safety or verification flow — as a public service that carries an ICP filing duty and needs compliant, in-country delivery. That is a residency-and-delivery design, not a matter of making an offshore API load faster, and never a hidden path that ships the content offshore anyway.
None of this is a verdict that Hive is “blocked” or “illegal.” Whether a given image or piece of UGC is sensitive personal information or “important data” turns on what you process and your sector — a blank form or a landscape photo is not an ID card or a face — and whether you owe a separate consent, a transfer mechanism, in-country storage, a data-export assessment, an Article 24 explanation, an ICP filing, or some combination depends on your entity, your volumes and who your users are. Settle the specifics with counsel before your China community depends on it.
The lawful path — map, localize, deliver
There is a compliant way to run content moderation for a China operation, and it has a shape. First, map: our China team inventories what you send Hive — which images, video, text, audio and UGC your China users generate — which of it is sensitive personal information (faces and other biometrics, ID and financial-account numbers in uploaded documents), where it is processed (a United States region, with no mainland-China option), the cross-border and Article 28/29 consent basis, whether any of it is “important data,” and whether you make an Article 24 automated decision when you enforce. The legal conclusions are settled with counsel; we build the technical picture that feeds them.
Then localize: because Hive offers no mainland region or customer-run build to localize onto, we help you keep the moderation of China content on a China-resident footing — a consented, in-country processing path, or a China-legal domestic moderation service where that is the right fit — so the China content and China personal data stay resident and stop leaving the country by default, while you keep Hive for your other markets. We minimize what crosses the border, obtain the Article 29 separate consent for the sensitive content, and handle any important-data and data-export-assessment duty, so that what leaves is only what may lawfully leave. Localize means keeping the content on an in-country path — never a tunnel that ships it offshore anyway.
Then deliver: the China-facing surfaces — the upload page, the community, the moderated feed, the verification flow — are a public service in the mainland, so they carry an ICP filing (备案) duty and need compliant, in-country delivery. 21YunBox delivers them in-country — the 21YunBox Optimizer — set in front of what you already run, with no rebuild and no re-platform, so your mainland users reach the service reliably on ICP-filed infrastructure. The result is a moderation and community stack that runs legally and compliantly for your users in China. 21YunBox never uses or suggests circumvention of any kind — we localize what must stay, deliver the rest compliantly from inside the mainland, and never move personal information across the border by stealth.
Related reading:
- China’s Personal Information Protection Law (sensitive data, Articles 24, 28, 29)
- Cross-border data transfers under PIPL
- China’s data-export security assessment measures
- How to get an ICP filing for China


