Does Amazon Rekognition Work in China? PIPL Cross-Border, Data Residency & Sensitive-Data Rules
Amazon Rekognition is AWS's computer-vision service for face detection, face comparison, identity verification, and content moderation — and AWS offers it in no mainland-China region. So the images and video your China operation sends it to analyze are themselves personal information, often biometric (faces), processed offshore: a PIPL cross-border transfer of sensitive personal data. A compliance-first look at the residency, sensitive-data, and cross-border exposure.
Does Amazon Rekognition work in China?
The images and video your China operation sends Amazon Rekognition to analyze are themselves the personal information — and when they contain faces, that content is biometric data, the most sensitive kind — and AWS offers Rekognition in no mainland-China region, so analyzing them is a PIPL cross-border transfer of sensitive personal data.
Rekognition detects and compares faces, runs face-liveness identity checks, and moderates user-generated images and video; the face or depicted person you transmit cannot be minimized or anonymized, because it is the identifier — PIPL Article 28 sensitive personal information. Sending it to a service hosted abroad is a cross-border transfer (Articles 38–40, with the Article 29 separate consent for sensitive data), an automatic pass/fail or flag/remove is automated decision-making under Article 24, and facial recognition carries its own 2025 national rules in China. The lawful lever is to keep the image and face processing in-country, minimize what crosses the border, obtain the separate consent, and ICP-file any China-facing surface — not to make the offshore API reachable.
Whether a given image or face is sensitive or “important data” turns on what you process and your sector — a risk to settle with counsel. Our China team can map your exposure →
What Amazon Rekognition's own documentation says about China
| Fact | Primary source |
|---|---|
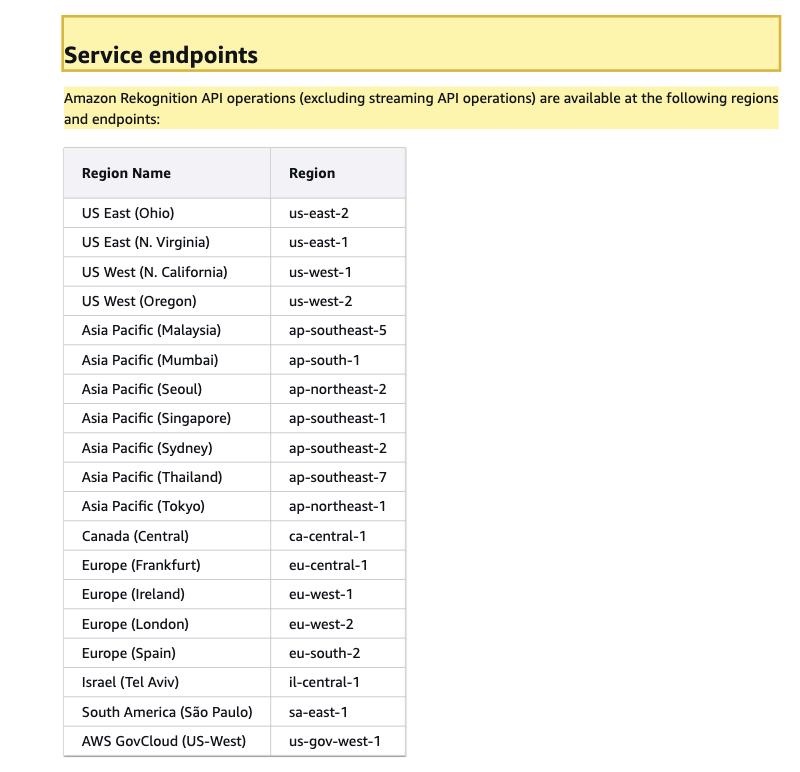
| Amazon Rekognition runs in no mainland-China AWS region. AWS's endpoints and quotas page lists where “Amazon Rekognition API operations (excluding streaming API operations) are available” — regions across the US, Europe, the Asia-Pacific, Canada, Israel, South America, and AWS GovCloud (US) — with no Beijing (cn-north-1) or Ningxia (cn-northwest-1) endpoint, and AWS lists no on-premises or self-managed edition. Images and video collected in China are therefore analyzed offshore. | AWS, “Amazon Rekognition endpoints and quotas,” AWS General Reference (docs.aws.amazon.com), retrieved 2026-10-11 |
| The content you send Rekognition is faces and user-generated media — the personal information itself. AWS describes Rekognition as a service that can “Detect faces appearing in images and videos” and “Detect potentially unsafe, inappropriate, or unwanted content across images and videos,” and it offers face comparison and face-liveness identity verification. A face is biometric data; it cannot be anonymized before transfer because it is exactly what the service was asked to recognize. | AWS, “Amazon Rekognition” product page (aws.amazon.com), retrieved 2026-10-11 |
| Faces are sensitive personal information under PIPL Article 28. China's Personal Information Protection Law classes biometric data — alongside financial accounts and national-ID numbers — as sensitive personal information, which may be processed only with a specific separate consent, a prior personal-information protection impact assessment, and strict necessity. See PIPL (Article 28). Facial recognition also carries dedicated 2025 national rules in China, layered on top of PIPL. | 21YunBox, “China Personal Information Protection Law (PIPL),” Article 28 (21cloudbox.com), retrieved 2026-10-11 |
| Analyzing China-collected images offshore is a PIPL cross-border transfer by you, the handler. Sending personal information outside the mainland engages PIPL Articles 38–40 — notice, a transfer mechanism (a CAC security assessment, the CAC standard contract, or certification), and, reinforced for sensitive data by Article 29, a separate consent — and, for a CIIO or high-volume handler, the Cybersecurity Law's in-country storage duty. See cross-border data transfers under PIPL. | 21YunBox, “Cross-Border Data Transfers under PIPL” (21cloudbox.com), retrieved 2026-10-11 |
Sources verified by the 21YunBox compliance team on 2026-10-11.
For a China operation running Amazon Rekognition, the question is not whether the API answers a call from Shanghai. It is that the images and video you send Rekognition to analyze are the personal information — and when they contain faces, that content is biometric data, the most sensitive kind Chinese law recognizes. Rekognition is AWS’s managed computer-vision service: it detects and compares faces, runs face-liveness identity checks, and moderates user-generated media. It runs only in AWS’s global regions and GovCloud (US); the AWS China partition — Beijing (Sinnet) and Ningxia (NWCD) — does not offer it, so images collected in China are analyzed offshore. A face cannot be anonymized — it is the identifier; sending it abroad is a cross-border transfer under PIPL (Articles 38–40, plus the Article 29 separate consent); an automatic approve/deny or flag/remove is automated decision-making (Article 24); and any China-facing surface carries an ICP duty.
Amazon Rekognition in China at a glance
| What decides it | In Amazon Rekognition's own terms — and China's law |
|---|---|
| What you send it | Rekognition analyzes images and video you upload or stream to it — AWS describes it as a service to “Detect faces appearing in images and videos” and to “Detect potentially unsafe, inappropriate, or unwanted content across images and videos.” That content is the personal information: user photos, uploaded identity or selfie images, and user-generated media. When an image shows a face, what you sent is biometric data — sensitive personal information under PIPL Article 28. |
| Where it runs | Rekognition is a managed cloud API available only in AWS's global commercial regions and GovCloud (US). AWS's own China partition — Beijing, operated by Sinnet, and Ningxia, operated by NWCD — does not offer Rekognition, and there is no self-managed or on-premises edition. So images and video collected from a China operation are analyzed offshore. For a China operation, that is a cross-border transfer (数据出境) of personal information under PIPL Articles 38–40. |
| The sensitive-data door | A face is biometric data, and biometrics — alongside financial accounts and national-ID numbers — are sensitive personal information under PIPL Article 28: a separate consent, a prior impact assessment, and strict necessity. You cannot minimize or anonymize a face, because it is the identifier you sent the image to recognize. Facial recognition is also specifically regulated in China under dedicated 2025 rules, on top of PIPL. |
| Automated decisions + residency | Where Rekognition decides an outcome — a face-liveness identity check that passes or fails a user, a moderation call that flags or removes content — that is automated decision-making under PIPL Article 24, which lets the individual refuse a decision made solely by automation. For a critical information infrastructure operator or high-volume handler, Cybersecurity Law Article 39 (formerly Article 37) requires China-collected personal information to be stored in China; large or sensitive volumes can add a CAC data-export security assessment. |
| Reachability is not the axis | Whether the Rekognition endpoint answers quickly from the mainland is an operational matter, not the compliance question. What decides it is where the images and faces are processed — offshore, or on an in-country path. 21YunBox maps the exposure, helps you localize the vision processing in-country, obtain the Article 29 separate consent, and delivers any China-facing surface compliantly on ICP-filed infrastructure. |
What you actually send it — and why the content is the risk
Amazon Rekognition is a computer-vision API: you hand it an image or a video frame and it returns an analysis. AWS groups the capabilities as face detection and analysis (“Detect faces appearing in images and videos”), face compare and search, face-liveness identity verification (“Verify identity online”), and content moderation (“Detect potentially unsafe, inappropriate, or unwanted content across images and videos”). In every one of them, the thing you transmit out of your environment to be read is the personal information itself — and frequently the most sensitive kind.
The sharp cases follow the feature set. A face-comparison or face-search call sends a human face, which is biometric data. A face-liveness or identity-verification flow sends a live selfie of a real person, often alongside an identity document. A content-moderation call ships user-generated images and video — other people’s faces, bodies and expression — out for review. None of it can be de-identified before it leaves, because the face or the depicted person is exactly what the service was asked to analyze. And Rekognition runs only in AWS’s global commercial regions and GovCloud (US): there is no AWS China region for it and no on-premises or self-managed edition, so for a China operation the processing happens offshore unless you put it on an in-country path.
The doors: sensitive personal data, cross-border transfer, and automated decisions
Once China-collected images and faces leave the mainland to be analyzed, several bodies of law decide whether they were allowed to. The faces and the people depicted in what you send are personal information under China’s Personal Information Protection Law; a face is biometric data, which Article 28 treats as sensitive personal information, requiring a separate, specific consent, a prior personal-information protection impact assessment, and strict necessity. There is no “minimize first” escape here, because the biometric identifier is the input. Facial recognition carries its own dedicated regime in China as well — the 2025 national rules on the application of facial-recognition technology (in force June 1, 2025) — layered on top of PIPL for any face-recognition use.
Sending that content to a service hosted abroad is a cross-border transfer (数据出境), and PIPL puts the duty on you, the handler — not on AWS. Articles 38–40 require notice, a transfer mechanism (a CAC security assessment, the CAC standard contract, or certification), and — reinforced for sensitive data by Article 29 — a separate consent. Where Rekognition decides an outcome automatically, such as a pass/fail identity check or a flag/remove moderation call, Article 24 governs that automated decision-making and lets the individual refuse a decision made solely by automation. At volume, image and video data can raise the “important data” question under the Data Security Law, which can make a CAC data-export security assessment mandatory before anything leaves; and for a critical information infrastructure operator or high-volume handler, the Cybersecurity Law’s Article 39 (formerly Article 37 — the data-localization provision was renumbered by the 2025 amendment that took effect on January 1, 2026, with its substance unchanged) requires China-collected personal information to be stored in China. Which of these bite your deployment turns on what you process and your sector.
Calling the API isn’t the question — compliant in-country processing is
The fix is not to make an offshore endpoint reachable — it is to put the image and face processing where the law needs it. Because Rekognition offers no AWS China region and no self-managed edition, localizing means keeping the China vision workload on an in-country path: a China-resident processing arrangement, or a China-legal domestic alternative for the face and moderation work, with only what may lawfully leave crossing the border. That is localization in the real sense — keeping the data on an in-country path — never a tunnel that ships the images offshore anyway. Minimize what you send, obtain the Article 28/29 separate consent and the Article 13/23 notice, and handle any Article 24 automated-decision duty. Any China-facing surface that calls the service — an upload page, a KYC or identity-verification flow, a moderated community — is an internet information service served in the mainland, so it carries an ICP filing (备案) duty bound to a mainland hosting resource, plus compliant in-country delivery. None of this is a verdict that Rekognition is “blocked” or “illegal” in China — whether a given image or face is sensitive or “important data” turns on what you process and your sector, so it is a residency-and-exposure map, not a ruling; settle the specifics with counsel before your China operations depend on it.
The lawful path — map, localize, deliver
There is a compliant way to run computer vision and content moderation for a China operation, and it has a shape. First, map: our China team inventories what you send Rekognition — the images and video, which of it is sensitive (faces and other biometrics, identity documents), where it is processed today, the cross-border and Article 28/29 consent basis each transfer needs, whether any of it is “important data,” and whether the service makes an automated decision under Article 24. The legal conclusions are settled with counsel; we build the technical picture that feeds them.
Then localize: we help you keep the China image and face processing in-country — on a China-resident processing path or a China-legal domestic alternative — so the biometric and user-generated content your mainland operation collects stops leaving the country by default, while only what may lawfully cross the border does. We minimize what you send, and help you obtain the Article 28/29 separate consent and the required notice. Localize means keeping the data on an in-country path, never moving it offshore by stealth.
Then deliver: any China-facing surface on top of the stack — an upload page, an identity-verification flow, a moderated community — needs compliant, in-country delivery and carries an ICP filing duty. 21YunBox delivers it in-country — the 21YunBox Optimizer — in front of what you already run, with no rebuild and no re-platform. The result is a vision and moderation footprint that runs legally and compliantly for your users in China. 21YunBox never uses or suggests circumvention of any kind — we keep in-country what the law says must stay, deliver the rest compliantly from inside the mainland, and never move personal information across the border by stealth.
Related reading:
- China’s Personal Information Protection Law (PIPL)
- Cross-border data transfers under PIPL
- China’s data-export security assessment (CAC)
- How to get an ICP filing for China


