Does Dayforce Work in China? Employee & Payroll Data Residency, PIPL Cross-Border & Sensitive PI
Dayforce (formerly Ceridian) HCM is reachable from mainland China, so speed is not the question — employee-data residency is. Dayforce is US-headquartered and publishes no mainland-China data region, and its own privacy statement routes personal information through EU, UK, Swiss and US transfer mechanisms only, so your China employees' payroll, benefits and biometric clock-in records rest in an offshore tenant — a cross-border transfer of often-sensitive personal information under PIPL. A compliance-first look at the residency, cross-border, sensitive-PI and ICP exposure, and the lawful in-country path.
Does Dayforce work in China?
Dayforce's applications are reachable from mainland China, so the honest answer is that speed is not the question. Dayforce is your workforce's system of record — pay, hours, benefits, and on its time clocks fingerprints and faces — and the China decision turns on where those employee records live and whether they were allowed to leave the country.
Dayforce (formerly Ceridian) is US-headquartered, and its own privacy statement routes personal information through EU, UK, Swiss and US transfer mechanisms only, publishing no mainland-China data region — so your China staff's records rest in an offshore tenant, which makes keeping them there a cross-border transfer (数据出境) of personal information under PIPL (Articles 38–40): notice, a transfer mechanism, and a separate consent that is especially fraught for employee data. Much of what Dayforce holds — pay, bank and benefits details, and the finger-, vein- and face-scan data its clocks can capture — is sensitive personal information (Articles 28–29), raising the consent bar and requiring an impact assessment, and above volume thresholds a data-export security assessment may apply. For a critical information infrastructure operator, the Cybersecurity Law's Article 39 (formerly Article 37) requires in-country storage an offshore region cannot meet.
21YunBox maps your cross-border, residency and sensitive-PI exposure, localizes the China employee data onto a China-resident footing (sending Dayforce only what may lawfully leave), and delivers any China-facing employee surface in-country on ICP-filed infrastructure — no rebuild, and never any form of circumvention. Treat the specifics as a risk to confirm with counsel.
What Dayforce's own documentation says about China
| Fact | Primary source |
|---|---|
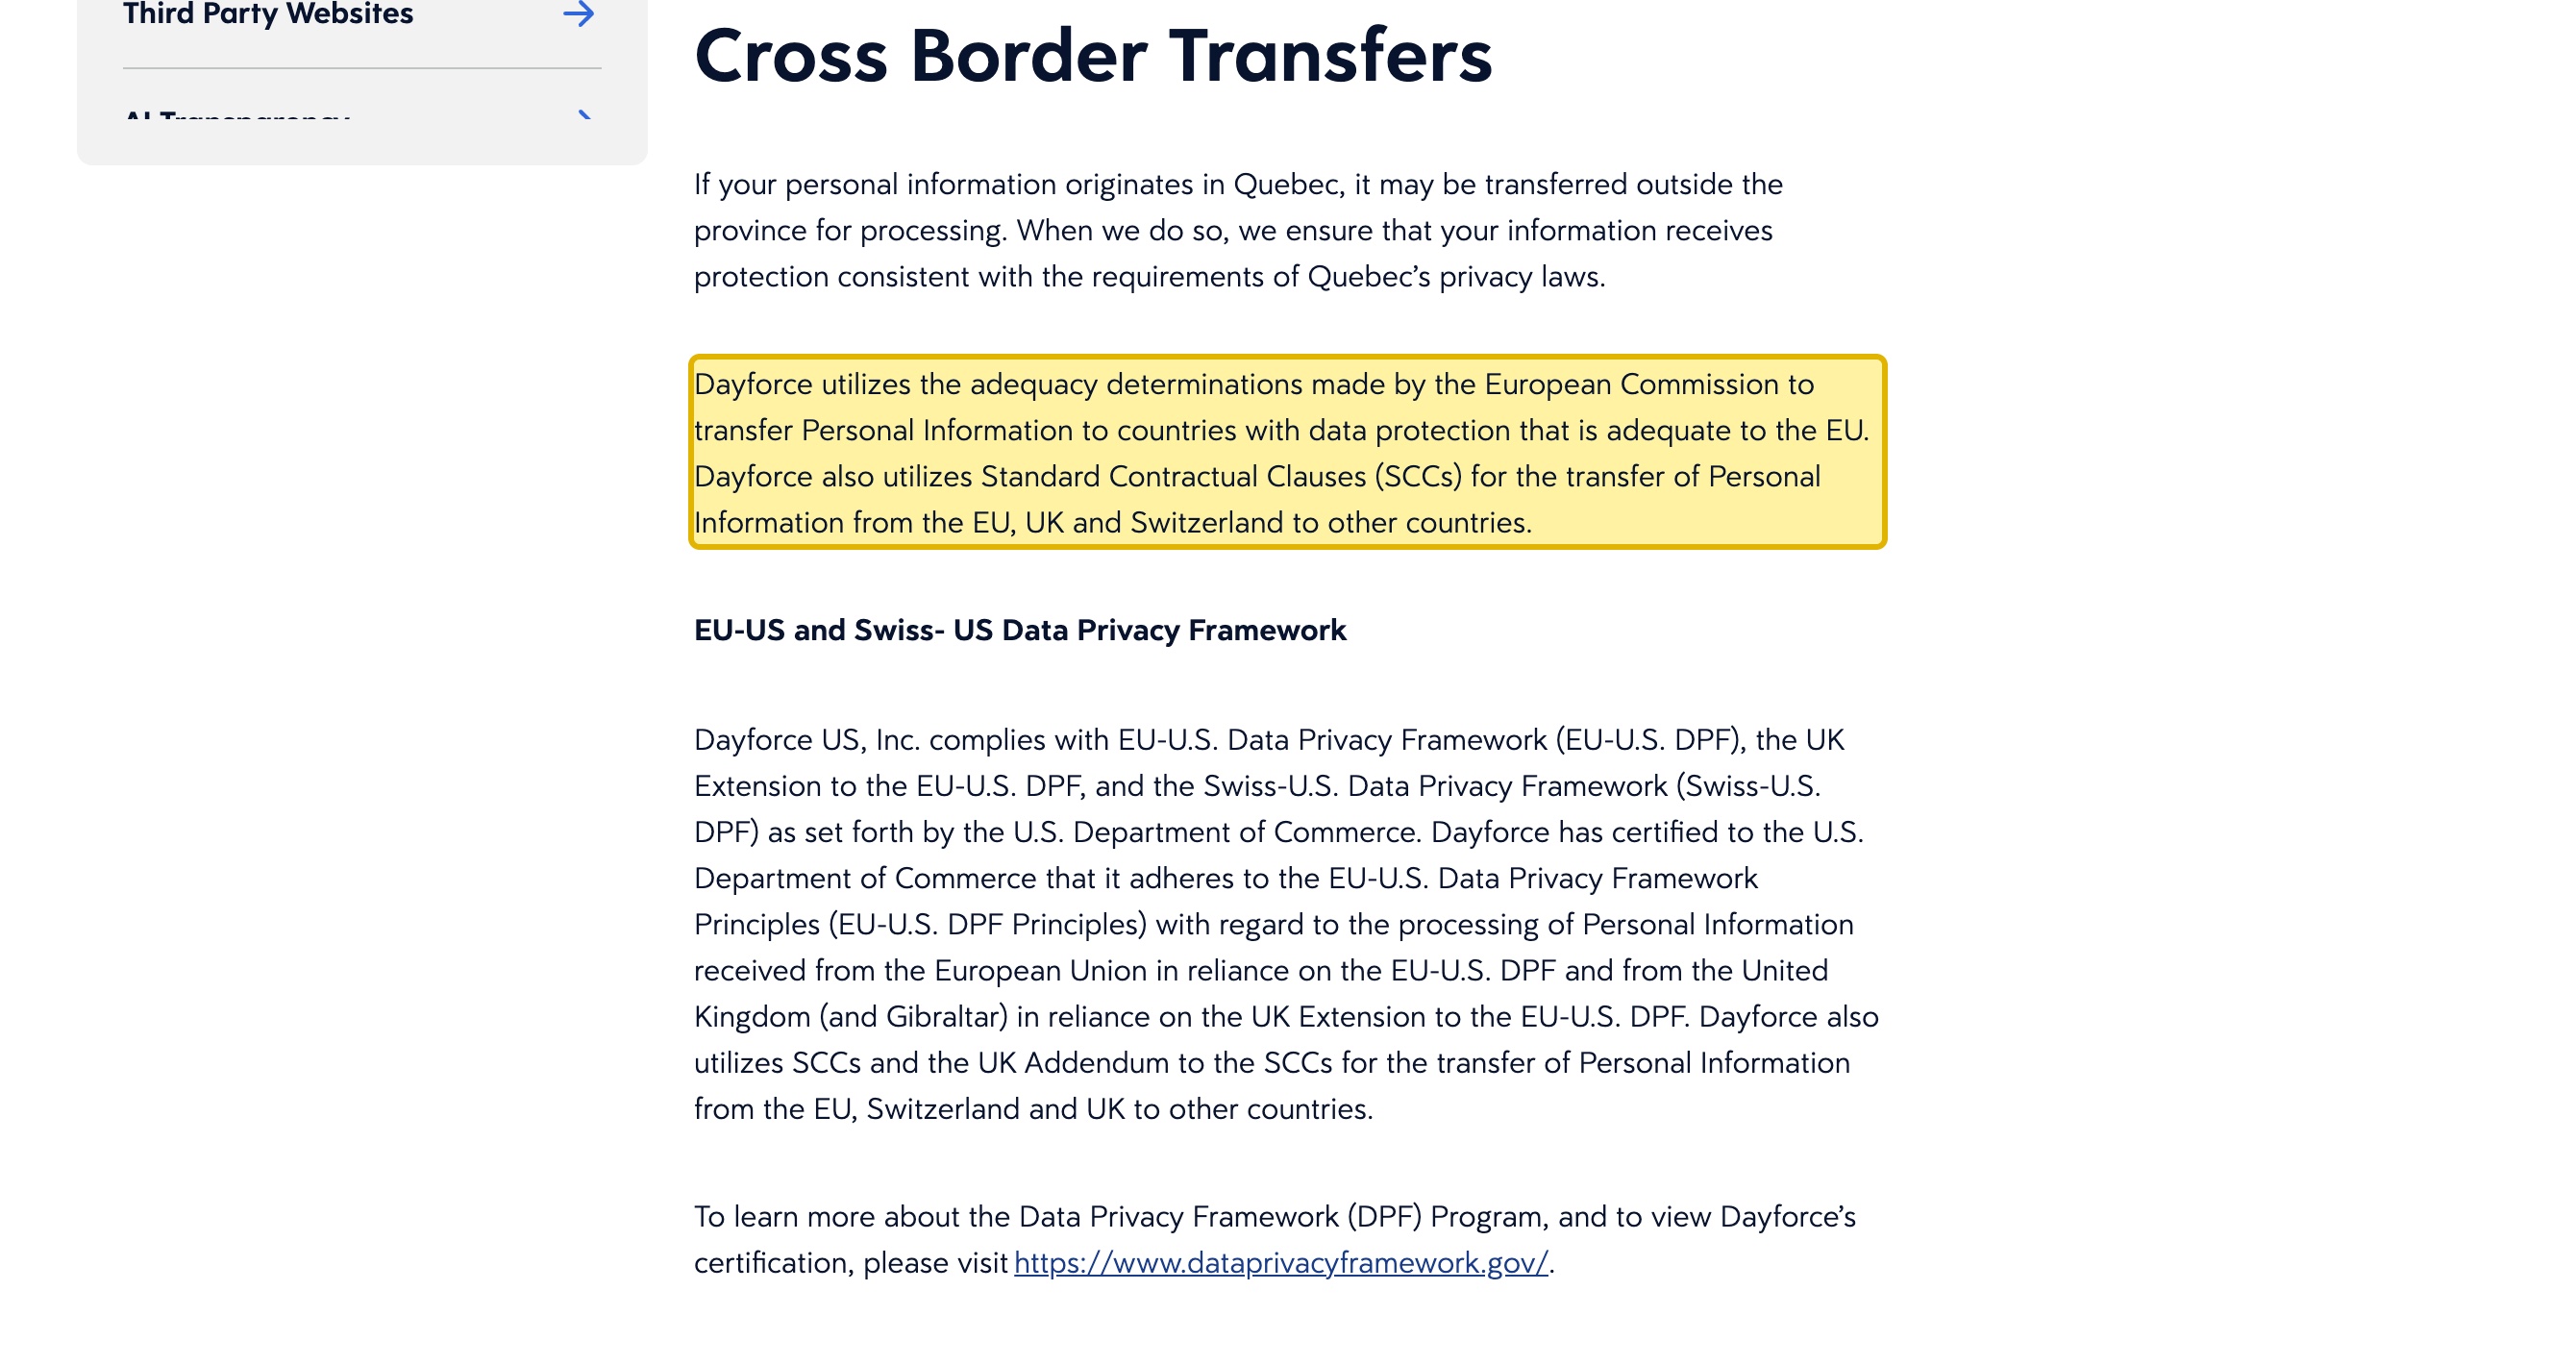
| Dayforce's own privacy statement builds its cross-border transfer framework on Western mechanisms only — none for mainland China. Under "Cross Border Transfers," Dayforce relies on the "adequacy determinations made by the European Commission," on Standard Contractual Clauses "for the transfer of Personal Information from the EU, UK and Switzerland to other countries," and states that "Dayforce US, Inc. complies with EU-U.S. Data Privacy Framework (EU-U.S. DPF)." It publishes no mainland-China data region and names no China transfer mechanism, so the records of your China staff rest in an offshore Dayforce tenant — a cross-border transfer of personal information under PIPL. | Dayforce — Global Privacy Statement, Cross Border Transfers (dayforce.com/privacy, last updated 2026-09-11), retrieved 2026-10-09 |
| Dayforce's time clocks can capture finger-, vein- and face-scan data — expressly sensitive personal information — and Dayforce puts the compliance call on you. Its Biometric Statement applies to timekeeping using "finger scan, vein scan, and facial recognition technology," says "Dayforce processes biometric data only on behalf of and at the direction of its customers," and that "It is the responsibility of Dayforce's customers to determine if applicable data protection and biometric privacy laws apply." Under PIPL, biometrics are sensitive personal information (Articles 28–29), requiring a specific purpose, a separate consent and a prior impact assessment. | Dayforce — Biometric Statement (dayforce.com/privacy/biometric-notice, last updated 2026-10-07); PIPL Articles 28–29, retrieved 2026-10-09 |
| Holding China employees' records in an offshore Dayforce tenant triggers PIPL's cross-border rules — with an employee-consent problem built in. Moving personal information collected from staff in mainland China to a tenant hosted abroad engages PIPL Articles 38–40: notice, one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification), and, where consent is the basis, a separate consent that is hard to treat as freely given inside an employment relationship. The duty falls on the handler — the employer — not on Dayforce as processor. | Personal Information Protection Law of the PRC, Articles 38–40 (cac.gov.cn), retrieved 2026-10-09 |
| For some handlers the data must stay in China, and switching Dayforce regions does not change that. For a critical information infrastructure operator or large-volume handler, personal information generated in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)), and a CAC data-export security assessment may apply before anything leaves. Every region Dayforce offers sits outside mainland China, so moving a tenant from one offshore region to another relocates the transfer rather than ending it. | PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37); Measures for the Security Assessment of Data Exports (cac.gov.cn), retrieved 2026-10-09 |
Sources verified by the 21YunBox compliance team on 2026-10-09.
For a payroll and workforce platform, whether Dayforce “works” in mainland China is settled by where your employees’ records are allowed to live, long before it is a question of how quickly a screen paints. Dayforce is the system that holds your people’s pay, hours, benefits and reporting lines — and, on its time clocks, their fingerprints and faces — and its applications answer from the mainland. So the decision is not reachability. It is whether the personal information of your China-based staff may lawfully rest in a Dayforce tenant hosted outside the country, and on what basis it crossed the border to get there. Dayforce (formerly Ceridian) is headquartered in the United States, and its own privacy statement describes a cross-border transfer framework built entirely on Western mechanisms — with no mainland-China data region in it.
Dayforce in China at a glance
| What decides it | In Dayforce's own terms — and China's law |
|---|---|
| What it is | Dayforce (formerly Ceridian) is a cloud HCM, payroll and workforce-management platform — the system of record for hiring, pay, time and attendance, benefits and scheduling. It keeps a continuous, identifiable record of every worker, much of it sensitive. |
| Is it reachable from the mainland? | Yes. Dayforce's applications answer from China and it is not a service blocked at the border, so reachability is not the China question. (Cross-border access to an offshore tenant can be uneven — an operational matter, below, not the decision.) |
| Where do the employee records live? | Outside mainland China. Dayforce is US-headquartered and publishes no mainland-China data region; its privacy statement rests on EU, UK, Swiss and US transfer mechanisms. Your China staff's records therefore sit in an offshore Dayforce tenant. |
| Putting China employee data into it | Those records are personal information, and holding them in an offshore tenant is a cross-border transfer (数据出境) under PIPL (Articles 38–40): notice, a transfer mechanism, and — where consent is the basis — a separate consent that an employee can rarely give freely to an employer. |
| Pay, benefits and biometric clock-in | Compensation, bank and benefits data, and the finger-, vein- and face-scan data Dayforce's own time clocks can capture, are sensitive personal information under PIPL (Articles 28–29): a specific purpose, a separate consent and a prior personal-information protection impact assessment. |
| In-country storage & volume | For a critical information infrastructure operator or large-volume handler, employee data generated in China must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)), and a CAC data-export security assessment may apply before anything leaves — duties an offshore Dayforce region cannot meet. |
| The lawful path | Keep the China employee data that must stay on a China-resident footing, send Dayforce only what may lawfully leave, keep Dayforce for the rest of your workforce, and serve any China-facing employee portal in-country on ICP-filed infrastructure. 21YunBox maps, localizes and delivers; it never uses or suggests circumvention of any kind. |
Reachable — but where do your employees’ records live?
Dayforce’s applications answer from inside China, and it is not a service China blocks at the border, so reachability is not where this is settled. Residency is. Dayforce is US-headquartered, and nowhere in its published security or privacy material does it name a mainland-China data center; its Information Security page offers only that “Dayforce maintains relevant industry certifications and attestations including ISO and SOC 2 Type II,” with no in-country region named. Its Global Privacy Statement then sets out a transfer framework resting on European Commission adequacy findings, Standard Contractual Clauses, and the EU-U.S., UK and Swiss-U.S. Data Privacy Frameworks — every one of them a Western mechanism. So unless and until that changes, the system-of-record data for your China employees sits in an offshore Dayforce tenant.
Cross-border access from the mainland to an offshore tenant can be uneven, and the temptation is to force the connection through. 21YunBox does neither that nor anything like it — the answer is never a network workaround, which is both a compliance risk and beside the point. For the same reason this page publishes no China latency figure for Dayforce: speed is not the axis for a decision that turns on residency and consent. The productive question is where the employee data rests and whether it had a lawful basis to be there.
Employee data offshore is a cross-border transfer under PIPL
Here is the gate most HR and payroll teams miss. Collecting personal information from staff in mainland China and keeping it in a Dayforce tenant hosted abroad is a cross-border transfer (数据出境) of personal information under the Personal Information Protection Law. PIPL places the duty on the personal-information handler — the employer, not Dayforce, which processes the data on the employer’s instructions: Articles 38–40 call for notice, one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification), and, where consent is your basis, a separate consent for sending the records overseas.
Employment makes that consent awkward. PIPL does let an employer process staff personal information where it is necessary to administer human resources under a lawfully adopted labor policy, so routine HR processing need not always rest on consent — but exporting those records to an offshore Dayforce tenant is a separate act that engages the cross-border rules in their own right, and a separate consent is seldom something an employee can withhold without cost. Recent CAC rules ease some human-resources transfers out of the heaviest assessment route, yet they do not switch off the underlying duties of notice, a lawful basis and a transfer mechanism. And for a critical information infrastructure operator or a large-volume handler, personal information generated in China must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37 — the data-localization provision renumbered by the 2025 amendment that took effect on January 1, 2026, with its substance unchanged)), and moving employee data across the border above volume thresholds can trigger China’s data-export security assessment (数据出境安全评估) before anything leaves. Which of these bind your organization is a risk to confirm with counsel against your actual headcount and data.
Biometric clock-in data is sensitive — a higher bar
What sharpens the exposure for Dayforce, beyond pay and performance, is the time clock. Dayforce’s own Biometric Statement says the document covers timekeeping that uses “finger scan, vein scan, and facial recognition technology,” and that “Dayforce processes biometric data only on behalf of and at the direction of its customers.” Under PIPL, biometric characteristics are sensitive personal information (Articles 28–29): processing them demands a specific purpose and strict necessity, a separate consent, and a prior personal-information protection impact assessment (Article 55) — and pay, bank and benefits records carry the same sensitive-PI bar. Dayforce is explicit about where the compliance call sits: “It is the responsibility of Dayforce’s customers to determine if applicable data protection and biometric privacy laws apply” to how the devices are used. That is the handler’s duty, and in China it is a demanding one, because moving sensitive employee data across the border above volume thresholds can additionally bring a data-export security assessment into play. None of this turns on how fast a page renders; it turns on whether sensitive data had a lawful basis to be abroad — so treat every line here as a matter to settle with counsel before you rely on it.
Why pointing Dayforce at another region isn’t the fix
The obvious move is to flip the tenant to a different Dayforce region and call the job done — but every region Dayforce runs sits outside mainland China. Relocating China employee data from a US environment to a European one moves the cross-border transfer; it does not close it, and it does not create the in-country home a residency duty requires. Keeping China-collected employee data in the country means standing up a China-resident footing for the records that must stay, and sending Dayforce only what may lawfully leave. Deciding which records must stay and which may go is a legal question before it is a technical one, and it is the heart of the work.
The lawful path — map, localize, deliver
There is a lawful way to run Dayforce for a workforce that includes mainland China, and it has a shape. First, map: our China compliance team works through your PIPL picture — which employee, payroll and biometric records collected in China have to stay in the country, what may lawfully cross the border, where a data-export security assessment or an Article 39 (formerly Article 37) storage duty applies, and what your notice, consent and impact-assessment flow must cover. The legal conclusions are settled with your counsel; we build the technical map that feeds them.
Then localize: we stand up and integrate a China-resident footing for the China employee data that must remain — a consented, in-country home for those records, biometric templates included — while Dayforce stays the system of record for the rest of your workforce, receiving only what may lawfully leave.
Then deliver: any China-facing surface of the system — an employee self-service portal, an onboarding or recruiting page actually served to people in the mainland — is a public service there, so it carries an ICP filing (备案) duty and needs compliant, in-country delivery. The 21YunBox Optimizer delivers it in-country, in front of the stack you already run, with no rebuild and no re-platform. What we never do — and what no one lawfully can — is hand you a way around China’s data-export rules or around any network restriction: we localize what must stay and deliver in-country, so your workforce system runs legally and compliantly for your people in China.
Related reading:
- Cross-border data transfers under PIPL
- China’s data-export security assessment
- China’s Cybersecurity Law (data localization, Article 39)
- How to get an ICP filing for China


