Does Workiva Work in China? Financial Disclosure Data, MNPI, PIPL & Data Residency
Workiva hosts its connected reporting and disclosure platform in four AWS data locations — the United States, Ireland, Japan and Canada — with none in mainland China. So the pre-release filings, consolidated results and named-preparer records your China entity feeds in rest offshore, making their collection a PIPL cross-border transfer. A compliance-first look at the residency, MNPI and sensitive-data exposure — and the lawful, in-country path.
Does Workiva work in China?
Workiva opens from the mainland, but it hosts customer data only in offshore AWS locations — the US, Ireland, Japan and Canada, none in mainland China — so using it for a China entity is a data-residency and PIPL cross-border question, not a speed one.
Workiva is the system of record for un-released SEC filings and financial statements — material non-public information before it is public — plus the identities and review trails of the named preparers who build them and the personal data inside the documents. Feeding China-collected records into a US, Ireland, Japan or Canada AWS location is a cross-border transfer under PIPL needing notice, a separate consent and a transfer mechanism; financial identifiers can be sensitive personal information, and a CIIO owes in-country storage under the Cybersecurity Law (Article 39, formerly Article 37).
Which duties bite is a question to settle with counsel against what you actually collect. Our China team can map your exposure →
What Workiva's own documentation says about China
| Fact | Primary source |
|---|---|
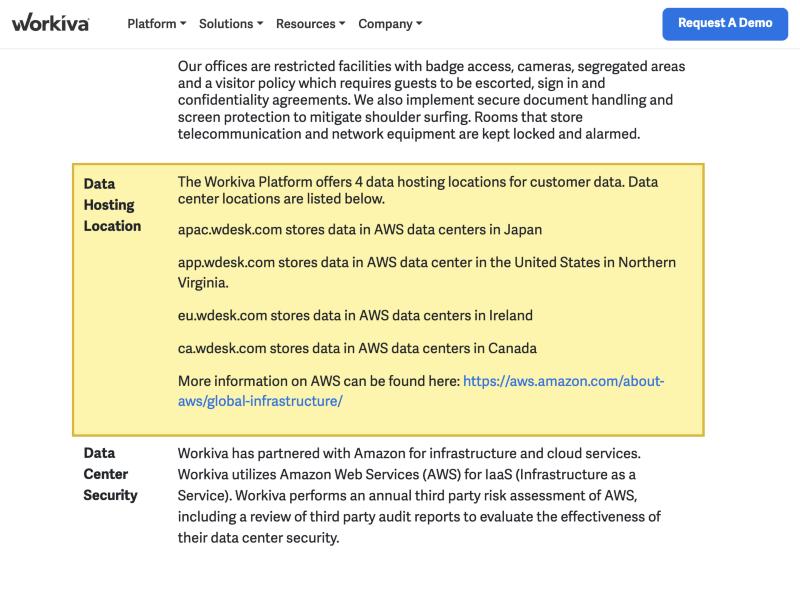
| Workiva hosts customer data in four AWS locations, none in mainland China. Its security page states that "The Workiva Platform offers 4 data hosting locations for customer data" and that "Workiva utilizes Amazon Web Services (AWS)" — AWS data centers reached at app.wdesk.com (United States, Northern Virginia), eu.wdesk.com (Ireland), apac.wdesk.com (Japan) and ca.wdesk.com (Canada). | Workiva Security page, Data Center and Physical Security (retrieved 2026-10-10) |
| Each Workiva tenant is bound to one offshore region selected at provisioning. The platform runs on distinct regional instances — apac.wdesk.com (Japan), app.wdesk.com (United States), eu.wdesk.com (Ireland) and ca.wdesk.com (Canada) — with data replicated across "multiple availability zones within your selected region." The closest option to China, Japan, is still outside the mainland, and Workiva offers no on-premises or in-country deployment. | Workiva Security page, Data Hosting Location / Availability and Continuity (retrieved 2026-10-10) |
| Holding China-collected personal information offshore is a cross-border transfer under PIPL. Articles 38–40 require notice, a separate consent, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification — before personal information collected in China may rest in a US, Ireland, Japan or Canada region. See cross-border data transfers and the data-export security assessment. | PIPL Articles 38–40; CAC Measures on the Standard Contract and Security Assessment |
| A critical information infrastructure operator must store China-generated personal information in China. The Cybersecurity Law data-localization duty sits at Article 39 (formerly Article 37) — the 2025 amendment in force January 1, 2026 renumbered it, substance unchanged — which an offshore AWS region cannot meet. Financial identifiers inside filings can be sensitive personal information under PIPL Article 28. | Cybersecurity Law Article 39 (formerly Article 37); PIPL Article 28 |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a company that builds its SEC filings, statutory reporting, ESG, SOX and audit work in Workiva for a China entity, the reflex is to ask whether the platform opens quickly, or at all, from the mainland. That is the wrong place to start. Workiva is a hosted connected-reporting platform — the Workiva Platform, reached at app.wdesk.com — and what actually decides whether you can use it in China is where the records it holds come to rest: the un-released financial statements and regulatory filings that are material non-public information before they are published, the review trails and identities of the named preparers and reviewers who assemble each filing, and the personal data sitting inside the documents themselves. Workiva’s own security page is clear about where that data lives — four AWS data locations, in the United States, Ireland, Japan and Canada, none in mainland China. That makes using it for China a data-residency and cross-border question under China’s law, not a speed one.
Workiva in China at a glance
| What decides it | In Workiva's own terms — and China's law |
|---|---|
| Where the records live | Offshore. Workiva's security page states it “utilizes Amazon Web Services (AWS)” and that “The Workiva Platform offers 4 data hosting locations for customer data” — app.wdesk.com (United States, Northern Virginia), eu.wdesk.com (Ireland), apac.wdesk.com (Japan) and ca.wdesk.com (Canada). There is no mainland-China location; the nearest, Japan, is still outside the mainland. |
| What it holds & why it's personal (and sensitive) | Workiva is the working system of record for un-released financial statements and regulatory filings — material non-public information before it is public — plus the comments, tasks and identities of the named preparers and reviewers who build each number, and the personal data inside the documents (named officers, signatories, compensation). That is identifiable personal information, and financial-account and similar identifiers can be sensitive personal information under PIPL Article 28. |
| Putting China data into it = cross-border | When records collected in China land in a US, Ireland, Japan or Canada AWS location, you have made a cross-border transfer (数据出境) under PIPL (Articles 38–40): notice, a separate consent distinct from any general agreement to use the platform, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. |
| In-country storage duty | A critical information infrastructure operator or high-volume handler owes in-country storage under Cybersecurity Law Article 39 (formerly Article 37) — a duty an offshore AWS region cannot meet. At volume, or where data counts as “important data,” a data-export security assessment (PIPL Article 40) may be required before anything leaves. |
| Reachable is not the axis | Workiva is a SaaS your preparers open over the public internet; whether someone in Shanghai can load app.wdesk.com is not the China question — where the filings rest is. Any China-facing surface around it (an intake or data-collection site, a disclosure portal) is a public service in the mainland and carries an ICP filing (备案) duty of its own. |
No mainland region, so your filings leave the country
Workiva’s security page settles where the data sits. It states that “Workiva utilizes Amazon Web Services (AWS) for IaaS (Infrastructure as a Service) and PaaS (Platform as a Service),” that “Our office locations have no data centers or access to data centers,” and that “The Workiva Platform offers 4 data hosting locations for customer data.” Those four are AWS data centers reached through distinct regional instances — apac.wdesk.com in Japan, app.wdesk.com in the United States (Northern Virginia), eu.wdesk.com in Ireland, and ca.wdesk.com in Canada — with data replicated across “multiple availability zones within your selected region.” None of the four is in mainland China; the nearest, Japan, is still offshore. So the filings, consolidated results and preparer records your China operations enter into Workiva are held outside the mainland.
The moment personal information collected in China lands in one of those AWS locations, you have made a cross-border transfer (数据出境) under China’s Personal Information Protection Law. PIPL puts the duty on the handler — you, Workiva’s customer, not Workiva the processor: Articles 38–40 require notice, a separate consent, and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. Above the regulated thresholds, or where the records amount to “important data,” the transfer may first require China’s data-export security assessment (数据出境安全评估) before anything leaves. And if your organization is a critical information infrastructure operator, the Cybersecurity Law’s Article 39 (formerly Article 37 — the data-localization clause was renumbered by the 2025 amendment that took effect on January 1, 2026, with its substance unchanged) requires that personal information generated in China be stored in China, a duty an offshore AWS region cannot discharge. Which of these bite your deployment is a question to settle with counsel against what you actually collect and where your preparers and officers sit.
Un-released filings and preparer records are personal information — and more
Reporting data is not neutral traffic. A Workiva workspace is the place a filing is drafted, reviewed and signed off, so it concentrates two kinds of exposure at once. First, it carries personal information: the named officers and signatories inside the documents, executive-compensation and ownership detail, and — because Workiva’s whole value is multi-user collaboration with an audit trail — a record of which individuals prepared, edited, commented on and reviewed each number. Under PIPL that is personal information, and financial-account and similar identifiers can be sensitive personal information (敏感个人信息), which requires a specific purpose and a showing of necessity, a separate consent, and a personal-information protection impact assessment beforehand — obligations that stack on top of the cross-border duties, not in place of them.
Second, and distinctively for a disclosure platform, much of what sits in Workiva is un-released results and draft filings — material non-public information before publication. MNPI is a securities-governance concern rather than a PIPL category, but it sharply raises the stakes of holding the data offshore: you are concentrating a China entity’s most price-sensitive, pre-disclosure records in a region outside Chinese jurisdiction and reachable under another country’s legal process. Workiva’s security controls — AES-256 encryption at rest, TLS 1.2/1.3 in transit, and certifications such as SOC 1, SOC 2 Type II and ISO 27001 — genuinely reduce security risk, but they do not change where the data rests or discharge the consent, necessity and residency duties, which sit with you as the personal-information handler. Whether a given field is sensitive, and what your notice and consent flow must say, are questions to confirm with counsel.
Narrowing the exposure doesn’t close the door
The instinct is to engineer the problem down: provision the China entity’s instance in the Japan region because it is the closest on the list, redact or minimize what gets fed in, or self-host the platform in China. Each lever changes what crosses the border, not that it crosses. Japan, like the US, Ireland and Canada locations, sits outside the mainland, so choosing it relocates the same cross-border transfer to a different offshore country rather than resolving any data-localization duty. Data minimization genuinely shrinks the volume and sensitivity of what you export, which is worth doing — but it does not make an offshore region a China-resident one. And self-hosting is not on the table here: Workiva is a cloud-only service on AWS, with no on-premises, client-managed or in-country deployment option, so there is no configuration of the product itself that places China-collected records on mainland soil. Keeping those records in-country means standing up a China-resident footing alongside Workiva and sending offshore only what may lawfully leave; any China-facing surface around the stack still carries an ICP filing duty. Drawing that line — what must stay, what may go — is a legal question before it is a technical one, and this page maps exposure rather than rendering a verdict: settle the specifics, and whether a data-export security assessment or an Article 39 storage duty applies to you, with your counsel against your actual data and entity.
The lawful path — map, localize, deliver
There is a compliant way to run connected reporting for a China operation, and it has three moves. First, map: our China team works through your PIPL exposure end to end — which filing data, preparer records and personal information collected in China must stay in the country, what may lawfully cross to Workiva, where a data-export security assessment or an Article 39 storage duty applies, which fields are sensitive, and what your consent and notice must cover. The legal conclusions are settled with counsel; we build the technical picture that feeds them.
Then localize: we help stand up and integrate a China-resident footing for the China filing, consolidation and preparer data — a lawful pattern of consented, in-country processing and storage — so the records that must stay in China stop leaving it by default, while you keep Workiva for the markets and group-level reporting where it already serves you.
Then deliver: the China-facing surfaces around your reporting stack — a data-collection or subsidiary-submission site, a disclosure portal, the integration edge your mainland preparers actually reach — are public services in the mainland, so they carry an ICP filing (备案) duty and need compliant, in-country delivery. 21YunBox delivers them in-country — the 21YunBox Optimizer — in front of what you already run, with no rebuild and no re-platform. 21YunBox is a compliant overlay, not a migration, and a partner to Workiva rather than a competitor. 21YunBox never uses or suggests circumvention of any kind. The result is a reporting stack that runs legally and compliantly for your users in China.
Related reading:
- Cross-border data transfers under PIPL
- China’s data-export security assessment
- China’s Cybersecurity Law (data localization, Article 39)
- How to get an ICP filing for China


