Does Simpplr Work in China? PIPL Cross-Border, Data Residency & Employee-Data Rules
Simpplr is an AI intranet and employee-experience platform hosted on AWS and Salesforce in US and EU regions, with no mainland-China region — so your China workforce's directory, profiles and internal communications sit offshore, a PIPL cross-border transfer, and its engagement and usage analytics profile your China employees under Article 24. A compliance-first look at the residency, employee-data and automated-decision exposure.
Does Simpplr work in China?
Your China workforce's employee personal information and your internal content sit on Simpplr's offshore cloud — hosted on AWS and Salesforce in the US and EU regions, with no mainland-China region — a PIPL cross-border transfer, and the platform profiles your China employees under Article 24.
Simpplr is an AI intranet and employee-experience platform: it concentrates the whole workforce — the employee directory and profiles, internal communications, employee engagement and listening, and the engagement and usage analytics built on top. Running it for a China operation holds that employee personal information offshore, a PIPL cross-border transfer under Articles 38–40 (with Article 13/23 consent to collect it), and the analytics that score your China employees raise the Article 24 automated-decision and profiling duty. The lawful lever is to keep the employee data and internal content in-country, handle the profiling duty, and ICP-file any China-facing surface — not to make the offshore platform reachable.
Whether your internal content is "important data" and which duties bite turn on your sector and workforce — settle the specifics with counsel. Our China team can map your exposure →
What Simpplr's own documentation says about China
| Fact | Primary source |
|---|---|
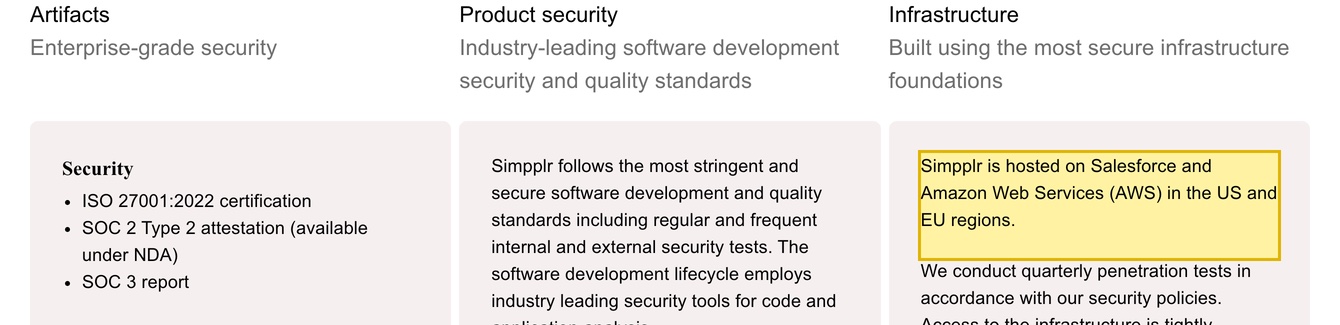
| Simpplr runs on AWS and Salesforce in US and EU regions — with no mainland-China region. Its Security & Compliance page states it is "hosted on Salesforce and Amazon Web Services (AWS) in the US and EU regions," and its customer-selectable deployment locations span the US, EU, Switzerland, UK, Canada, Australia, New Zealand, Brazil and India — none in mainland China, and there is no China sovereign-cloud partition. | Simpplr — Security & Compliance (retrieved 2026-10-11) |
| Simpplr holds your whole China workforce and profiles it. By its own security page it "captures personal data to provide functionality (such as access control, notifications, and analytics)" and "also captures usage and performance data" — across the employee directory, profiles, internal communications and engagement. The analytics that score and rank individuals are the sharp point, not whether the app loads. | Simpplr — Security & Compliance (retrieved 2026-10-11) |
| Running Simpplr for a China workforce is a PIPL cross-border transfer of employee personal information. PIPL Articles 38–40 require notice, a transfer mechanism (a CAC security assessment, the CAC standard contract, or certification) and a separate consent before employee data leaves the mainland, on top of the Article 13/23 notice-and-consent to collect it. | PIPL Articles 38–40, 13, 23 (21YunBox) — retrieved 2026-10-11 |
| Scoring your China employees with engagement analytics is automated decision-making under PIPL Article 24. Where profiling informs a decision about an individual, the person may refuse a decision made solely by automated means; and for a CIIO or high-volume handler, Cybersecurity Law Article 39 (formerly Article 37) requires China-generated personal information to be stored in China. | PIPL Article 24; Cybersecurity Law Article 39 (21YunBox) — retrieved 2026-10-11 |
Sources verified by the 21YunBox compliance team on 2026-10-11.
For a company running Simpplr for a mainland-China operation, the question is not whether the intranet loads from Shanghai. It is where your China workforce’s employee personal information and your internal content live — and the fact that the platform profiles those employees. Simpplr is an AI intranet and employee-experience platform: it concentrates the whole workforce — the employee directory and profiles, internal communications, employee engagement and listening, and the analytics built on top. By its own security page, Simpplr is “hosted on Salesforce and Amazon Web Services (AWS) in the US and EU regions,” and its customer-selectable deployment locations span the US, EU, UK, Canada, Australia and other countries — none in mainland China. So for a China operation that data sits offshore: a PIPL cross-border transfer of employee personal information (Articles 38–40), on top of the Article 13/23 consent to collect it. The engagement and usage analytics that score your employees raise Article 24; your internal content raises a residency and “important data” question; a CIIO or high-volume handler faces in-country storage; and any China-facing surface it serves carries an ICP filing.
Simpplr in China at a glance
| What decides it | In Simpplr's own terms — and China's law |
|---|---|
| What it holds | An AI intranet and employee-experience platform: your internal content (company communications and newsfeed, knowledge articles, documents, recognition and survey responses) and your whole workforce — the employee directory and profiles, plus the engagement and usage analytics the platform records about each person. The content is company data; the directory, profiles and engagement records are employee personal information. |
| Where it runs | Hosted on Salesforce and Amazon Web Services (AWS) in the US and EU regions, with customer-selectable deployment locations in the US, EU, Switzerland, UK, Canada, Australia, New Zealand, Brazil and India — none in mainland China, and no China sovereign-cloud partition. For a China operation, holding your workforce's data there is a cross-border transfer (数据出境) of employee personal information under PIPL Articles 38–40. |
| The automated-decision door | Simpplr does not just store your workforce — it profiles it: engagement scores, adoption and usage analytics, who-read-what. Where that profiling informs a decision about an individual, it is automated decision-making under PIPL Article 24, and the person may refuse a decision made solely by automated means. This is the half a reachability review misses: the platform is watching and scoring your China employees, offshore. |
| Employee-PII + internal-content residency | Collecting your China employees' data needs the Article 13/23 notice-and-consent. For a critical information infrastructure operator or high-volume handler, Cybersecurity Law Article 39 (formerly Article 37 — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged) requires China-generated personal information to be stored in China. Internal content at volume or in a sensitive sector can be treated as "important data" (重要数据) with its own export controls. |
| Reachability is not the axis | Whether Simpplr loads quickly from the mainland is an operational matter, not the compliance question. What decides it is where your China workforce's employee data and internal content live, and that the platform profiles those employees. 21YunBox keeps the employee data and internal content on a lawful in-country path, handles the Article 24 profiling duty, and delivers any China-facing surface with an ICP filing — in front of the stack you already run. |
What it actually holds — your internal content and your people’s data
Simpplr is where a company’s employees go to work and to hear from the company. As an intranet and employee-experience platform it holds two kinds of data that matter for China. The first is your internal content: the newsfeed and company communications, knowledge articles and documents, recognition posts, and the employee-listening and survey responses people submit — company material that is sometimes confidential and can carry other people’s personal information. The second, and the sharper one, is your workforce itself: the employee directory and profiles an intranet is built around, and the activity the platform records about each person. Simpplr’s own security page says it “captures personal data to provide functionality (such as access control, notifications, and analytics)” and “also captures usage and performance data.” All of it runs on Simpplr’s cloud — hosted on Salesforce and AWS in the US and EU regions, with customer-selectable deployment locations in the US, EU, Switzerland, UK, Canada, Australia, New Zealand, Brazil and India. None of those locations is in mainland China, and there is no China sovereign-cloud partition, so for a China operation your whole workforce’s data is held offshore.
The doors: employee personal data, cross-border transfer, and automated decisions
Once your China workforce’s data is held in an offshore region, a separate body of law decides whether it was allowed to go there. The directory, profiles, communications and engagement records Simpplr holds about your China employees are personal information under China’s Personal Information Protection Law — ordinary personal information, in the main, not the sensitive category, but personal information all the same. Collecting it requires the Article 13/23 notice-and-consent; holding it on a platform with no mainland-China region makes running Simpplr a cross-border transfer (数据出境), and PIPL Articles 38–40 put the duty on you, the handler — notice, a transfer mechanism (a CAC security assessment, the CAC standard contract, or certification), and a separate consent for the transfer.
The distinctive door here is the one a reachability review never opens. Simpplr does not merely store your employees; it profiles them — engagement scores, adoption and usage analytics, who-read-what, the “analytics and insights” the platform is sold on. Where that profiling informs a decision about an individual — a readiness or engagement ranking, a targeted nudge — it is automated decision-making under PIPL Article 24, which lets the person refuse a decision made solely by automated means and requires that profiling offer an option not targeted at their personal characteristics. Analytics over a China workforce also sit against China’s employee-monitoring and labor norms. On residency, if your organization is a critical information infrastructure operator or a high-volume handler, Cybersecurity Law Article 39 (formerly Article 37) requires personal information generated in China to be stored in China — a duty an offshore platform cannot meet. And at volume, or in a sensitive sector, internal content can be treated as “important data” under the Data Security Law, which adds its own export controls. Which of these bite your case turns on your sector, your workforce and your data volumes.
Logging in isn’t the question — compliant in-country employee data is
The fix is not to make an offshore Simpplr reachable from the mainland — reachability was never the question, and Simpplr loads from China like any global SaaS. It is to put your China workforce’s data where the law needs it. Keep the China employee personal information and internal content on an in-country path — a China-resident or sovereign-cloud path, or a China-legal domestic alternative — with data minimization, so the directory, profiles, communications and engagement records of your China employees stay inside the country and only what may lawfully leave crosses the border. Obtain the Article 13/23 notice-and-consent, handle any Article 24 automated-decision and profiling duty and its opt-out, and classify whether any internal content is “important data.” Then any China-facing surface the platform serves — a public knowledge base, an external help center or microsite — is an internet information service in the mainland, so it carries an ICP filing (备案) duty and needs compliant, in-country delivery. None of this is a verdict that Simpplr is “blocked” or “illegal” in China; it is a residency-and-exposure map, and whether your internal content is “important data,” and which duties bite, turns on your sector and workforce — worth settling the specifics with counsel before your China operations depend on it.
The lawful path — map, localize, deliver
There is a compliant way to run an employee-experience platform for a China operation, and it has a shape. First, map: our China team inventories the employee personal information Simpplr holds about your China workforce — the directory, profiles, internal communications, and the engagement and usage analytics — and your internal content; establishes where each is processed and stored today (an offshore region, with no China partition); whether the platform profiles individuals under Article 24; the consent and cross-border basis each transfer needs; and whether any content is “important data.” We build the technical picture; the legal conclusions are settled with counsel.
Then localize: we help you keep the China employee data and internal content in-country — on a China-resident or sovereign-cloud path, or a China-legal domestic alternative — with minimization, obtain the Article 13/23 consent, and handle the Article 24 profiling duty and its opt-out. Localize means keeping the data on an in-country path, never a tunnel that ships it offshore anyway.
Then deliver: any China-facing surface on top of the platform — a public knowledge base, an external help center — needs compliant, in-country delivery and carries an ICP filing duty. 21YunBox delivers it in-country — the 21YunBox Optimizer — in front of what you already run, with no rebuild and no re-platform. The result is an employee experience that runs legally and compliantly for your users in China. 21YunBox never uses or suggests circumvention of any kind — we keep in-country what the law says must stay, deliver the rest compliantly from inside the mainland, and never move personal information across the border by stealth.
Related reading:
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law
- China’s Personal Information Protection Law (PIPL)
- How to get an ICP filing for China


