Does SailPoint Work in China? Identity-Governance Data Residency, PIPL Cross-Border & the Data-Resident Path
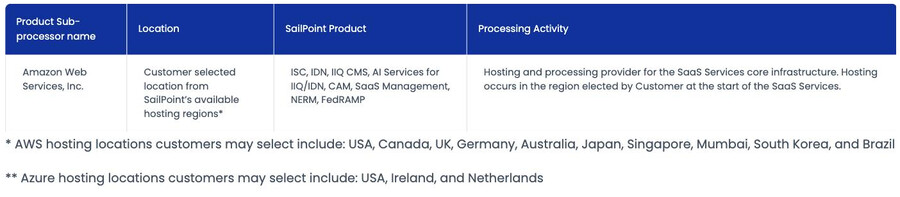
SailPoint Identity Security Cloud (formerly IdentityNow) is reachable from mainland China, so the deciding question isn't speed — it's data residency and cross-border personal information. SailPoint's own sub-processor page says SaaS hosting occurs in the region the customer elects, and the AWS regions it offers (USA, Canada, UK, Germany, Australia, Japan, Singapore, Mumbai, South Korea, Brazil) include none in mainland China — so the workforce identities, entitlement inventories and access-review records it holds for your China employees rest offshore: a PIPL cross-border transfer, with a Cybersecurity Law Article 39 (formerly Article 37) residency duty for CII operators. The data-resident path is a self-managed IdentityIQ deployment, or a domestic IGA for the China entity, on China-resident infrastructure.
Does SailPoint work in China?
Yes — SailPoint Identity Security Cloud (formerly IdentityNow) is reachable from mainland China, so the honest answer is that reachability is not the problem. What decides the China question for an identity-governance platform is data residency and cross-border personal information.
SailPoint offers no mainland-China hosting region. Its own Sub-processors page states SaaS “Hosting occurs in the region elected by Customer,” and the AWS regions it lists — USA, Canada, UK, Germany, Australia, Japan, Singapore, Mumbai, South Korea, and Brazil — include none in the mainland. So the workforce identities, entitlement inventories, and access-review records it holds for your China employees rest offshore, which makes their collection a cross-border transfer (数据出境) under PIPL — requiring notice, a separate consent, and a transfer mechanism — and it may trigger China's data-export security assessment. For a critical information infrastructure operator, the Cybersecurity Law's Article 39 (formerly Article 37) requires such data to be stored in China, which no offshore SailPoint region can satisfy.
21YunBox maps your cross-border and residency exposure, localizes the China-resident identity-governance data onto an in-country footing — a self-managed IdentityIQ deployment or a domestic IGA — and delivers any China-facing surface in-country on ICP-filed infrastructure, with no rebuild, and never any form of circumvention. Treat the specifics as a risk to confirm with counsel.
What SailPoint's own documentation says about China
| Fact | Primary source |
|---|---|
| SailPoint hosts its SaaS in the region the customer elects — and the list of regions includes none in mainland China. SailPoint's Sub-processors page states, for its SaaS core infrastructure on AWS, that “Hosting occurs in the region elected by Customer at the start of the SaaS Services,” and a footnote lists the choices: “AWS hosting locations customers may select include: USA, Canada, UK, Germany, Australia, Japan, Singapore, Mumbai, South Korea, and Brazil.” | SailPoint, “Sub-processors” (sailpoint.com/legal/sub-processors), retrieved 2026-10-09 |
| SailPoint's own region announcement confirms nine global points of presence — and data stays within its region, not in the mainland. SailPoint's November 27, 2024 Mumbai-region release describes Mumbai as its “ninth point of presence globally,” alongside Frankfurt, London, Tokyo, Singapore, Sydney, Montreal, and both US-West and East Regions, and states that a tenant is “completely isolated” so that “no data will be replicated, backed up, or stored in any other AWS Region.” None of the nine is in mainland China. | SailPoint press release, “SailPoint now runs on AWS through the AWS Asia Pacific (Mumbai) Region,” November 27, 2024 (retrieved 2026-10-09) |
| Identity-governance data is personal information, so an offshore SailPoint tenant is a PIPL cross-border transfer. The workforce identities, account and entitlement inventories, and access-review and certification records SailPoint holds for your China employees are personal information; moving them into a tenant hosted outside the mainland triggers PIPL Articles 38–40 — notice, a separate consent, and one transfer mechanism (a CAC security assessment, the CAC standard contract, or certification). The duty sits with you, the handler, not SailPoint the processor. | Personal Information Protection Law of the PRC, Articles 38–40 (cac.gov.cn), retrieved 2026-10-09 |
| For a critical information infrastructure operator, China-collected identity data must be stored in China. The Cybersecurity Law's Article 39 (formerly Article 37 — renumbered by the 2025 amendment in force January 1, 2026, its substance unchanged) requires personal information generated in China to be stored in the mainland — an in-country storage duty an offshore SailPoint region cannot meet. SailPoint's self-managed IdentityIQ, by contrast, is customer-hosted, so an in-country deployment is a lawful, data-resident footing. | Cybersecurity Law of the PRC, Article 39 (formerly Article 37), 2025 amendment in force 2026-01-01 (cac.gov.cn), retrieved 2026-10-09 |
Sources verified by the 21YunBox compliance team on 2026-10-09.
For a company that runs SailPoint to govern who inside the organization may reach which systems, the mainland-China question rarely turns on whether the console loads. SailPoint Identity Security Cloud — the SaaS formerly called IdentityNow — is callable from inside China, so reachability is not where the decision is made. What settles it is residency and cross-border transfer. An identity-governance platform exists to hold a precise, continuous record of your workforce: who each person is, which accounts and entitlements they hold, who approved that access and when it was last certified. For your China-based employees, that record is personal information — and where SailPoint keeps it, and whether it was lawful to move it there, is a question China’s law answers before performance ever enters the frame. SailPoint settles the first half of that question in its own documentation.
SailPoint in China at a glance
| What decides it | In SailPoint's own terms — and China's law |
|---|---|
| What it is | SailPoint is an identity governance and administration (IGA) platform. Identity Security Cloud (the SaaS, formerly IdentityNow) and the self-managed IdentityIQ hold your workforce identities, account and entitlement inventories, and the access-review and certification records that document who may reach which systems — a continuous, identifiable record of your employees. |
| Is it reachable from the mainland? | Yes. Identity Security Cloud is callable from inside China and is not a service blocked at the border, so reachability is not the China question. (Cross-border traffic to an offshore tenant can be inconsistent — an operational matter, not the decision, and never a reason for a network workaround.) |
| Where does the identity-governance data sit? | Offshore. SailPoint's own sub-processor page states SaaS “Hosting occurs in the region elected by Customer,” and lists the AWS regions a customer may select — USA, Canada, UK, Germany, Australia, Japan, Singapore, Mumbai, South Korea and Brazil. None is in mainland China, and SailPoint states that “no data will be replicated, backed up, or stored in any other AWS Region.” |
| Collecting China workforce data into it | The identities, entitlement inventories and access-review records are personal information. Holding them in an offshore tenant is a cross-border transfer (数据出境) under PIPL (Articles 38–40): notice, a separate consent, and one transfer mechanism. A data-export security assessment may apply above thresholds, and access-review data — a map of who can reach what — is operationally sensitive. For a critical information infrastructure operator, Cybersecurity Law Article 39 (formerly Article 37) sets an in-country storage duty an offshore region cannot meet. |
| The data-resident path | Keep China-resident identity-governance data in-country — a self-managed IdentityIQ deployment on China-resident infrastructure, or a domestic IGA for the China entity — with consented in-country processing and storage, and deliver any China-facing surface in-country on ICP-filed infrastructure. 21YunBox maps, localizes and delivers; it never uses or suggests circumvention of any kind. |
Reachable — but where does the identity-governance data live?
SailPoint’s position is set in its own documentation, not by a load-time test. Its Sub-processors page describes the SaaS core infrastructure running on AWS, where “Hosting occurs in the region elected by Customer at the start of the SaaS Services,” and a footnote names the choices: “AWS hosting locations customers may select include: USA, Canada, UK, Germany, Australia, Japan, Singapore, Mumbai, South Korea, and Brazil.” There is no mainland-China option on that list — the nearest selections, in Japan, Singapore and South Korea, are all outside the mainland. SailPoint’s November 2024 announcement of its Mumbai region tells the same story from the other side: it counted Mumbai as its “ninth point of presence globally,” alongside Frankfurt, London, Tokyo, Singapore, Sydney, Montreal and two United States regions, and stated that each tenant’s data is “completely isolated” so that “no data will be replicated, backed up, or stored in any other AWS Region.”
So “can the SailPoint tenant be reached from Shanghai?” is the wrong test. It can be reached. The real question is where your China-collected identity-governance data comes to rest, and whether it was lawful to move it there at all. For that reason this page publishes no first-party China latency or reachability figure for SailPoint: speed is not the axis for a decision that turns on residency and consent. One operational note worth naming — cross-border traffic from the mainland to an offshore tenant can be inconsistent, and the temptation is to force it through a network workaround. 21YunBox neither uses nor suggests any such circumvention; it is both a compliance risk and beside the point. The productive question is how to keep the China identity data on a lawful footing.
An identity-governance record is workforce personal information — kept offshore
Here is the structural point. SailPoint’s whole job is to hold a precise, continuous record of your workforce and its access — the accounts each employee holds, the entitlements behind them, the approvals and the periodic certifications that prove the access was reviewed. For your employees in mainland China, every field of that record is personal information, and much of it is operationally sensitive: an access-review export is, in effect, a map of who inside your organization can reach which systems. The moment that record lives in a SailPoint tenant hosted in the US, the EU or any of the other offshore regions SailPoint offers, you have made a cross-border transfer of personal information under China’s Personal Information Protection Law.
PIPL puts the duty on the handler — you, the employer, not SailPoint the processor. Articles 38–40 require notice, a separate consent distinct from any general employment or system-use agreement, and one transfer mechanism: a CAC security assessment, the CAC standard contract, or certification. Above certain thresholds, or where the data counts as “important data,” that transfer may also require China’s data-export security assessment (数据出境安全评估) before anything leaves. And if your organization is a critical information infrastructure operator, the Cybersecurity Law’s Article 39 (formerly Article 37 — the data-localization provision was renumbered by the 2025 amendment that took effect on January 1, 2026, with its substance unchanged) requires that personal information generated in China be stored in China — an in-country storage duty an offshore SailPoint region cannot satisfy. None of this turns on how quickly a certification campaign renders; it turns on whether the data had a lawful basis to be where it is. Which of these bite your specific deployment is a risk to confirm with counsel against what you actually govern and store.
Why switching SailPoint regions isn’t the fix
The obvious move is to pick a different region and keep the data in-region — but the only regions SailPoint offers its SaaS are the ten its sub-processor page lists, and not one of them is in mainland China. Moving a China workforce’s identity-governance data from a US tenant to a Singapore or Tokyo tenant merely relocates the cross-border transfer; it does not end it, and none of those regions resolves a China residency duty. Keeping China-collected identity data in-country means standing up a China-resident footing for it: SailPoint’s self-managed IdentityIQ, deployed on China-resident infrastructure you or a local operator control, or a domestic IGA adopted for the China entity — with the SaaS kept for the markets where it already serves you. That split — what must stay in China, what may lawfully leave — is the heart of the work, and it is a legal question before it is a technical one.
This is a risk map, not a verdict: whether you owe separate consent, a transfer mechanism, in-country storage, a data-export assessment, or some combination depends on your data volumes, your role as handler, and whose identities you govern — worth settling with counsel before you rely on it.
The lawful path — map, localize, deliver
There is a lawful way to run identity governance for a China presence, and it has a shape. First, map: our China team works through your PIPL exposure for the workforce identity data SailPoint holds — which identities, entitlement inventories and access-review records collected in China must stay in the country, what may lawfully leave, where a data-export security assessment or an Article 39 storage duty bites, and what your consent and notice flow has to cover. The legal conclusions are settled with counsel; we build the technical picture that feeds them.
Then localize: we stand up and integrate a China-resident footing for the China identity-governance data — a self-managed IdentityIQ deployment on China-resident infrastructure, or a domestic IGA for the China entity — so the governance you depend on keeps working while that data stops leaving the country by default, and you keep Identity Security Cloud for the regions where it already serves you.
Then deliver: the China-facing surface that authenticates against it — the access-request and self-service portal your employees actually open — is itself a service reached inside the mainland, so it carries an ICP filing (备案) consideration and needs compliant, in-country delivery. 21YunBox delivers it in-country — the 21YunBox Optimizer — in front of what you already run, with no rebuild and no re-platform. The result is identity governance that runs legally and compliantly for your users in China. What we never do — and what no one lawfully can — is hand you a route around China’s data-export rules or around any network restriction: we localize what must stay and deliver in-country, and we never move personal information out of China by stealth.
Related reading:
- Cross-border data transfers under PIPL
- China’s data-export security assessment
- China’s Cybersecurity Law (data localization, Article 39)
- How to get an ICP filing for China


