Does Persona Work in China? Identity-Verification Data Residency, PIPL Sensitive PI & ICP
Persona's identity-verification flow is reachable on the wire, so the real question isn't speed — it's that a KYC check collects exactly what PIPL treats as sensitive personal information: a government ID and a facial-biometric selfie. Persona's own documentation runs its platform from the United States, the EU and India with no mainland-China region, so every Chinese applicant's ID image and face scan it stores is a cross-border transfer of sensitive personal information under PIPL — carrying a stricter separate-consent and impact-assessment load, an in-country storage duty under the Cybersecurity Law for a CIIO or large-volume handler, and no footing for an ICP filing. A compliance-first look at the sensitive-PI, residency, cross-border and ICP exposure, and the lawful in-country path.
Does Persona work in China?
Reaching Persona isn't the problem — what it collects is. A KYC check gathers a government ID and a facial-biometric selfie, the two things China's law treats most strictly, and Persona holds them offshore.
By Persona's own documentation its platform runs from the United States, the EU and India, and its Security Statement offers data residency in the US (default) or the EU only — no mainland-China region. So every ID scan, ID number and face selfie it captures from a Chinese applicant is sensitive personal information (PIPL Article 28) that leaves the mainland — a cross-border transfer PIPL governs that needs a separate consent, a transfer mechanism and a prior impact assessment (Articles 29, 38–40, 55–56), with a data-export security assessment more readily in play and, for a CIIO or large-volume handler, an in-country storage duty under Cybersecurity Law Article 39 (formerly Article 37). A China-facing onboarding screen served from the mainland also needs an ICP filing Persona has no resource to attach.
This is a risk map, not a verdict — what you owe turns on your entity, the data you hold, your role as handler and who your applicants are, and it's worth settling with counsel. Our China team can map your exposure with you →
What Persona's own documentation says about China
| Fact | Primary source |
|---|---|
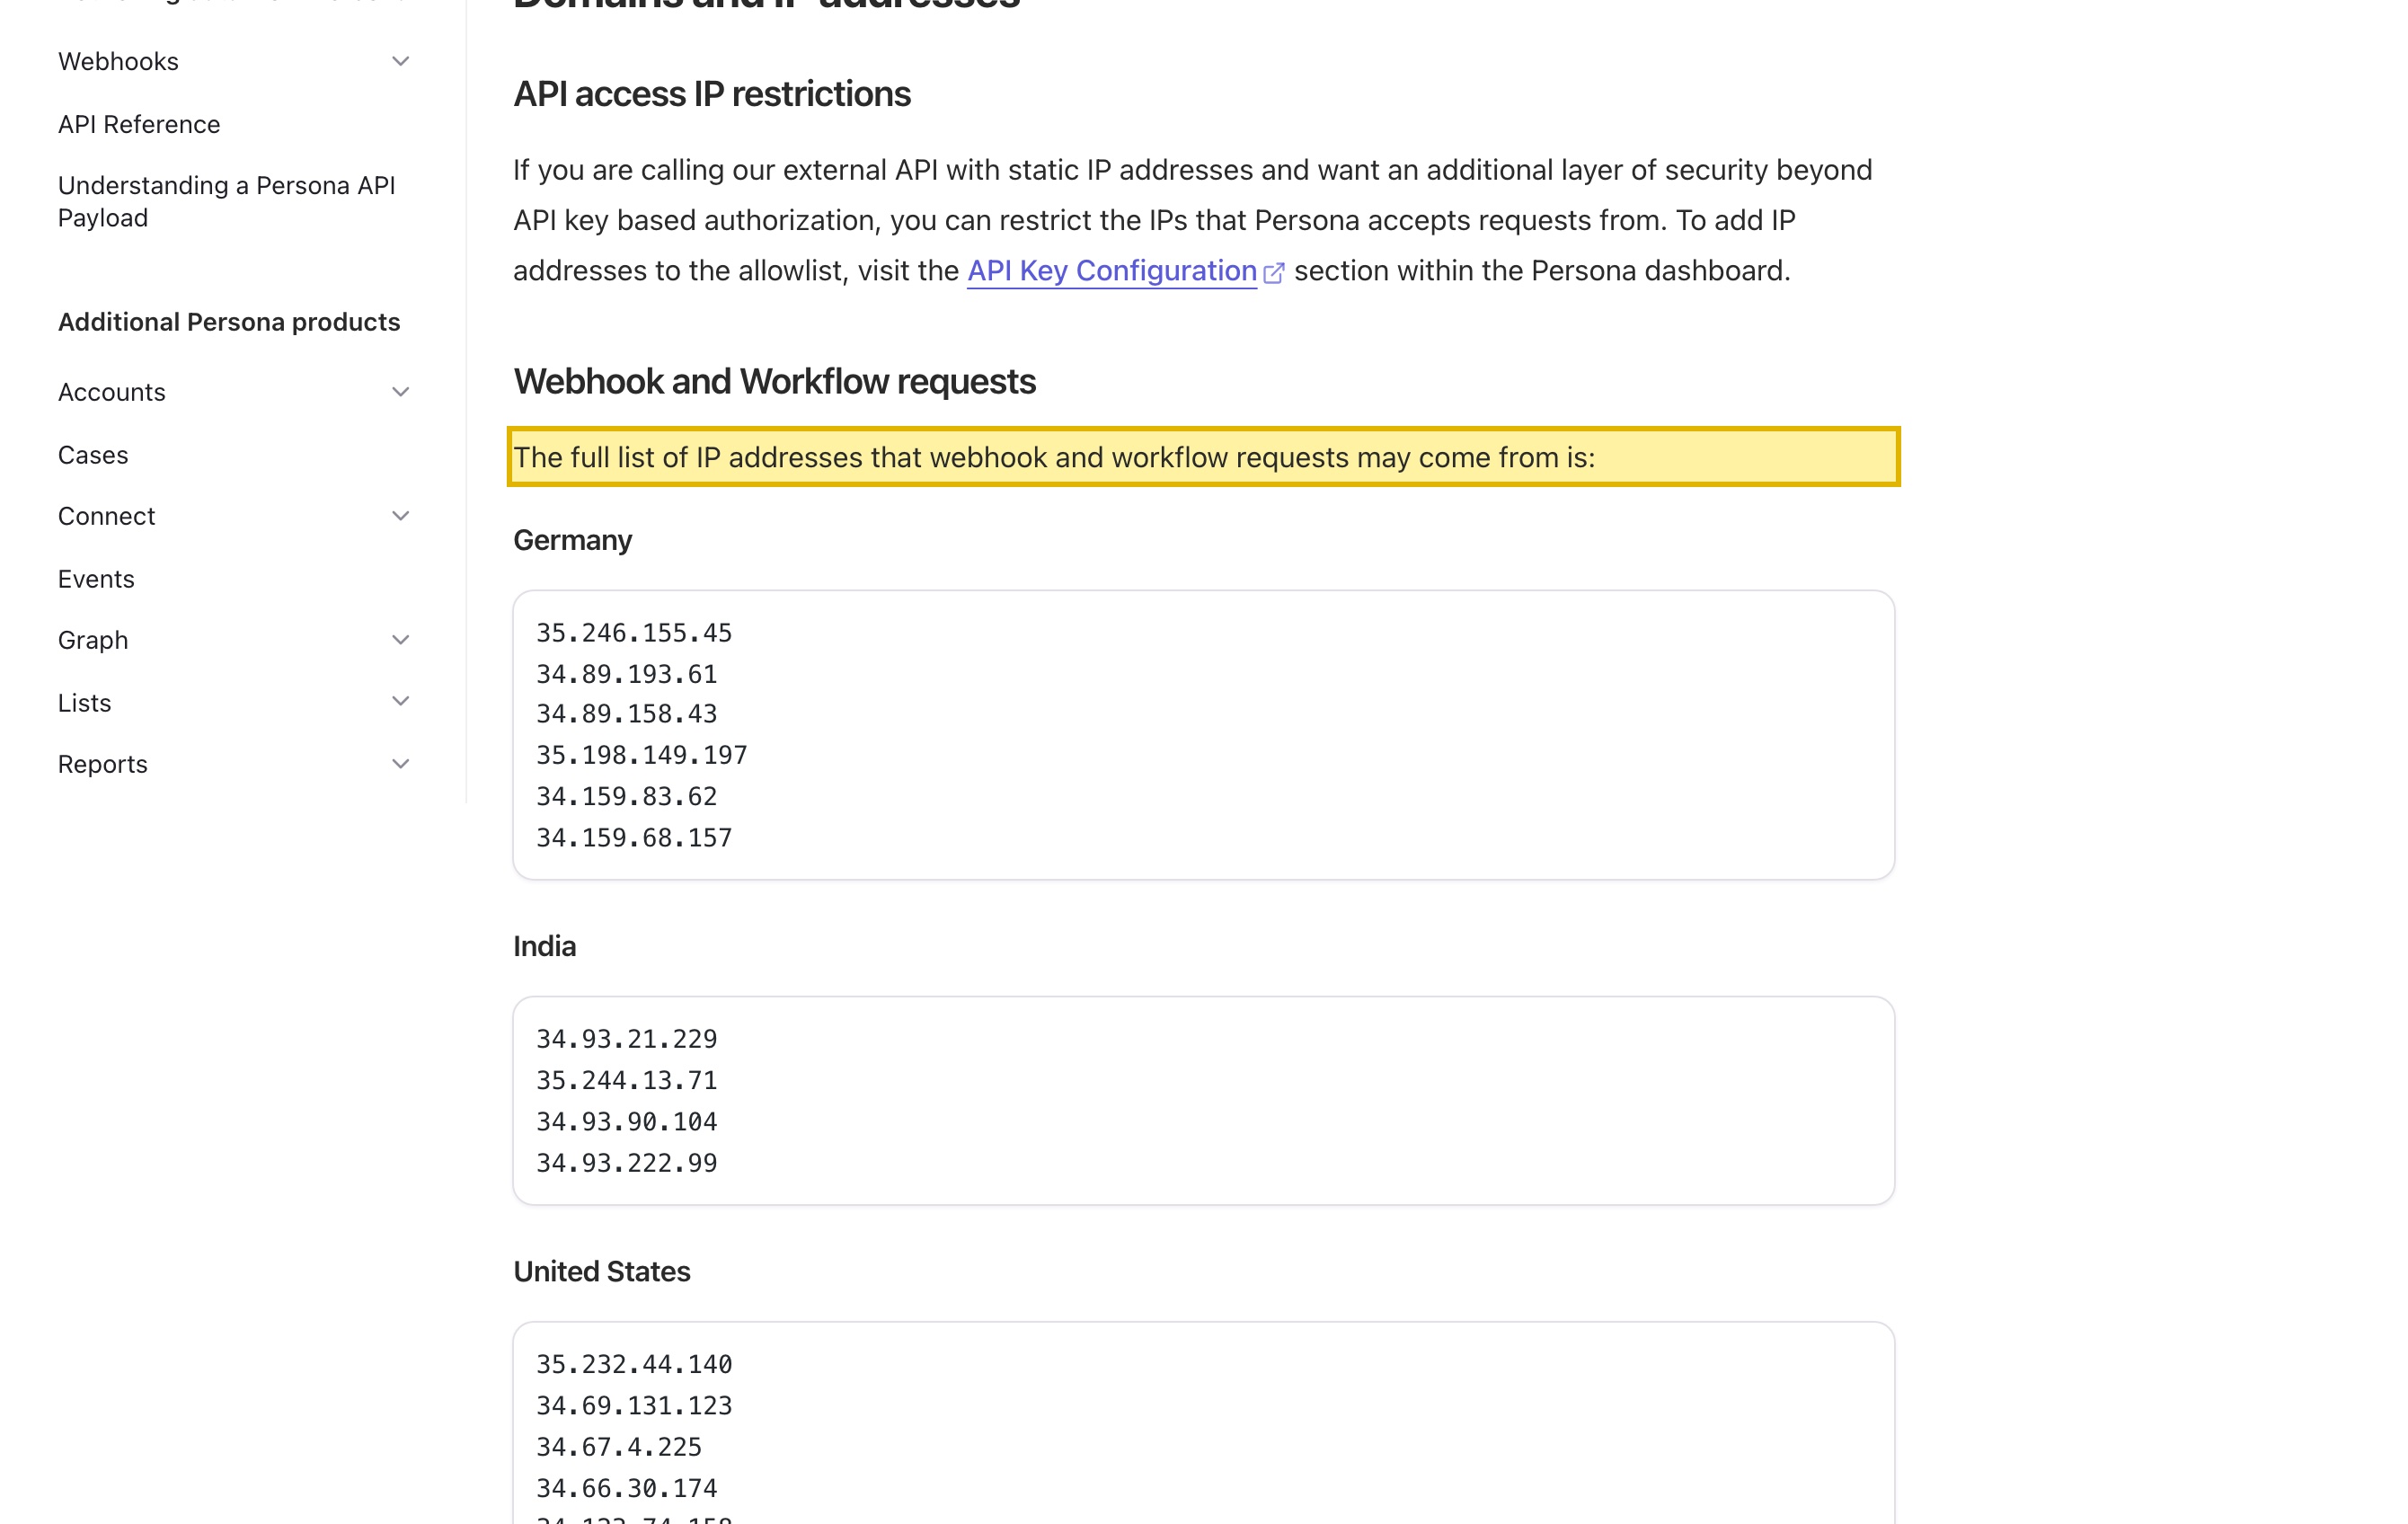
| Persona's own security documentation shows a US, EU and India footprint — no mainland-China region. Its developer-docs Security page (version 2026-09-29) states that "The full list of IP addresses that webhook and workflow requests may come from is:" and groups them under "Germany," "India" and "United States," with end-user email sent from "frompersona.com" or, for the "European Union," "eu.frompersona.com." Mainland China is named nowhere, so the ID images and face selfies it captures from Chinese applicants come to rest offshore. | Persona developer docs — Security (version 2026-09-29), retrieved 2026-10-09 |
| Persona offers data residency in the US or the EU only. Persona's Security Statement lets customers choose where verification data is stored between the United States (the default) and the European Union, and its published sub-processor list places its infrastructure and data-handling vendors (including AWS and Google Cloud) with service locations in the USA. Neither region is in the mainland, so switching between them only relocates the cross-border transfer — it does not satisfy a China in-country duty. | Persona Security Statement and sub-processor list (withpersona.com), retrieved 2026-10-09 |
| A government ID and a facial biometric are 'sensitive' personal information, so the consent and assessment load is heavier. Under PIPL, biometric characteristics and a person's specific identity are sensitive personal information (Article 28), requiring a separate, specific consent and demonstrated necessity (Article 29) and a prior impact assessment (Articles 55–56); exporting them to an offshore Persona region is a cross-border transfer needing a further separate consent and a transfer mechanism (Articles 38–40), with China's facial-recognition rules (in force since 2025) adding obligations specific to face data. | PIPL Articles 28, 29, 38–40, 55–56; China's facial-recognition rules (2025) |
| For some handlers the data must stay in China — and serving from inside the mainland triggers an ICP filing. Where the handler is a critical information infrastructure operator or moves personal information at volume, personal information collected in China must be stored in the mainland (Cybersecurity Law Article 39 (formerly Article 37)) — which an offshore verification store cannot satisfy — and authoritative verification of a mainland resident's identity runs through licensed domestic channels a foreign vendor cannot reach. Any public onboarding page actually served from inside China must also carry an ICP filing (State Council Order No. 292; MIIT Order No. 33) bound to a mainland resource Persona does not provide. | Cybersecurity Law Article 39 (formerly Article 37); State Council Order No. 292; MIIT Order No. 33, retrieved 2026-10-09 |
Sources verified by the 21YunBox compliance team on 2026-10-09.
When a team plans KYC onboarding or identity verification for mainland China with Persona, the first instinct is to ask whether the verification flow loads for an applicant in Shanghai or Shenzhen. That is the wrong first question. Persona’s whole job is to collect a government-issued identity document and a selfie and match the two — so the very first thing it does on Chinese soil is gather the two categories China’s law guards most tightly: a facial biometric and an official identity document. Whether the hosted flow renders quickly is a delivery detail. Whether you were allowed to move that data out of the country, and where it then comes to rest, is the decision — and that is settled by China’s law, not by a load-time test. Persona answers the “where” in its own documentation.
Persona operates no identity-verification region inside mainland China. Its own security documentation shows a platform running from the United States, the European Union and India, and its Security Statement lets a customer choose data residency in the United States (the default) or the EU — with no mainland site to select. The moment an ID photograph, a passport scan or a liveness selfie captured from a person in China lands in one of those regions, a cross-border transfer (数据出境) of sensitive personal information has taken place, and a separate body of law decides whether it was ever permitted.
Persona in China at a glance
| What decides it | In Persona's own terms — and China's law |
|---|---|
| What it is | Persona is an identity-verification and KYC onboarding platform: it captures a government-issued ID document and a selfie, runs a liveness and face-match check, and returns a verified identity. By design it collects a facial biometric and an official identity record for every person it screens. |
| Is it reachable from the mainland? | Reachability is not where this is decided, so this page publishes no China load-time figure. Even a flow that renders instantly can be unlawful to use — the question is the data it gathers and where that data goes, not its speed. (Cross-border delivery of an offshore verification flow can be inconsistent; that is an operational matter, not the decision, and never a reason to reach for a network workaround.) |
| Where does the verification data sit? | Offshore. Persona's security documentation shows its platform operating from the United States, the EU and India, and its Security Statement offers data residency in the United States (default) or the EU only. Its published sub-processor list places its infrastructure and data-handling vendors with service locations in the USA. There is no mainland-China region, so the ID scans and face selfies rest outside the country. |
| Collecting China KYC data into it | A government ID number and a facial biometric are sensitive personal information under PIPL (Article 28). Holding them in an offshore Persona is a cross-border transfer (数据出境) that needs notice, a separate consent specific to sensitive data, a transfer mechanism and a prior impact assessment (Articles 29, 38–40, 55–56); a data-export security assessment is more readily triggered for sensitive data. For a critical information infrastructure operator or large-volume handler, the Cybersecurity Law's Article 39 (formerly Article 37) adds an in-country storage duty an offshore region cannot meet. |
| Serving the public | A China-facing onboarding or verification screen actually served to mainland visitors from inside China needs an ICP filing bound to a mainland hosting resource. Persona names no mainland region, so there is nothing of its own to file against. |
| The lawful path | Keep China-collected verification data in-country on a consented, licensed domestic identity-verification route with in-country processing and storage, and deliver the China-facing onboarding surface in-country on ICP-filed infrastructure. 21YunBox maps, localizes and delivers; it never uses or suggests circumvention of any kind. |
A KYC check collects exactly what PIPL calls “sensitive” personal information
This is where an identity-verification platform differs from an ordinary data tool, and why it sits at the sharp end of China’s law. What Persona gathers to do its job — a photograph of a passport or national ID, the ID number on it, and a selfie or liveness video used to match a face — is not ordinary personal information. Under the Personal Information Protection Law, biometric characteristics and a person’s specific identity are sensitive personal information (Article 28): the category whose misuse most easily harms a person’s dignity or safety. Processing it at all requires a stricter footing than general data — a separate, specific consent and a demonstrated necessity (Article 29), and a personal-information protection impact assessment carried out before processing begins (Articles 55–56).
Layer the cross-border element on top and the consents stack: a transfer of that sensitive data to an offshore Persona region needs a further separate consent for the export, distinct from any agreement to be verified at all. Facial data carries an additional layer again — China’s dedicated rules on facial-recognition technology, in force since 2025, add their own necessity, notice and (at scale) filing obligations specific to face data. None of this is discharged by the fact that Persona is the tool doing the verifying; the duties land on you, the handler who decided to collect and export the data. Exactly which of them bite your flow is a risk to confirm with counsel against what your onboarding actually captures and stores.
An offshore verification store is a cross-border transfer — and “pick the EU region” doesn’t end it
Here is the gate most teams miss. A Persona account in any of its regions is, by definition, outside the mainland. The ID images, ID numbers, selfies and match results it holds for your applicants in China are personal information — mostly sensitive personal information — and loading them into an offshore Persona is a cross-border transfer under PIPL. The law puts the duty on the handler, not on Persona the processor: Articles 38–40 require notice, a separate consent and one transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. Because the data is sensitive and tied to identity, China’s data-export security assessment (数据出境安全评估) is more readily in play, and may be required before anything leaves.
Residency is the other half. If your organization is a critical information infrastructure operator or moves personal information at volume, the Cybersecurity Law’s Article 39 (formerly Article 37 — the data-localization provision was renumbered by the 2025 amendment that took effect on January 1, 2026, its substance unchanged) requires that personal information generated in China be stored in China — a duty a Persona account hosted in the US or the EU cannot satisfy. The obvious reflex is to flip the account to whichever region feels closest and call it in-country, but Persona offers only the United States and the EU; moving a Chinese applicant’s face scan from the US region to the EU region merely relocates the cross-border transfer, it does not retire it. Neither region is in the mainland, so neither resolves a China residency duty. Which of these obligations apply to your specific deployment is a risk map to settle with counsel, not a verdict — but none of them turns on how fast the verification returns.
No mainland region to file against — and why China identity checks tend to run domestically
A public-facing onboarding page, sign-up screen or verification step actually served to mainland visitors from inside China turns on an ICP filing (ICP 备案) under State Council Order No. 292 and MIIT Order No. 33, and that filing has to attach to a hosting resource physically in the mainland. Persona provides none, so there is nothing on Persona to file against — the same structural gap the residency duty exposes, seen from the licensing side.
There is also a product reality that points the same way. Verifying a mainland resident’s identity authoritatively means checking it against China’s national population and identity systems, which are reached through licensed, domestic channels — not something a foreign identity-verification vendor can do from offshore. So for the China portion of your onboarding, the lawful and the practical answer converge: the verification step itself generally needs to run on a consented, in-country route, while Persona keeps doing its work for the rest of your markets. That split — what must stay in China, what may stay with Persona — is a legal question before it is a technical one.
This is a risk map, not a verdict: whether you owe separate consent for sensitive data, a transfer mechanism, a data-export assessment, in-country storage, an ICP filing, or some combination depends on your entity, the verification data you hold, your role as handler, and who your applicants are — worth settling with counsel before you rely on it.
The lawful path — map, localize, deliver
There is a compliant way to run identity verification for a China-facing presence, and it has a shape. First, map: our China team works through your PIPL exposure on both fronts — the processing of sensitive data and its transfer — pinning down which verification records collected in China (ID images, ID numbers, selfies, match results) must stay in the country, what may lawfully leave, where a data-export security assessment or an Article 39 storage duty bites, and what your consent, notice and impact-assessment flow has to cover for sensitive personal information. The legal conclusions are settled with counsel; we build the technical picture that feeds them.
Then localize: we stand up and integrate a China-resident footing for the China verification data — a consented, in-country identity-verification route run through a licensed, CAC-filed domestic option, with processing and storage that stay in the mainland — so the check keeps working while the ID scans and face data stop leaving the country by default, and you keep Persona for the markets where it already serves you.
Then deliver: the China-facing onboarding or verification screen your applicants actually reach is itself a public service in the mainland, so it carries an ICP filing (备案) duty and needs compliant, in-country delivery. 21YunBox delivers it in-country — the 21YunBox Optimizer — set in front of what you already run, with no rebuild and no re-platform. The result is identity verification that runs legally and compliantly for your users in China. What we never do — and what no one lawfully can — is hand you a route around China’s data-export rules or around any network restriction; we localize what must stay and deliver in-country, and we never move personal information out of China by stealth.
Related reading:
- Cross-border data transfers under PIPL
- China’s data-export security assessment
- China’s Cybersecurity Law (data localization, Article 39)
- How to get an ICP filing for China


