Does Freshservice Work in China? Data Residency, ICP & Cross-Border Rules
Freshservice is cloud-only ITSM: your CMDB, tickets and the directory of China IT staff and requesters live in offshore Freshworks regions — US, EEA, UAE, India or Australia, none in mainland China — so your employees' PII and your IT-estate record are held abroad under PIPL. A compliance-first look at the data-residency, important-data and ICP doors.
Does Freshservice work in China?
Whether you can run Freshservice for a China operation is a data-residency and compliance-risk question, not a speed one. Freshservice is cloud-only ITSM: your CMDB, asset inventory, incident and change tickets, and the directory of your China IT staff and requesters live in Freshworks' offshore regions — US, EEA, UAE, India or Australia, none in mainland China.
So your China employees' personal information and the security-sensitive map of your China IT estate are held and processed abroad — a cross-border transfer under PIPL (Articles 38–40, with notice and separate consent), and for a CIIO or high-volume handler a data-localization duty under Cybersecurity Law Article 39 (formerly Article 37) that no offshore region can meet. A reachability check never sees this; where the data lives does. Our China team can map your Freshservice exposure with you →
What Freshservice's own documentation says about China
| Fact | Primary source |
|---|---|
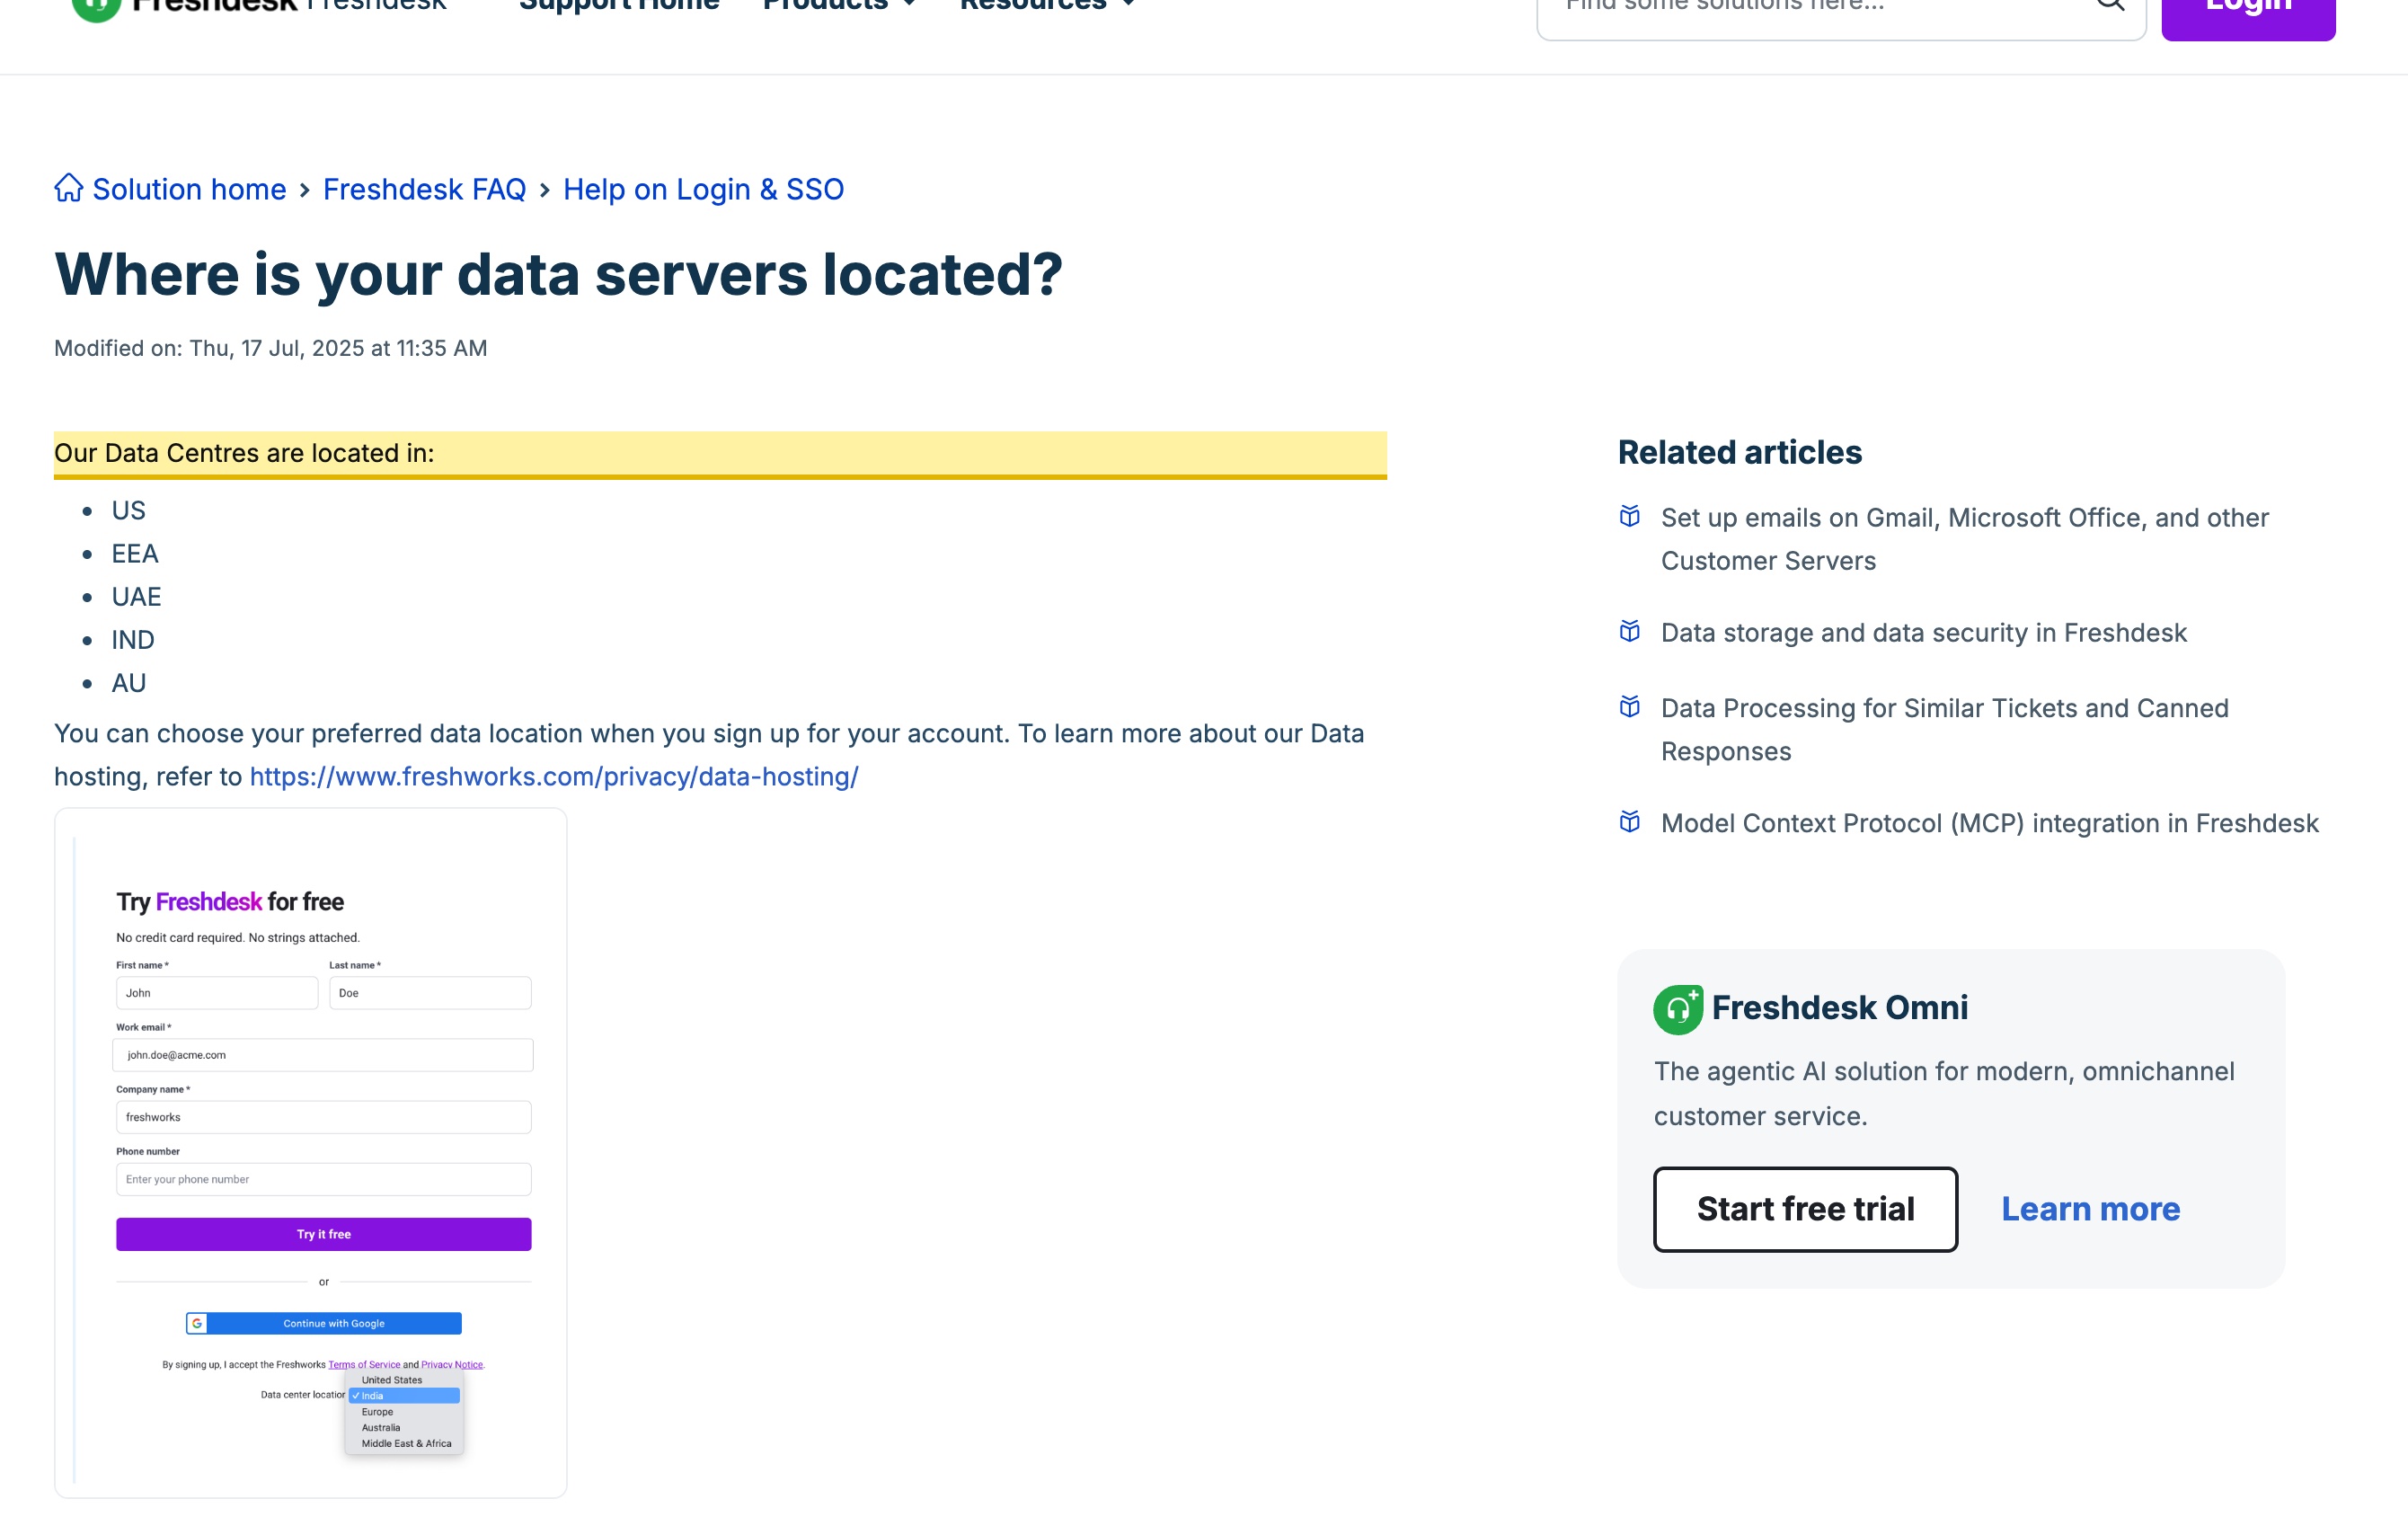
| In Freshworks' own words: “Our Data Centres are located in: US, EEA, UAE, IND, AU,” and “You can choose your preferred data location when you sign up for your account.” The region is fixed at signup, there is no mainland-China option, and the nearest regions — India and the UAE — are still offshore. | Freshworks support — Where is your data servers located?, retrieved 2026-10-11 |
| Freshservice is a cloud-hosted ITSM platform: the CMDB, asset inventory, incident and change tickets, and the directory of your China IT staff and requesters all live in whichever offshore Freshworks region your tenant is assigned. Optional on-network components (discovery and orchestration agents) still feed that offshore cloud — they are not an in-country data-residency option. | Freshworks — Data Hosting, retrieved 2026-10-11 |
| Personal information your tenant collects from people in China sits offshore — a cross-border transfer under PIPL Articles 38–40, with Article 13/23 notice and separate consent. For a CIIO or high-volume handler, Cybersecurity Law Article 39 (formerly Article 37) requires China-collected personal information to be stored in the mainland — which no offshore region meets. | PIPL Articles 38–40 and 13/23; Cybersecurity Law Article 39 (formerly Article 37) |
| The CMDB and tickets are a concentrated map of your China IT estate — hostnames, topology, configs, sometimes embedded secrets. Held offshore, that is both a cross-border data issue and, for sensitive operations, may implicate “important data” (重要数据) duties under the Cybersecurity Law (confirm classification with counsel). A public China-facing self-service portal is an internet information service, so it also carries an ICP filing duty bound to mainland hosting. | Cybersecurity Law — important data (重要数据); ICP filing (State Council Order No. 292, MIIT Order No. 33) |
Sources verified by the 21YunBox compliance team on 2026-10-11.
For a company running Freshservice to support a mainland-China operation, the deciding question is not how quickly the agent console or the self-service portal paints from Shanghai. It is where your data is allowed to live — because Freshservice is the system of record for your entire China IT estate. It holds the directory of your China IT staff and every requester who files a ticket, the CMDB and asset inventory that map how your China operation is built, the incident and change tickets that routinely carry internal system details and sometimes embedded secrets, and the workflow automation and AI triage that act on all of it. Freshservice is a cloud-only SaaS platform, hosted in Freshworks’ offshore data regions, with no region inside mainland China — so all of that is held and processed abroad. That makes this a compliance-risk question first, not a performance one.
Freshservice in China at a glance
| What decides it | In Freshworks' own terms — and China's law |
|---|---|
| What it holds | The record of your whole China IT estate: the directory of your IT staff and every requester who files a ticket (names, emails, phone, org, sometimes device and location); the CMDB and asset inventory (hostnames, network topology, service maps); the incident and change tickets that carry internal configs and sometimes embedded credentials; and the workflow automation and AI triage acting on all of it. |
| Where it runs | Freshservice is a cloud-only SaaS platform. Freshworks' data regions are the US, EEA (Europe), UAE, India and Australia; the location is fixed at signup, and none is inside mainland China. Optional on-network components (discovery and orchestration agents) still feed that offshore cloud — they are not an in-country data-residency option. |
| Employee & requester PII | Your China staff's and requesters' personal information rests in whichever offshore region your tenant is assigned — a cross-border transfer under PIPL Articles 38–40, layered on the Article 13/23 notice-and-consent. For a critical information infrastructure operator or a high-volume handler, Cybersecurity Law Article 39 (formerly Article 37) requires China-collected personal information to be stored in the mainland. |
| The CMDB & tickets — a security exposure | This is the half a speed test never sees. Offshore, the CMDB and tickets are a concentrated map of how your China operation is built and run — configuration, topology and operational secrets. That is both a cross-border data issue and, for sensitive operations, may implicate “important data” (重要数据) handling and data-security duties. Frame it as a risk to confirm with counsel, not a settled classification. |
| Automated triage & AI | Auto-triage and assignment, and predictive or agentic workflows that categorize, prioritize or decide about individual requesters, are automated decision-making under PIPL Article 24 — which requires transparency and an opt-out from decisions made solely by automated means. |
| A China-facing portal | A public self-service or ticket portal served to mainland users is an internet information service, so it carries an ICP filing (备案) duty bound to a mainland hosting resource. A Freshworks-hosted portal runs on offshore infrastructure, so it offers no ICP-filing path of its own. |
| Reachability is not the axis | Whether the console loads quickly from the mainland is operational, not the compliance question. What decides it is where the employee PII and the IT-estate record live. 21YunBox helps you keep the regulated data in-country, ICP-file any public portal, and deliver it compliantly — the 21YunBox Optimizer — in front of the Freshservice you already run. |
What it actually holds — the record of your China IT estate
Freshservice is not a static asset like a font or a script; it is the operational core of your China IT function, and it concentrates two kinds of data China’s law cares about. The first is personal information: the directory of your China IT staff and every requester who opens a ticket — names, work emails and phone numbers, org and reporting lines, and often device and location detail. The second — the half a reachability check never sees — is the CMDB and the tickets: the configuration management database with its hostnames, network topology, asset inventory and service maps, and the incident and change records that routinely carry internal system details, configs and sometimes credentials or secrets pasted into a ticket body or attachment. Together they are a precise map of how your China operation is built and run. Because Freshservice is a cloud-only SaaS platform hosted in Freshworks’ offshore regions, that map — and your China employees’ personal information — is held and processed abroad by default.
The doors: residency, the CMDB as a security exposure, automated triage, and ICP
The first door is personal-information residency. The staff and requester identities your Freshservice tenant collects from people in China are personal information under China’s Personal Information Protection Law, and holding them in an offshore region is a cross-border transfer (数据出境). The duty lands on you, the handler, not on Freshworks: Articles 13 and 23 require notice and a basis to collect the data, and Articles 38–40 require a transfer mechanism to send it abroad — a CAC security assessment, the CAC standard contract, or certification. Where a ticket carries sensitive personal information — ID numbers, health or disciplinary detail — PIPL Articles 28–29 raise the bar with a specific-purpose, necessity and separate-consent test. And for a critical information infrastructure operator or a high-volume handler, the Cybersecurity Law’s Article 39 (formerly Article 37 — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, with its substance unchanged) requires personal information generated in China to be stored in the mainland, which an offshore tenant cannot satisfy.
The second door is the one that makes an ITSM different from an ordinary SaaS. Your CMDB and tickets are not just more personal data — offshore, they are a concentrated, security-sensitive record of your China IT estate’s configuration, topology and operational secrets. That exposure is both a cross-border data issue and, for sensitive operations, may implicate “important data” (重要数据) handling and the data-security duties that attach to it. Treat the classification as a risk to confirm with counsel rather than a label to claim — the point is that a map of how your operation is built, sitting abroad, is a governance question a speed test will never surface.
The third door is automated handling. Freshservice’s auto-triage and assignment, and its predictive and increasingly agentic workflows that profile, prioritize or decide about individual requesters, are automated decision-making under PIPL Article 24, which gives individuals transparency and an opt-out from decisions made solely by automated means.
The fourth door is the ICP filing. If you publish a China-facing self-service or ticket portal to mainland users, you are running a public internet information service, and that turns on an ICP filing (ICP 备案) duty bound to a hosting resource physically inside the mainland. A Freshworks-hosted portal runs offshore, so there is nothing on it to file against — tuning the stack does not create the mainland footing a filing needs.
A reachability check never sees this
Freshservice is not the kind of service that simply refuses to load in China — the exposure is quieter and more durable than a slow paint. Even if the agent console and the portal opened instantly, using them would still place your China staff’s personal information and the concentrated record of your IT estate outside the country. A reachability test answers “did the page come back?”; it is blind to where the CMDB, the tickets and the employee directory come to rest, and to who is lawfully allowed to hold them. Where the data lives, not how fast it arrives, is what China’s law responds to.
This is a risk map, not a verdict that Freshservice is “blocked” or “illegal” in China. Which duties bite your case turns on your entity, what your tickets and CMDB actually hold, your role under Chinese law, and who your requesters are — worth settling the specifics with counsel before your China operation depends on it.
The lawful path — map, localize, deliver
There is a compliant way to run IT service management for a China operation, and it sits in front of the Freshservice your team already uses — no rebuild, no second tool, no migration.
First, map: our China team inventories what your Freshservice tenant holds — the staff and requester directory, the CMDB and asset data, the ticket content, and any China-facing portal — establishes where it is hosted (an offshore Freshworks region), the ICP status of any public portal, and the consent and residency basis each flow relies on. We build the technical picture; the legal conclusions are settled with counsel.
Then localize/govern: we help you keep the regulated data — employee and requester PII and the security-sensitive CMDB and ticket record — on a lawful in-country path, obtain the Article 13/23 notice-and-consent, provide the Article 24 opt-out for automated triage, and protect the IT-estate record rather than leaving it to rest abroad. Localize means keeping the data on an in-country path — never a route that ships it offshore anyway.
Then deliver: any public China-facing portal is an internet information service, so it carries an ICP filing duty bound to mainland hosting and needs compliant, in-country delivery. 21YunBox stands that up — the 21YunBox Optimizer — in front of what you already run, so it serves your users in China legally and compliantly. 21YunBox never uses or suggests circumvention of any kind — we keep in-country what the law says must stay, deliver the rest compliantly from inside the mainland, and never move personal information across the border by stealth. Making an offshore tenant merely reachable is not the answer; keeping the regulated data in-country, ICP-filing the portal and delivering it compliantly is. 21YunBox is a compliance overlay and partner to the ITSM you already run, not a competitor to it.
Related reading:
- How to get an ICP filing for China
- Cross-border data transfers under PIPL
- China’s Personal Information Protection Law (PIPL)
- China’s Cybersecurity Law


