Does Lokalise Work in China? PIPL Cross-Border Data Transfer & Content Residency
Lokalise is a cloud translation-management platform: the source strings, translation memory, glossaries and screenshots you send it are stored on AWS in EU regions, with no mainland-China region. Translating China content is a PIPL cross-border transfer of the personal information inside it, plus a permanent offshore corpus. A compliance-first look at where your content is allowed to live.
Does Lokalise work in China?
Whether Lokalise “works” in China is a content-residency question, not a reachability one — the risk is what happens to the source content you send it to translate.
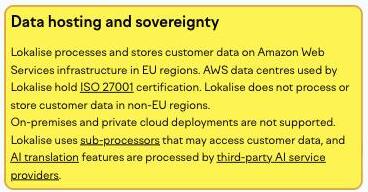
Lokalise is a cloud translation-management platform that, in its own words, "processes and stores customer data on Amazon Web Services infrastructure in EU regions" and "does not process or store customer data in non-EU regions" — EU, not mainland China, and it adds that "On-premises and private cloud deployments are not supported." So every string, document, translation memory entry, glossary and screenshot you send it leaves China for an offshore store: a PIPL cross-border transfer of the personal and sensitive information inside it, persisting in a corpus that grows with every sync. The lawful lever is to keep China content’s translation in-country — a licensed in-country alternative plus minimized, pseudonymized strings — not to make the offshore API reachable.
This is a risk map, not a verdict — settle the specifics with counsel. Our China team can map your Lokalise exposure →
What Lokalise's own documentation says about China
| Fact | Primary source |
|---|---|
| Lokalise stores your content offshore, with no China region and no self-host. Its security page states Lokalise "processes and stores customer data on Amazon Web Services infrastructure in EU regions" and "does not process or store customer data in non-EU regions," adding that "On-premises and private cloud deployments are not supported." EU is still offshore to mainland China, and there is no region to select in between. | Lokalise — Security (Data hosting and sovereignty), retrieved 2026-10-10 |
| As a translation-management system, Lokalise keeps a permanent offshore corpus of your content. It stores source strings, documents, translations, a shared translation memory, glossaries and context screenshots, plus the accounts of staff and external translators. Lokalise also states "AI translation features are processed by third-party AI service providers," and its published sub-processor list names machine-translation and AI providers, several located in the United States — so some content is sent onward beyond Lokalise’s own EU store. | Lokalise — List of Sub-processors; Help Center (What is Lokalise / Translation memory), retrieved 2026-10-10 |
| Sending source content abroad to be translated is a cross-border transfer the PIPL governs (数据出境). The handler — you, the Lokalise customer, not Lokalise the processor — must give notice, obtain a separate consent, and satisfy one transfer mechanism: a CAC security assessment, the CAC standard contract, or certification (PIPL Articles 38–40). Where the content is sensitive, Article 28 adds its own separate consent and a prior personal-information protection impact assessment. | Personal Information Protection Law, Chapter III (Articles 38–40) and Article 28 |
| For a CIIO or high-volume handler, personal information and important data collected in the mainland must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged). A translation memory and project store that live on offshore AWS cannot meet that in-country storage duty. | PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a team localizing into or out of mainland China, the question about Lokalise was never whether the platform loads — it does. Lokalise is a cloud translation-management system, and the real question is what happens to the content you hand it. Every source string, document, translation memory entry, glossary and context screenshot you send is stored on the vendor’s offshore infrastructure to be translated — and the content you most need translated is the content most likely to carry personal information: names and IDs in support tickets and user-generated text, employee data in HR files, customer records, and legal, medical or financial copy. By its own security page, Lokalise “processes and stores customer data on Amazon Web Services infrastructure in EU regions” — EU, not mainland China. So translating China content is a cross-border transfer of the personal information inside it (PIPL Articles 38–40, 数据出境), often Article 28 sensitive, and — because a translation-management system keeps a permanent translation memory and project store that grows with every sync — a content-residency question too.
Lokalise in China at a glance
| What decides it | In Lokalise's own terms — and China's law |
|---|---|
| What you hand it — and why it is personal information | Source strings and keys, uploaded documents and localization files, the resulting translations, a shared translation memory, glossaries, and context screenshots — plus the accounts of staff and the external vendors and freelance translators who touch the work. The content you most need translated is the content most likely to carry names, emails, IDs and HR, legal, medical or financial detail — often Article 28 sensitive personal information. You cannot anonymize a document you need translated in full. |
| It leaves China to be translated | By its own security page, Lokalise "processes and stores customer data on Amazon Web Services infrastructure in EU regions" and "does not process or store customer data in non-EU regions" — EU, not mainland China, with no region to select in between. Sending your content there is a cross-border transfer the PIPL governs (Articles 38–40, 数据出境): notice, a separate consent, and one transfer mechanism. The handler on the hook is you, not Lokalise. |
| It accumulates — the permanent corpus | A translation-management system does not translate and forget: your source, translations, translation memory, glossaries and screenshots persist on the vendor's offshore infrastructure and grow with every sync. For a critical-information-infrastructure operator or high-volume handler, mainland personal information and important data must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged — a duty an offshore corpus cannot meet. Sensitive content adds Article 28: separate consent and a prior impact assessment. |
| Kept, and sent onward to translate | Lokalise retains the corpus for the life of the contract — its security page says customer data is "automatically deleted" only "upon contract termination." Machine and AI translation reach further: Lokalise states "AI translation features are processed by third-party AI service providers," and its published sub-processor list names machine-translation and AI providers, several in the United States, so some text is processed and may be retained beyond Lokalise's own store. There is no no-data-retention self-host option: "On-premises and private cloud deployments are not supported." |
| Is it reachable? | Reachability is the delivery half, not the question — the web app and API load from China. The lawful lever is to keep China content's translation in-country: minimize and pseudonymize personal information in strings before any offshore call, route personal or sensitive China content through a licensed in-country translation path, and disable AI-training retention — not to make the offshore service reachable. Any China-facing surface that consumes the translations needs an ICP filing tied to a mainland hosting resource (State Council Order No. 292; MIIT Order No. 33). |
What you actually send — and where it goes
Lokalise is a translation-management system, so it does not merely pass text through — it holds your localization content as a working corpus. What you send it is the source material itself: UI strings and keys, uploaded documents and localization files, the translations produced against them, a shared translation memory that is common to every project and member on a team by default, glossaries, and the context screenshots Lokalise matches to strings. Around that sit the accounts of everyone who touches the work — your staff and the external vendors and freelance translators who are themselves people whose data Lokalise processes.
The sharp point is that the content you most need translated is the content most likely to carry personal information. Support tickets and user-generated content carry names, emails and addresses; HR and legal documents carry employee and counterparty data; product, medical, financial and contractual copy carries confidential and often Article 28 sensitive information. You cannot meaningfully anonymize a document you need translated in full.
And all of it comes to rest offshore. On its own security page, Lokalise states it “processes and stores customer data on Amazon Web Services infrastructure in EU regions” and “does not process or store customer data in non-EU regions.” From a mainland-China standpoint, EU is offshore — there is no mainland-China region to select. Machine and AI translation reach further still: Lokalise says “AI translation features are processed by third-party AI service providers,” and its published sub-processor list names machine-translation and AI providers, several of them in the United States. So the content does not sit in one place; it fans out to the vendor’s store and its processors, and the translation memory keeps a copy that grows with every job.
It’s a cross-border data transfer — under PIPL
Sending your source content abroad to be translated is, in plain terms, a cross-border transfer of everything inside it. Under the Personal Information Protection Law, moving the personal information in your strings, documents and screenshots to Lokalise’s offshore infrastructure (数据出境) requires the handler — you, the customer, not Lokalise the processor — to give notice, obtain a separate consent for the export, and stand up one transfer mechanism: a CAC security assessment, the CAC standard contract, or certification (PIPL Articles 38–40). Where the content is sensitive — health, financial, biometric, religious, government-ID or similar categories that translated material so often contains — Article 28 adds its own separate consent and a prior personal-information protection impact assessment on top.
For a translation-management system there is a second, quieter leg. The content is not translated and forgotten: it accumulates in the translation memory, glossaries and project store and stays there for the life of the contract — Lokalise says customer data is “automatically deleted” only “upon contract termination.” That is content residency. A critical-information-infrastructure operator or a high-volume handler owes an in-country storage duty an offshore corpus cannot meet — mainland personal information and important data must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). And where an export is permitted at all, crossing a volume or sensitivity threshold can require a CAC-led data-export security assessment before anything lawfully leaves.
Reaching the API isn’t the question — keeping the content in-country is
Treat reachability as the delivery half, not the question. Lokalise’s web app and API load from inside mainland China, and SOC 2 Type II, ISO 27001 and ISO 27017 certifications speak to how the vendor runs its EU platform — none of which changes where your China content comes to rest, or that it left China to get there.
Here the honest answer is narrower than the usual “just self-host it” lever, because Lokalise does not offer that door: its security page states plainly that “On-premises and private cloud deployments are not supported,” and there is no mainland-China region. So keeping China content’s translation in-country means a different set of moves. Minimize and pseudonymize the personal information in strings before anything is pushed offshore — strip the names, emails, addresses and IDs that a UI string or screenshot does not need, and disable or constrain the AI-translation features that route text to third-party providers. For the China-origin content that still carries personal or sensitive information, route its translation through a licensed in-country machine-translation or localization path whose data stays in the mainland, rather than exporting it to an offshore corpus. Localize here means stopping the export of China content and keeping its translation on an in-country path — never a tunnel that ships the content offshore anyway.
This is a risk map, not a verdict. Whether you owe a transfer mechanism, a separate consent, a personal-information protection impact assessment, in-country storage, a data-export security assessment, an ICP filing, or some combination of them turns on your entity, your data volumes, how much of what you translate is personal, sensitive or confidential, and whose data it is — settle the specifics with counsel before you decide what may lawfully leave.
The lawful path — map, localize, deliver
You do not have to drop Lokalise to run your China localization lawfully. 21YunBox is a compliant overlay, not a migration — and, for a platform you already run, a partner alongside your stack, not a competitor to it. Three moves fit together.
Map. Our China compliance team reads your PIPL cross-border, data-residency and data-localization obligations against your actual entity, your data volumes, and whose personal information your content carries — the users, employees and counterparties in China, and how much of it is sensitive — so the exposure is written down before anything moves.
Localize. Because the risk is the content leaving China and persisting offshore, we keep China-origin content’s translation in-country: minimized, pseudonymized strings, a licensed in-country machine-translation or localization path for what carries personal or sensitive information, and AI-training retention switched off. Localize means a lawful in-country path for China content, never a tunnel back to an offshore endpoint; only the minimized, lawfully transferable subset ever crosses.
Deliver. For any China-facing surface that consumes the translations — the website, the app, the help center your mainland users hit — the 21YunBox Optimizer provides ICP-filed, in-country delivery, in front of the stack you already run. No rebuild, no second codebase. 21YunBox never uses or suggests circumvention of any kind; the entire point is a lawful, filed, in-country path.
The goal is plain: your Lokalise localization runs legally and compliantly for your users in China.
Related reading:
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law and data localization (Article 39)
- China’s data-export security assessment measures
- How to get an ICP filing for China


