Does Amazon RDS Work in China? Data Residency, Localization & PIPL Cross-Border
Amazon RDS is AWS's managed relational database — the system of record for customer accounts and transactions. AWS's global partition has no mainland-China region, so an RDS instance there keeps China data offshore; an in-country option exists only in the separate AWS China partition (Sinnet/NWCD). A compliance-first look at RDS data residency, localization and PIPL cross-border transfer.
Does Amazon RDS work in China?
Whether Amazon RDS "works" in China is first a data-residency question — where the database's data is allowed to rest, not whether it connects.
RDS is AWS's managed relational database (MySQL, PostgreSQL, MariaDB, Oracle, SQL Server and Amazon Aurora) — the system of record that holds customer accounts, transactions and other personal information. AWS's global partition has no mainland-China region to select, so an RDS instance in any global region keeps your China users' data offshore, and every read and write from China is a cross-border transfer PIPL governs. A genuine in-country option does exist, but it is a separate partition: AWS China — Beijing operated by Sinnet, Ningxia operated by NWCD — runs under a distinct Amazon Web Services (China) account with its own ICP duty and feature gaps, an in-country region rather than automatic compliance. For a CIIO or high-volume handler, China personal information must stay on the mainland — PIPL Article 40 and the Cybersecurity Law Article 39 (formerly Article 37) localization duty — which an offshore RDS instance cannot do.
This is a risk map, not a ruling — your obligations turn on your entity, data volumes and whose data sits in the database. Our China team can map your RDS data-residency exposure →
What Amazon RDS's own documentation says about China
| Fact | Primary source |
|---|---|
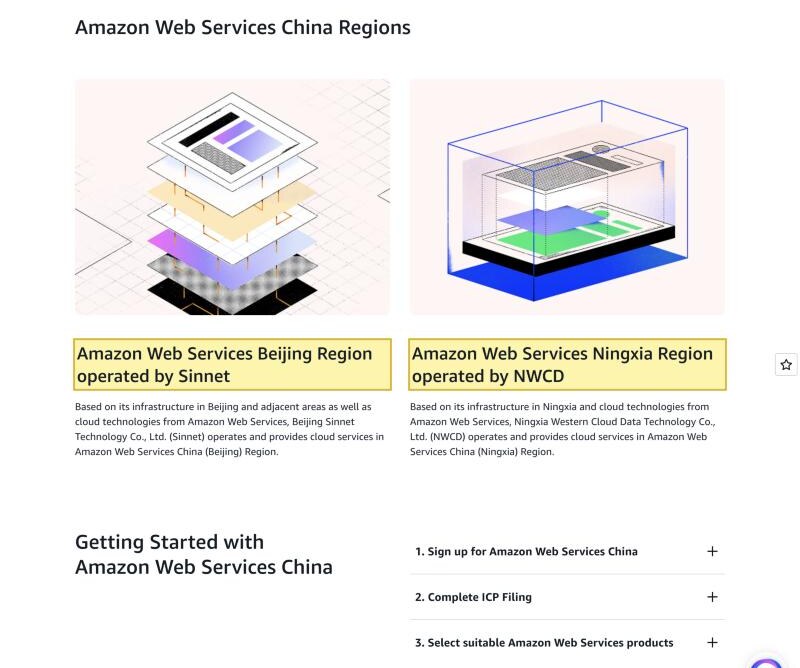
| AWS China is a separate partition, not the global service. On AWS's own China site, "China Regions' operations are separate from Amazon Web Services Global Regions," with the Beijing Region "operated by Sinnet" (Beijing Sinnet Technology Co., Ltd.) and the Ningxia Region "operated by NWCD" (Ningxia Western Cloud Data Technology Co., Ltd.). Using these regions requires a distinct Amazon Web Services (China) account and an ICP filing — and AWS's global regions include no mainland-China region to select. | AWS China — About the China Regions, retrieved 2026-10-10 |
| Amazon RDS is available in both AWS China regions — but only on the separate China account. AWS's regional product-services list shows "Amazon Relational Database Service (RDS)" available in the AWS China (Beijing) Region operated by Sinnet and the AWS China (Ningxia) Region operated by NWCD. That in-country capacity is a lawful, sovereign-cloud residency option — yet it is a distinct operator, account and feature set, so it is an in-country region, not automatic compliance. | AWS China — Regional Product Services, retrieved 2026-10-10 |
| China personal information in an offshore RDS instance is a cross-border transfer under PIPL. Where RDS holds the personal information of people in China and the instance sits in an offshore region, the handler — you, the AWS customer, not AWS — must give notice, obtain separate consent and satisfy one transfer mechanism: a CAC security assessment, the CAC standard contract, or certification. PIPL Articles 38–40 govern that transfer, and the security-assessment measures set when the assessment is mandatory. | PIPL Articles 38–40; CAC cross-border data measures |
| CIIOs and high-volume handlers must store China personal information on the mainland. PIPL Article 40 and Cybersecurity Law Article 39 (formerly Article 37) impose an in-country storage duty on critical-information-infrastructure operators and large-volume handlers; the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39 (substance unchanged). An RDS instance in an offshore global region structurally cannot meet that duty — the lawful levers are a licensed in-country deployment (self-hosted or the sovereign AWS China partition) with the China-facing surface on ICP-filed delivery. | PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a mainland-China audience, the deciding question about Amazon RDS is not whether a database instance launches or whether an application can connect to it — both are routine. It is where the data that instance holds is allowed to come to rest. Amazon RDS is AWS’s managed relational database service — MySQL, PostgreSQL, MariaDB, Oracle, SQL Server and Amazon Aurora — and a relational database is the most literal data-residency question on your whole stack: it is the system of record where customer accounts, orders, transactions and other personal information physically live. AWS’s global regions include no mainland-China region to select, so an RDS instance provisioned in a global region keeps that data offshore. A genuine in-country option does exist — but it is a separate AWS China partition, operated by local companies under a distinct account and its own filing duties, not the same service you reach from a global account.
Amazon RDS in China at a glance
| What decides it | In Amazon RDS's own terms — and China's law |
|---|---|
| Where the data physically rests (the region reality) | AWS's global partition has no mainland-China region. An RDS instance in a global region (Tokyo, Singapore, Hong Kong) keeps the data offshore. Mainland capacity exists only in the separate AWS China partition — Beijing (operated by Sinnet) and Ningxia (operated by NWCD) — on a distinct Amazon Web Services (China) account. |
| What the database holds, and why it is personal information | RDS is the system of record: customer accounts, orders, transactions, support history. Most of that is personal information under PIPL, and some — contact, financial and ID data — is sensitive. So where it rests is a legal question, not a performance one. |
| Your China users' records when the instance is offshore | Hold China personal information in an offshore RDS instance and you are making a cross-border transfer under PIPL (Articles 38–40): notice, separate consent, and one transfer mechanism — a CAC security assessment, the standard contract, or certification. |
| The in-country storage duty (CIIO / high-volume handler) | A critical-information-infrastructure operator or high-volume handler must keep China personal information on the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37) — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged). An offshore RDS instance structurally cannot. |
| Reachability is not the axis (and the China-facing surface) | Whether the database is reachable from China is a delivery matter, not the legal test; data-at-rest residency is. The lawful levers are to run the database in-country — a licensed sovereign AWS China region, or another in-country deployment — and to put any China-facing surface in front of it on ICP-filed delivery. |
Where the data actually rests
Pick an RDS region from a standard AWS account and the list you choose from is the global partition — and it contains no mainland-China region. The nearest regions, in Tokyo, Singapore or Hong Kong, are all outside the mainland, so the database and every byte it stores sit offshore. (Hong Kong is Chinese territory, but it is treated separately from the mainland for data-localization purposes.)
Mainland capacity does exist, but through a different door. AWS China is a separate partition: the Beijing Region is operated by Sinnet (Beijing Sinnet Technology Co., Ltd.) and the Ningxia Region by NWCD (Ningxia Western Cloud Data Technology Co., Ltd.). AWS states plainly that its China Regions’ operations are separate from the global Regions, that they require a distinct Amazon Web Services (China) account, and that using them involves an ICP filing. Amazon RDS is offered in both China regions — so an in-country, sovereign-cloud residency option genuinely exists.
What it is not is the same service you already run globally. It is a separate operator, a separate contract and account, its own service and general-availability gaps, and its own compliance surface. An in-country region is a lawful option; it is not automatic compliance.
What it holds is personal information
A relational database is not a cache or a CDN edge — it is the system of record. An RDS instance holds customer accounts, orders, payments, support history and the identifiers that tie them together. Most of that is personal information under PIPL, and some of it — contact details, financial data, government IDs — is sensitive personal information that draws heightened duties.
That is why residency, not reachability, is the test. When the personal information of people in China rests in an offshore RDS instance, you are making a cross-border transfer, and PIPL Articles 38–40 govern it: notice, separate consent, and one lawful transfer mechanism — a CAC security assessment, the CAC standard contract, or certification. The security-assessment measures set when that assessment is mandatory rather than optional.
On top of the transfer rules sits a harder duty. A critical-information-infrastructure operator or a high-volume handler must store China personal information inside the mainland — PIPL Article 40 and the data-localization rule in Cybersecurity Law Article 39 (formerly Article 37). An RDS instance in an offshore global region cannot satisfy an in-country storage duty, because the data is, by definition, not in the country.
Running it offshore — or on a no-China-region managed service — doesn’t meet the residency duty, and what does
The fix is not to make an offshore RDS endpoint reachable from China. Reachability was never the problem; residency is. If your obligations require China personal information to stay on the mainland, the lawful lever is to run the database in-country — self-hosted on mainland infrastructure where you operate your own engine, or on a licensed in-country, sovereign-cloud managed option such as Amazon RDS in the AWS China partition — and to keep consented, in-country storage for what the law says must stay.
Crucially, this is not a migration project in the usual sense. You are not re-platforming your application; you are placing a compliant, in-country system of record where the data must live, and putting the China-facing surfaces that read from it — the app, the API edge, the admin and reporting portals your mainland users reach — on ICP-filed, in-country delivery in front of the stack you already run. Localize means an in-country endpoint, not a tunnel back to an offshore one.
This page maps exposure; it is not a legal ruling. Your actual duties turn on your entity, how you classify the data, your transfer volumes and whether you are a critical-information-infrastructure operator — so settle those specifics with qualified China counsel before you rely on any single path.
The lawful path — map, localize, deliver
21YunBox is a compliant overlay, not a migration — and a partner to AWS and to your database team, not a competitor to them.
- Map. We read the PIPL cross-border, data-residency, data-localization (CII) and ICP obligations against your entity, your data volumes and whose personal information actually sits in the database — so you know which duties bite before you move anything.
- Localize. We run the database in-country so the personal information stays on mainland soil — self-hosted on mainland infrastructure where your engine allows, or on a licensed in-country / sovereign-cloud managed option — and keep consented, in-country storage for what must stay. For a managed service with no global China region, localize means standing up a lawful in-country equivalent, not a tunnel to the offshore endpoint.
- Deliver. Any China-facing surface in front of the database — the application, the API edge, the admin and reporting portals your mainland users hit — runs over ICP-filed, in-country delivery (the 21YunBox Optimizer), in front of the stack you already run. No rebuild, no second codebase.
The result is a database that runs legally and compliantly for your users in China. 21YunBox never uses or suggests circumvention of any kind.
Related reading
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law and data localization
- China’s data-export security assessment measures
- How to get an ICP license for a website in China


