Does Bynder Work in China? Data Residency, Localization & PIPL Cross-Border
Bynder is a cloud-only digital-asset-management SaaS on AWS, provisioned into one region — Frankfurt by default, or Tokyo, North Virginia, California, Ohio or Oregon, none in mainland China — so your brand assets, metadata and rights records come to rest offshore. A compliance-first look at where DAM content is allowed to rest under PIPL and China's data-localization law.
Does Bynder work in China?
Bynder works from the mainland, but it has no mainland-China region — so your brand assets, their metadata and rights records come to rest offshore, and residency, not reachability, is the compliance question.
Bynder is a cloud-only digital-asset-management SaaS on AWS, provisioned into one region — Frankfurt by default, or Tokyo, North Virginia, California, Ohio or Oregon. None is in mainland China, so the master files, web derivatives and replicated metadata rest abroad. The library is mostly brand IP, but it carries personal information too — model and talent releases, employee and customer likenesses, rights-and-usage records, and DAM user accounts — so exporting it is a PIPL cross-border transfer, and for a CIIO or high-volume handler there is an in-country storage duty an offshore cloud cannot meet. Bynder has no self-hosted edition, so the lawful lever is a licensed in-country equivalent, not a false self-host claim.
This maps exposure, not a ruling — settle specifics with counsel. Our China team can map your exposure →
What Bynder's own documentation says about China
| Fact | Primary source |
|---|---|
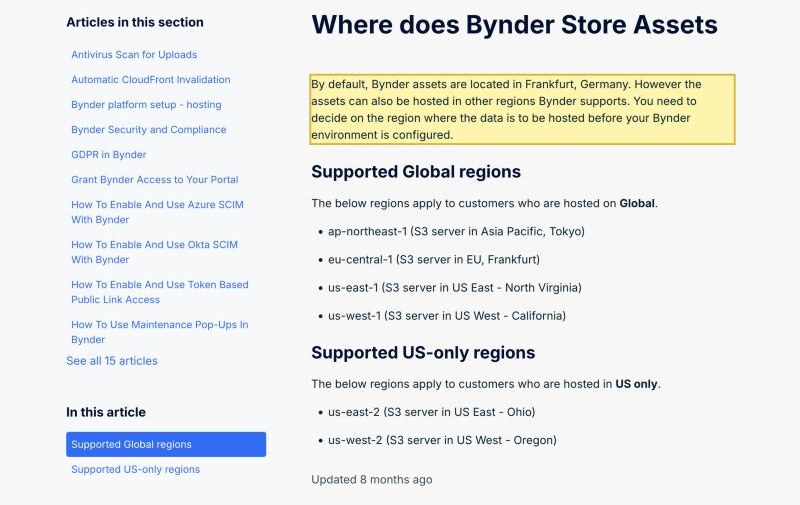
| Bynder stores assets in six AWS regions — none in mainland China. Its support docs say "By default, Bynder assets are located in Frankfurt, Germany," with Global customers on Tokyo (ap-northeast-1), Frankfurt (eu-central-1), North Virginia (us-east-1) and California (us-west-1), and US-only customers on Ohio (us-east-2) and Oregon (us-west-2). No mainland-China region exists to select, so master files, web derivatives and metadata come to rest offshore. | Bynder Support — Where does Bynder Store Assets (retrieved 2026-10-10) |
| Bynder is cloud-only, with no self-hosted edition to run on mainland infrastructure. Its hosting doc states your "application, user database, Javascript code, and content are hosted on a dedicated platform" across US-only, EU-only or Global setups, and that "Assets are stored in the region where they are uploaded. Metadata is replicated to all regions for fast access." The region is fixed before the environment is configured. | Bynder Support — Bynder platform setup - hosting (retrieved 2026-10-10) |
| Exporting the China personal information in your library is a PIPL cross-border transfer. Model and talent releases, the people depicted in photos and video, rights-and-usage records and DAM user accounts are personal information; sending it to an offshore region needs notice, separate consent and a transfer mechanism under PIPL Articles 38–40. | Personal Information Protection Law, Articles 38–40 (retrieved 2026-10-10) |
| A CIIO or high-volume handler owes an in-country storage duty an offshore DAM cannot meet. Personal information and important data collected in the mainland must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)); the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged. | PIPL Art 40; Cybersecurity Law Art 39 (formerly Art 37) (retrieved 2026-10-10) |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a team serving mainland China, the question about Bynder was never whether the platform loads or whether your users can reach the brand portal — it is a cloud application on AWS, and it opens from the mainland. The real question is a residency one: where are the assets Bynder holds allowed to come to rest? Bynder is a digital asset management (DAM) system — the single source of truth for a brand’s images, video, creative files, logos and product media, together with the metadata, versions and usage rights wrapped around them. It holds the actual files, not a pointer to them. Most of that is brand intellectual property, but a real slice is personal information — model and talent releases, the employees and customers depicted in photos and video, rights-and-usage records that name people, and the user accounts of everyone with access. Bynder is cloud-only: a SaaS provisioned into one region — Frankfurt by default, or a US or Tokyo region — with no mainland-China region to select and no self-hosted edition to run in-country.
Bynder in China at a glance
| What decides it | In Bynder's own terms — and China's law |
|---|---|
| Where the assets physically rest | You choose one region before the environment is configured; in Bynder's own words, "Assets are stored in the region where they are uploaded. Metadata is replicated to all regions for fast access." The supported regions are Frankfurt, Tokyo, North Virginia, California, Ohio and Oregon — none in mainland China. Master files, web derivatives and metadata therefore rest offshore. |
| What the library holds, and why residency bites | A DAM is mostly brand intellectual property — images, video, creative, logos, product media — but it still carries personal information: model and talent releases, the employees and customers depicted in the files, rights-and-usage records that name people, and the user accounts of everyone with access. It is not the uniformly Article 28 sensitive trove a legal or health repository is, yet specific items — a model's government-ID in a release, an identifiable biometric likeness — can reach that bar, and the rest is personal information under PIPL all the same. |
| Your mainland users' assets | Assets uploaded, and personal information captured, in China that come to rest in Frankfurt, Tokyo or a US region are a cross-border transfer PIPL governs: notice, a separate consent, and one transfer mechanism (PIPL Articles 38–40). The handler on the hook is you, the operator — not Bynder, and not Thomas H. Lee Partners, which took a majority stake in 2022. |
| In-country storage duty | A critical information infrastructure operator or high-volume handler owes an in-country storage duty an offshore DAM cannot meet — mainland personal information and important data must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39, substance unchanged. |
| Is it reachable? | Treat reachability as the delivery half, not the question — the portal and APIs load from the mainland, and Bynder even distributes "the web versions (derivatives) of the content" globally via CDN. Because Bynder is cloud-only with no self-hosted edition, the lawful lever is to run the asset store in-country on a licensed in-country or sovereign equivalent, and any China-facing surface in front of it — the brand portal, public share links, the web client or admin console — needs an ICP filing tied to a mainland hosting resource (State Council Order No. 292; MIIT Order No. 33). |
Where the assets actually rest
Bynder does not give you a region to toggle after the fact; you decide where the data is to be hosted before your environment is configured, and that choice decides where your asset library lives. Its own support documentation makes the footprint explicit: assets default to Frankfurt, Germany, and the supported regions are, for Global customers, Tokyo (ap-northeast-1), Frankfurt (eu-central-1), North Virginia (us-east-1) and California (us-west-1), and for US-only customers, Ohio (us-east-2) and Oregon (us-west-2). There is no mainland-China region on that list and no China data-residency option to select. Point your brand at Bynder and it lands on one of those offshore regions.
Two things then rest abroad, not one. First the content itself: Bynder states that your “application, user database, Javascript code, and content are hosted on a dedicated platform,” and that “Assets are stored in the region where they are uploaded. Metadata is replicated to all regions for fast access.” So the master files sit in your chosen offshore region, and the descriptive metadata — the fields that name people, products and usage rights — is copied to every region in the set. Second, delivery: to serve a global audience, Bynder distributes “the web versions (derivatives) of the content” worldwide over a CDN. Under the Personal Information Protection Law, moving the China personal information those assets and records contain out of the country is a cross-border transfer, and the handler responsible is you.
What it holds is personal information — and some of it sensitive
Be precise about a DAM, because overstating it helps no one. A brand-asset library is, in the main, intellectual property — the creative, the logos, the product imagery — not a case file of health or financial records. But it is not free of personal information either. Model and talent releases carry names, signatures and sometimes a government-ID number; the photos and video themselves depict identifiable employees, customers and models, and an identifiable face or voice can be biometric; rights-and-usage records name the people and parties a license runs to; and the user directory holds the names and email addresses of everyone with access. Some of that reaches the Article 28 sensitive bar — a release that captures an ID number, a biometric likeness tied to an identity — while the rest is ordinary personal information under PIPL. Either way, the moment that material is stored and replicated on an offshore region, that personal information has left the mainland.
That matters beyond best practice. For a critical information infrastructure operator, and for a handler whose volumes cross the regulators’ thresholds, personal information and important data collected in the mainland must be stored in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)). An offshore DAM structurally cannot satisfy that duty — the content is, by definition, in the wrong country. And where an export is permitted at all, crossing a volume or sensitivity threshold can trigger a CAC-led data-export security assessment before any of it lawfully leaves.
Running it on a no-China-region cloud doesn’t meet the residency duty — and what does
The honest summary is narrow and important: nothing about Bynder is “blocked,” and the exposure is not the software — it is a managed service that parks a brand’s asset library, its metadata and its rights records outside the mainland. There is a wrinkle specific to this vendor, though: Bynder is cloud-only. There is no self-hosted Bynder edition you can stand up on mainland-China infrastructure, so the in-country lever here is not “run the vendor’s binary locally.” It is to run the asset store in-country another way — a lawful in-country or licensed sovereign-cloud equivalent that keeps the master files, metadata and rights records on mainland soil — while only a minimized, consented, lawfully transferable subset ever crosses the border. Pointing a mainland connector back at the offshore Bynder endpoint is not localization and does not meet the storage duty; standing up a lawful in-country equivalent is. And because a DAM exists to distribute, there is a delivery half: any China-facing surface in front of the library — the brand portal, the public share links, the web client or admin console your mainland users hit — earns its own ICP filing tied to a mainland host.
This is a risk map, not a verdict. Whether you owe in-country storage, a transfer mechanism, a separate consent, an ICP filing, or some combination turns on your entity, your data volumes, how much of the library and its rights records is personal or Article 28 sensitive, and who those people are — and it is worth settling with counsel before you decide where a single mainland asset comes to rest.
The lawful path — map, localize, deliver
You do not have to drop Bynder to run digital asset management lawfully for mainland China. 21YunBox is a compliant overlay, not a migration — and, for a platform you already run, a partner that sits alongside your stack, not a competitor to it. There are three moves, and they fit together.
Map. Our China compliance team reads your PIPL cross-border, data-residency and data-localization (CII) obligations against your actual entity, your asset and user volumes, and whose personal information your releases, media and rights records carry — so the exposure is written down before anything is moved.
Localize. Because the risk is where the asset library rests, we run the content repository in-country — on a licensed in-country or sovereign-cloud equivalent — so the master files, metadata and rights records China requires to stay on mainland soil do. Localize means a lawful in-country deployment of the asset store, never a tunnel back to an offshore endpoint; only the minimized, lawfully transferable subset ever crosses.
Deliver. For any China-facing surface in front of the library — the brand portal, the public share links, the reporting console, the web client your mainland users hit — the 21YunBox Optimizer provides ICP-filed, in-country delivery, in front of the stack you already run. No rebuild, no second codebase. 21YunBox never uses or suggests circumvention of any kind; the entire point is a lawful, filed, in-country path.
The goal is plain: your digital asset management runs legally and compliantly for your users in China.
Related reading:
- How to get an ICP filing for China
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law and data localization
- China’s data-export security assessment measures


