Does AuditBoard (Now Optro) Work in China? Audit Evidence, PIPL & Data Residency
AuditBoard — rebranded Optro in 2026 — is hosted on AWS in the US, Canada, UK, EU and Singapore, with no mainland-China region, so the audit evidence, control and risk records, and personnel PII it holds come to rest offshore: a PIPL cross-border transfer. A compliance-first look at where your audit and GRC data is allowed to live.
Does AuditBoard work in China?
Reaching AuditBoard (now Optro) isn't the question — where the audit evidence and personnel PII it holds comes to rest is, and that's offshore.
Optro (formerly AuditBoard) is hosted on AWS in the US, Canada, UK, EU and Singapore — no mainland-China region. So the workpapers, control and risk records, and the PII of control owners, auditees and employees it collects in China are stored outside the mainland: a cross-border transfer under PIPL. 21YunBox maps that exposure, localizes in-country storage for the records that must stay, and delivers any China-facing surface over ICP-filed infrastructure — no rebuild.
What AuditBoard (now Optro)'s own documentation says about China
| Fact | Primary source |
|---|---|
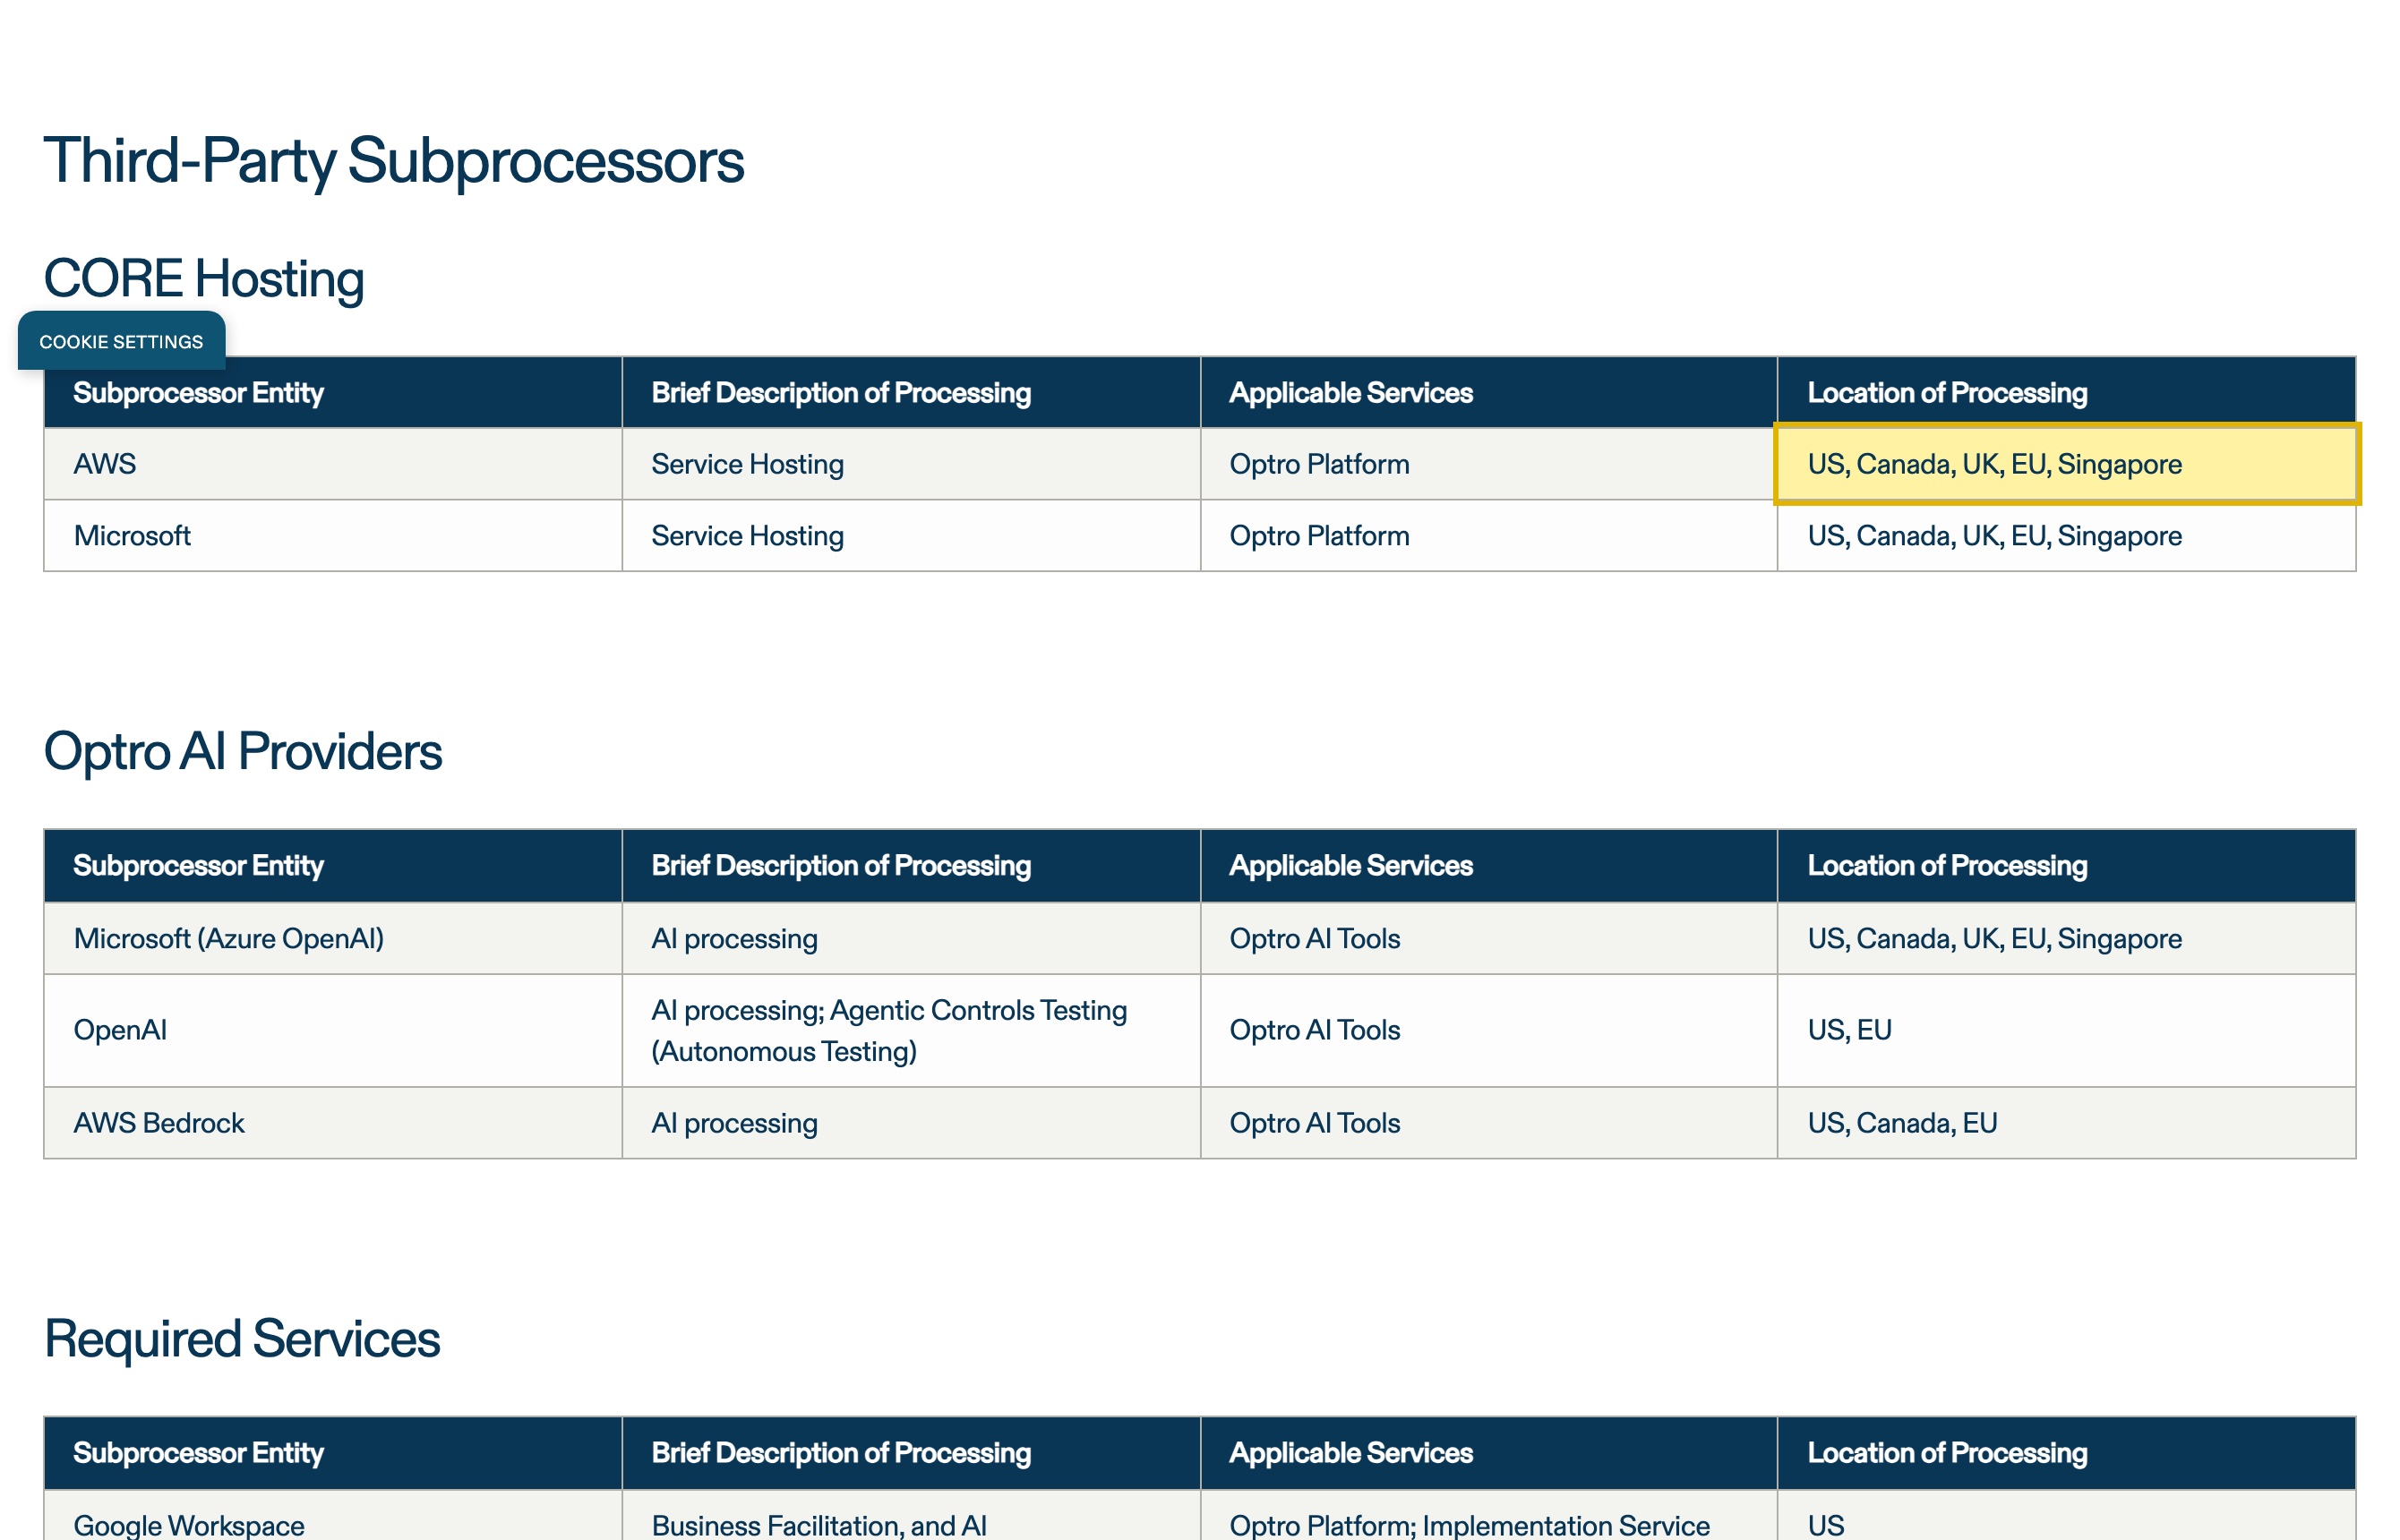
| Optro (formerly AuditBoard) hosts its platform on AWS, and its subprocessor register gives the 'Optro Platform' a 'Location of Processing' of 'US, Canada, UK, EU, Singapore' — none in mainland China. | Optro subprocessor list |
| Optro's Technology & Security page states 'Optro is hosted on AWS' and that servers are 'replicated and load-balanced across data centers and regions' — a region set that includes no mainland-China location. | Optro Technology & Security |
| Sending personal information collected in mainland China to an offshore region is a cross-border transfer requiring notice, a separate consent, and a transfer mechanism (CAC security assessment, standard contract, or certification). | PIPL Articles 38–40 |
| Personal information collected in the mainland by a critical information infrastructure operator or large-volume handler must be stored in China (data localization). | Cybersecurity Law Article 39 (formerly Article 37) |
Sources verified by the 21YunBox compliance team on 2026-10-10.
For a team serving mainland China, the question about AuditBoard — the connected-risk platform rebranded Optro in March 2026 — was never whether the dashboard loads. It almost always does. The question is where the records behind it are allowed to come to rest, and the platform answers that plainly in its own trust documentation. Optro is hosted on AWS, and its subprocessor register lists exactly one set of hosting locations: the United States, Canada, the UK, the EU and Singapore. None is in mainland China. Yet the platform is where your audit workpapers and evidence, SOX control tests, risk registers and third-party records live — together with the names, roles and emails of the control owners, auditees and employees written throughout them. Reaching it is the delivery half; where that evidence is stored is the exposure.
AuditBoard (now Optro) in China at a glance
| What decides it | In Optro's own terms — and China's law |
|---|---|
| Where the records live | "Optro is hosted on AWS," and its subprocessor register gives the platform's "Location of Processing" as "US, Canada, UK, EU, Singapore." None is in mainland China, and the hosting region is fixed once, at provisioning. |
| What it holds, and why it's personal information | Audit workpapers and evidence, SOX control tests, risk registers, InfoSec and third-party records — plus the names, roles and emails of the control owners, auditees and employees throughout them. Findings that document allegations about an identifiable person edge into Article 28 sensitive personal information. |
| Your mainland data on the platform | Collected in China and written to an offshore AWS region, it is a cross-border transfer PIPL governs — notice, a separate consent, and one transfer mechanism (PIPL Articles 38–40). |
| In-country storage duty | A critical information infrastructure operator or large-volume handler owes an in-country storage duty the hosted platform cannot meet — mainland personal information must stay in the mainland (PIPL Article 40; Cybersecurity Law Article 39 (formerly Article 37)) — the 2025 Cybersecurity Law amendment, in force January 1, 2026, renumbered the data-localization article from 37 to 39. |
| Is it reachable? | Treat reachability as the delivery half, not the question. A China-facing dashboard, portal or intake form also needs an ICP filing tied to a mainland hosting resource (State Council Order No. 292; MIIT Order No. 33). |
No mainland region, so the audit trail leaves the country
Optro’s subprocessor register is explicit about where the platform runs: under Location of Processing, AWS hosts the Optro Platform in “US, Canada, UK, EU, Singapore.” The company’s Technology & Security page says the same thing in plainer words — “Optro is hosted on AWS,” and its servers are “replicated and load-balanced across data centers and regions.” Not one of those regions is in mainland China; Singapore, added to the platform’s core hosting in October 2026, is the nearest, and it still sits outside the border. The hosting region is chosen once, at provisioning, from that offshore list. So when your mainland teams upload evidence, close out control tests, or log an issue, that data is written to whichever offshore AWS region your tenant was created in. Under China’s Personal Information Protection Law, sending personal information collected in the mainland to one of those regions is a cross-border transfer — and the handler on the hook is you, not the vendor.
The evidence AuditBoard holds is personal information
Audit and compliance records are dense with people. A workpaper names the control owner who signed off; a test records the auditee who provided the sample; an issue names the manager whose process failed; a third-party review carries the counterparty’s and signatory’s details. Email addresses, job titles, reporting lines and reviewer notes are personal information the moment they describe an identifiable person — and a mainland employee’s or user’s personal information sent to an offshore region is governed by PIPL on export. The exposure sharpens where findings document allegations, investigations or misconduct tied to a named individual: that edges into sensitive personal information under PIPL Article 28, which carries a higher bar — a specific purpose, strict necessity, and separate consent. For a handler that crosses the data-export security assessment threshold, the whole export may need a CAC review before any of it lawfully leaves. The irony is hard to miss: the platform you run to manage compliance can create a cross-border exposure of its own.
Narrowing the exposure doesn’t close the door
There are real levers to reduce what crosses the border — scope which modules hold mainland data, redact or tokenize fields before they are entered, and pick the provisioning region nearest your users. They are worth pulling, but be clear about what they do. They change the contents and the destination of the transfer; they do not change the fact of it. The platform is SaaS with no mainland-China region to select and no self-managed, on-premises edition to run inside the border, so every lever still lands the data in an offshore AWS region. Residency is untouched. And a China-facing surface — an auditee portal, an evidence-request form, a dashboard shared with mainland staff — additionally needs an ICP filing tied to a mainland hosting resource before it may be served, whatever you do about the data behind it. This is a risk map, not a verdict: whether you owe a transfer mechanism, a separate consent, in-country storage, an ICP filing, or some combination turns on your entity, your data volumes, how much of the record is personal or sensitive, and who your users are — worth settling with counsel before you point a single mainland user at the platform.
The lawful path — map, localize, deliver
You do not have to drop AuditBoard, now Optro, to run it lawfully for mainland China. 21YunBox is a compliant overlay, not a migration — and for a platform like this, a partner that sits alongside the tool you already run, not a competitor to it. There are three moves, and they fit together.
Map. Our China compliance team reads your PIPL cross-border, data-residency and sensitive-PI obligations against your actual entity, your data volumes, and who your mainland users and employees are — so the exposure in your audit, risk and compliance records is written down before anything is rewired.
Localize. Because the hosted platform has no mainland region, we stand up consented, in-country storage and processing for the records that must stay on mainland soil, so the evidence and personnel data China requires to remain in-country does — while only the minimized, lawfully transferable subset ever reaches your offshore tenant.
Deliver. For any China-facing surface — a dashboard, an auditee portal, an intake or evidence-request form — the 21YunBox Optimizer provides ICP-filed, in-country delivery, in front of the stack you already run. No rebuild, no second codebase, no move off the platform. 21YunBox never uses or suggests circumvention of any kind; the entire point is a lawful, filed, in-country path.
The goal is plain: your audit and compliance program runs legally and compliantly for your users in China.
Related reading:
- How to get an ICP filing for China
- Cross-border data transfers under PIPL
- China’s Cybersecurity Law and data localization
- China’s data-export security assessment measures


